

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

binary-analysisdebuggersexploitation+5
113
3 years ago
jadx preview

jadx

GitHubskylot/jadx

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
50.8k0 days ago
r2gopclntabParser preview

r2gopclntabParser

GitHubasherdll/r2gopclntabparser

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
binary-analysisdebuggersforensics+3
175 months ago
failpoint preview

failpoint

GitHubpingcap/failpoint

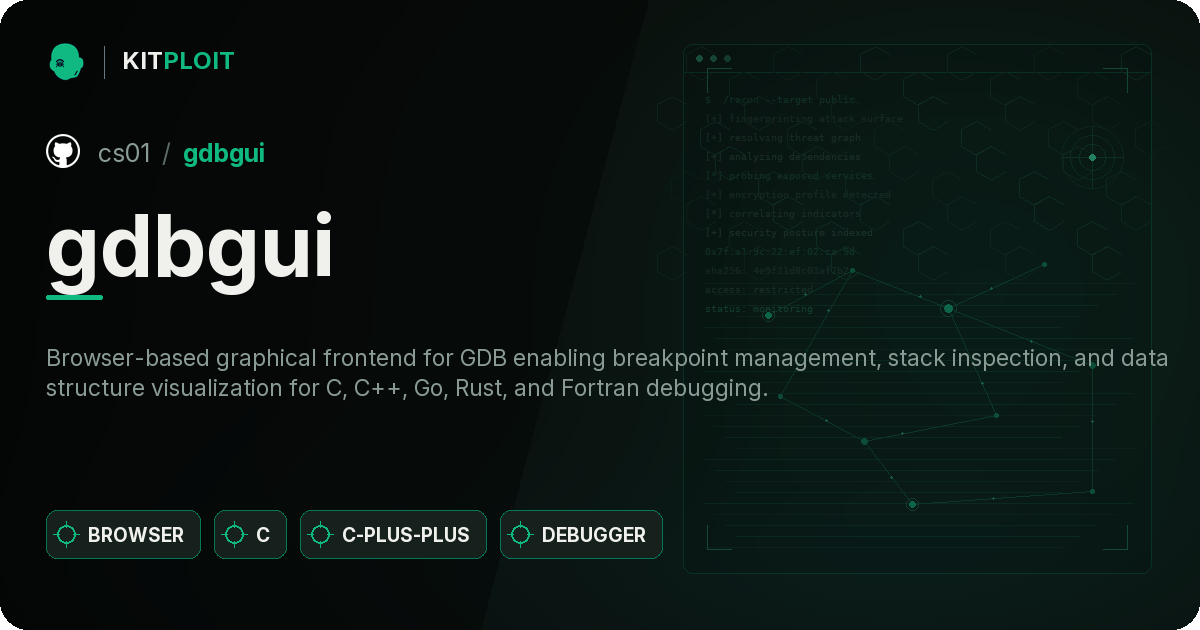
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
chaos-engineeringdebuggersgeneral-purpose-utilities
8961 month ago
gdbgui preview

gdbgui

GitHubcs01/gdbgui

Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…

binary-analysisdebuggersreverse-engineering+1
10.4k1 year ago
COM-Code-Helper preview

COM-Code-Helper

GitHubfboldewin/com-code-helper

Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
binary-analysisdebuggersmalware-analysis+1
1866 years ago
asafw preview

asafw

GitHubnccgroup/asafw

Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
binary-analysisdebuggersembedded-systems-security+4
1084 years ago
gftrace preview

gftrace

GitHubleandrofroes/gftrace

A command line Windows API tracing tool for Golang binaries.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1592 years ago
super-trouper preview

super-trouper

GitHubcrissyfield/super-trouper

MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…

android-securitybinary-analysisdebuggers+5
474 days ago
ctf-tools preview

ctf-tools

GitHubzardus/ctf-tools

Some setup scripts for security research tools.

binary-analysiscryptographyctf+9
9.5k29 days ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.2k19h 26m ago
rr preview

rr

GitHubrr-debugger/rr

Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
binary-analysisdebuggersdynamic-code-analysis
10.7k10 days ago
PowerShell-Suite preview

PowerShell-Suite

GitHubfuzzysecurity/powershell-suite

My musings with PowerShell
binary-analysisdebuggersforensics+5
2.7k4 years ago
bincat preview

bincat

GitHubairbus-seclab/bincat

Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
binary-analysisdebuggersreverse-engineering+2
1.9k1 year ago
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

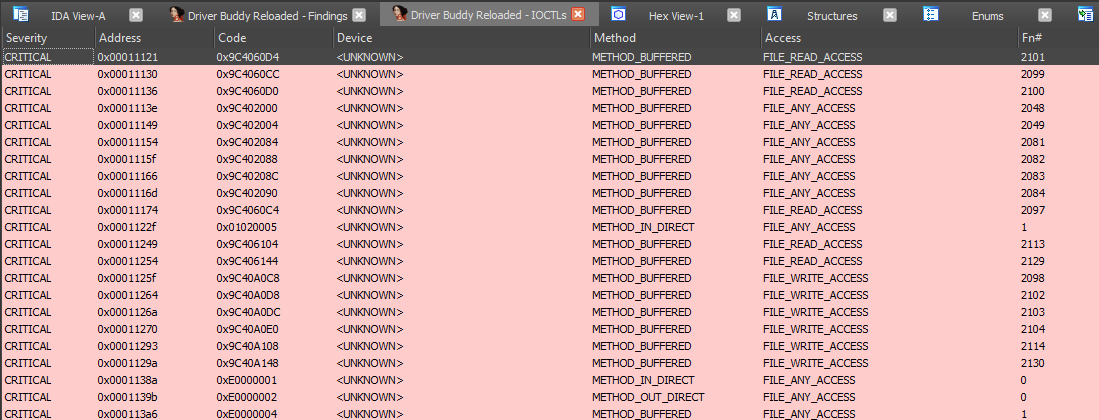
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
binary-analysisdebuggersreverse-engineering+2
4703 months ago
mcpsnoop preview

mcpsnoop

GitHubkerlenton/mcpsnoop

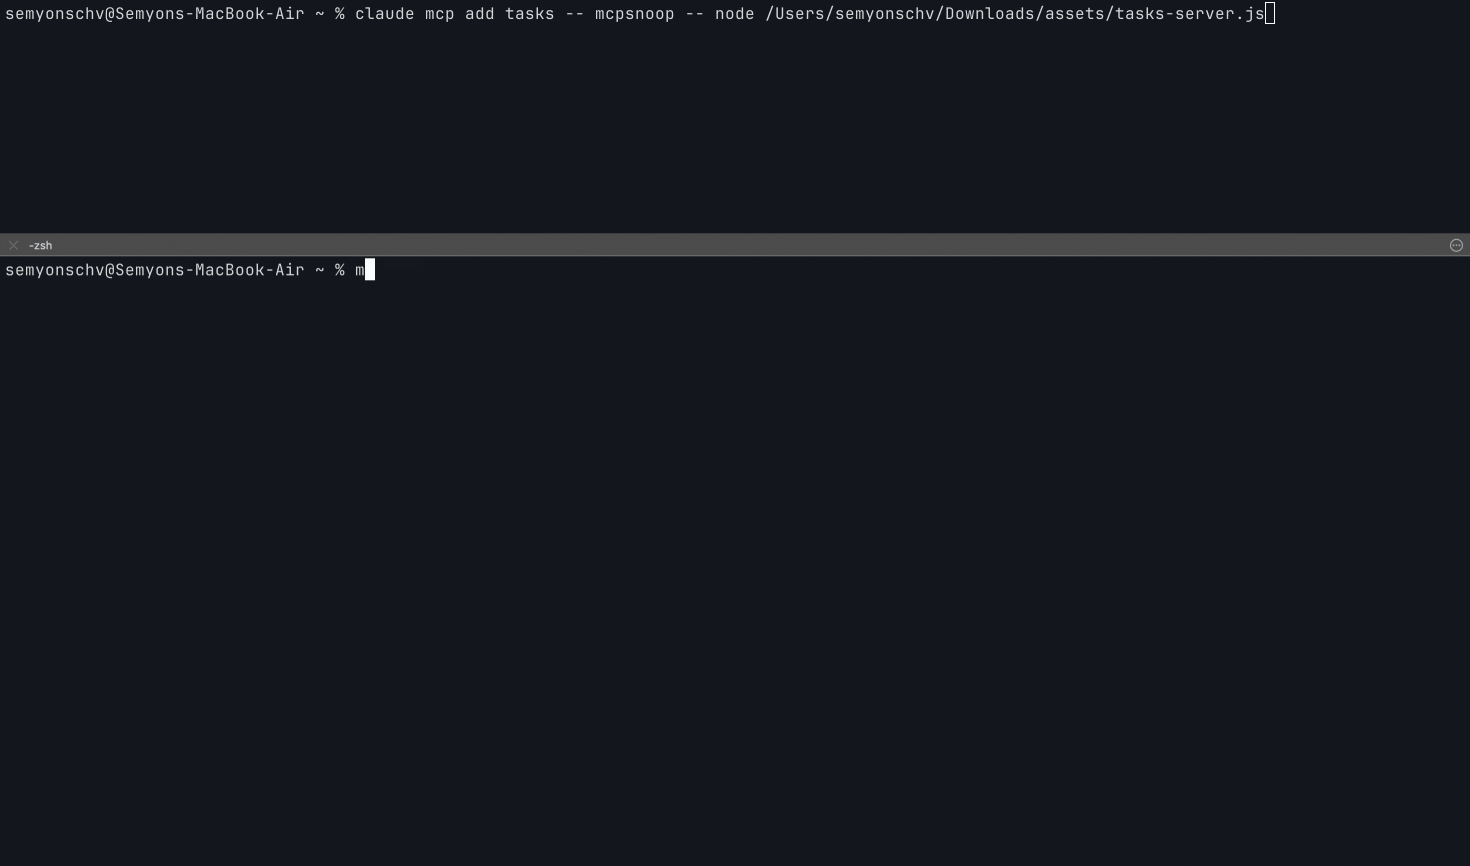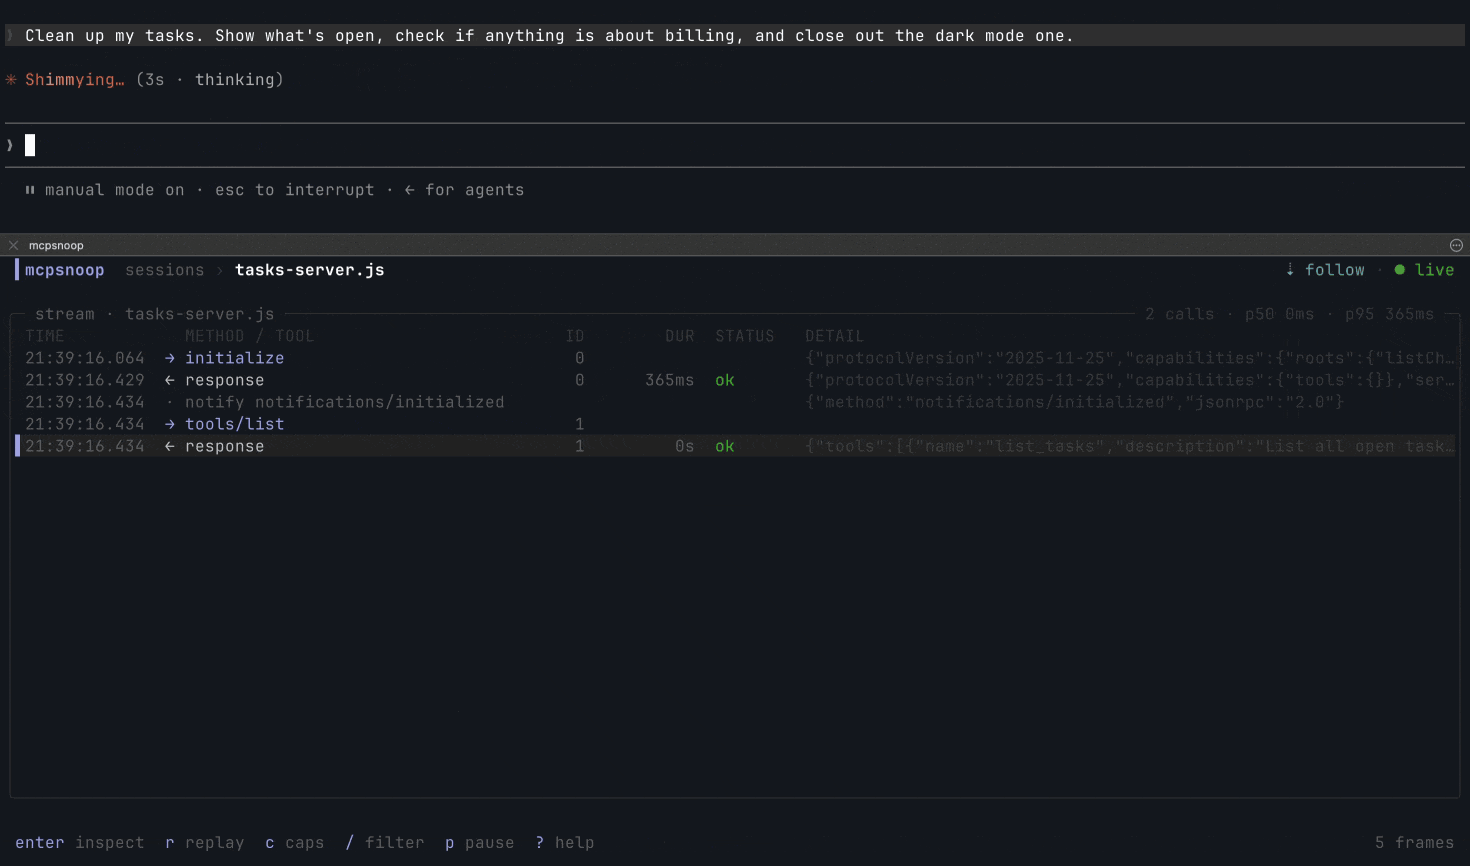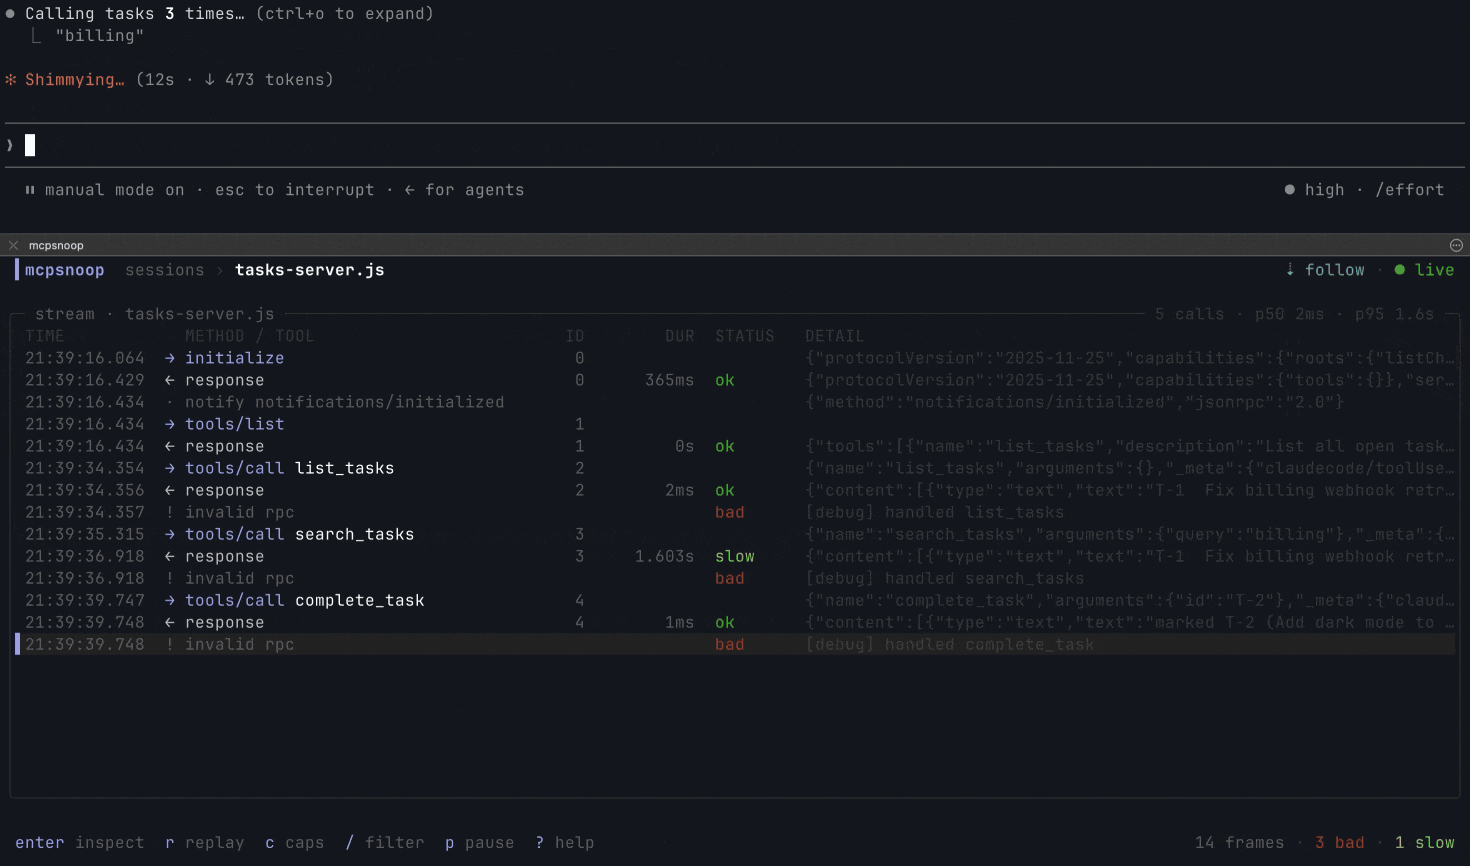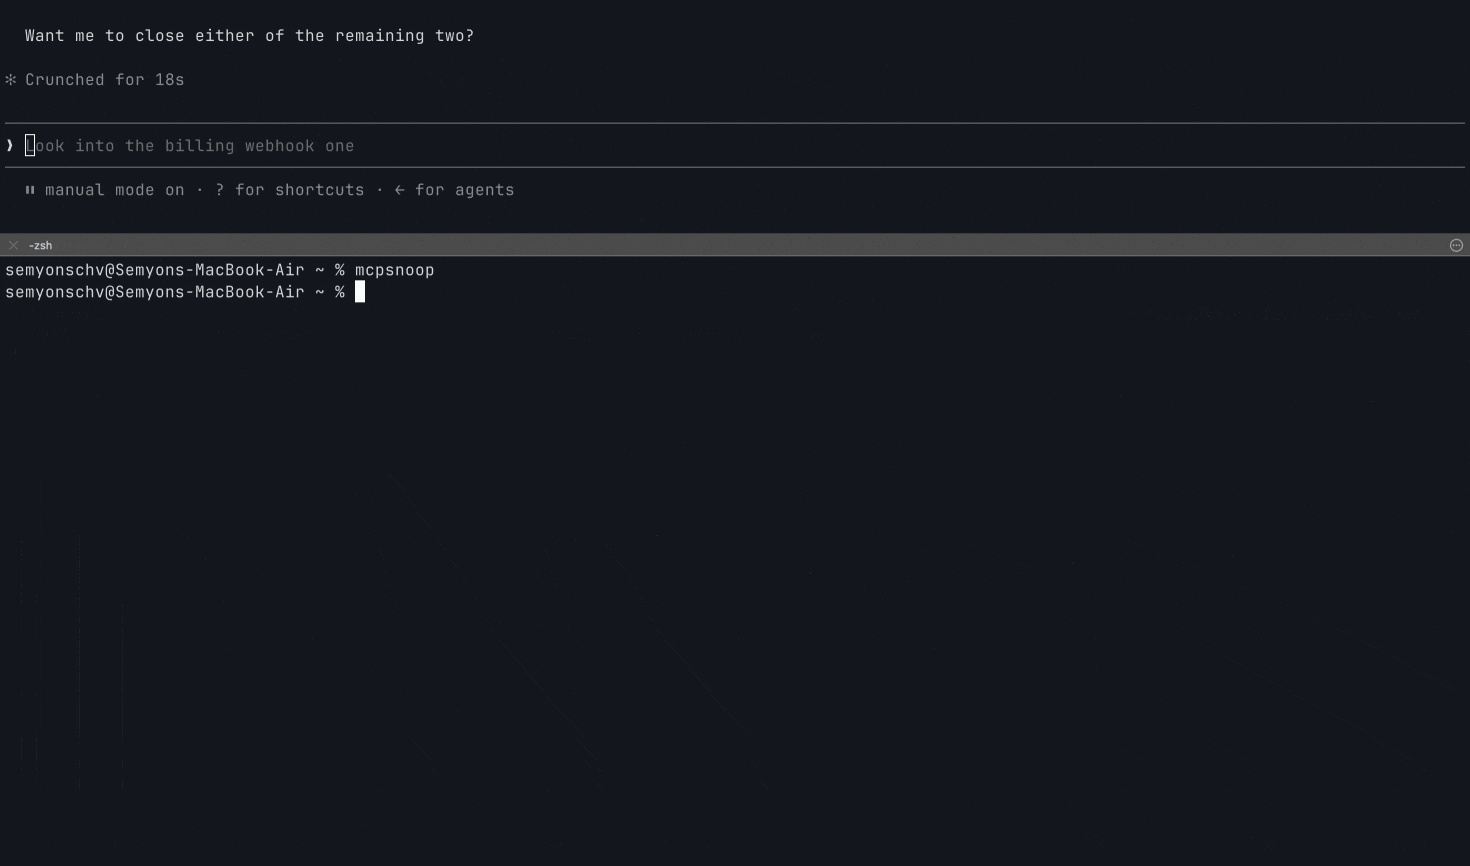
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
api-security-testingdebuggersdynamic-analysis-sandboxing+5
3611 day ago
ttddbg preview

ttddbg

GitHubairbus-cert/ttddbg

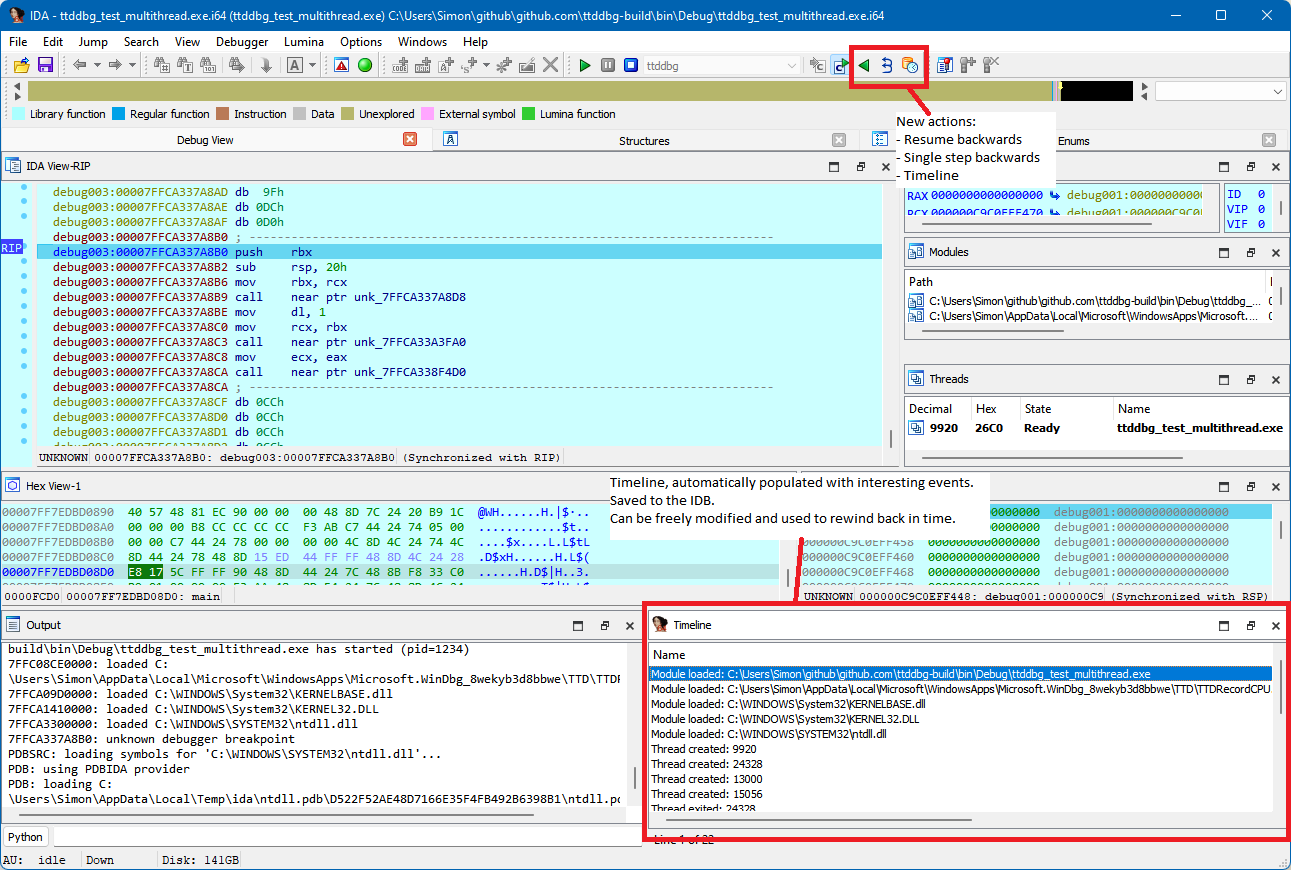
Time Travel Debugging IDA plugin
binary-analysisdebuggersdynamic-code-analysis+1
5952 years ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

debuggersdynamic-analysis-sandboxingforensics+1
2485 years ago
Previous123Next