

delve
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
code-analysisdebuggersdynamic-code-analysis+1
24.9k
go-delve/delveSource-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
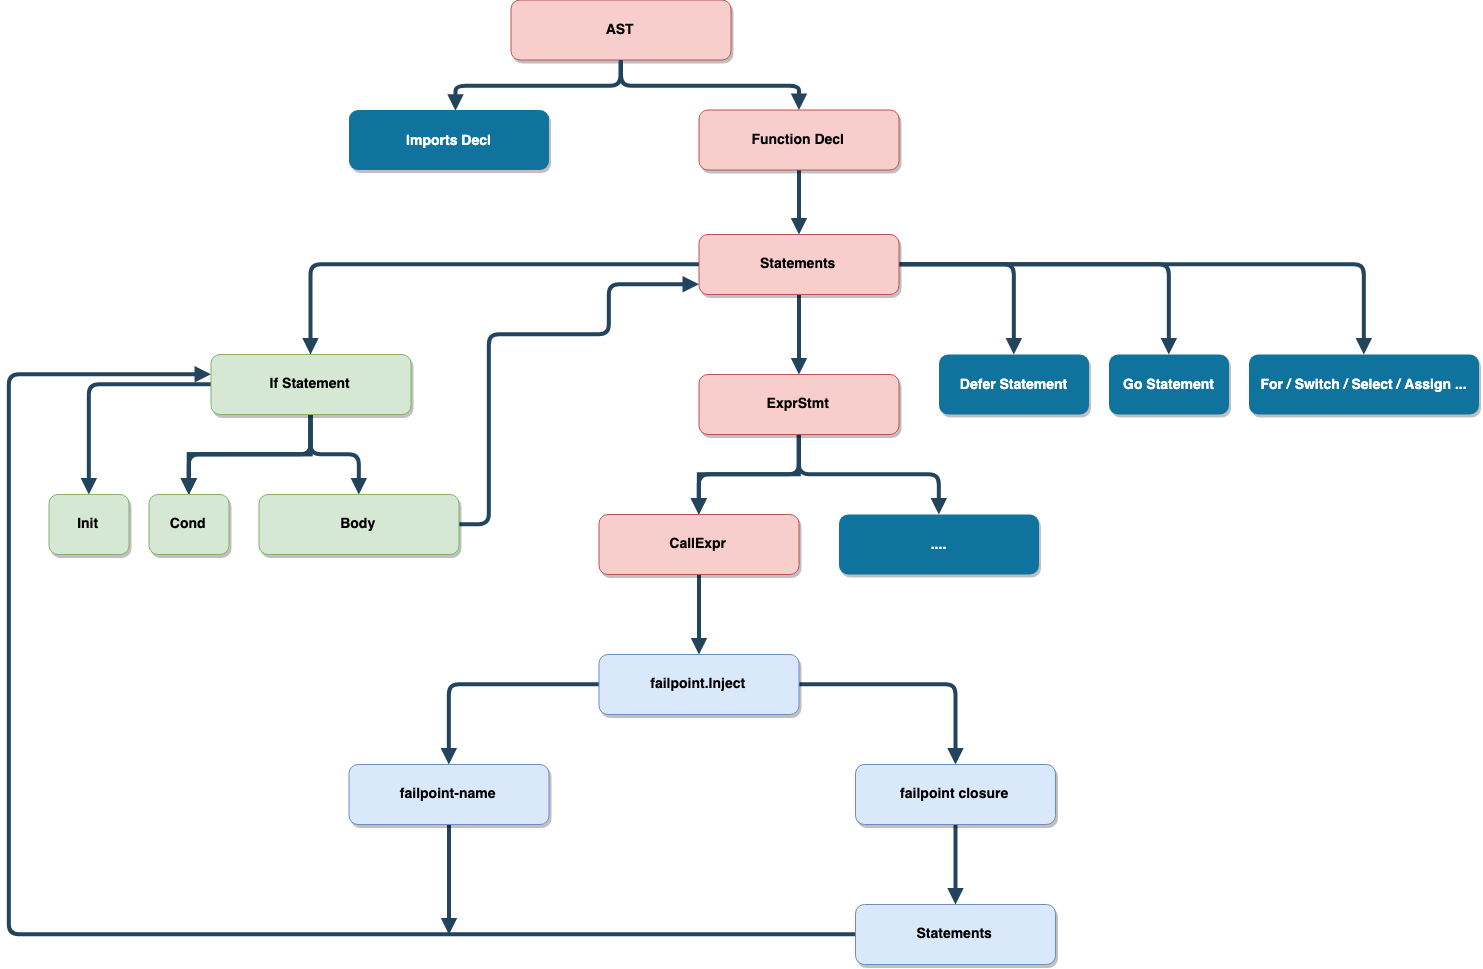 pingcap/failpoint
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 sentinelabs/alphagolang
IDApython Scripts for Analyzing Golang Binaries
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 zardus/ctf-tools
Some setup scripts for security research tools.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 lauriewired/ghidramcp
MCP Server for Ghidra
