
drmemory
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
dynamorio/drmemoryMemory Debugger for Windows, Linux, Mac, and Android
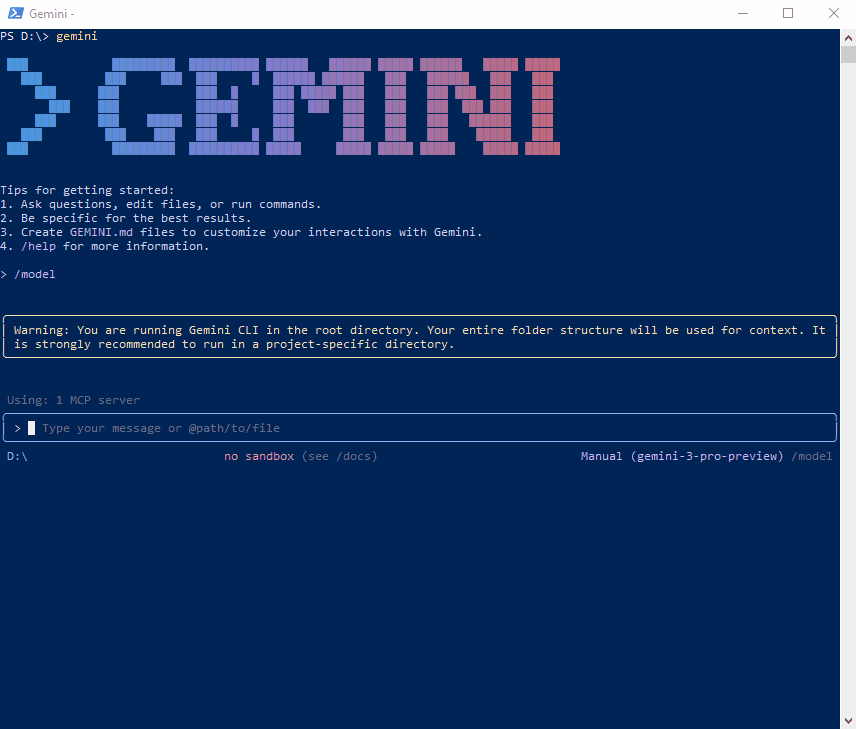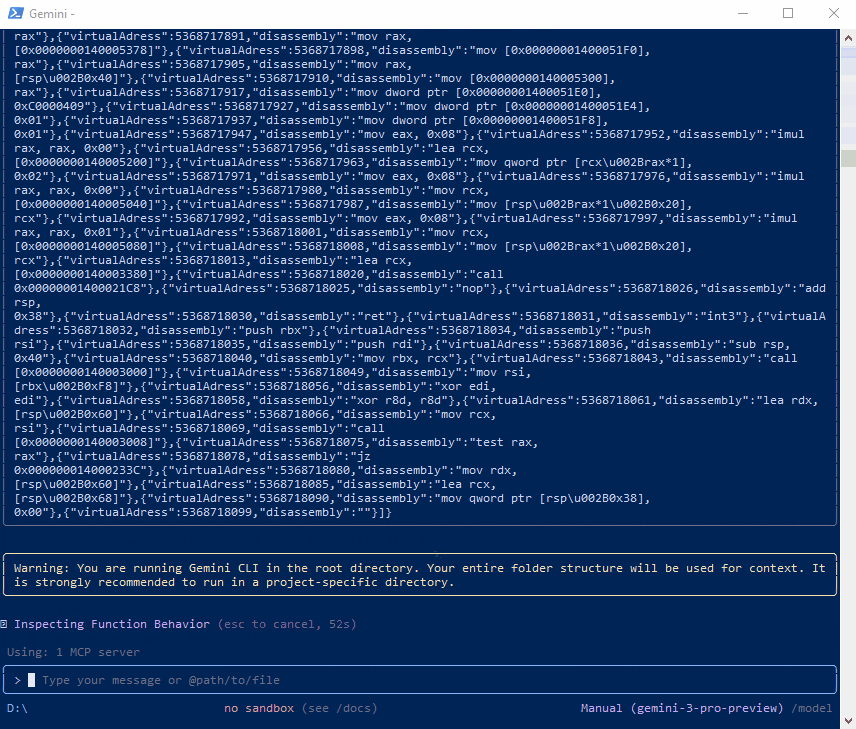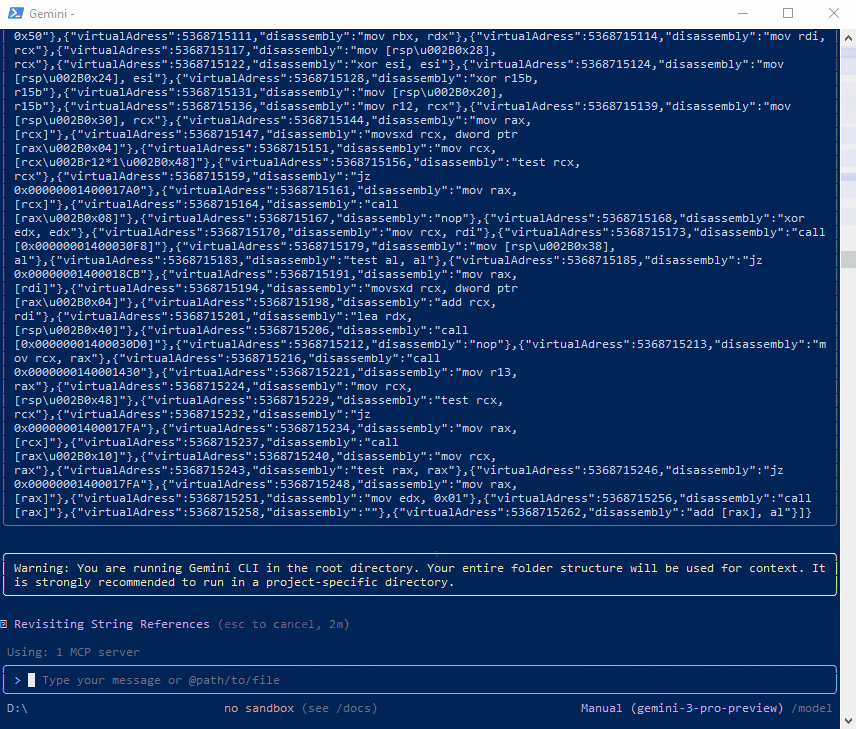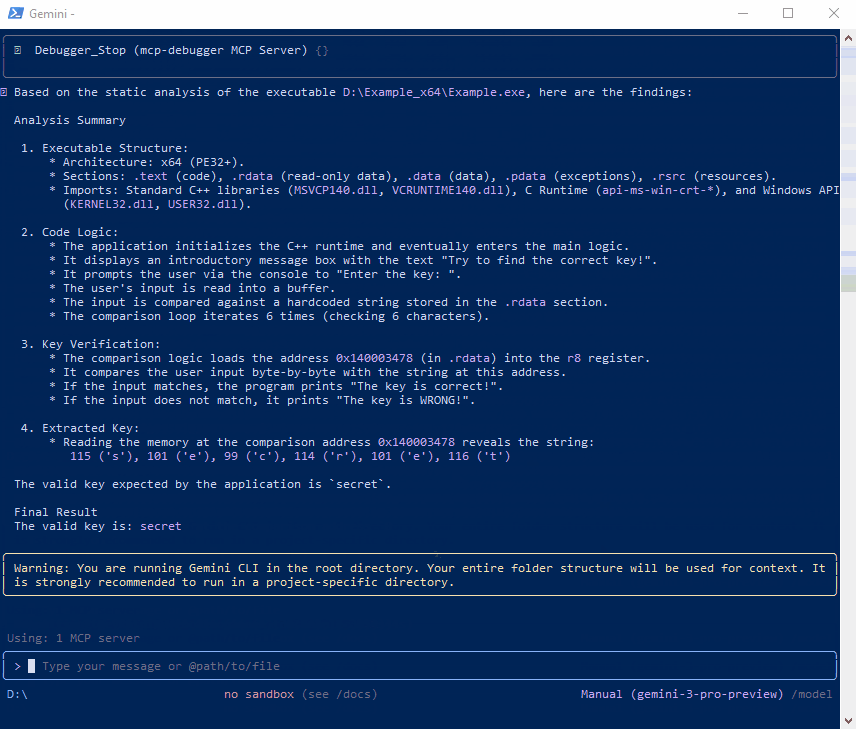 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 darthton/blackbone
Windows memory hacking library
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 amossys/memitm
Tool to make in memory man in the middle
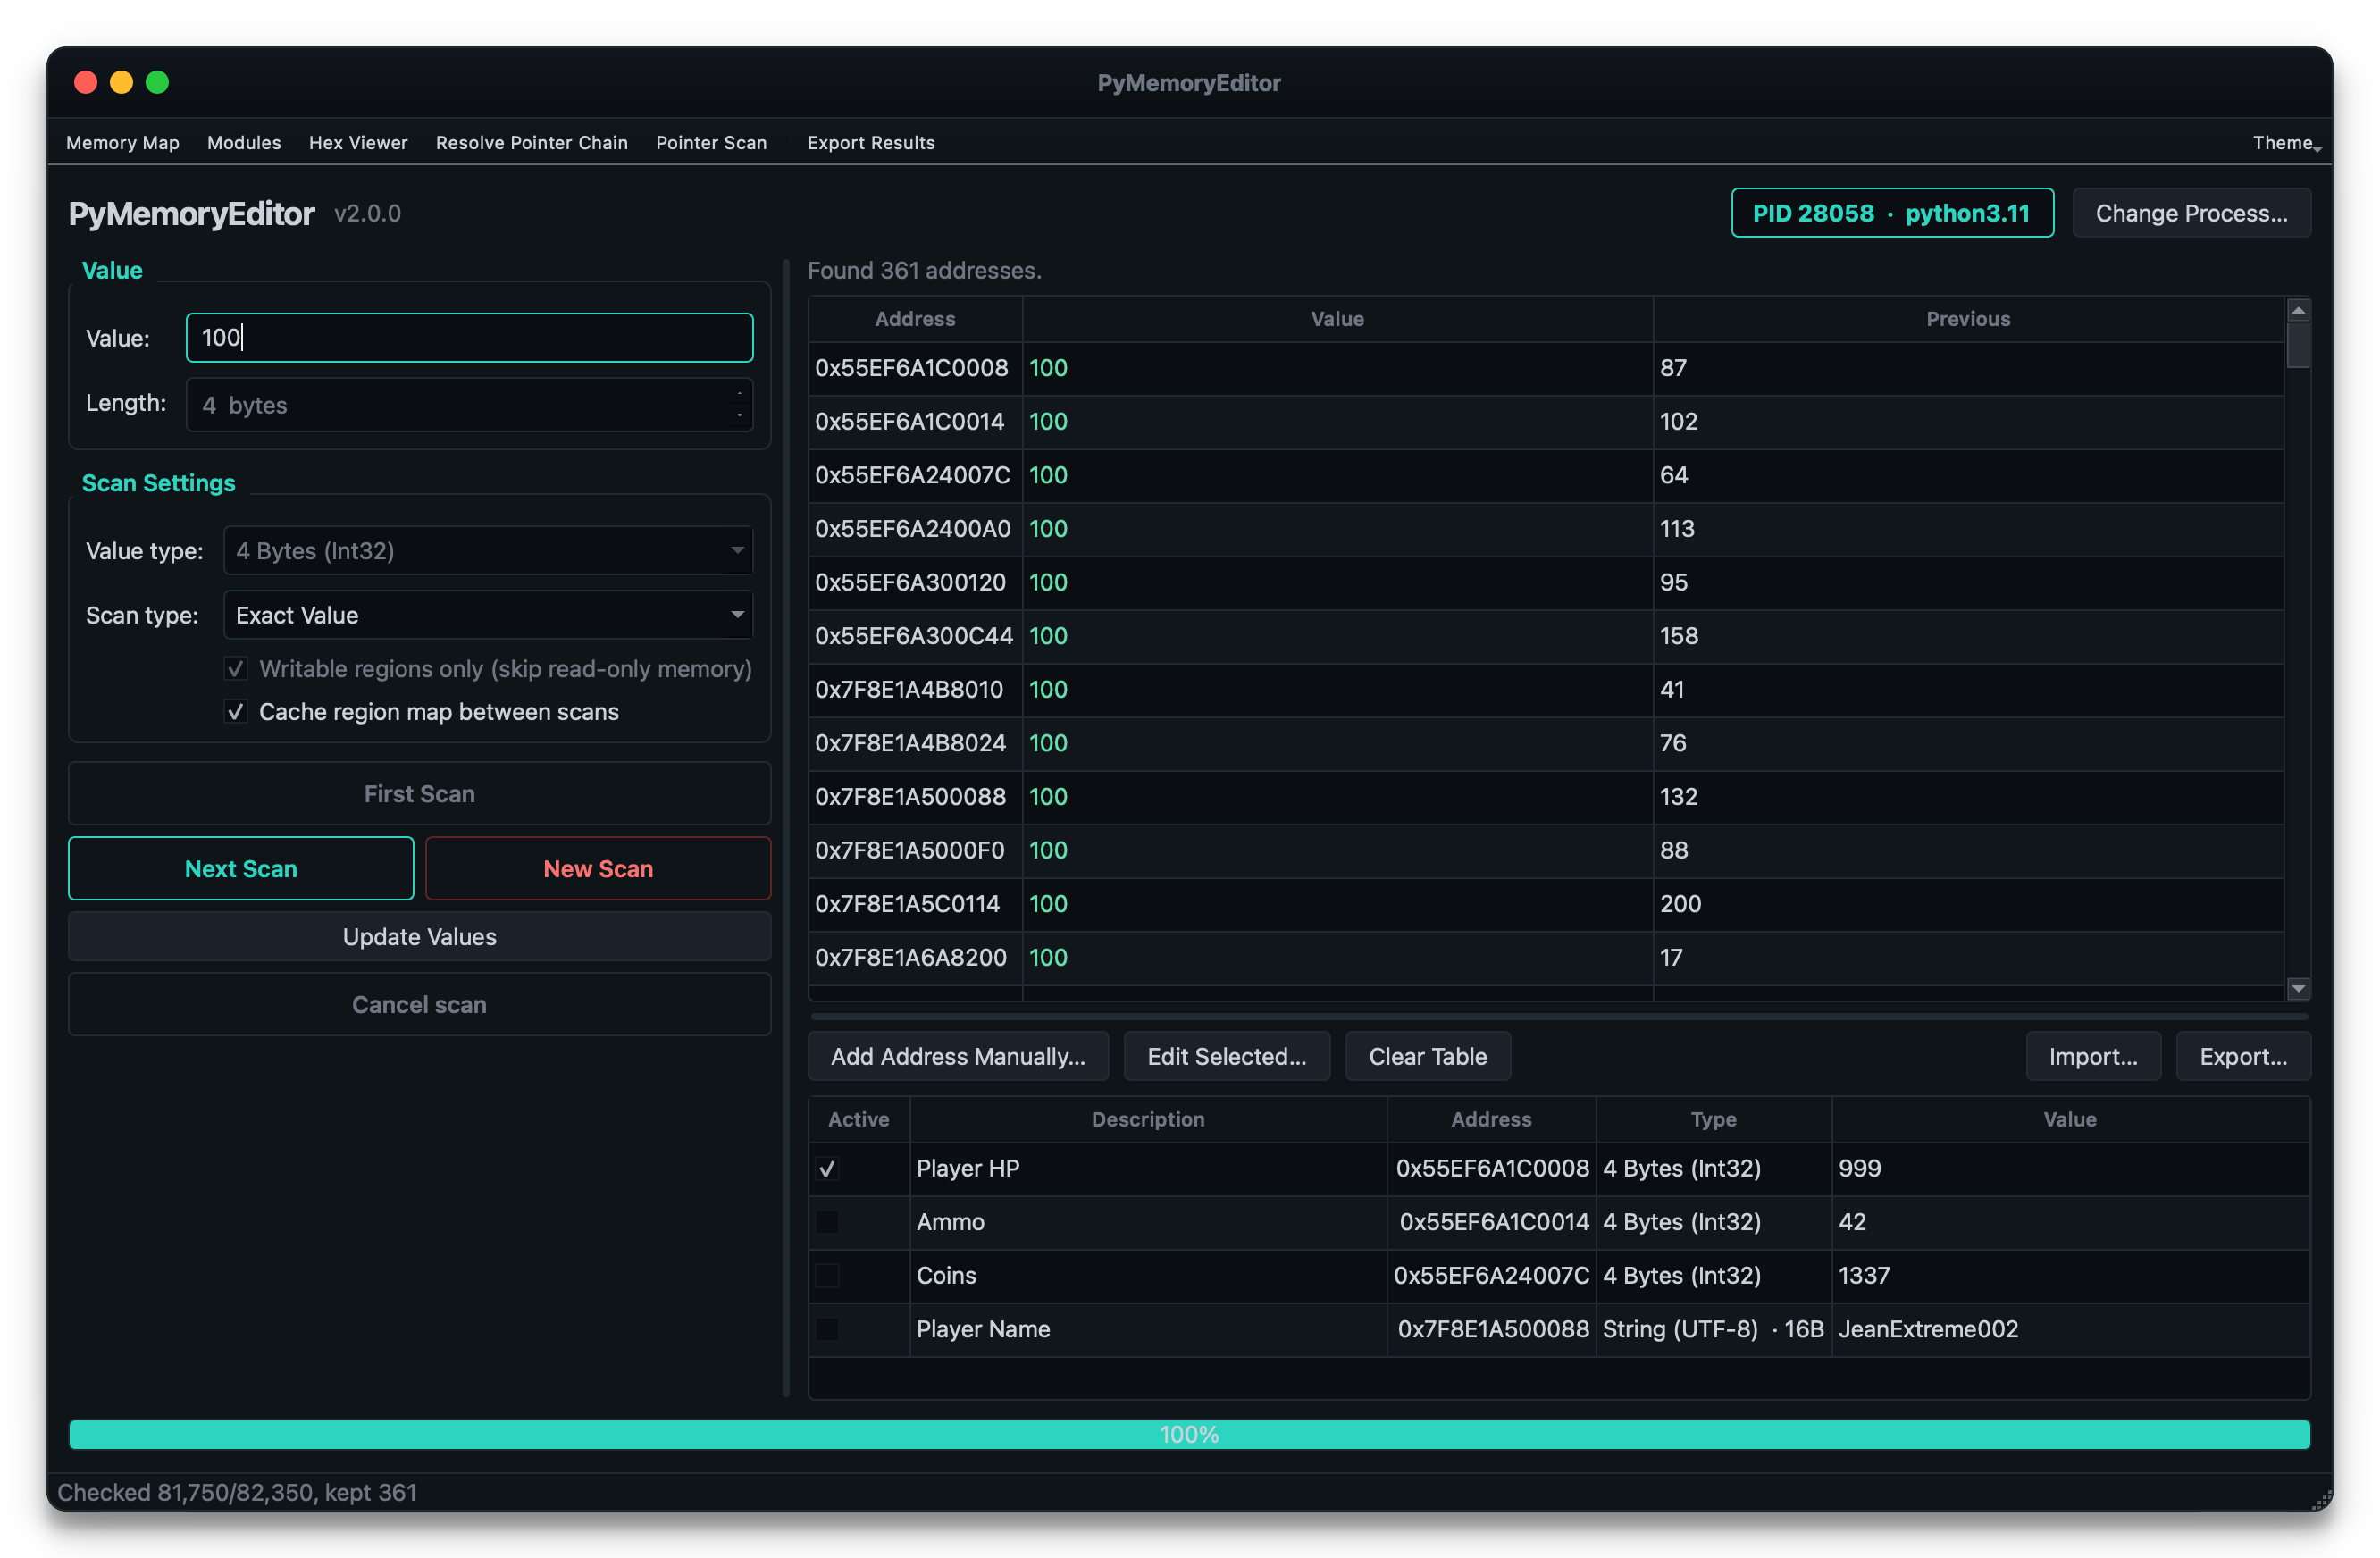 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 nickcano/xenoscan
Open source memory scanner written in C++
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
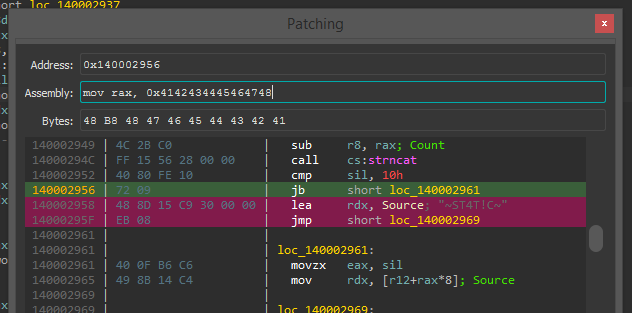 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro