
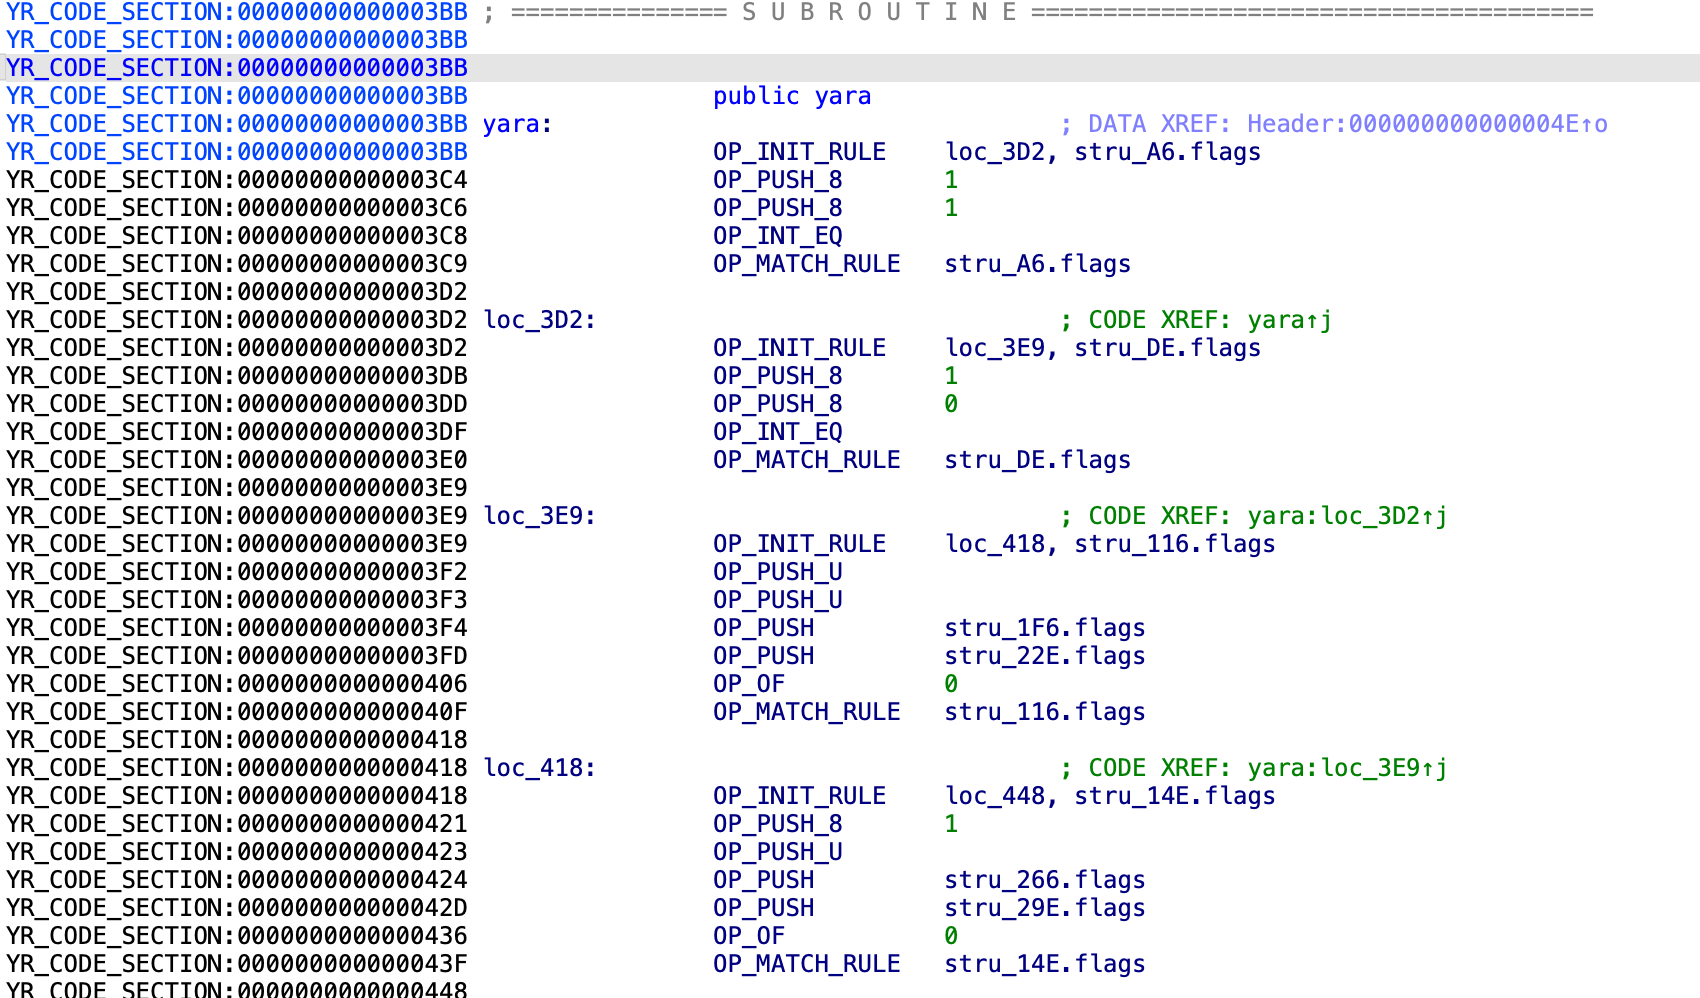
YaraVM
 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
binary-analysisdebuggersmalware-analysis+2
milankovo/yaravmThis repository contains an IDA processor for loading and disassembling compiled yara rules.
 badmonkey7/cve-2021-34730
Cisco RV110w UPnP stack overflow
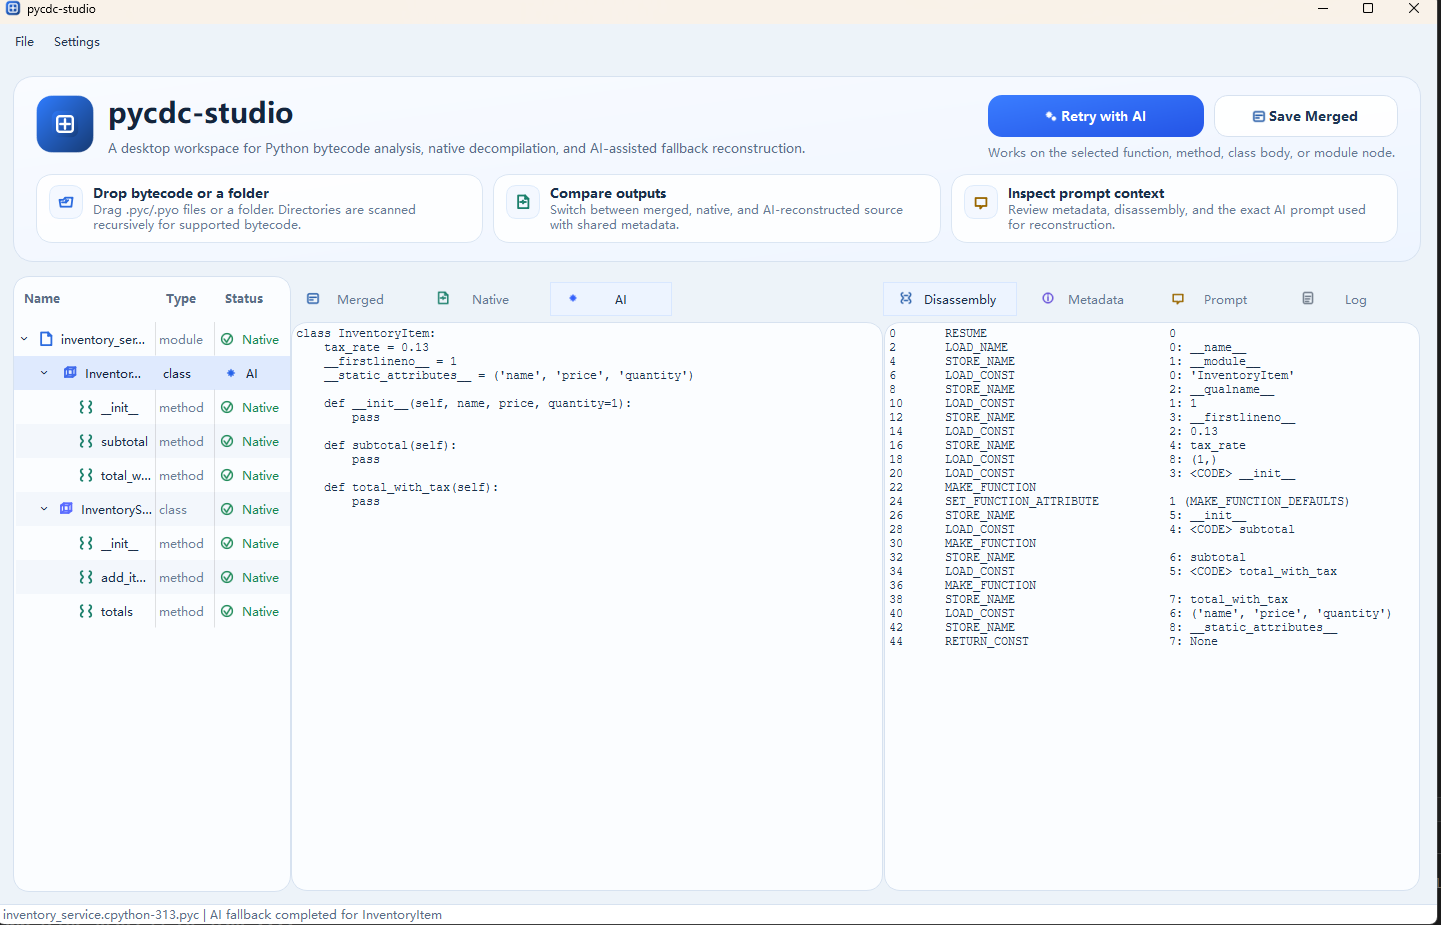 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 saint0x/fzy
a systems programming language prioritizing verifiable correctness, determinism, and performance
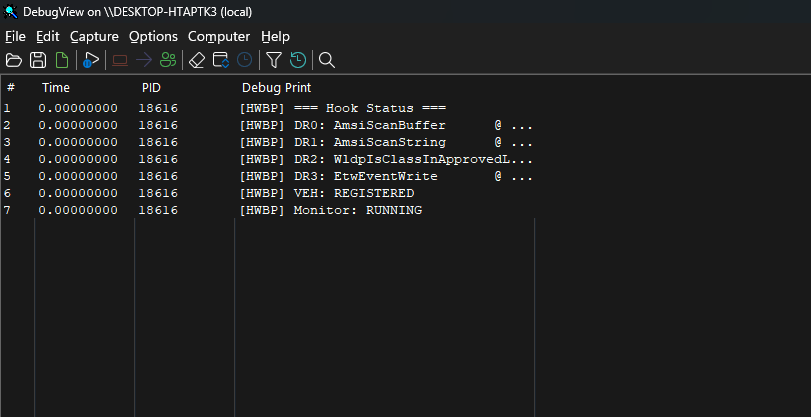 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
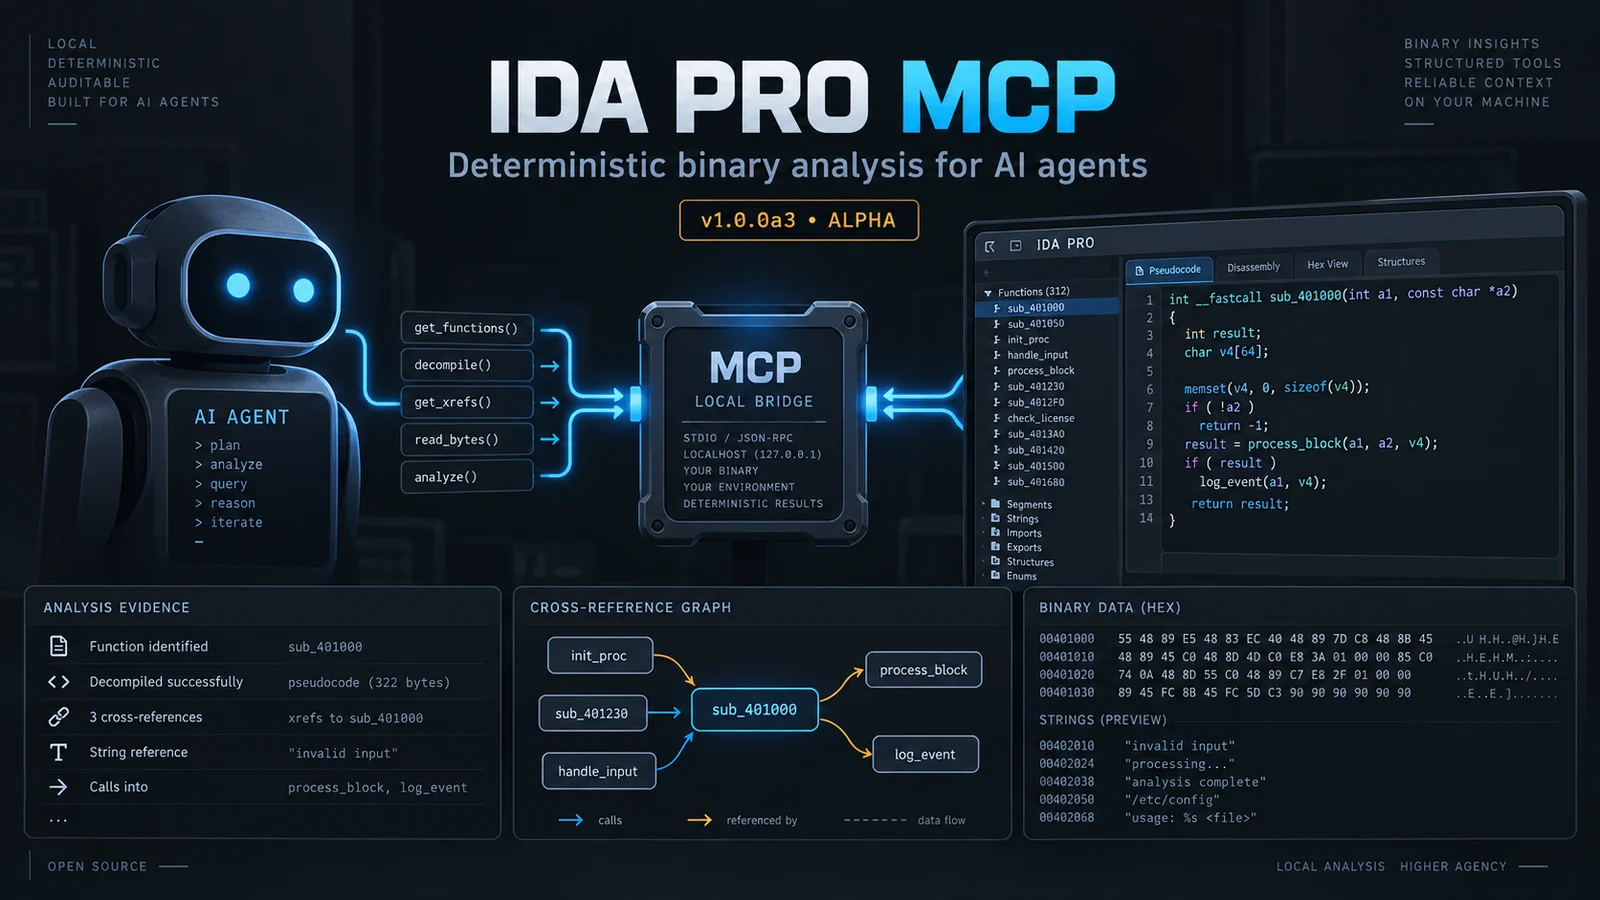 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
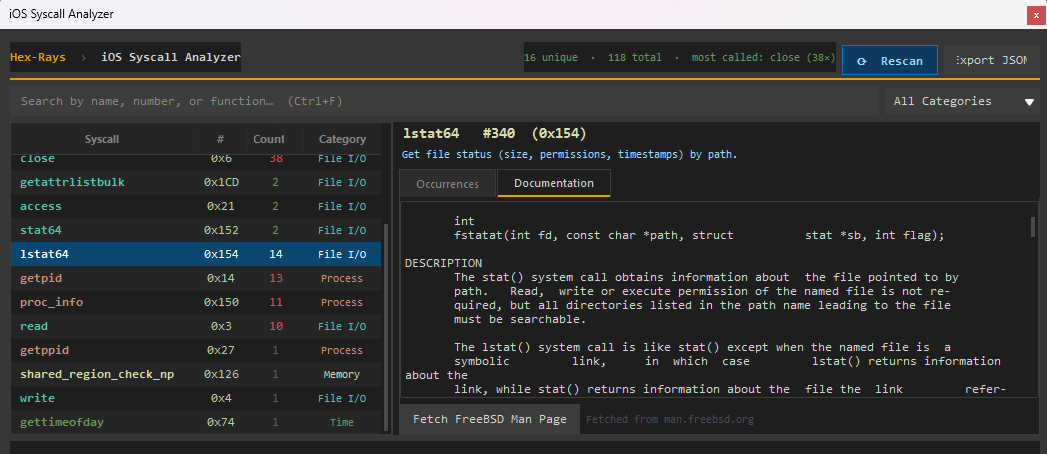 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…