

Driver-PiDqSerializationWrite-Example
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
gmh5225/driver-pidqserializationwrite-exampleHow to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 gmh5225/kernelmode-driver
Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
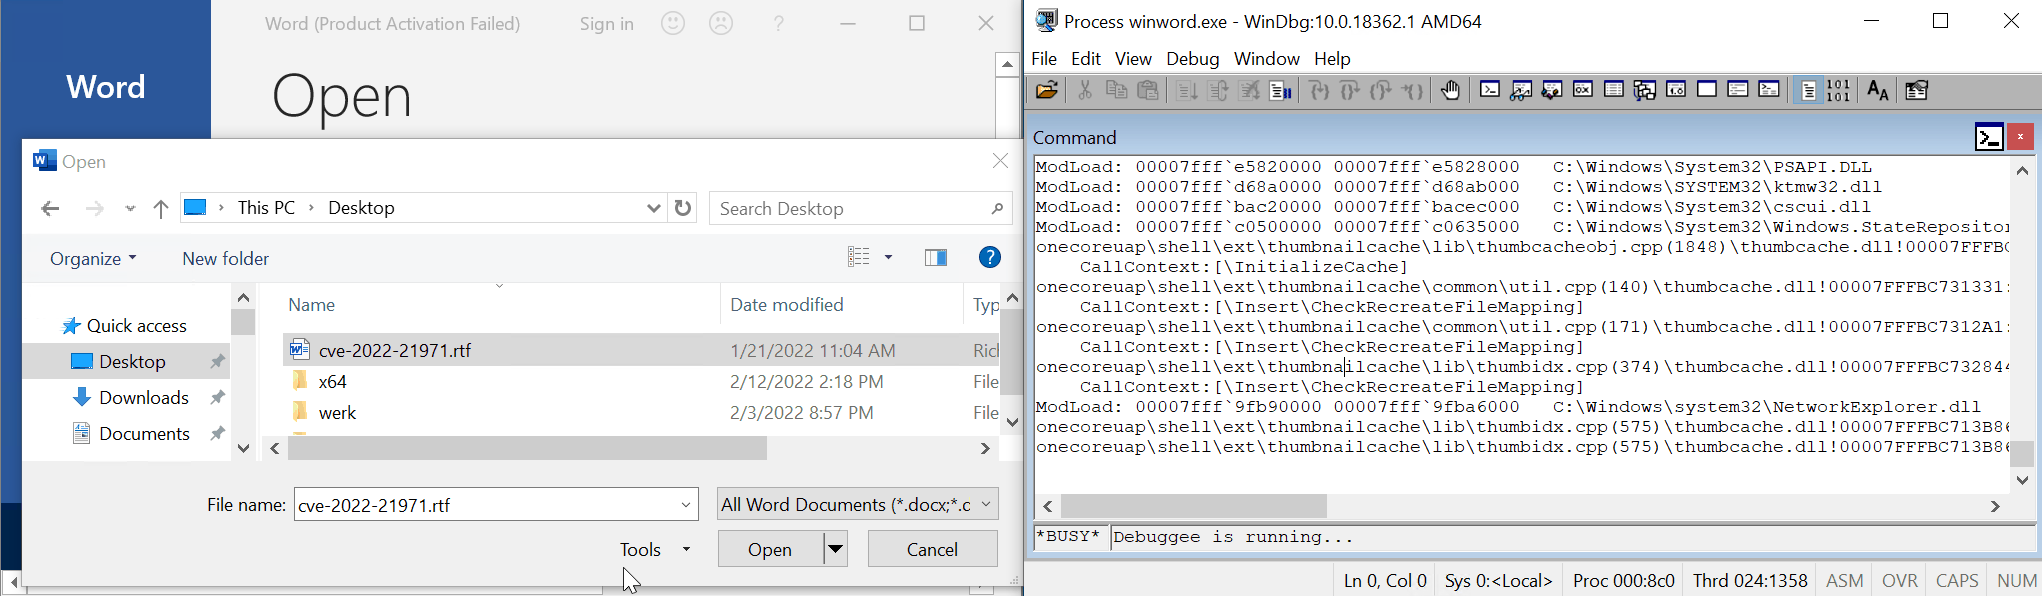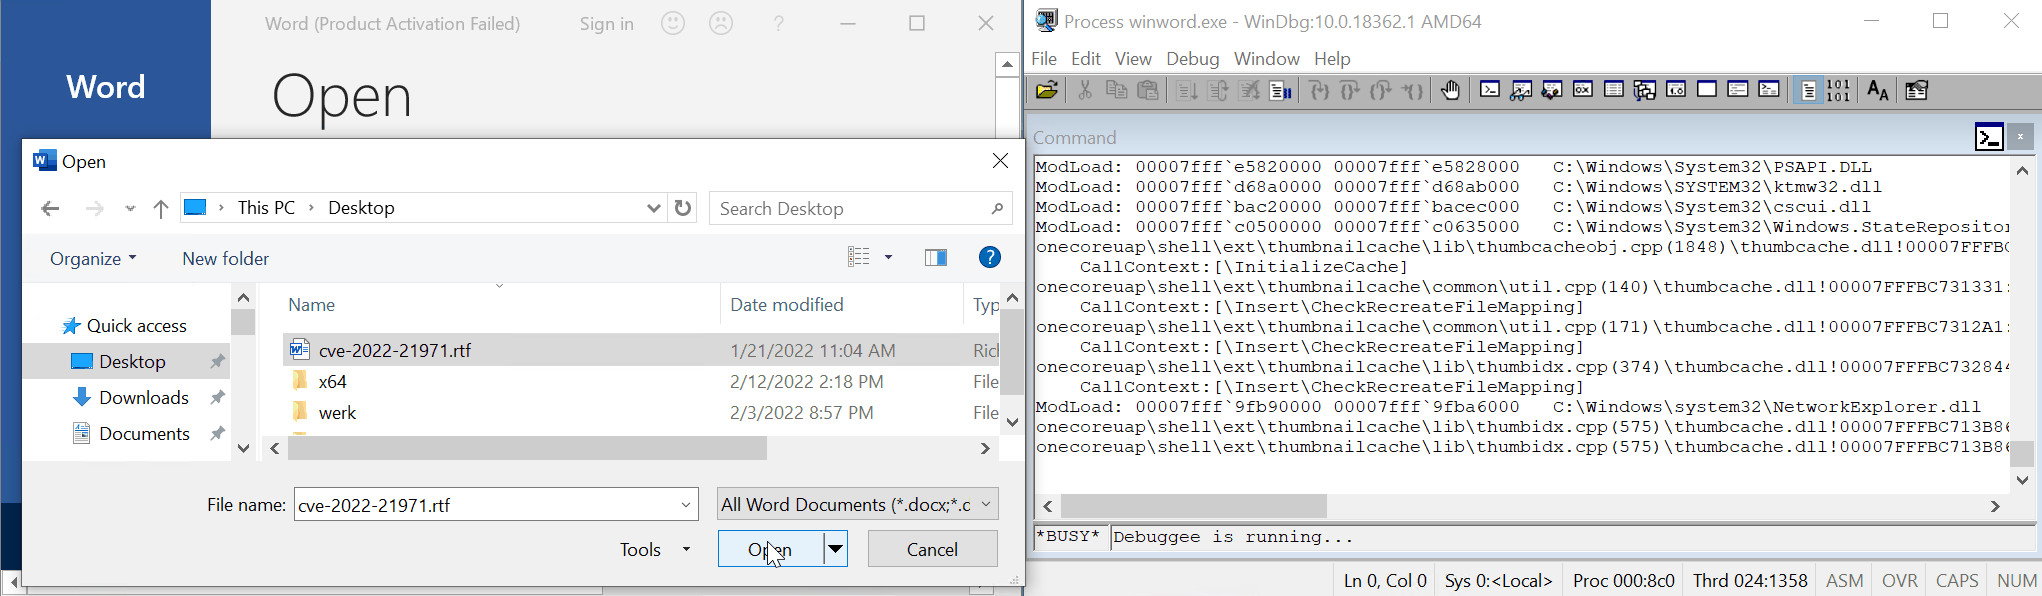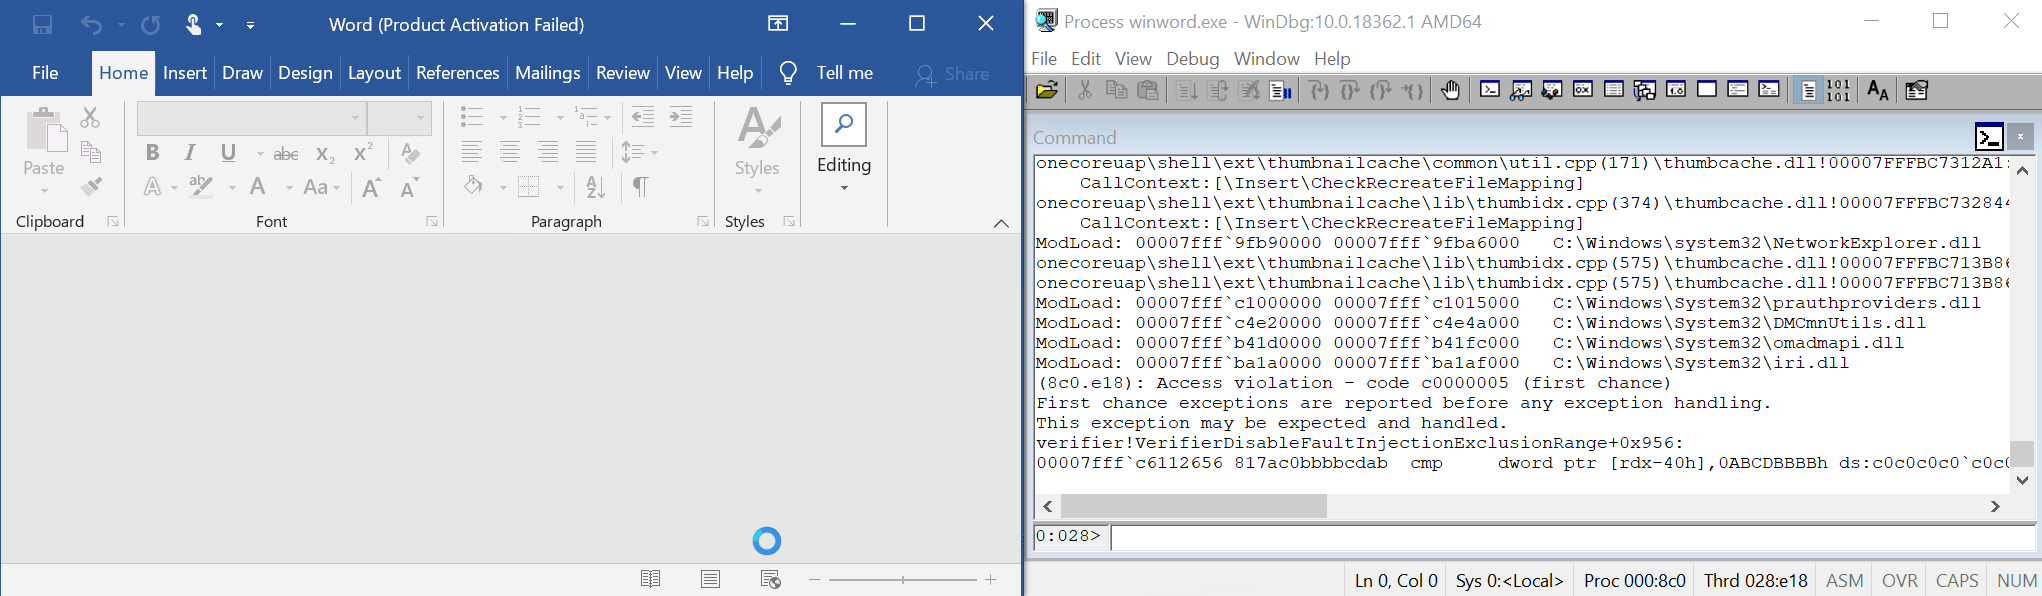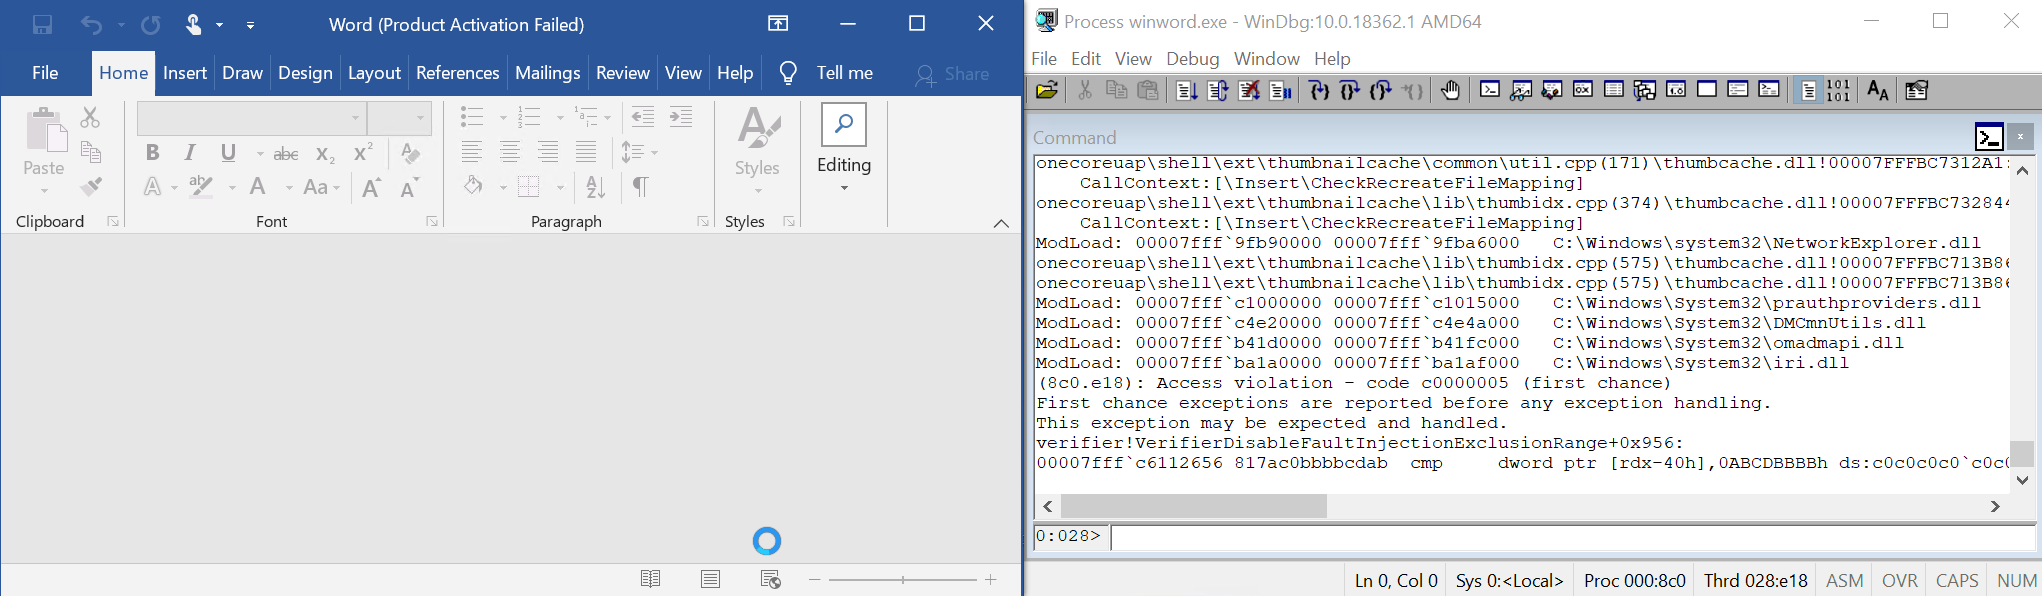 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
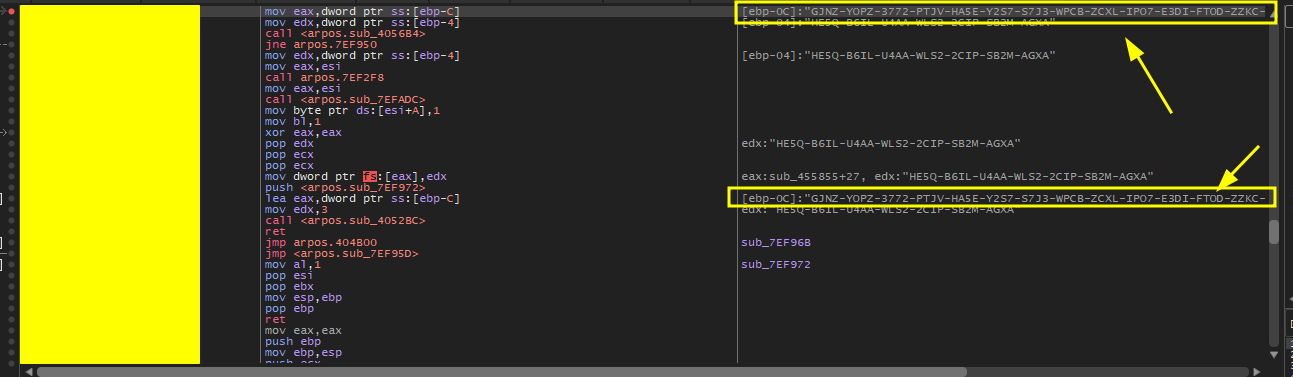 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
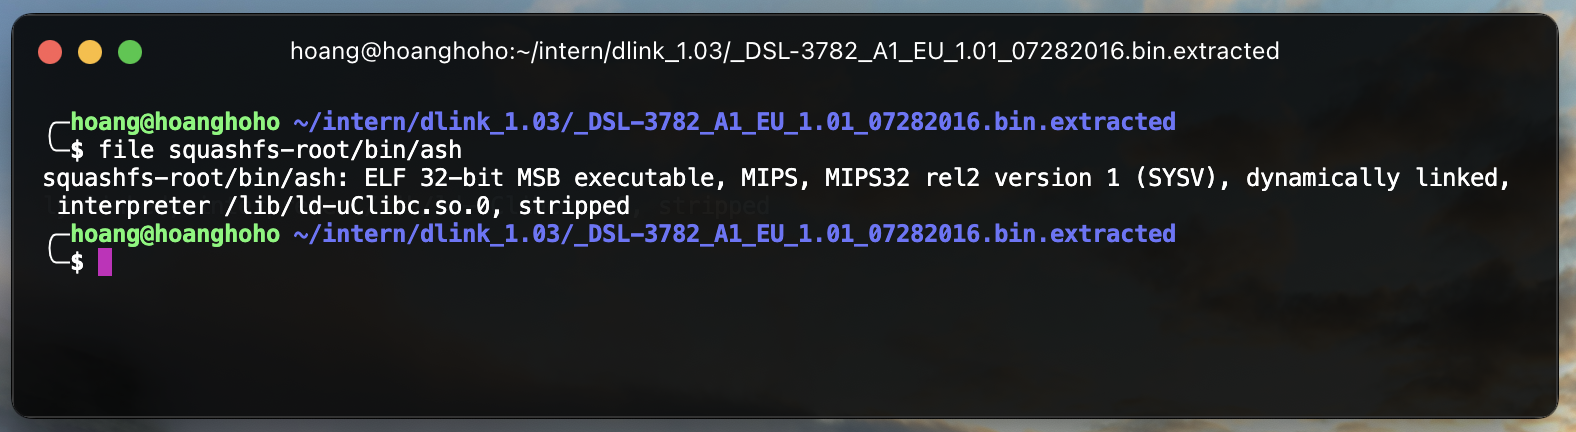 hoangrealer/cve-2023-27216
Newbie's approach to firmware hacking
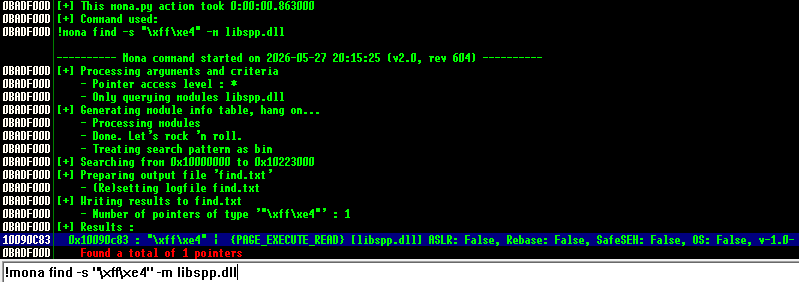 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
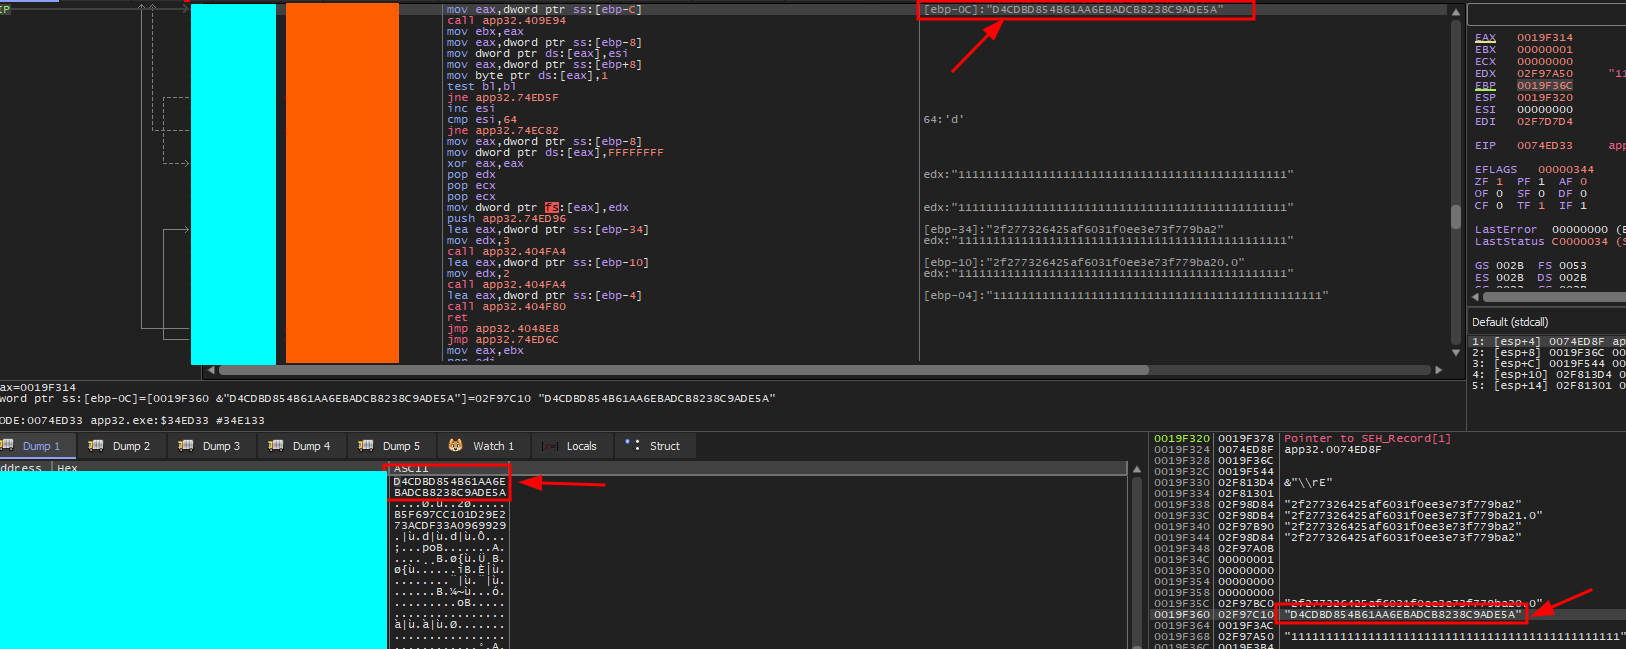 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…
 halcy0nic/cve-2023-40294-and-cve-2023-40295
Proof of concept for CVE-2023-40294 and CVE-2023-40295
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 ngtuonghung/cve-2022-27666
Heap buffer overflow exploit for CVE-2022-27666 in Linux kernel IPsec ESP6 implementation. Includes kernel build, debug setup with GDB stub, and…
 business1sg00d/cve-2023-25136
Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 smarttfoxx/cve-2025-65320
Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…