

rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
3.9k
rizinorg/rizinUNIX-like reverse engineering framework and command-line toolset.
 0xnobody/vmpdump
A dynamic VMP dumper and import fixer, powered by VTIL.
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 libtero/idaguides
indent guides plugin for hex-rays decompiler
 dsfau/cve-2018-1000199
Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…
 renukaselvar/libunwind_cve-2015-3239
C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
 renukaselvar/libunwind_cve-2015-3239_after
Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.
 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
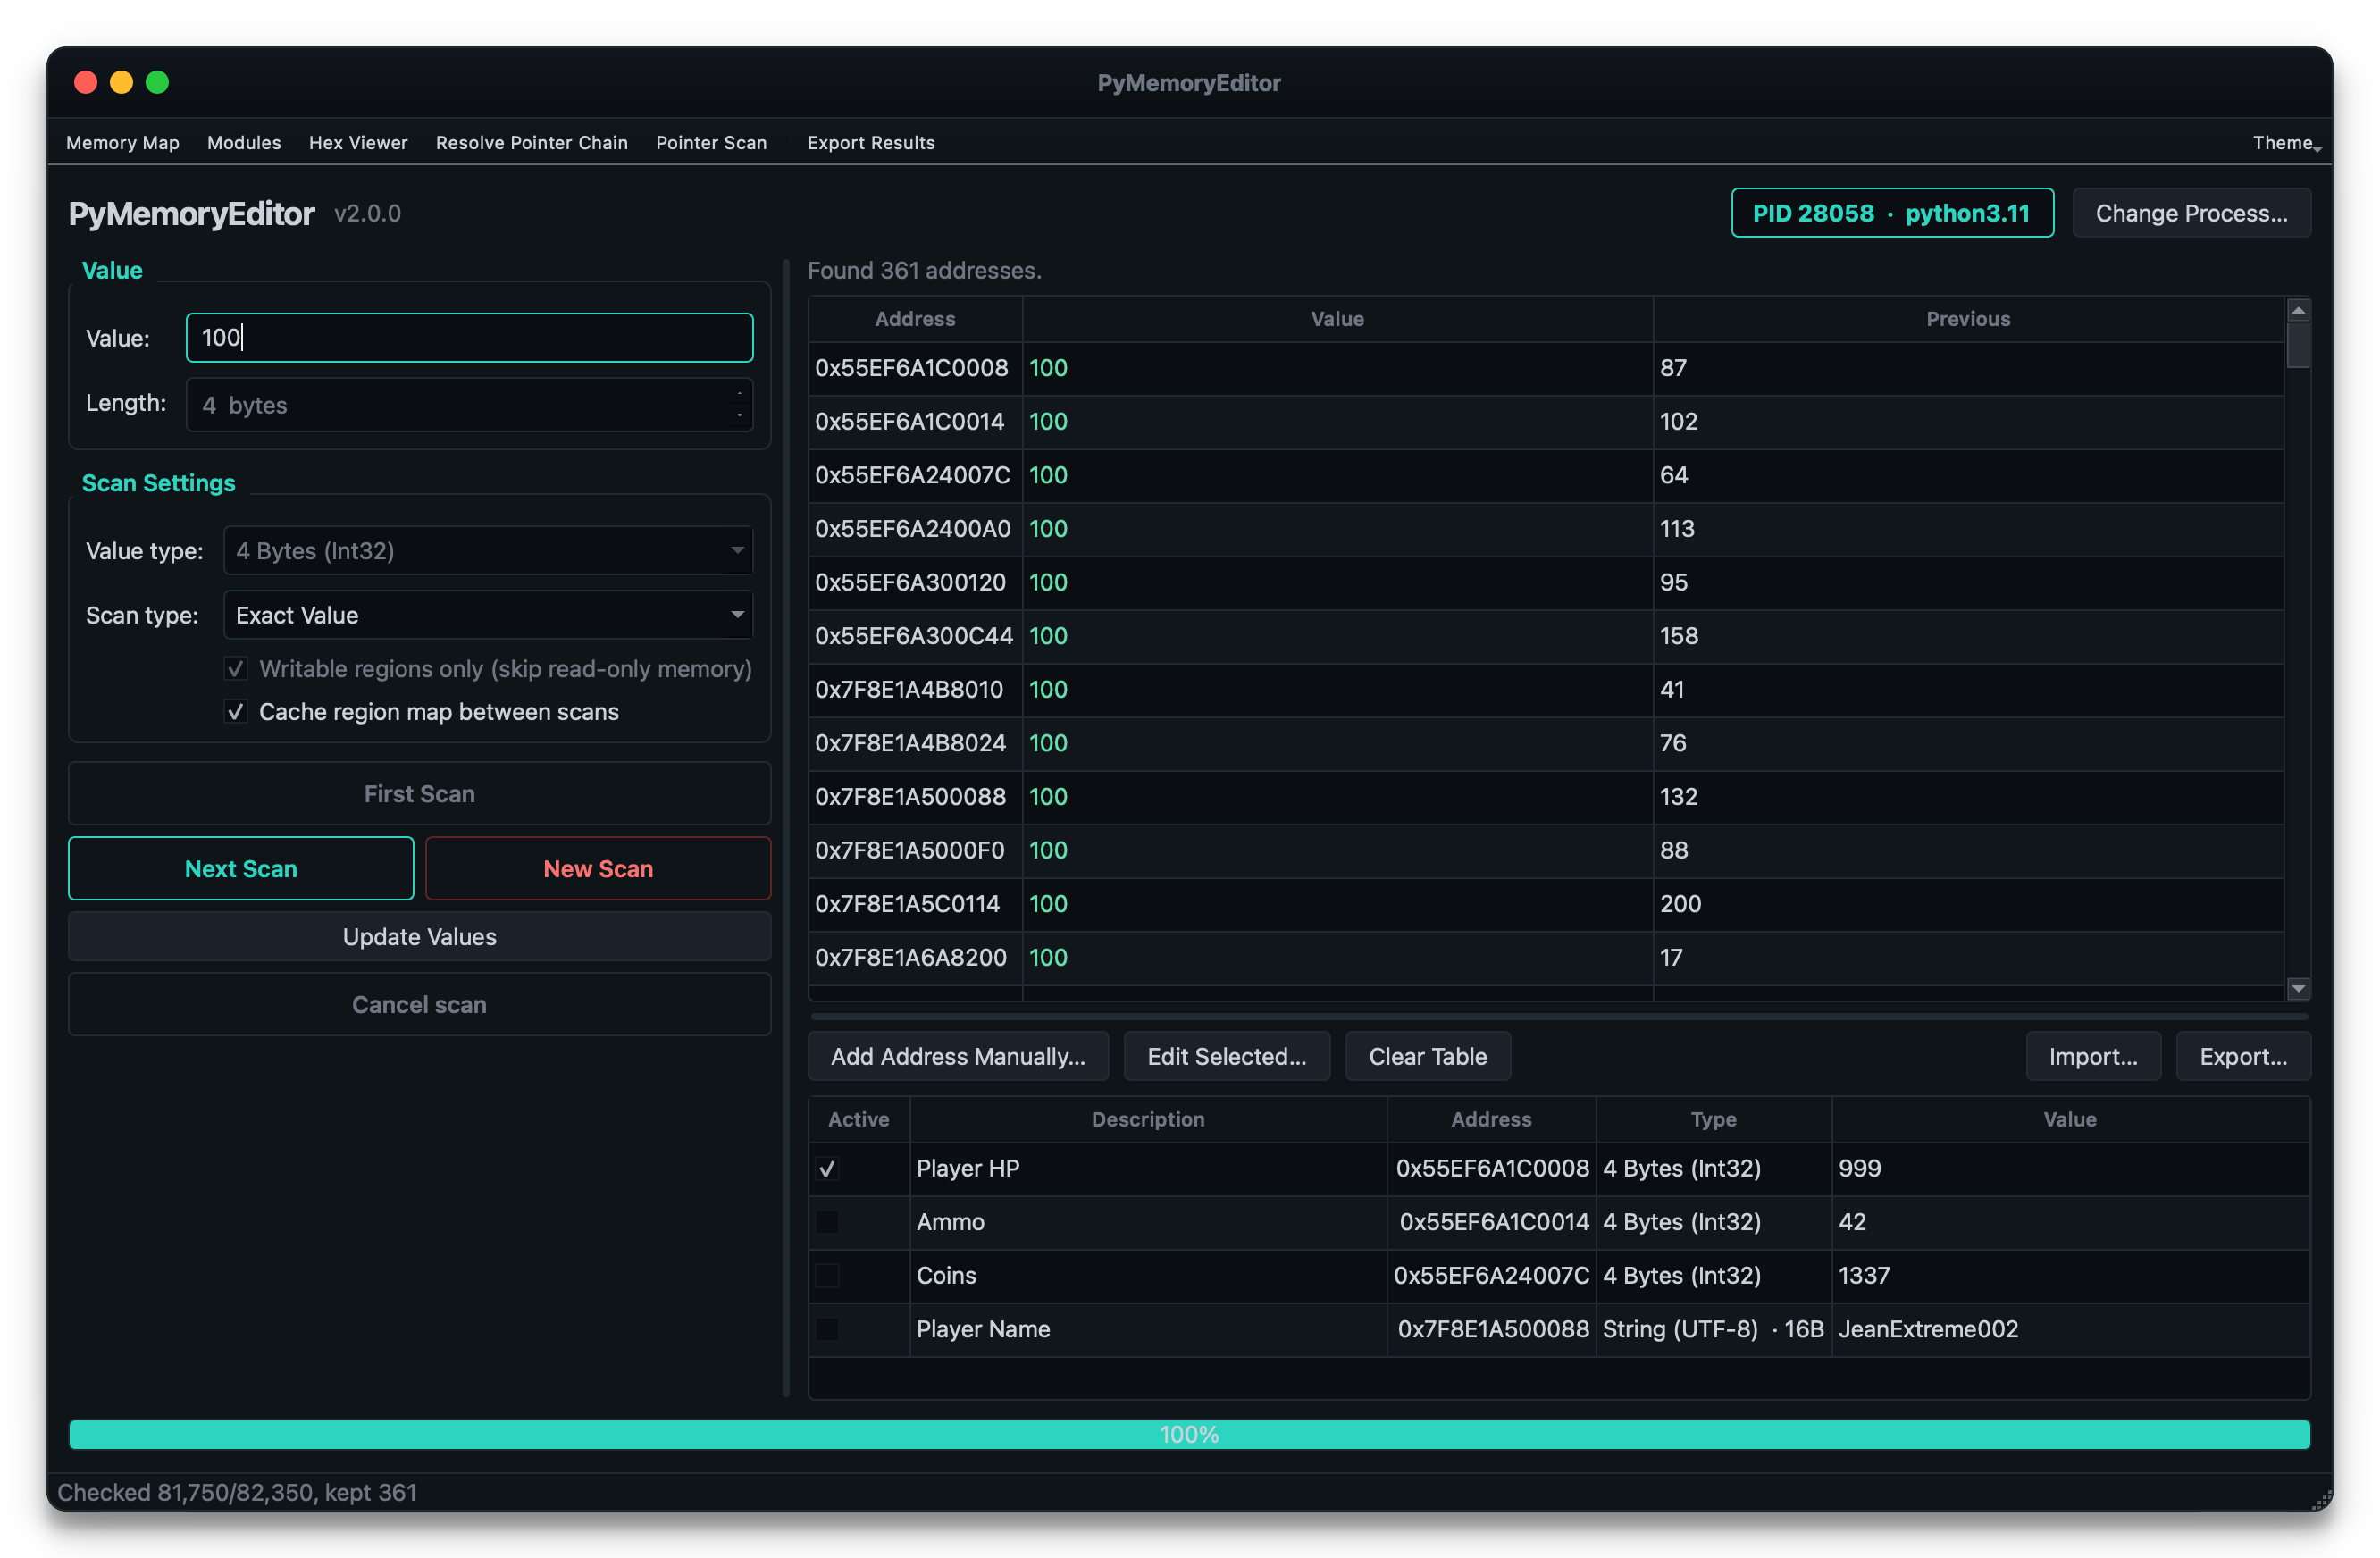 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
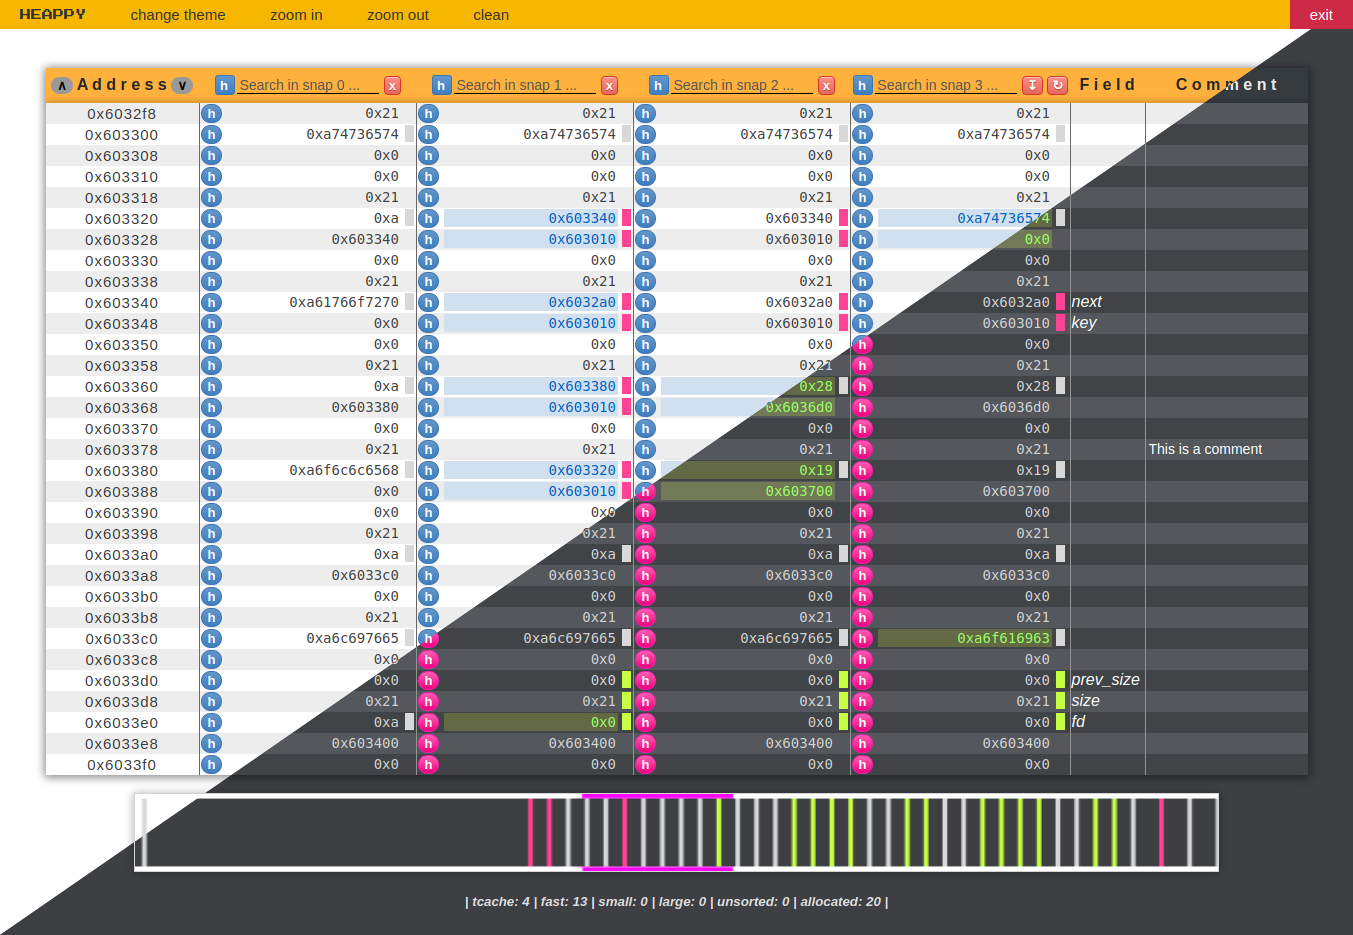 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering