

libunwind_CVE-2015-3239
 renukaselvar/libunwind_cve-2015-3239
C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
binary-analysisdebuggersexploitation+3
renukaselvar/libunwind_cve-2015-3239C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
 renukaselvar/libunwind_cve-2015-3239_after
Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
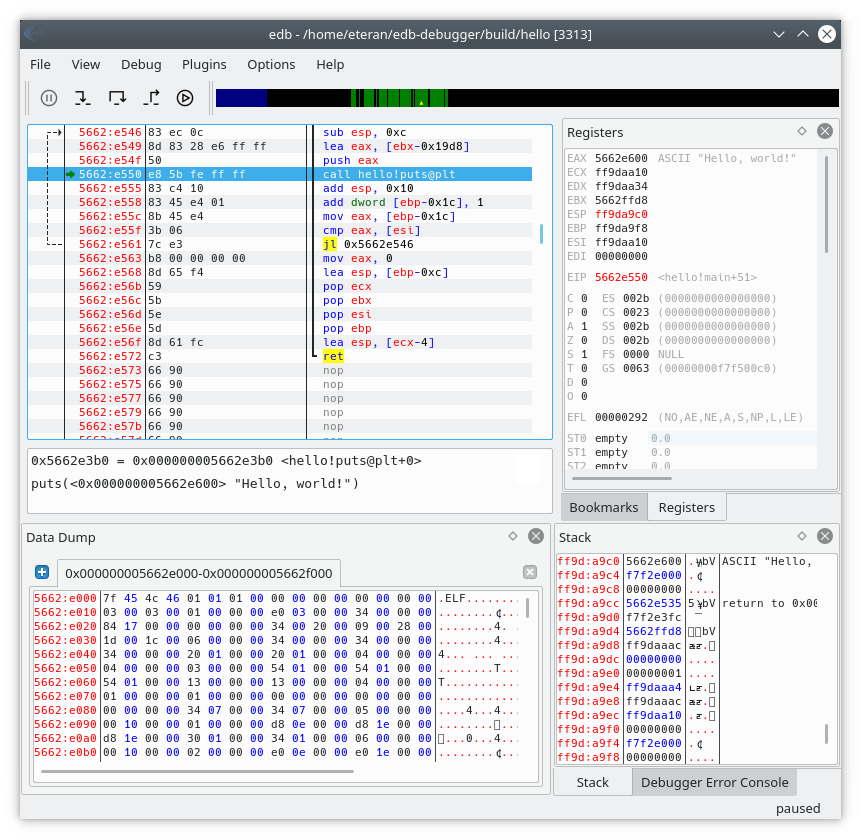 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
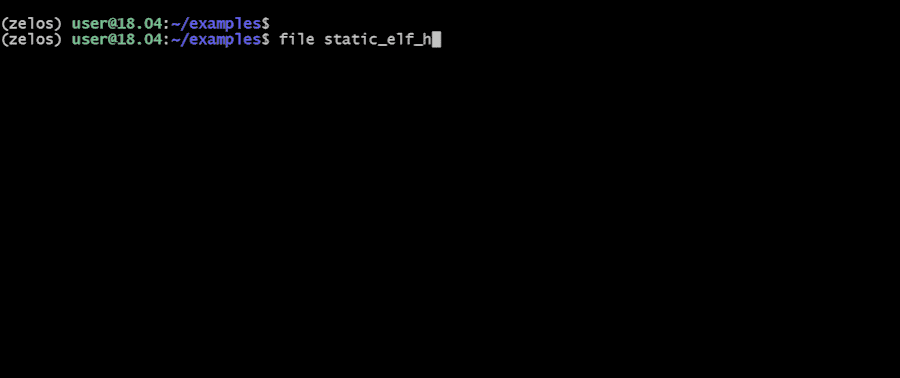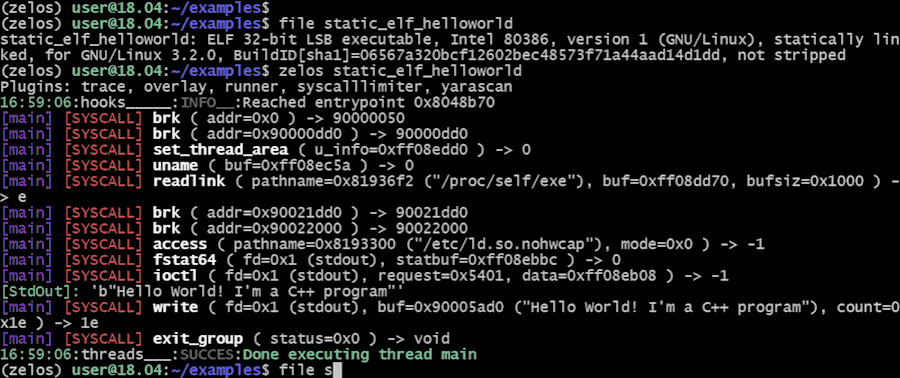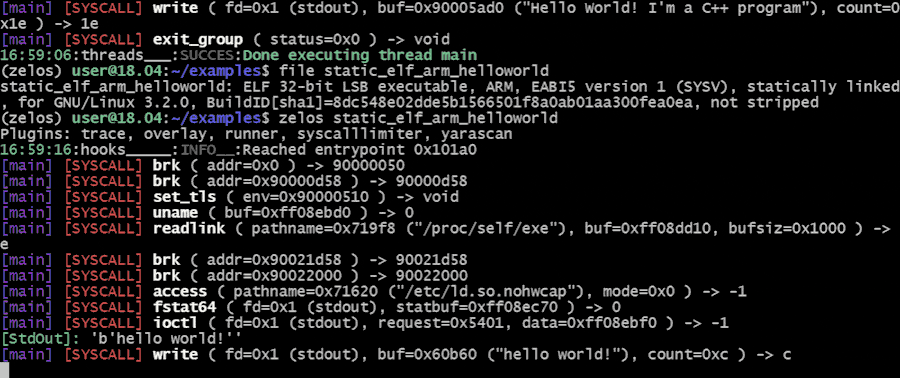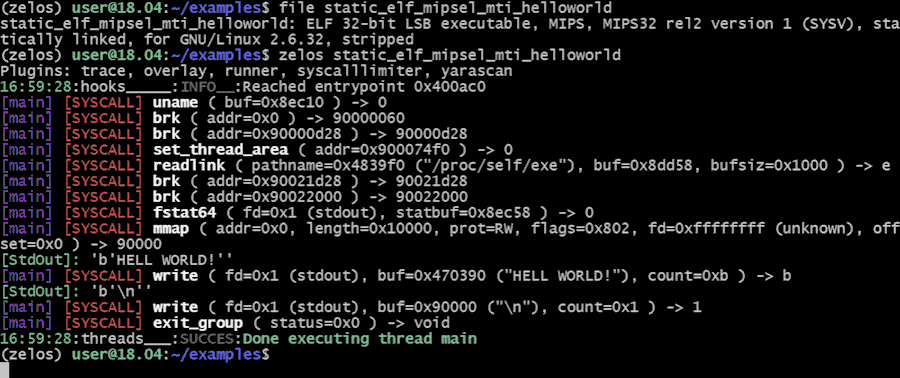 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 hugsy/gdb-static
Public repository of statically compiled GDB and GDBServer
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
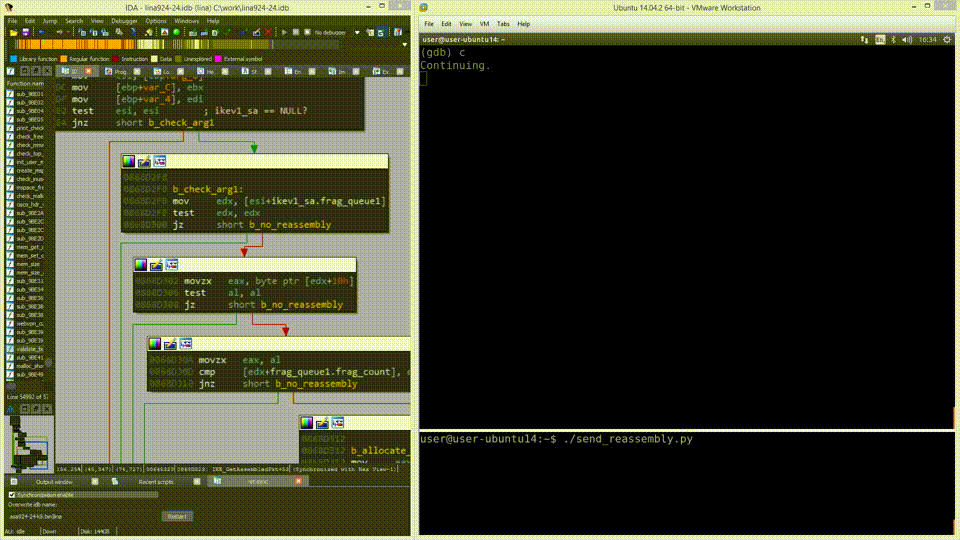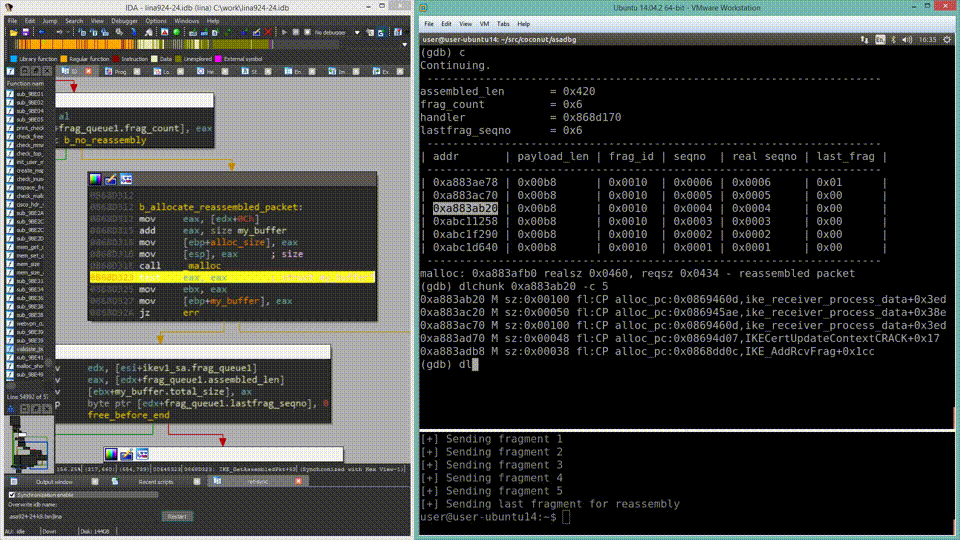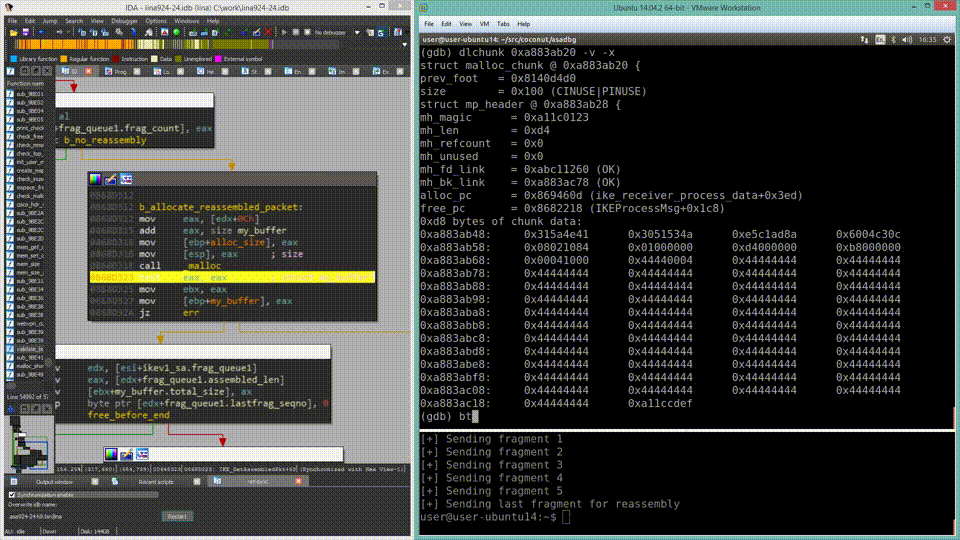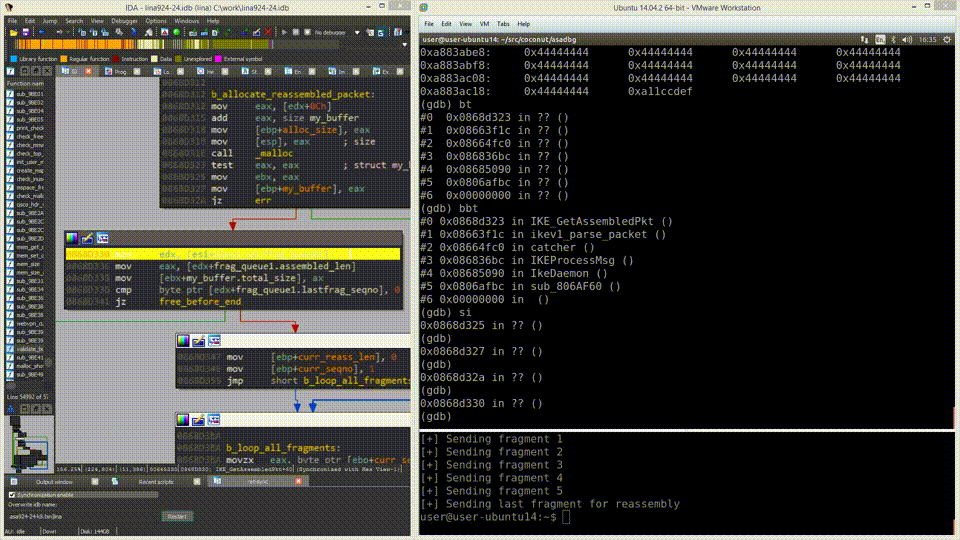 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin