
CVE-2022-43343
 halcy0nic/cve-2022-43343
Proof of concept for (CVE-2022-43343)
binary-exploitationdebuggerseducation+3
1
halcy0nic/cve-2022-43343Proof of concept for (CVE-2022-43343)
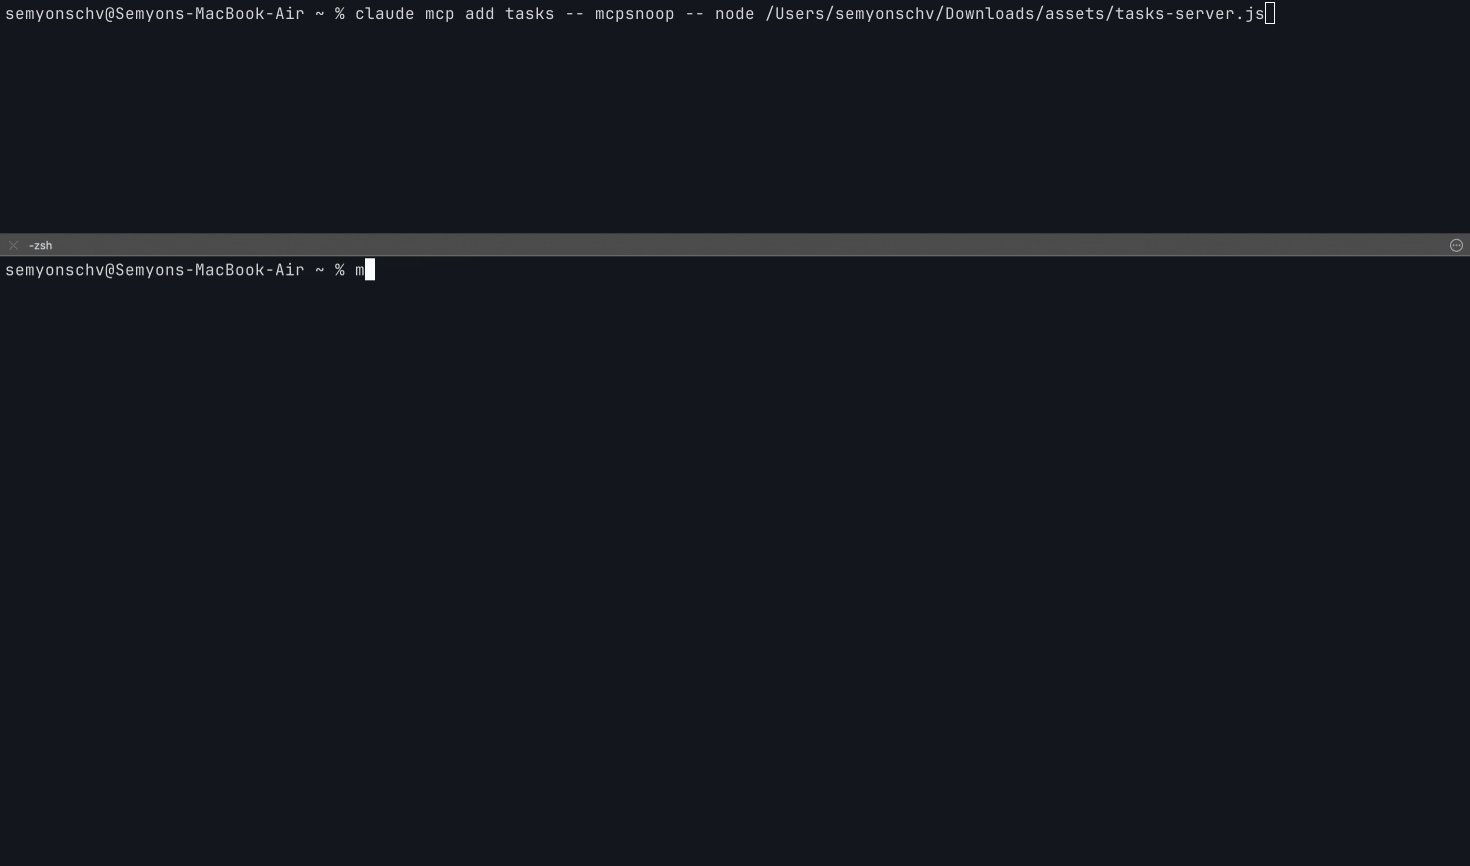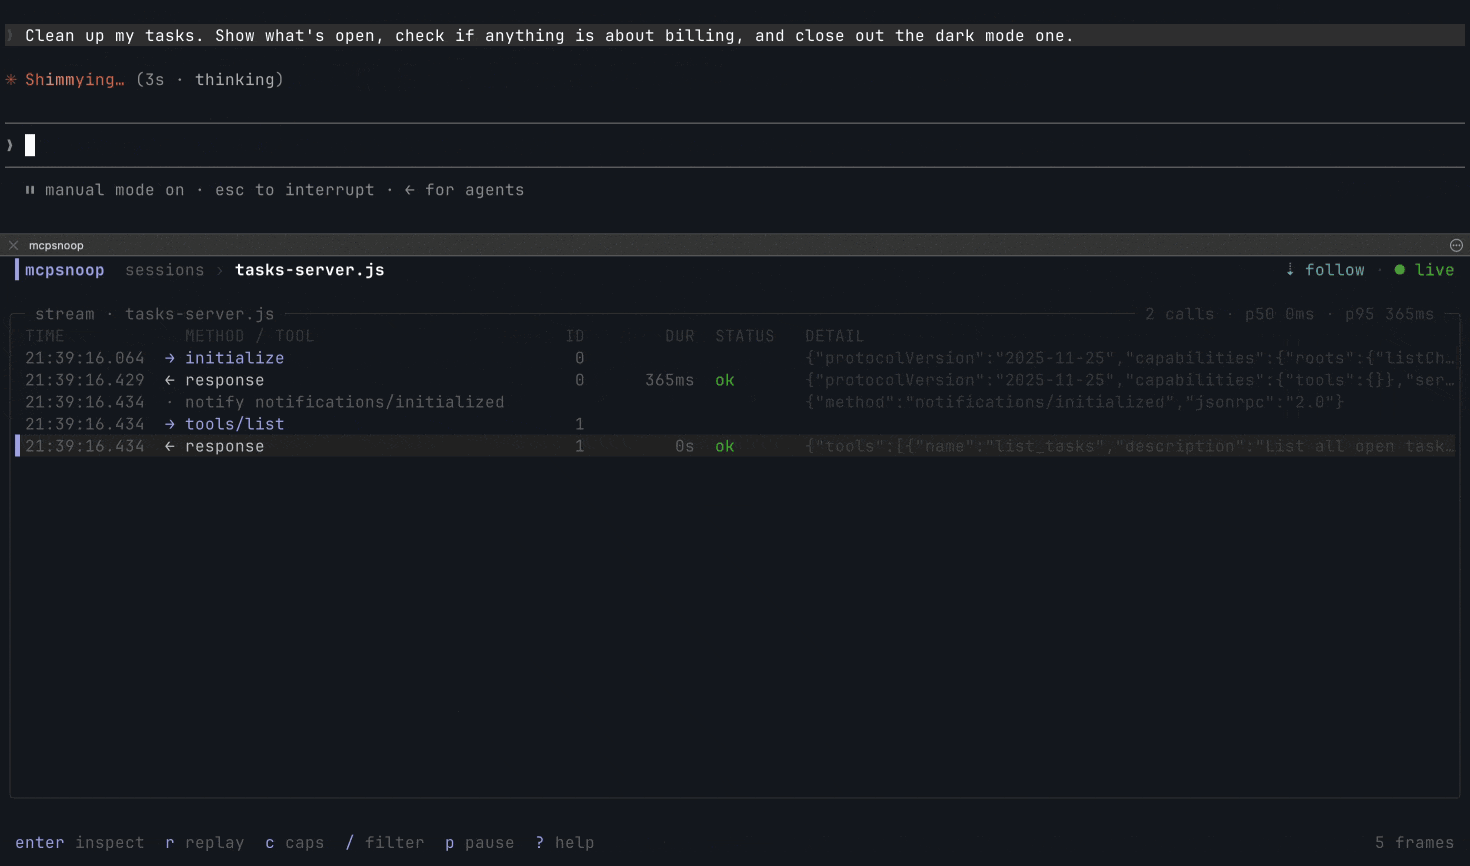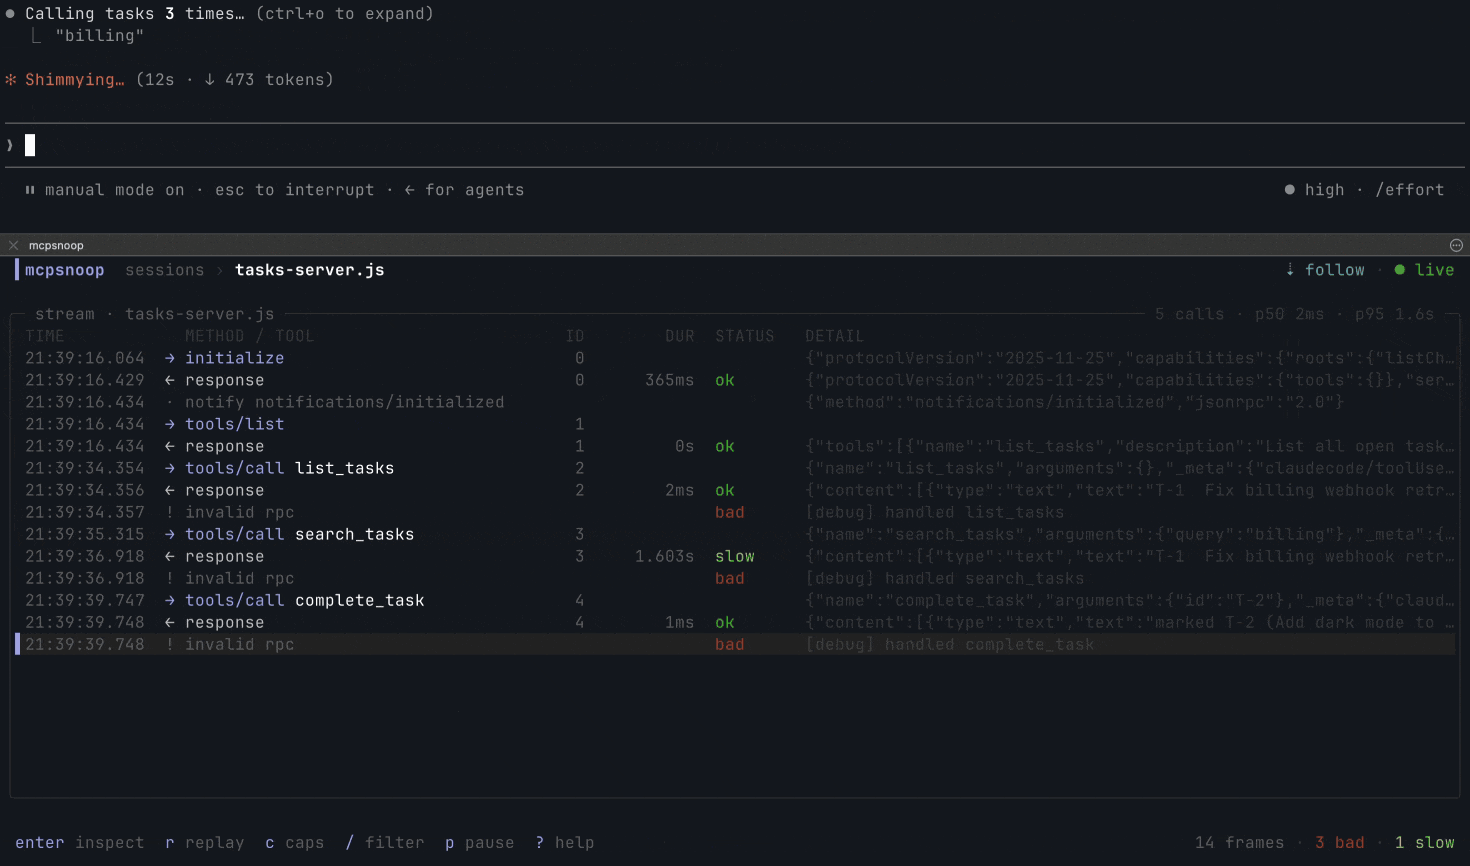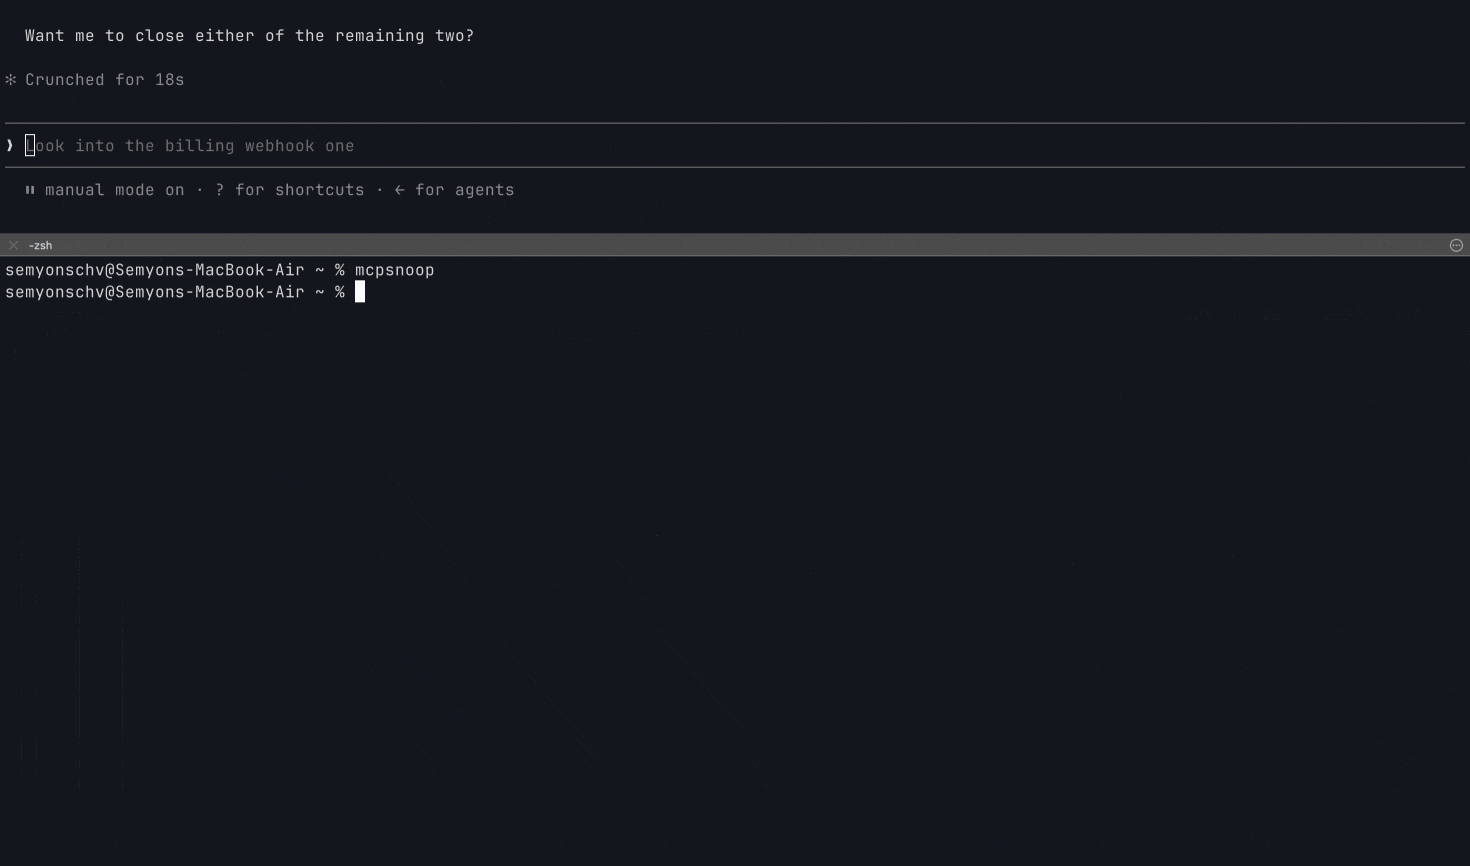 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 zardus/ctf-tools
Some setup scripts for security research tools.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset

 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
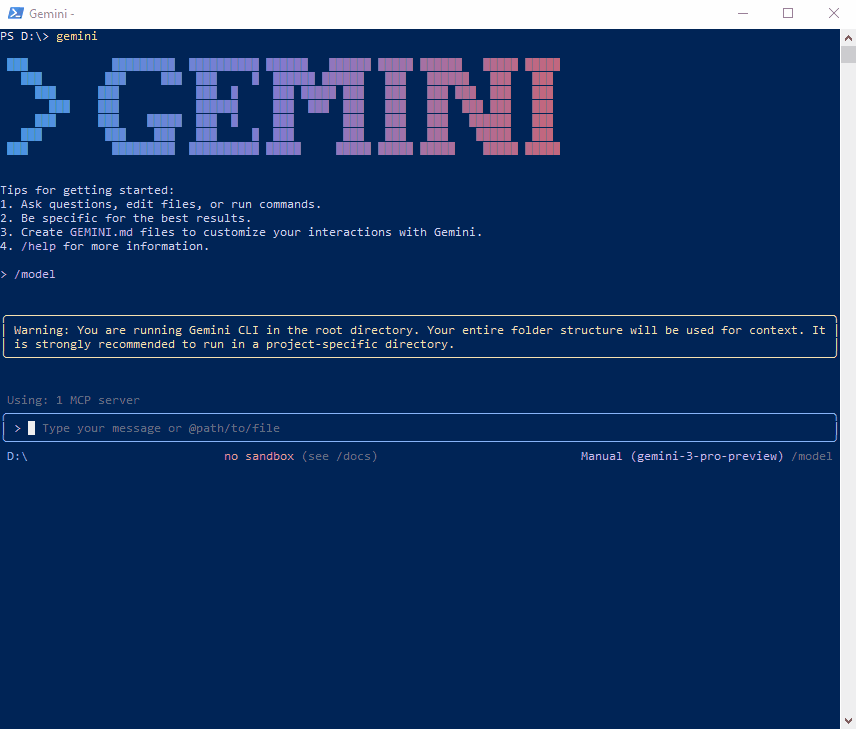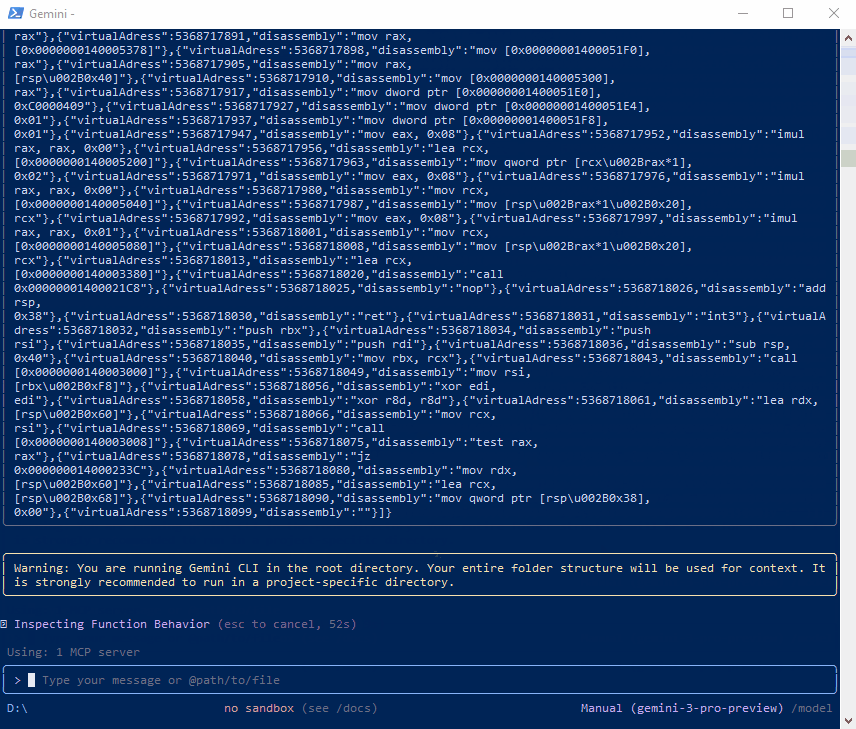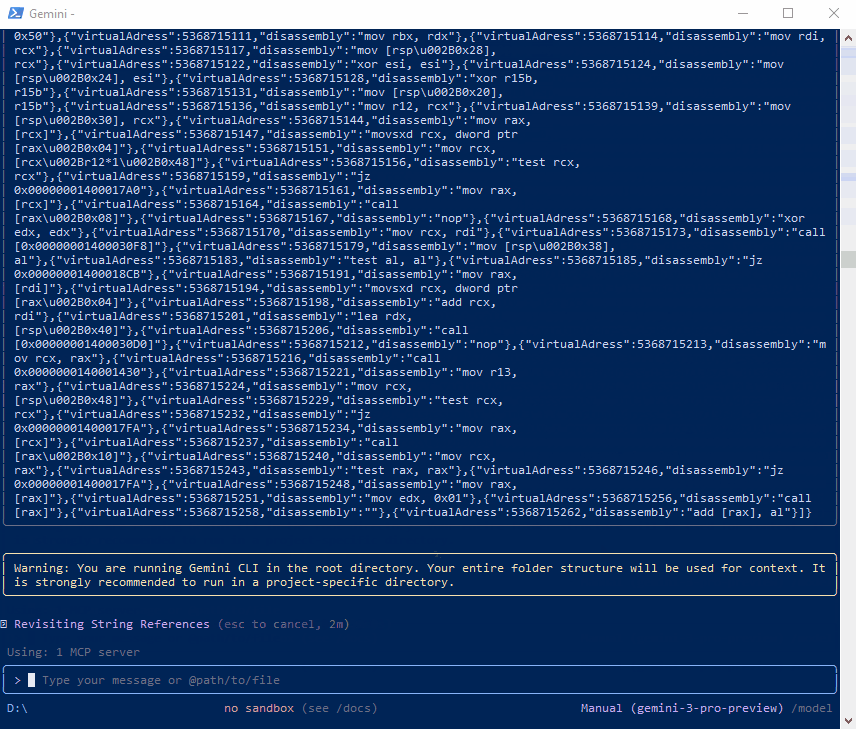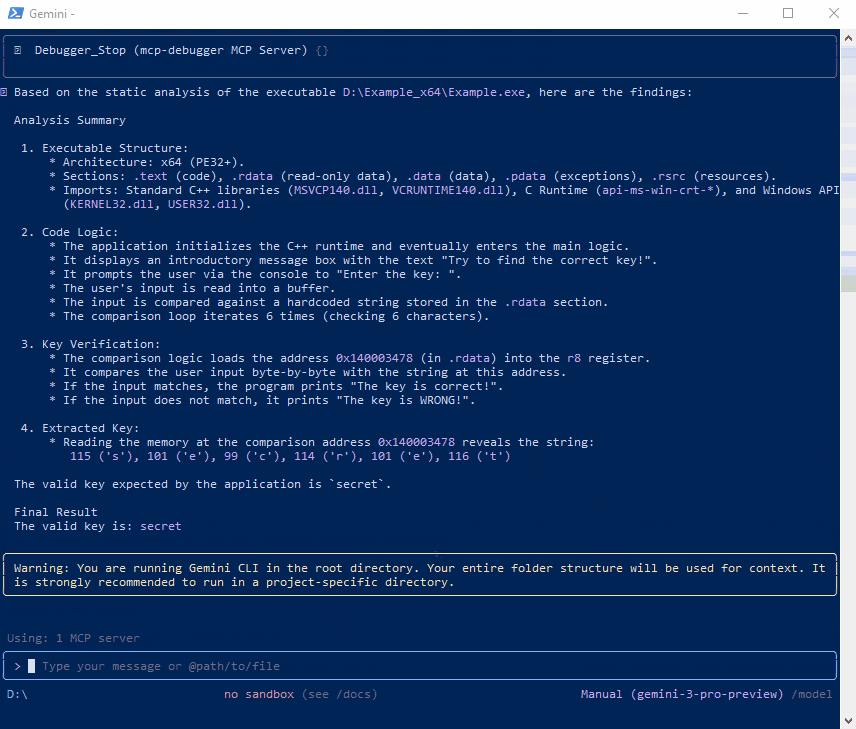 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 davidcarliez/cve-2026-62737-lab
Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
 k3vinlusec/whatsapp-double-free-vulnerability_cve-2019-11932
Step-by-step exploit analysis of WhatsApp's CVE-2019-11932 double-free vulnerability using GEF-GDB debugger for dynamic debugging and arbitrary code…
 renukaselvar/libunwind_cve-2015-3239_afterpatch
C library for stack unwinding and backtrace generation across multiple architectures, providing APIs for programmatic inspection of call stacks and…
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.