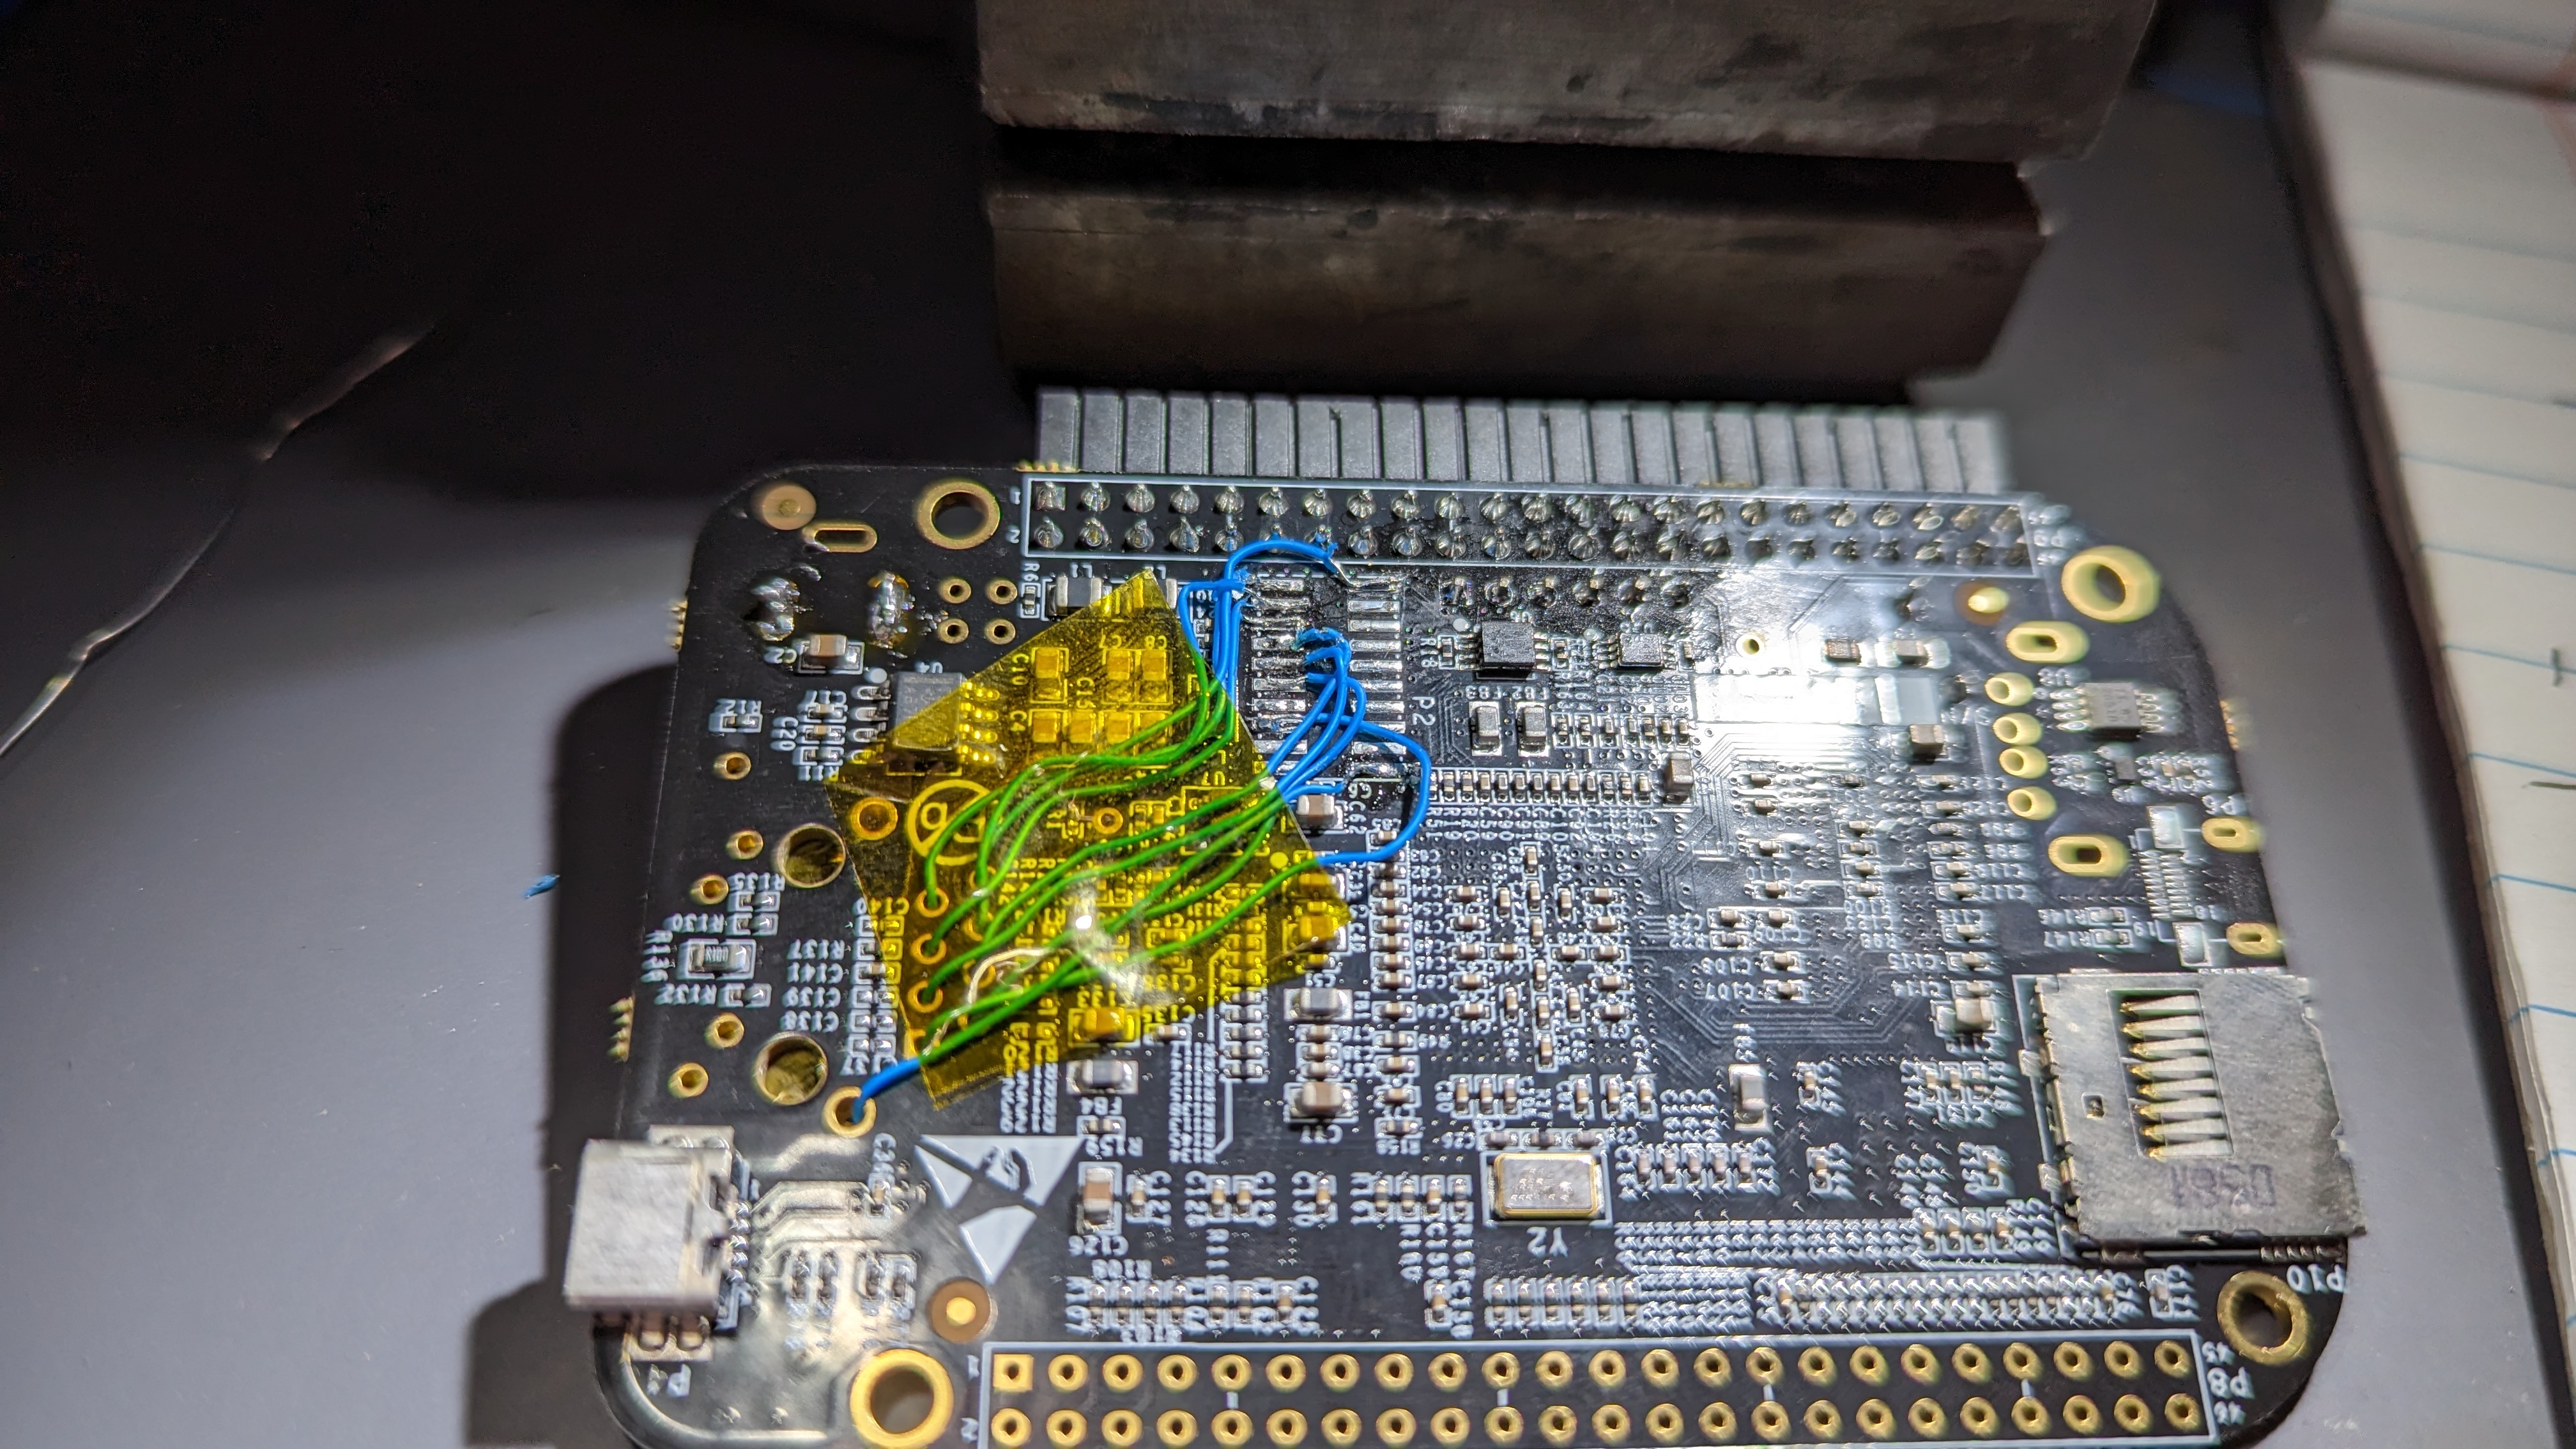
am335xbootrom
 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
binary-analysisdebuggerseducation+4
sjgallagher2/am335xbootromReverse engineering the TI AM3358 boot ROM
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 ejfkdev/pycdc
Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 piffd0s/ntoskrnl-metadata
eprocess offset puller for relevant member offsets and function addresses for cve-2026-40369
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
 day6reak/cve-2014-1773
Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…