
edb-debugger
 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
binary-analysisdebuggersreverse-engineering
eteran/edb-debuggeredb is a cross-platform AArch32/x86/x86-64 debugger.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
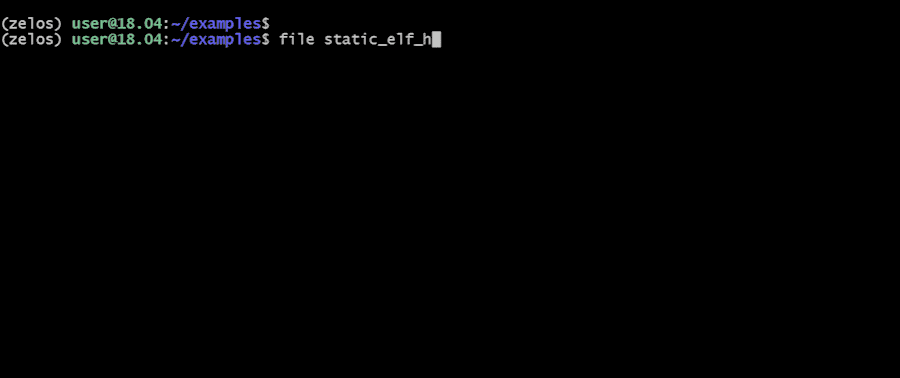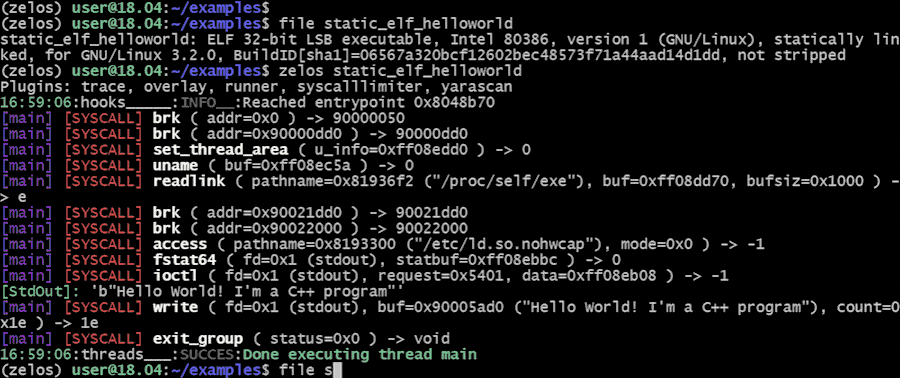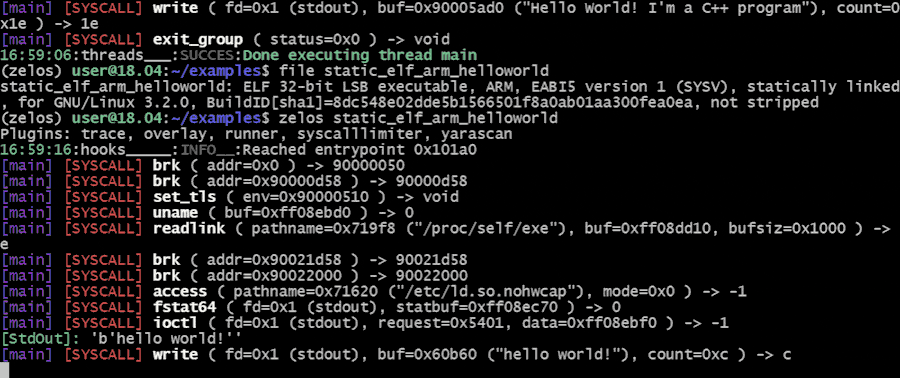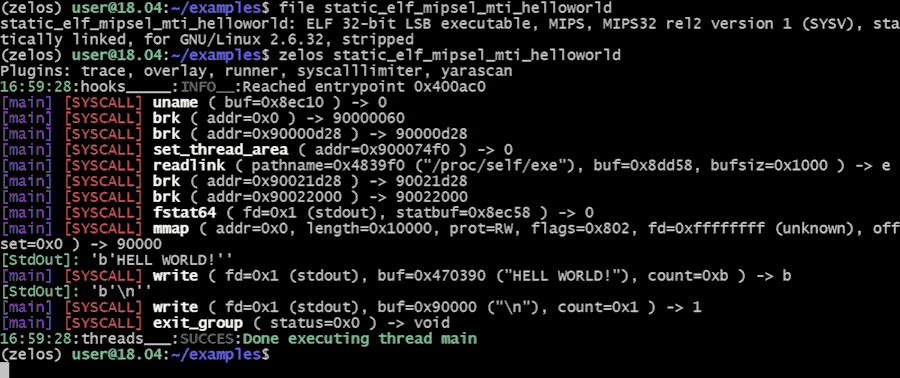 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 hugsy/gdb-static
Public repository of statically compiled GDB and GDBServer
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
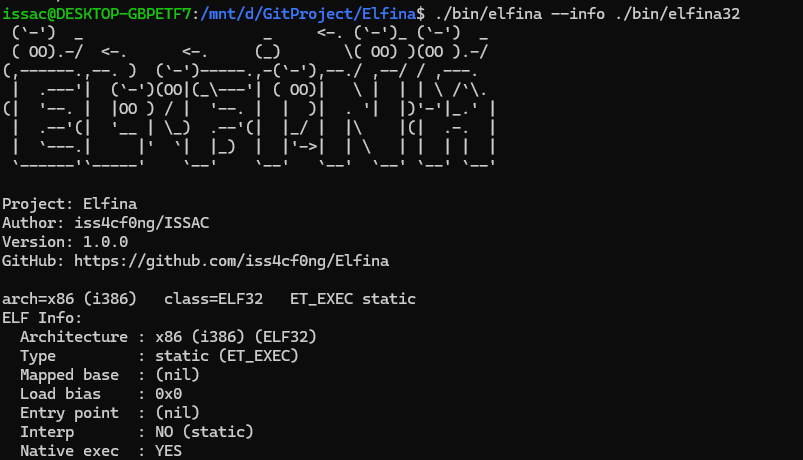 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
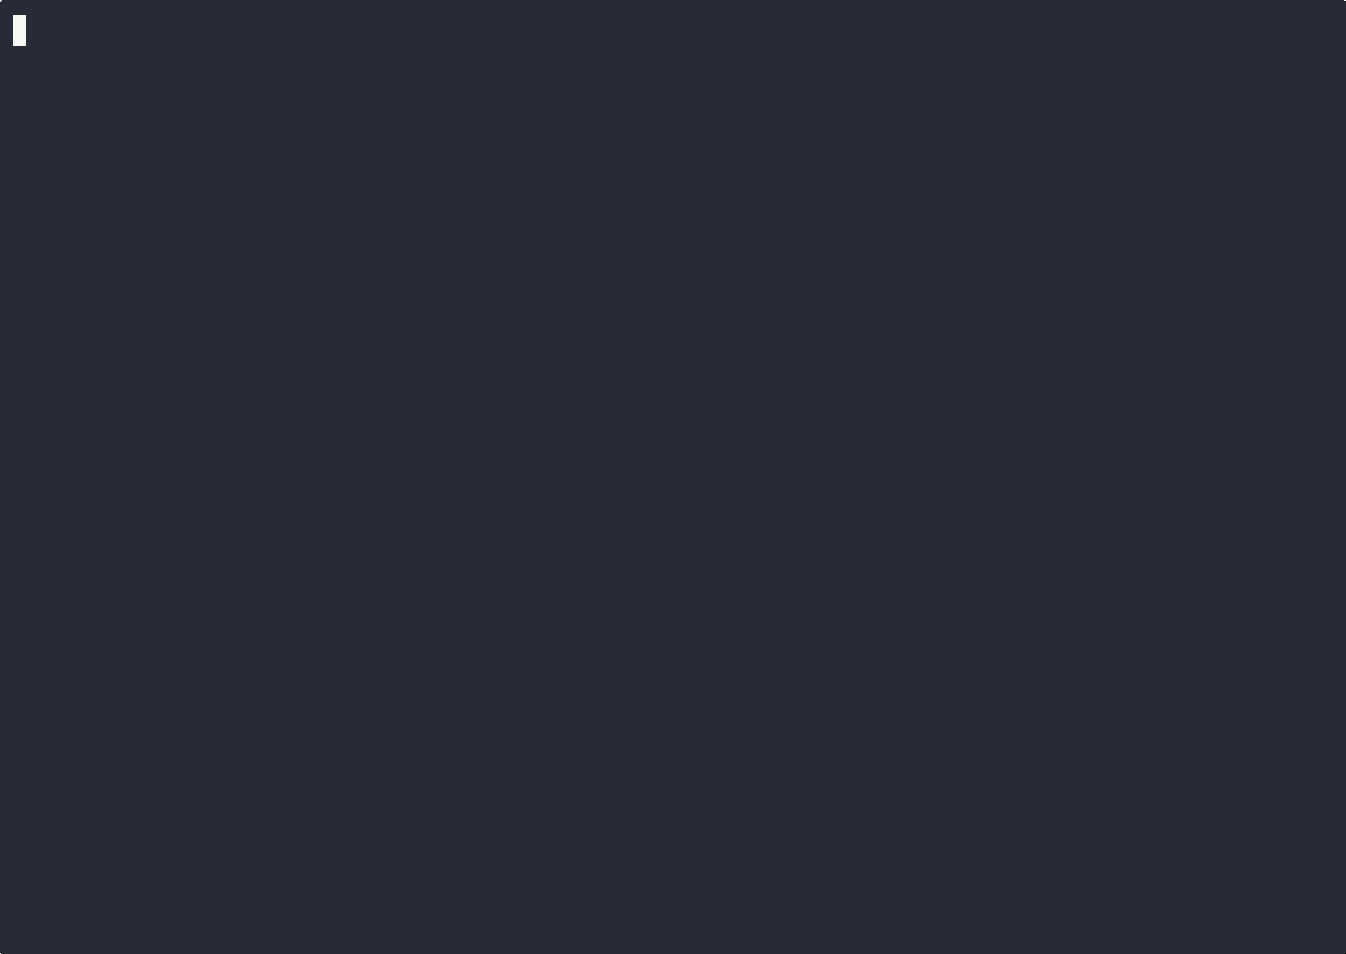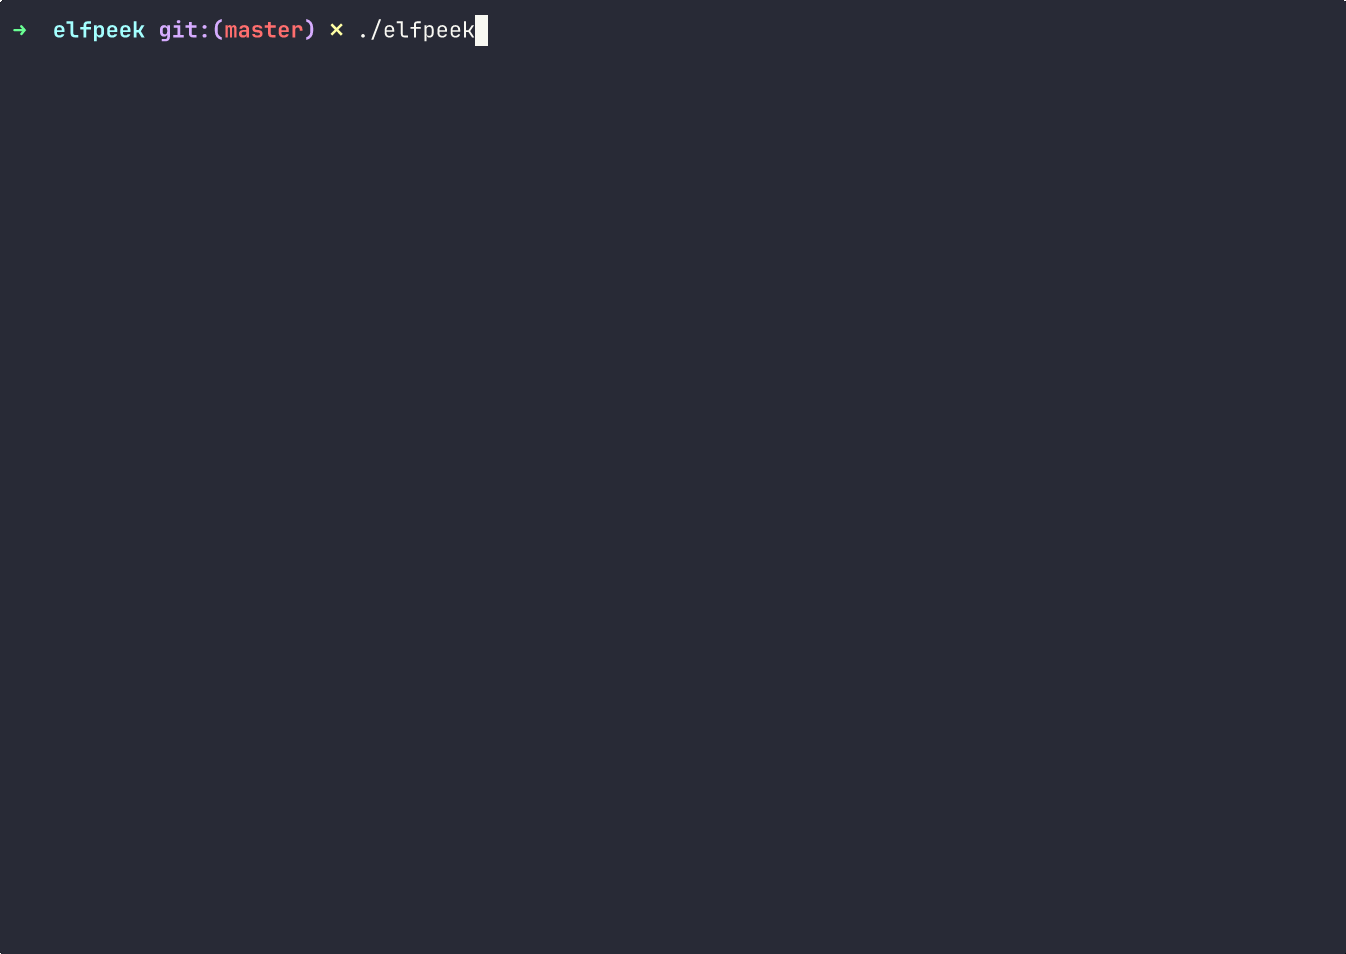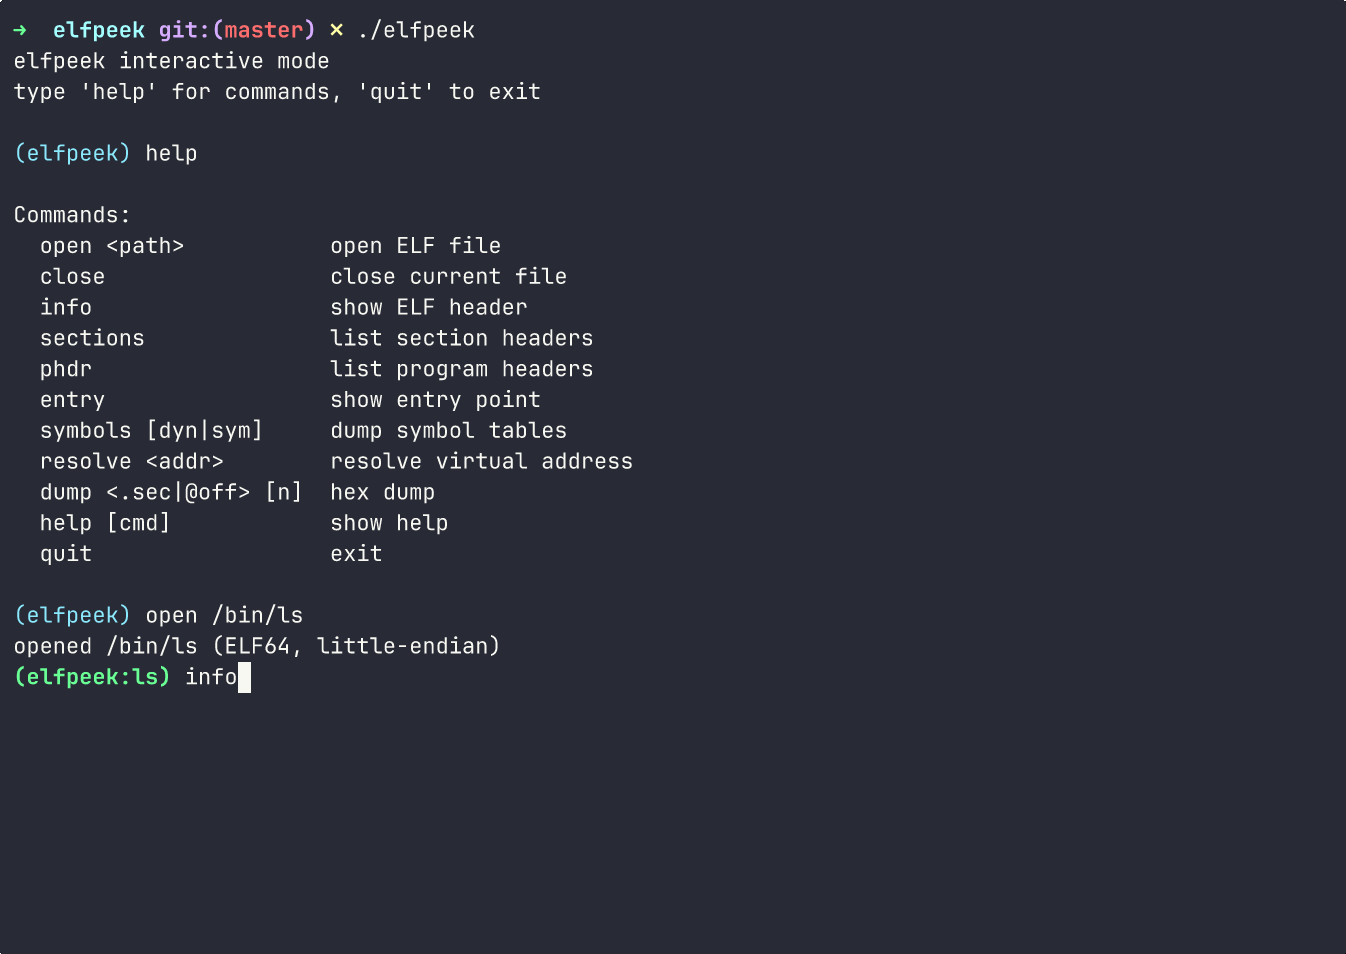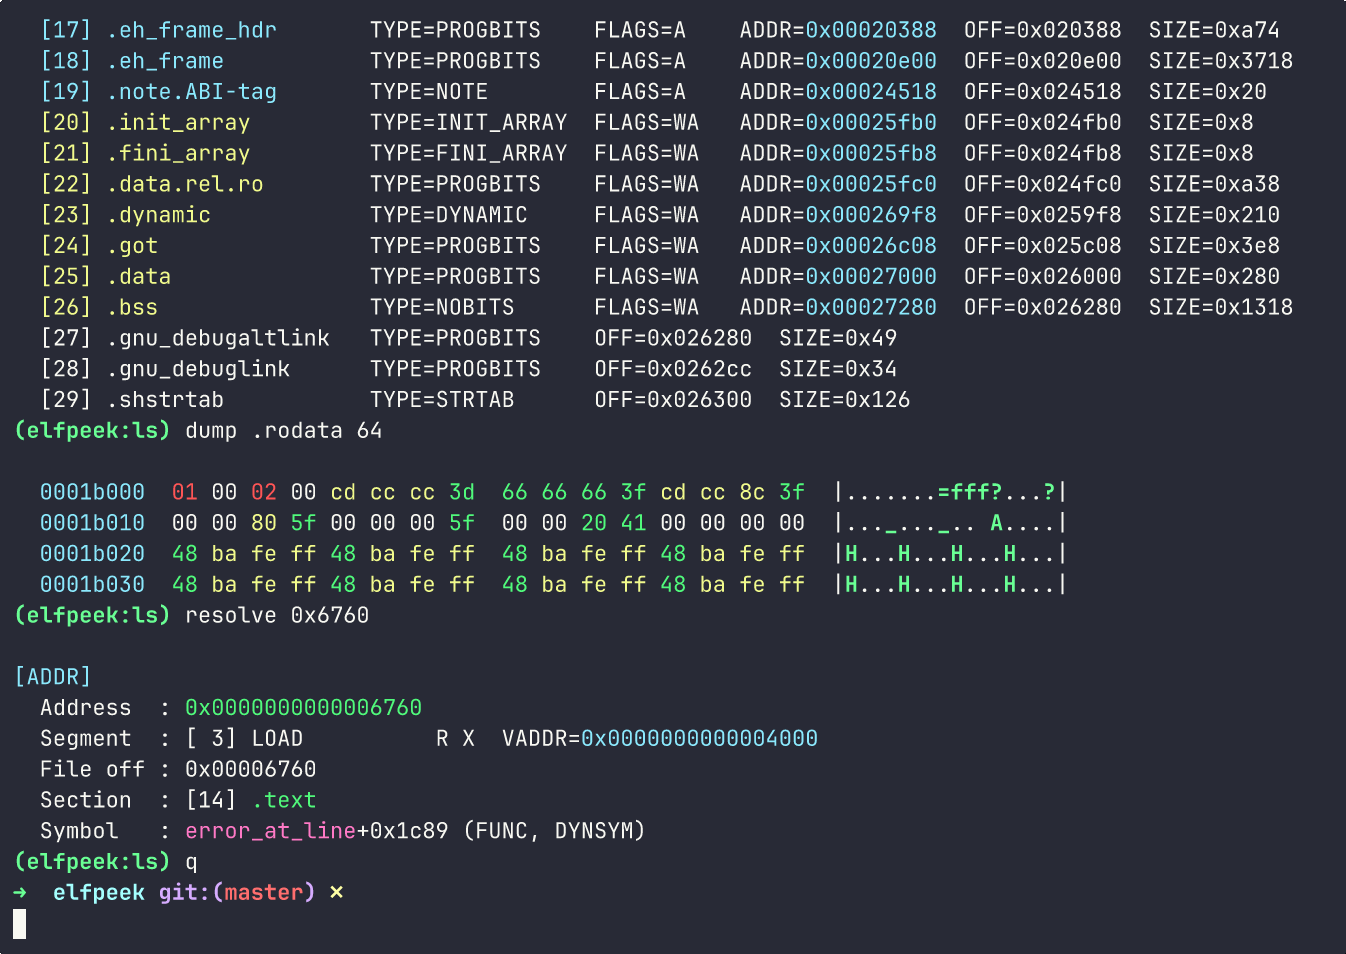 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
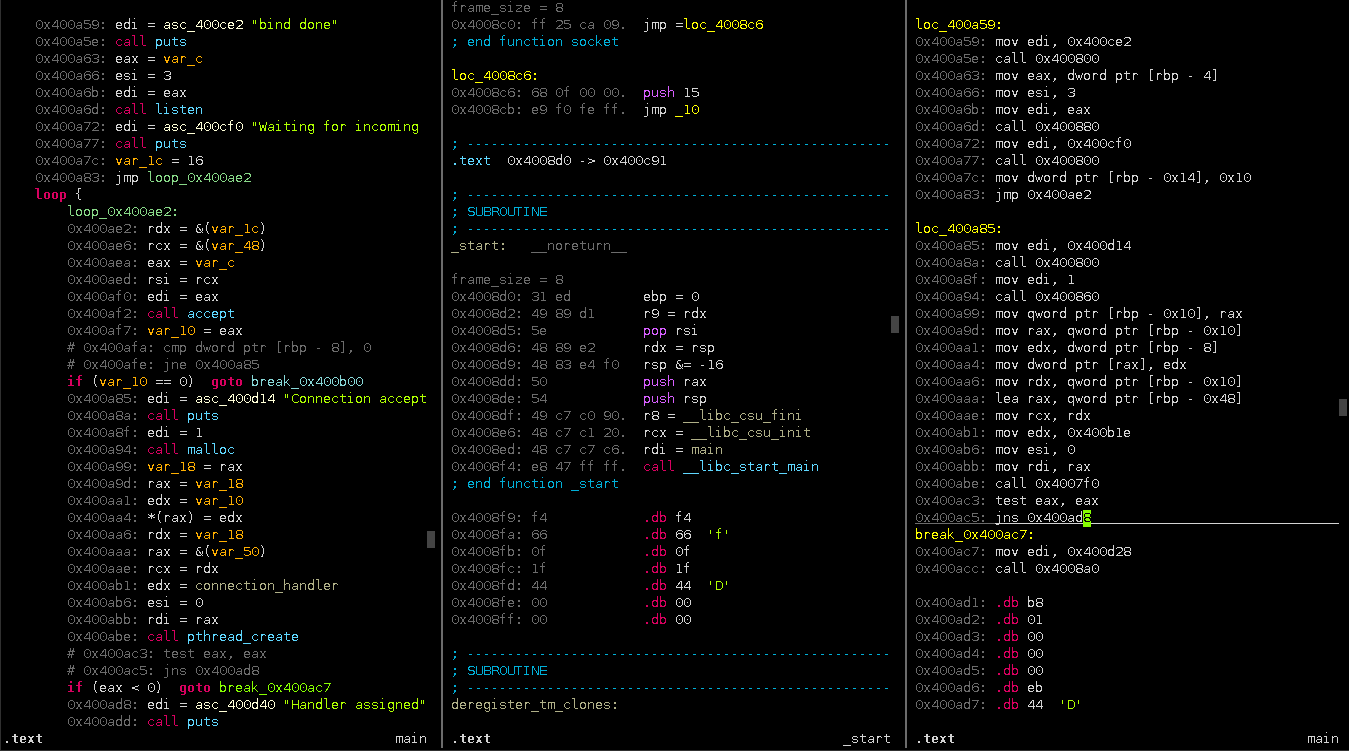 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 fabiobaroni/awesome-exploit-development
A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode