
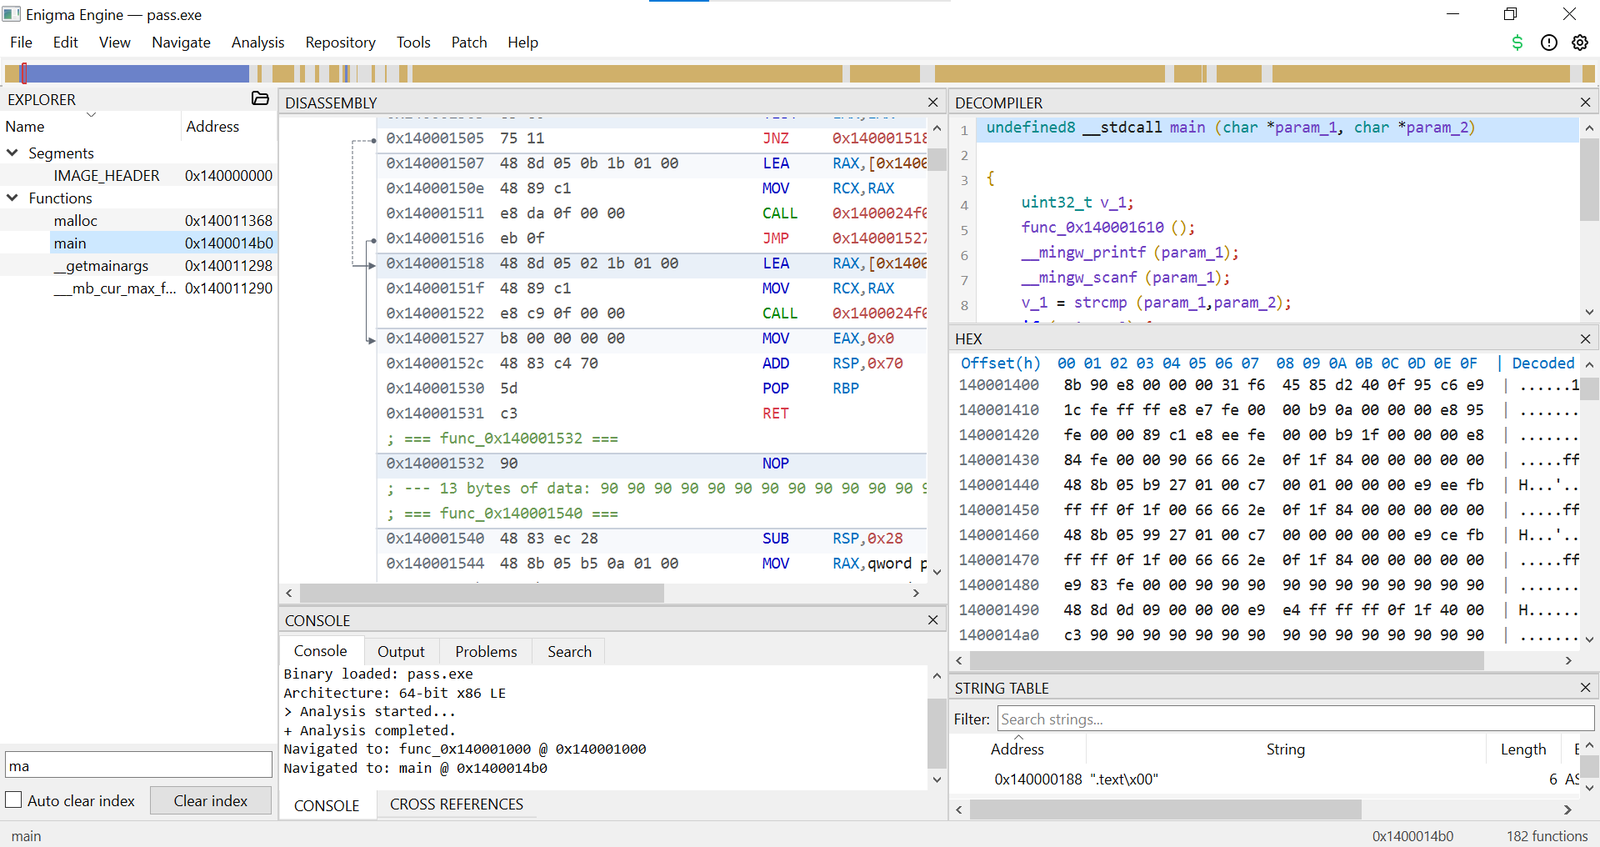
Enigma
 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
ai-assisted-reversingbinary-analysisdebuggers+3
63
bunnybuzz/enigmaNative C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
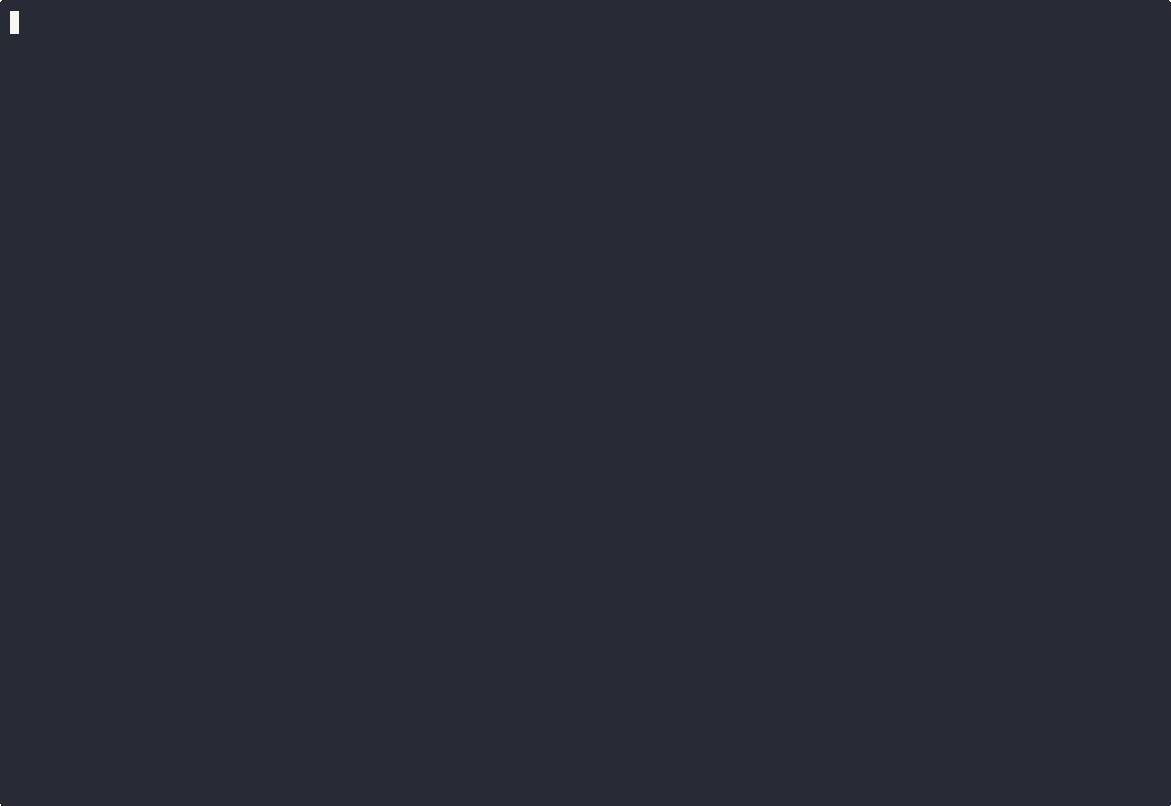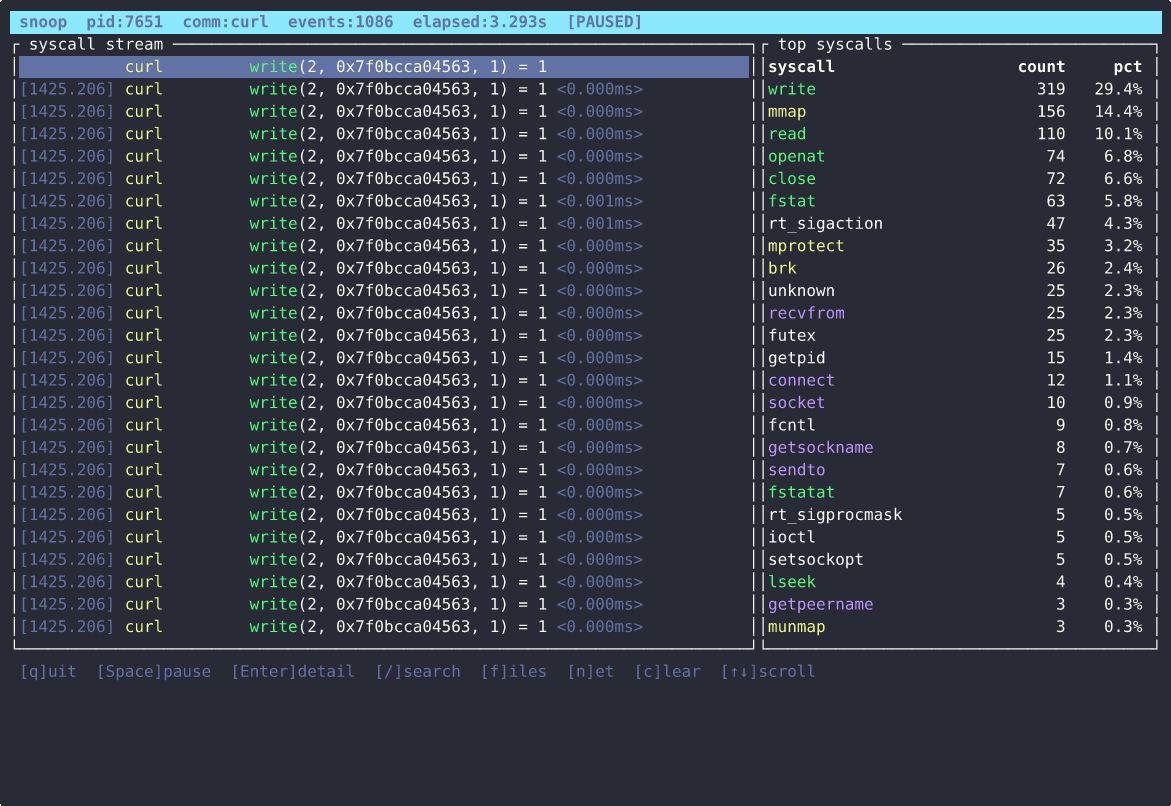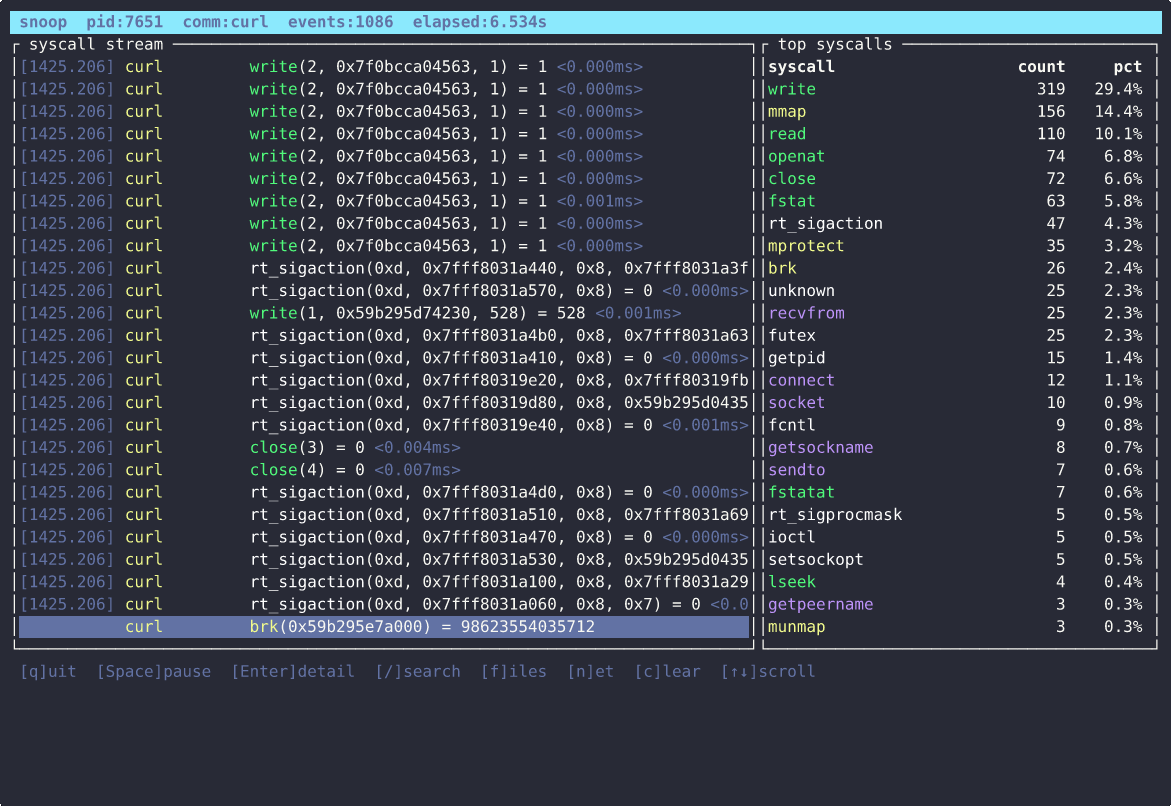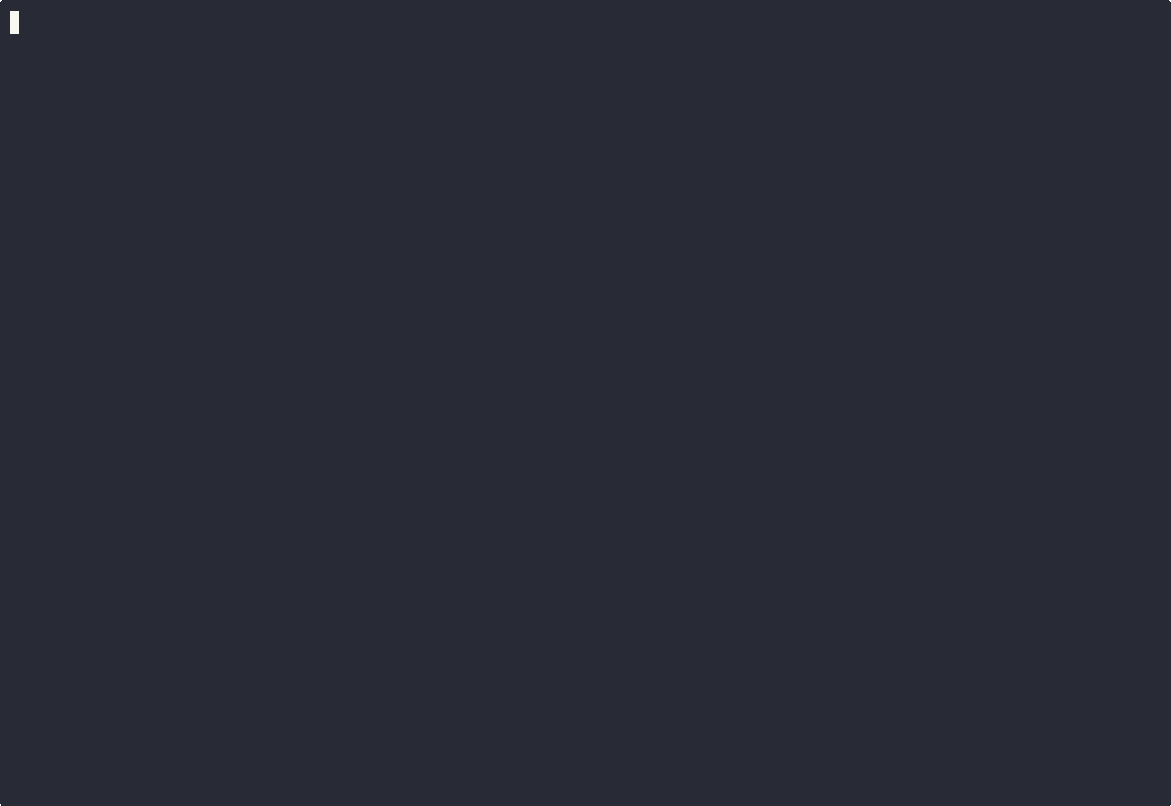 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 fail0verflow/ps5-umtxdbg
C++ exploit reliability experimentation for a PlayStation 5 FreeBSD kernel vulnerability, with VM kernel builds and GDB remote-debugging setup.
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
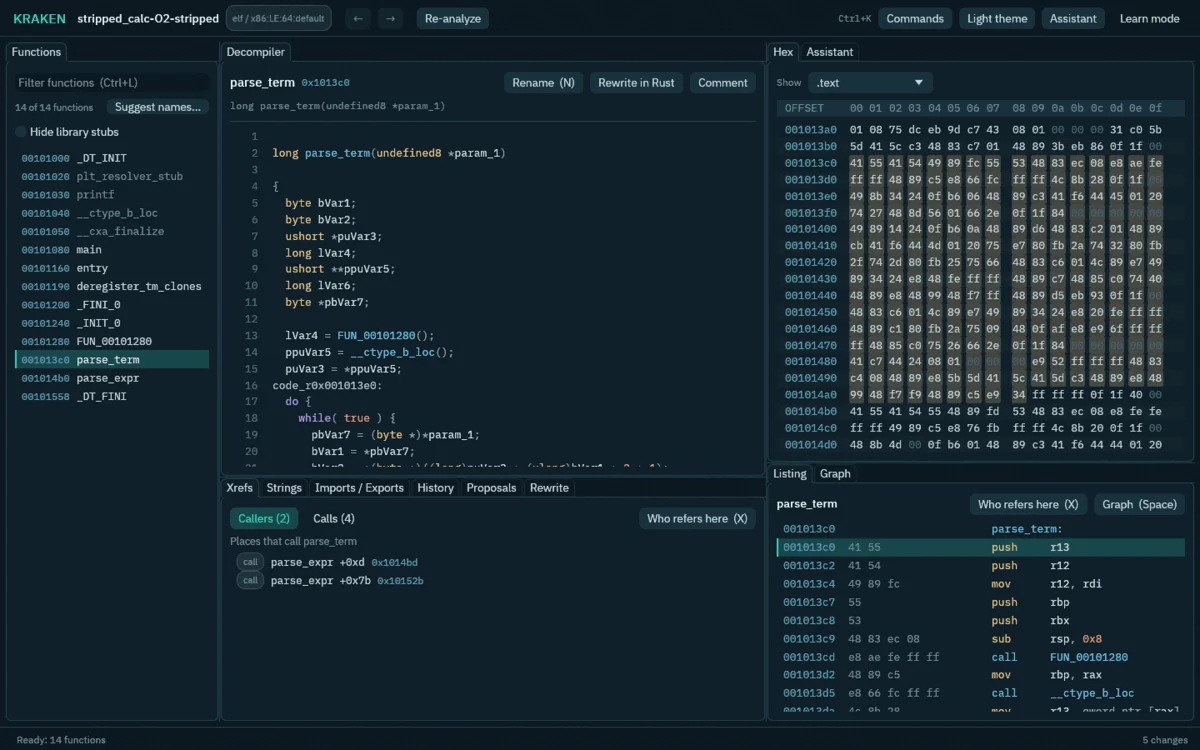 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
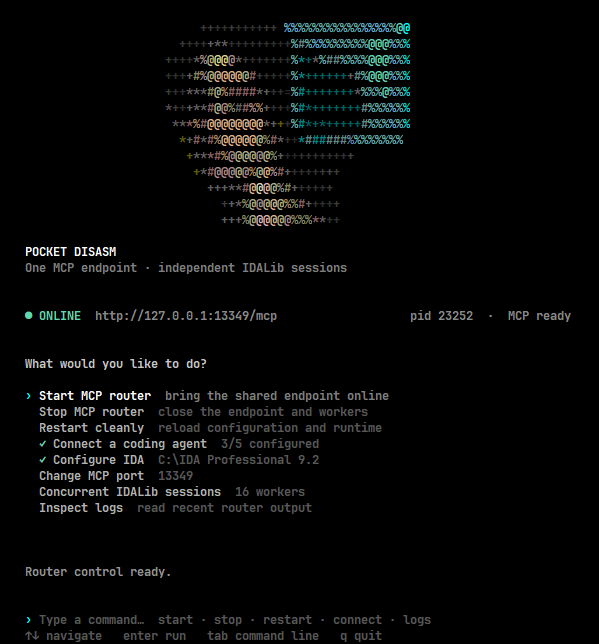 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
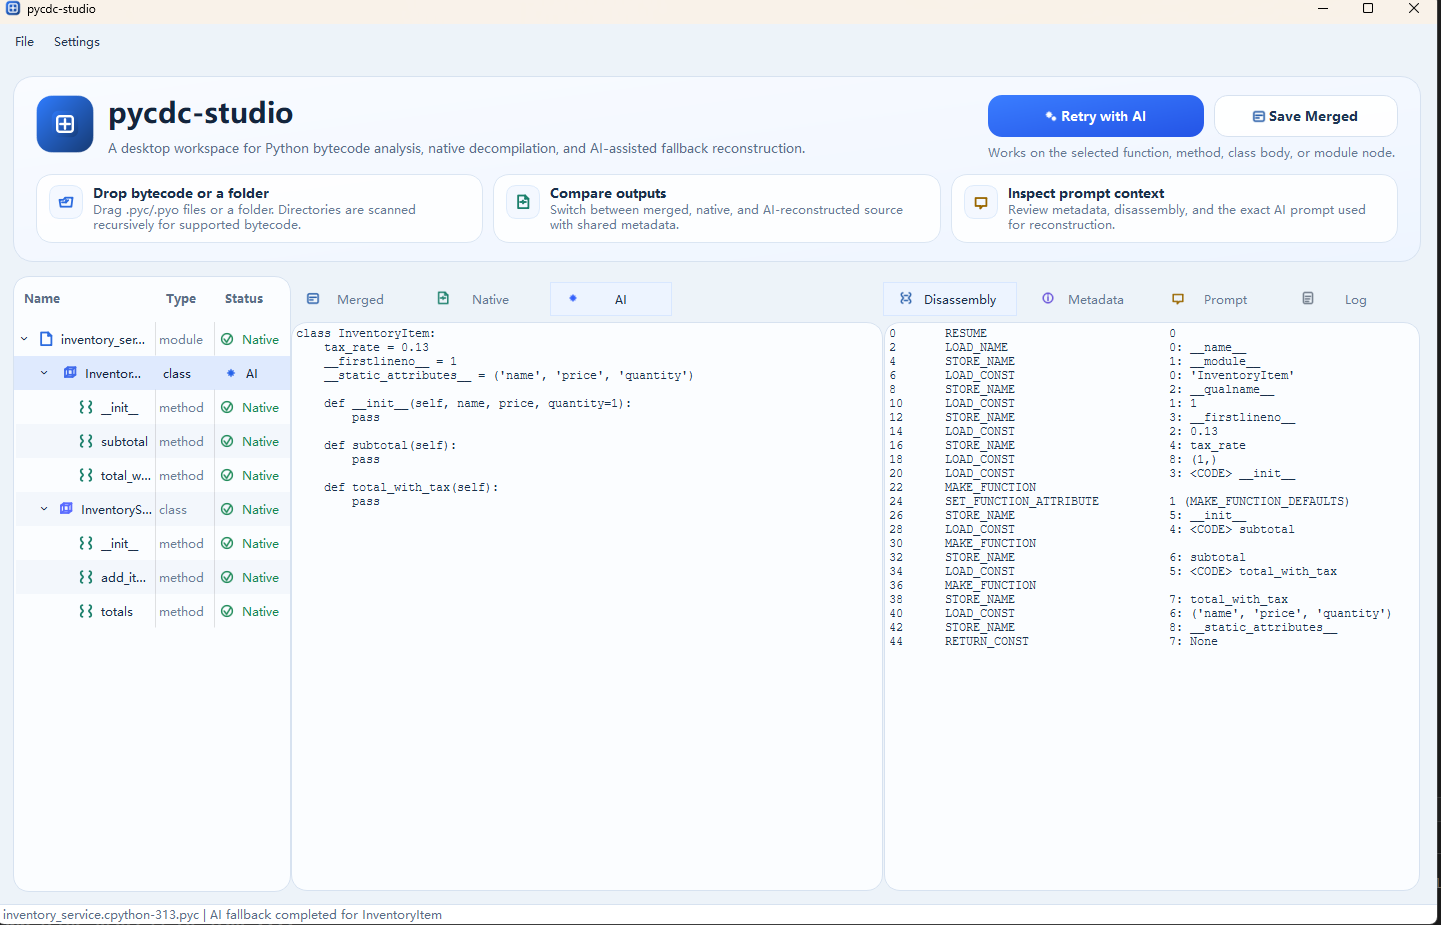 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 zhuowei/cve-2025-27363-proof-of-concept
Proof-of-concept for CVE-2025-27363 demonstrating a heap buffer overflow in FreeType 2.13.0 via a crafted variable font, with ASAN-verified crash…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 baiyibai/pico-usb-wifi
Firmware for Raspberry Pi Pico W that creates a driverless USB Wi-Fi adapter with transparent layer-2 bridging, WPA2/WPA3 authentication, and…
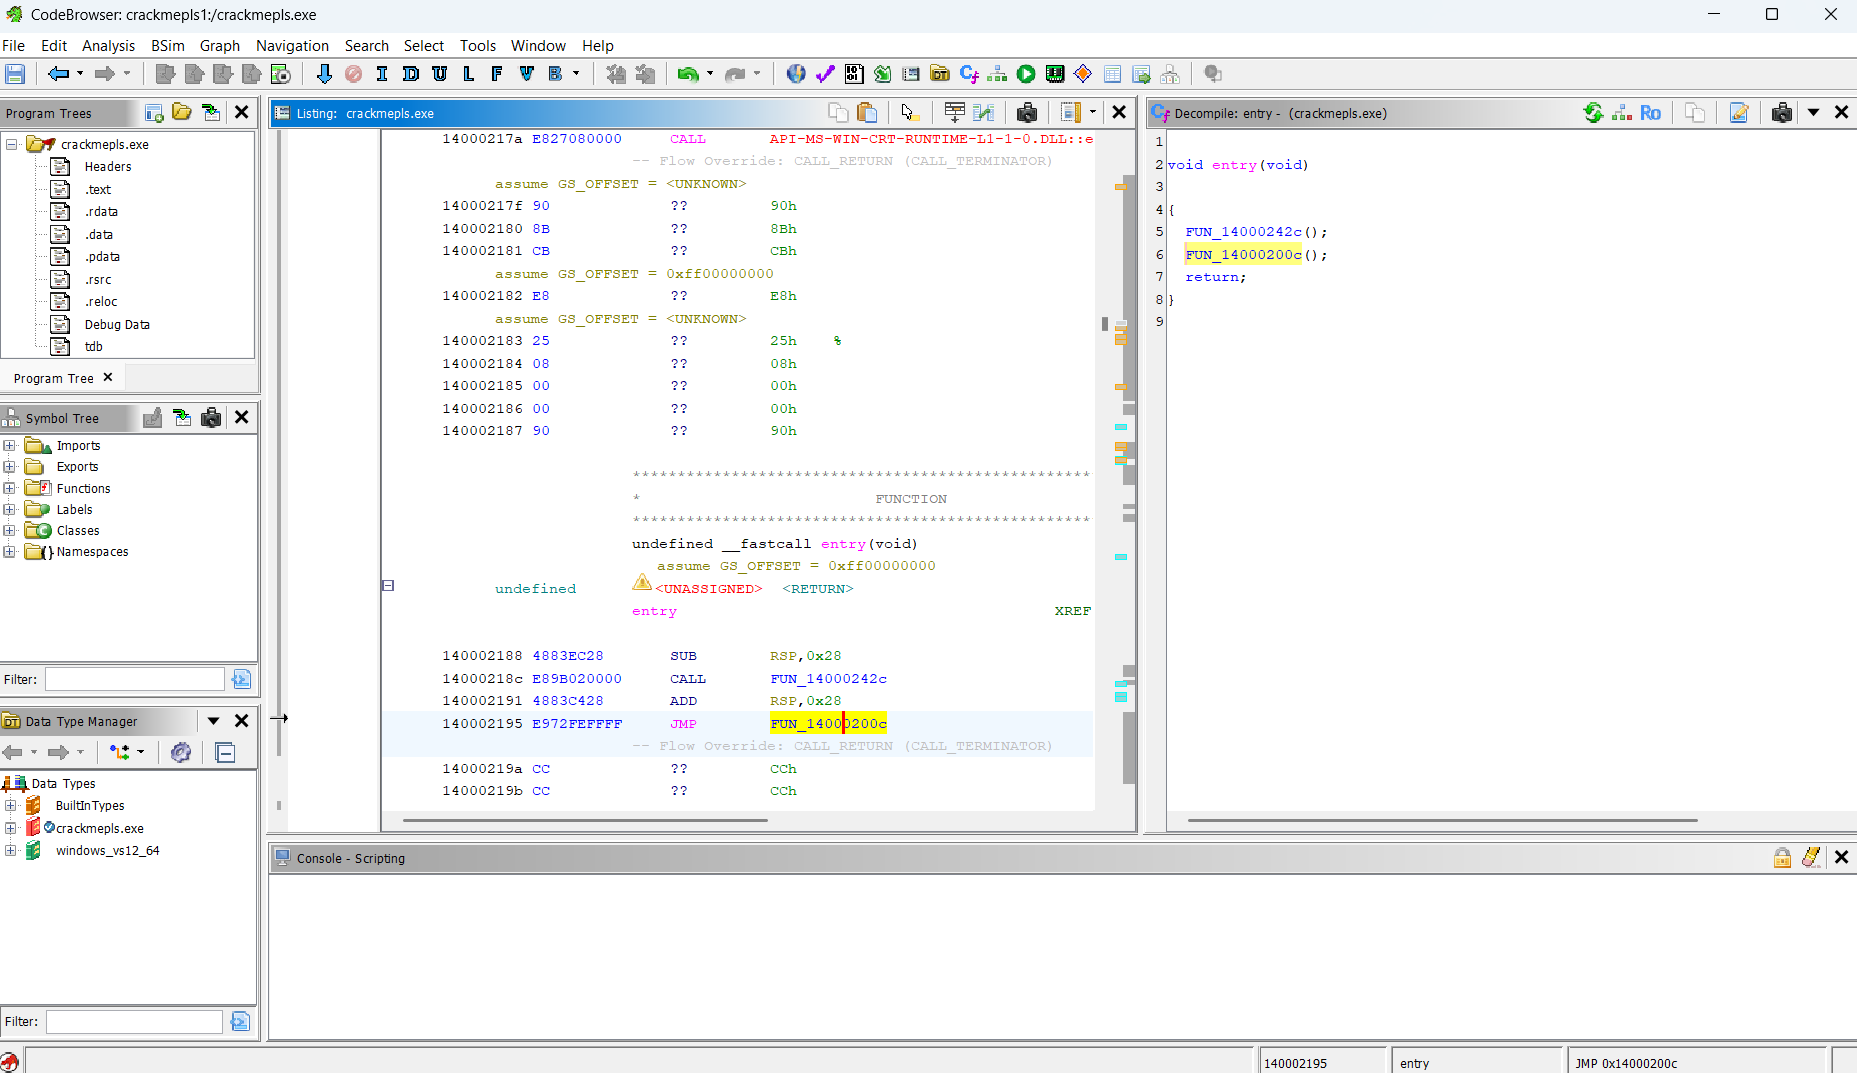 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 bitstream93/shellcode-test-harness
A lightweight test harness designed to speed up shellcode development by providing an execution environment with integrated crash diagnostics and…
 show0ne/archivo-syxe05-snat
Historical archive of reverse engineering and unpacking tutorials covering commercial protectors (Armadillo, ASProtect, Themida) with classic tools…
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging