

c0ntextomy
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
data-exfiltrationdebuggersexploitation+9
73
c0ntextomy/c0ntextomyCVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
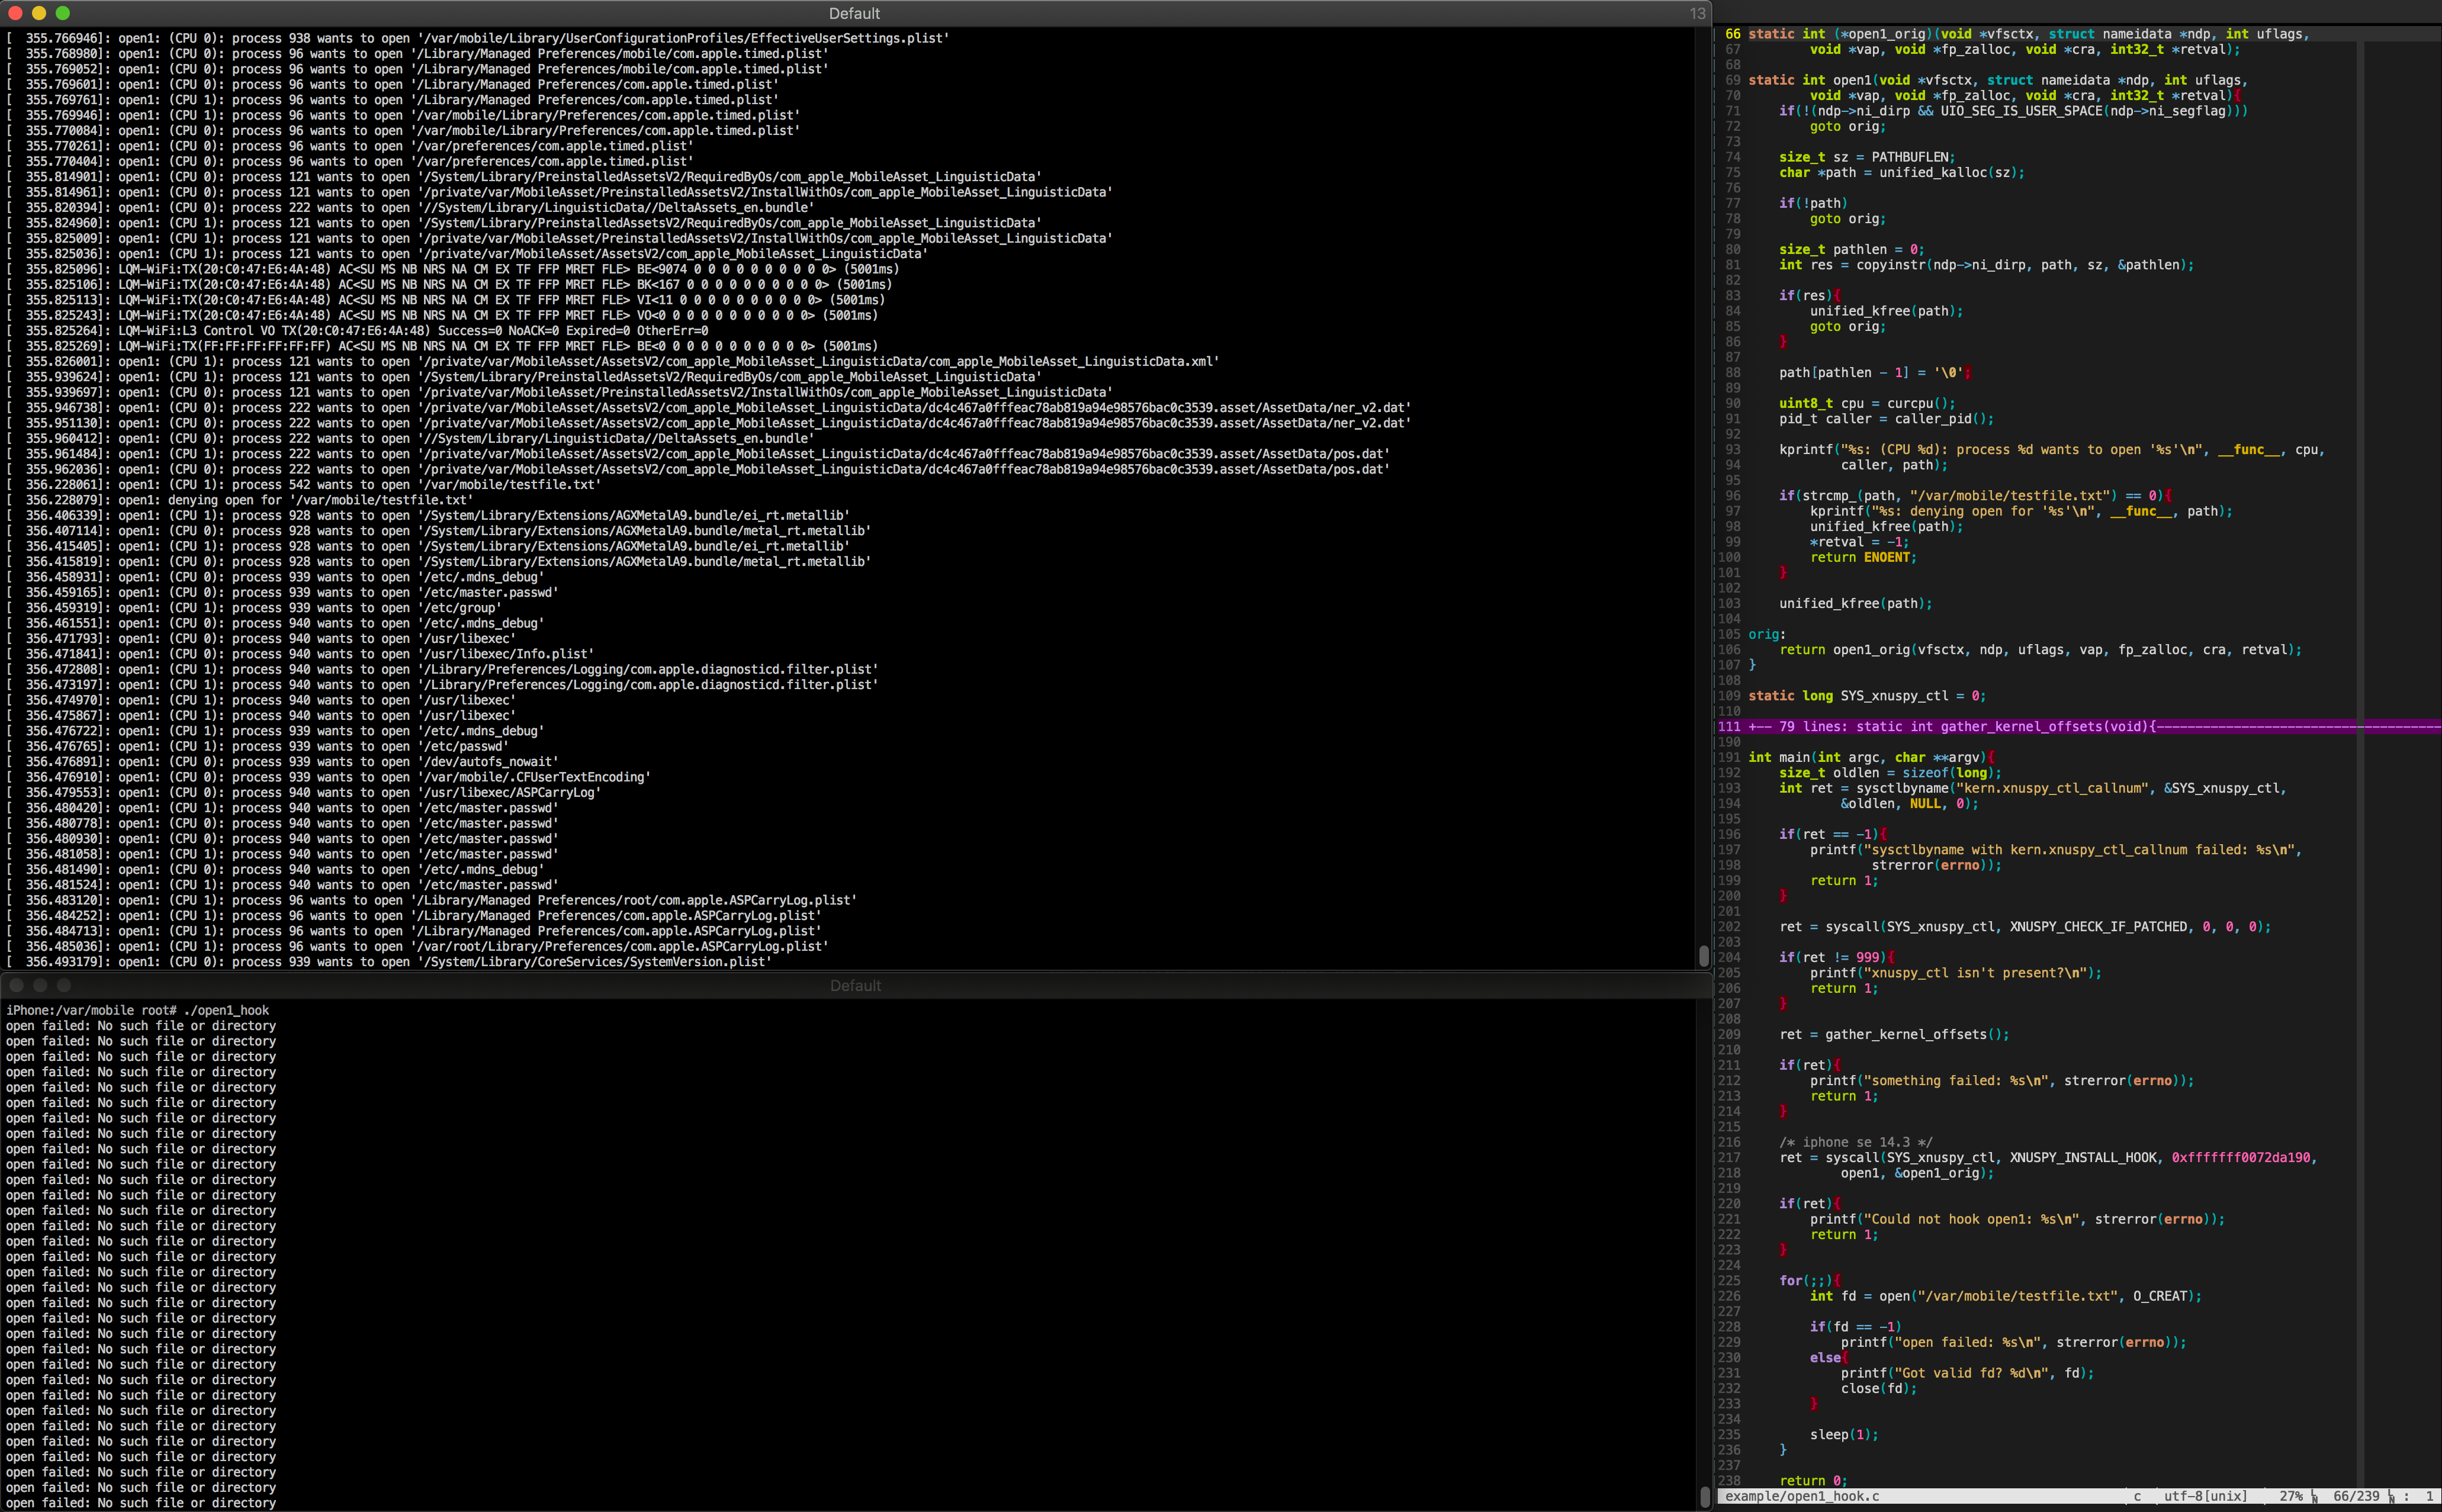 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
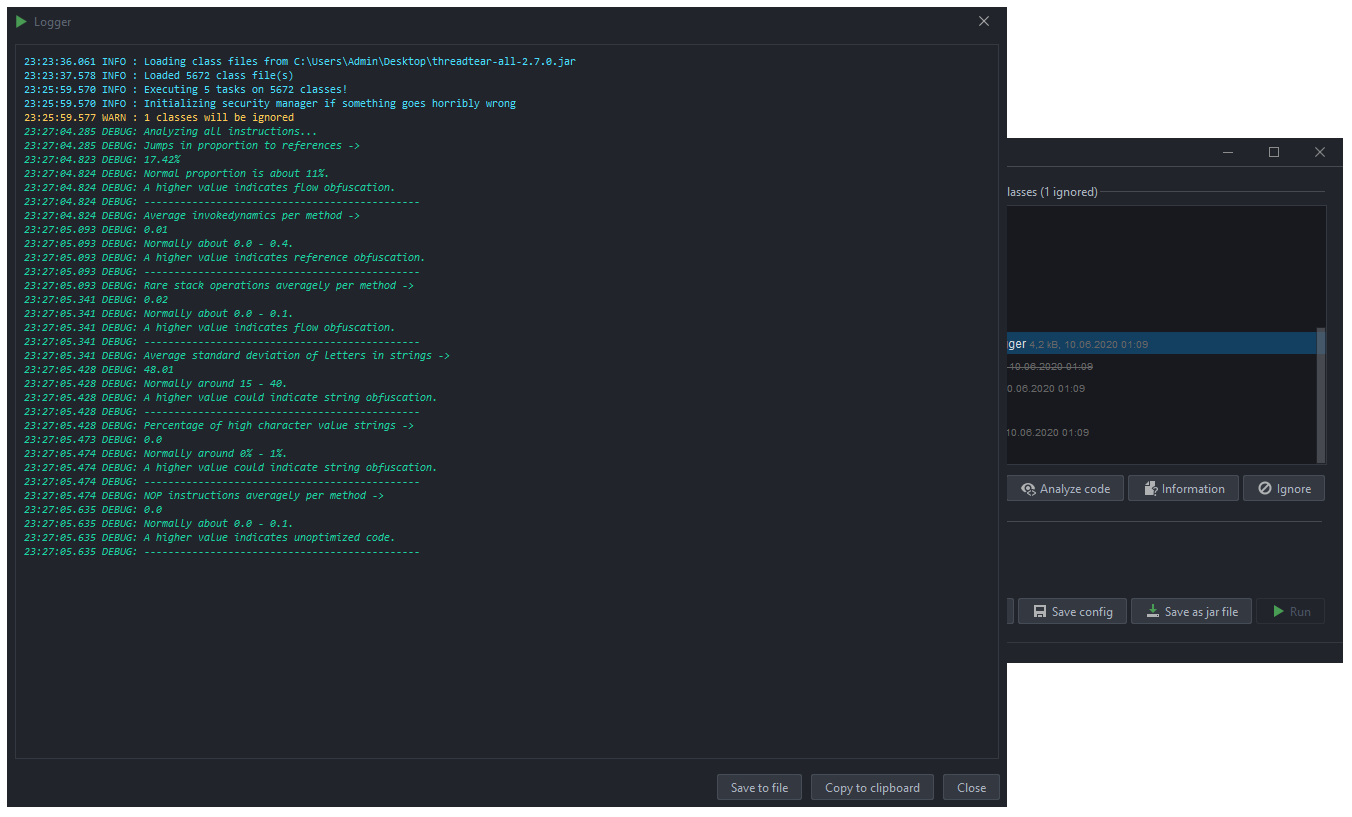 loerting/threadtear
Multifunctional java deobfuscation tool suite
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks

