
CVE-2021-3156
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
binary-exploitationcode-analysisdebuggers+8
114 years ago
chenaotian/cve-2021-3156CVE-2021-3156 POC and Docker and Analysis write up
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
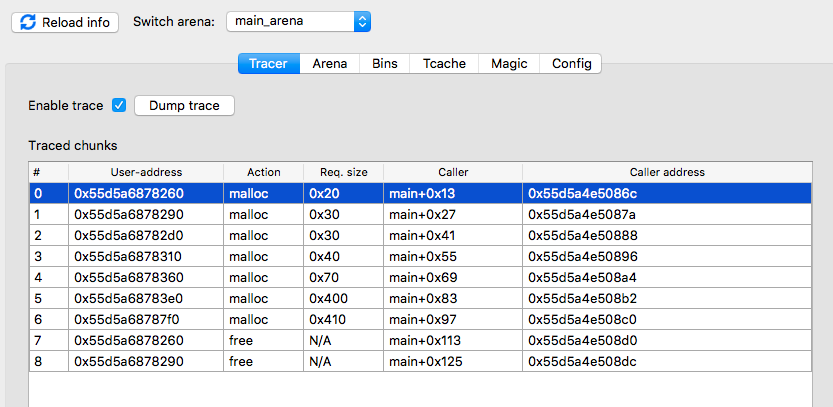 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 fabiobaroni/awesome-exploit-development
A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
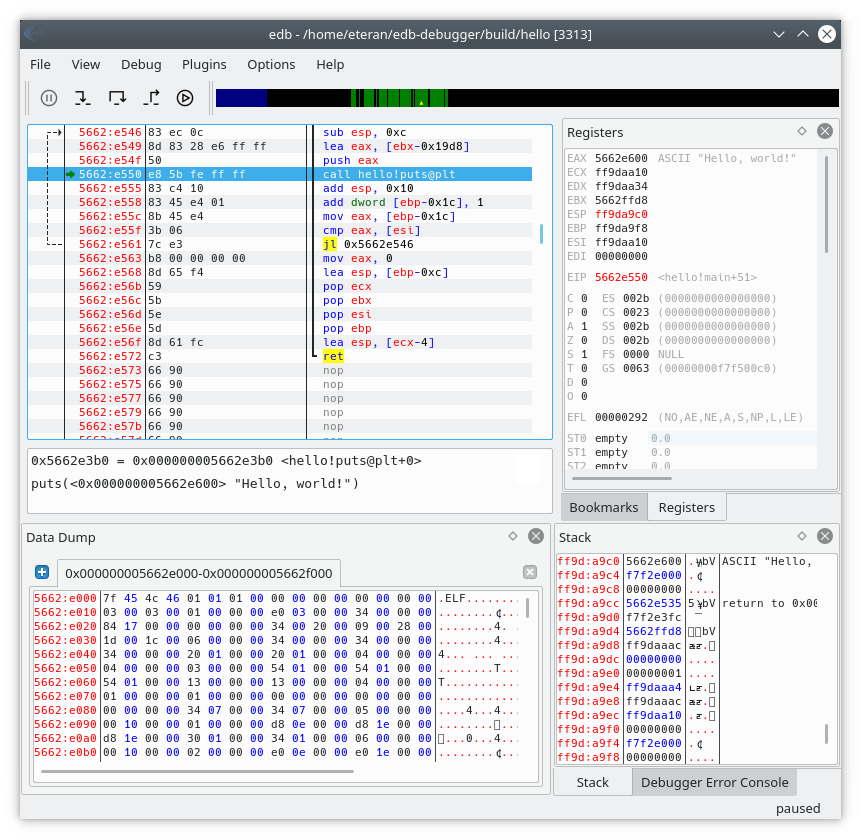 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 illera88/ponce
IDA 2016 plugin contest winner! Symbolic Execution just one-click away!
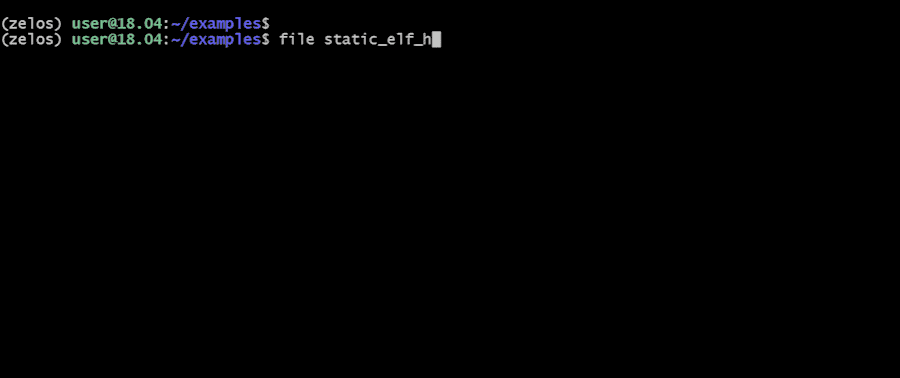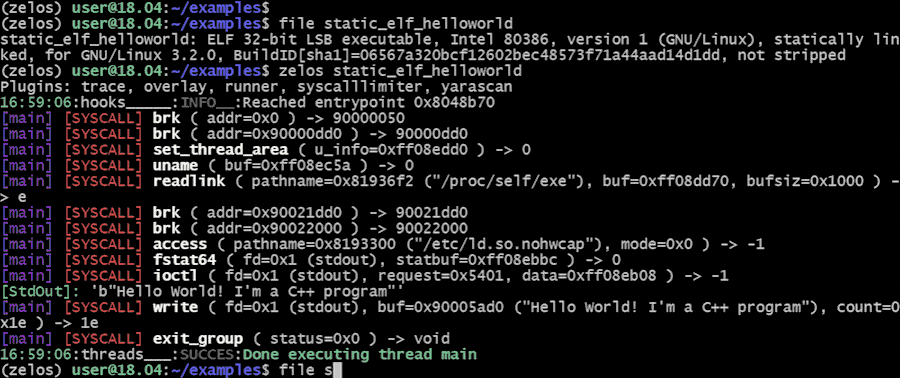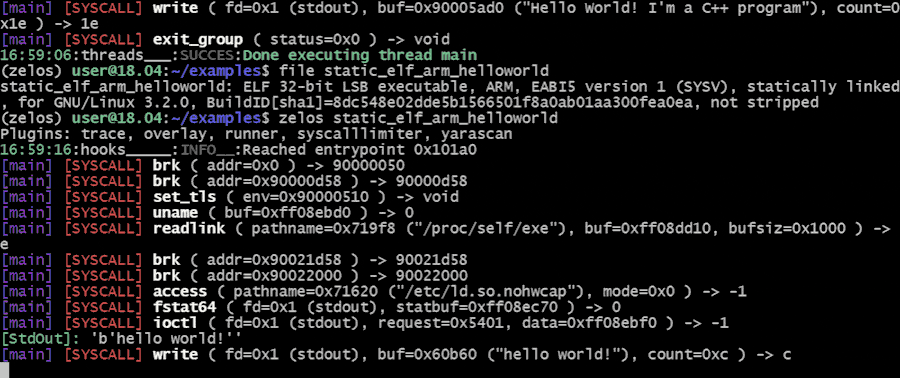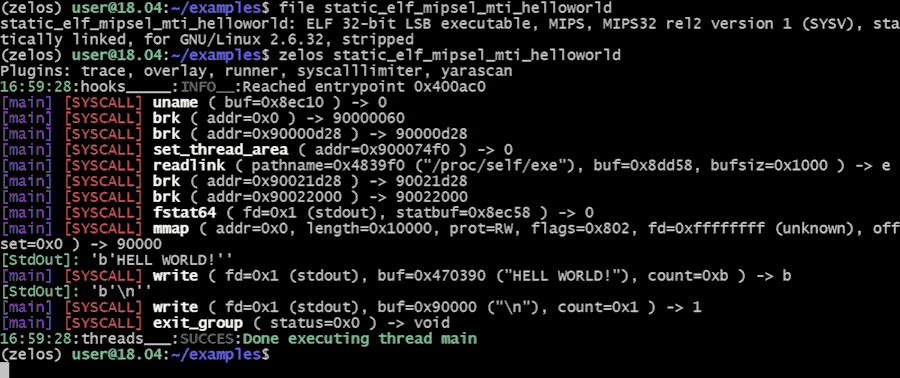 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 hugsy/gdb-static
Public repository of statically compiled GDB and GDBServer
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…