
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
125 results
rsyscall preview

rsyscall

GitHubcatern/rsyscall

Process-independent interface to Linux system calls
binary-analysisdebuggersdynamic-analysis-sandboxing+3
9611 days ago
bochs_linux_kernel_debugging preview

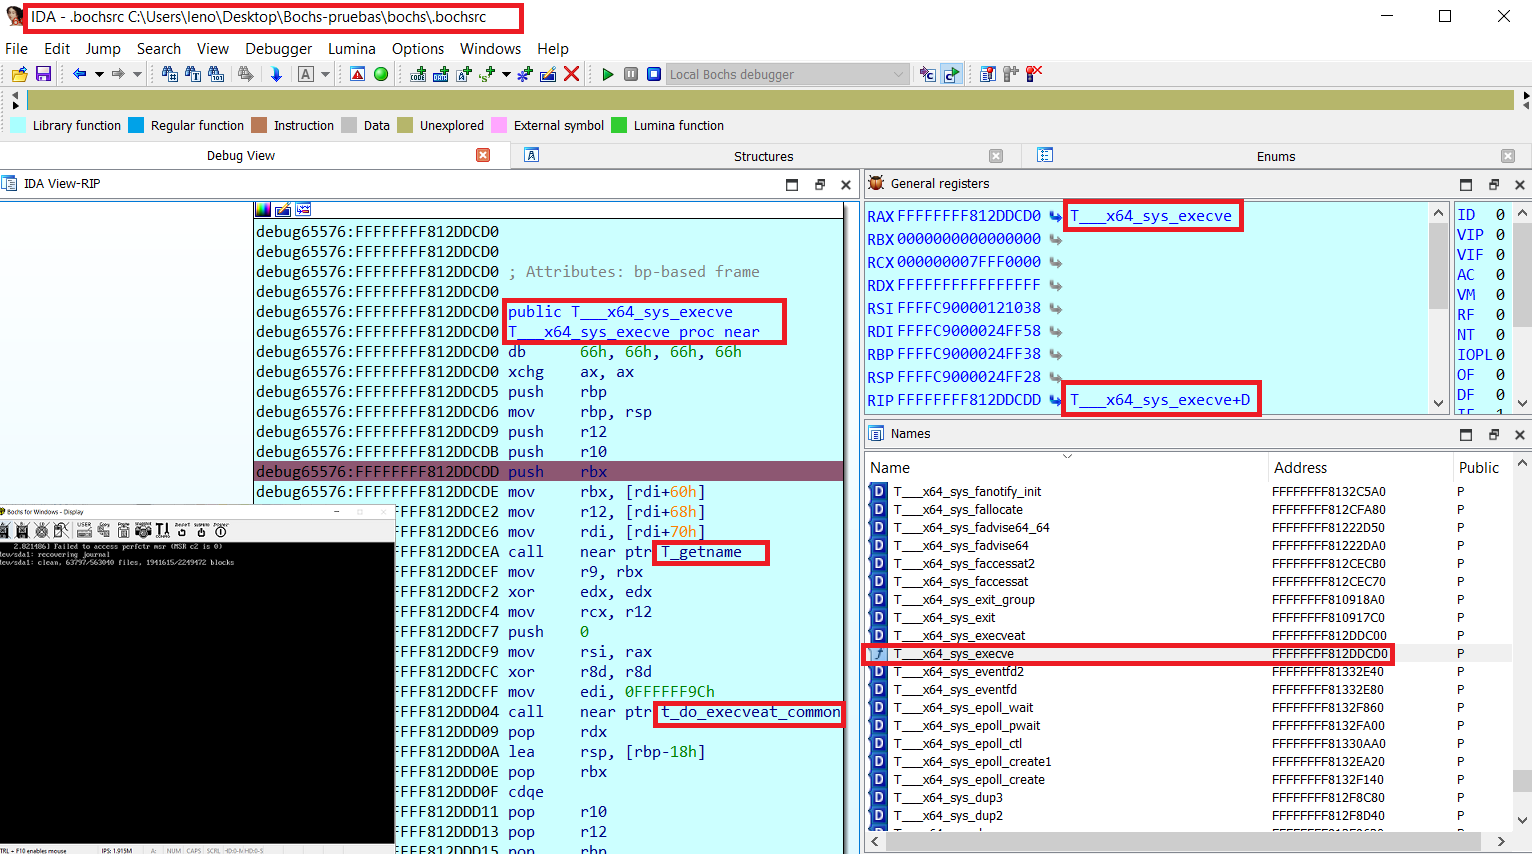
bochs_linux_kernel_debugging

GitHubtherealdreg/bochs_linux_kernel_debugging

Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)

binary-analysisdebuggerseducation+1
333 years ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
253 months ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool
debuggersdynamic-analysis-sandboxingincident-response+2
3.1k4 days ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k1 day ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

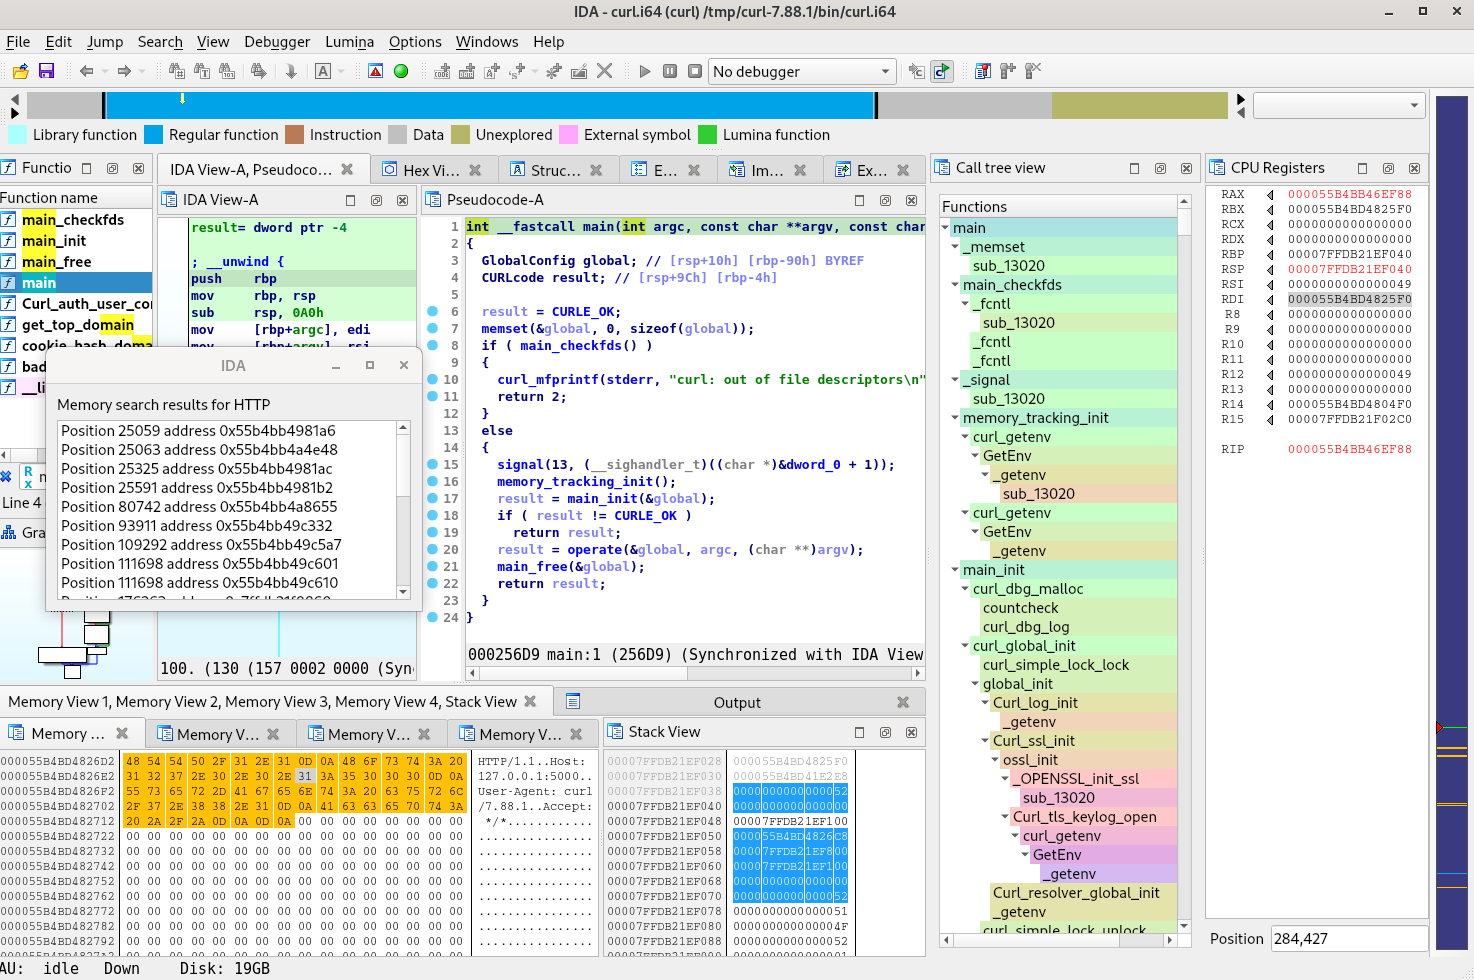
Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.8k10 months ago
frinet preview

frinet

GitHubsynacktiv/frinet

Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
6374 months ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
android-securitybinary-analysisdebuggers+4
7177 months ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

debuggersdynamic-analysis-sandboxingforensics+1
2485 years ago
ceasta preview

ceasta

GitHubngwg/ceasta

disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
16924 days ago
libslub preview

libslub

GitHubnccgroup/libslub

Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…

binary-exploitationdebuggersexploitation+1
1891 year ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
1588 years ago
Learning-Linux-Binary-Analysis preview

Learning-Linux-Binary-Analysis

GitHubpacktpublishing/learning-linux-binary-analysis

Learning Linux Binary Analysis, published by Packt
binary-analysisbinary-exploitationdebuggers+7
893 years ago
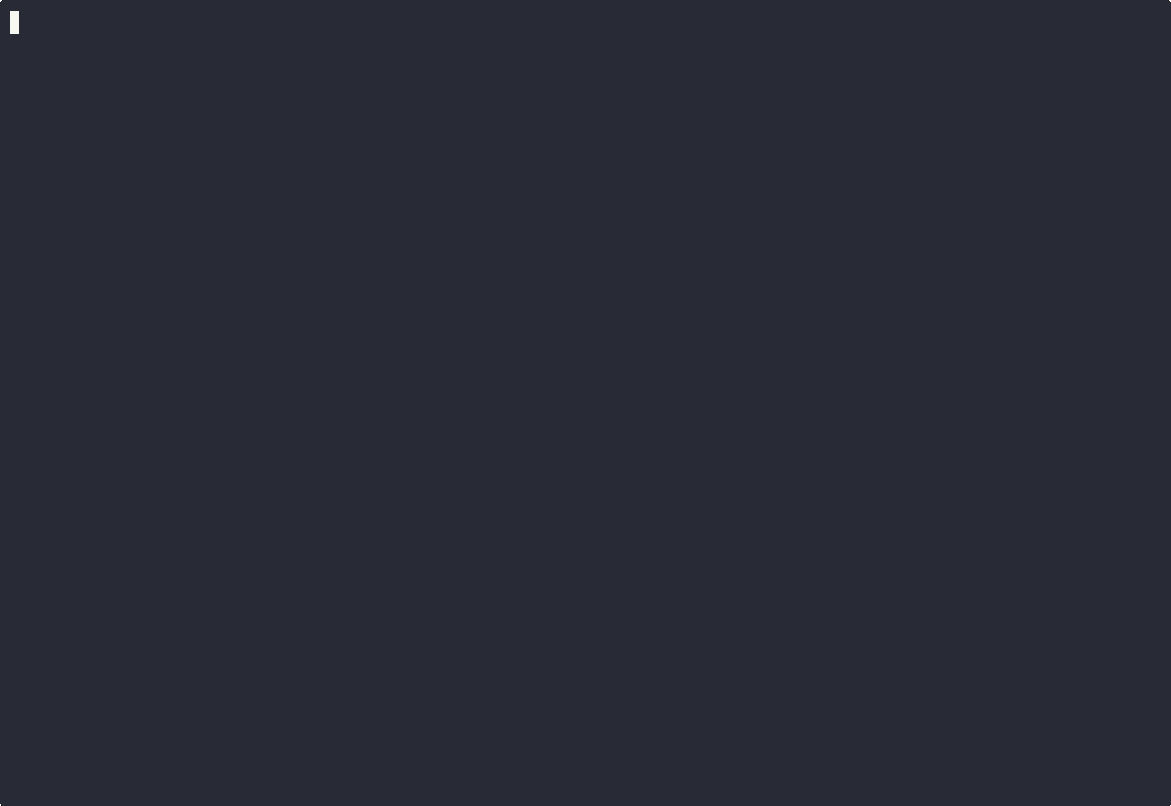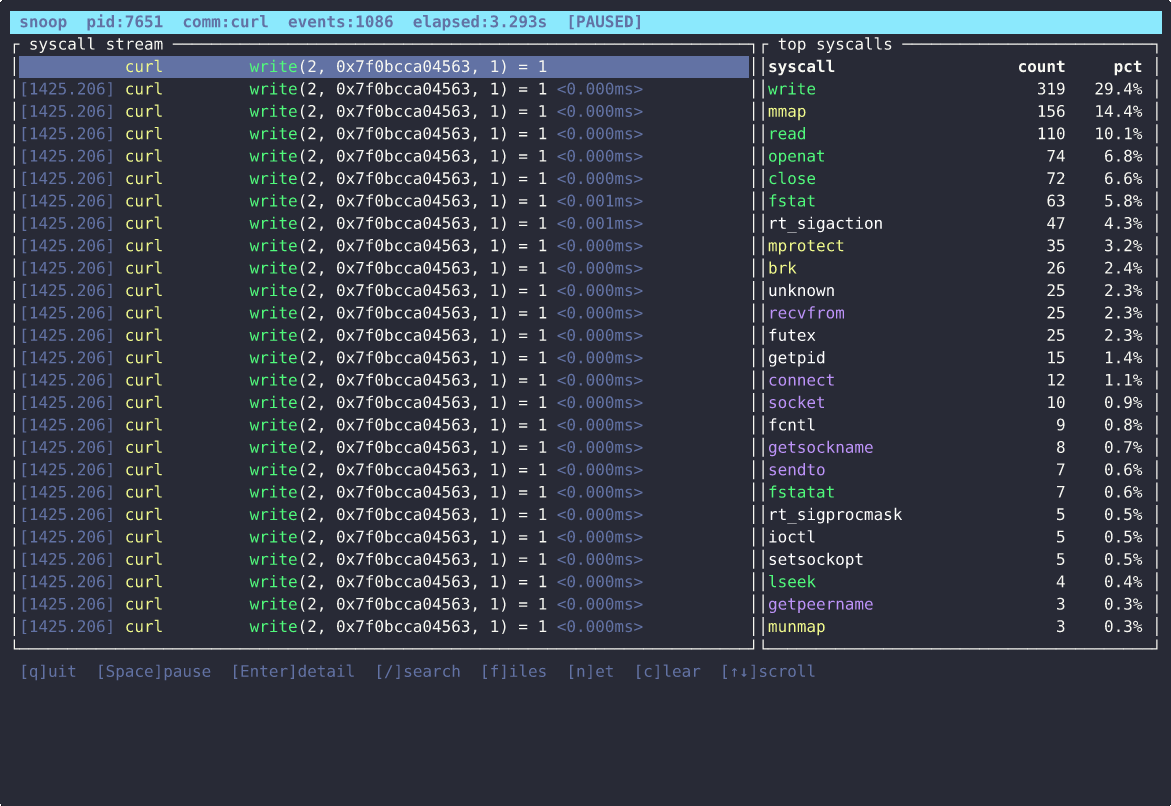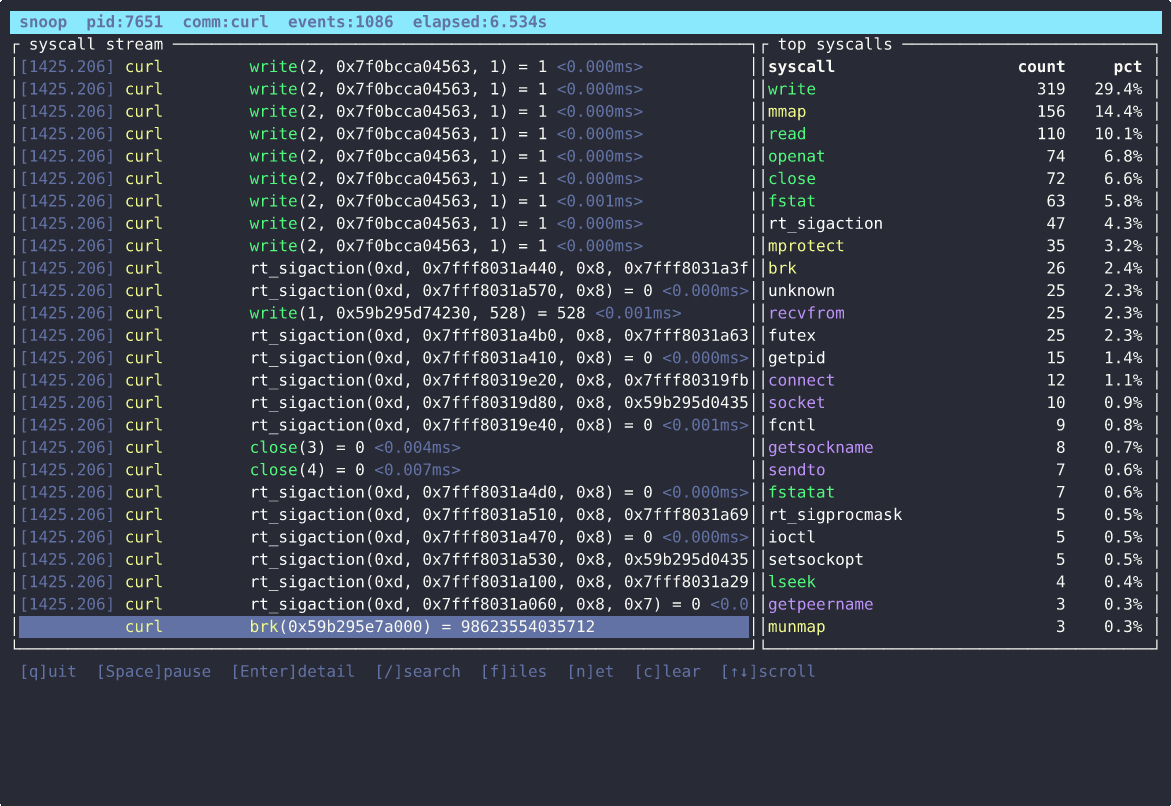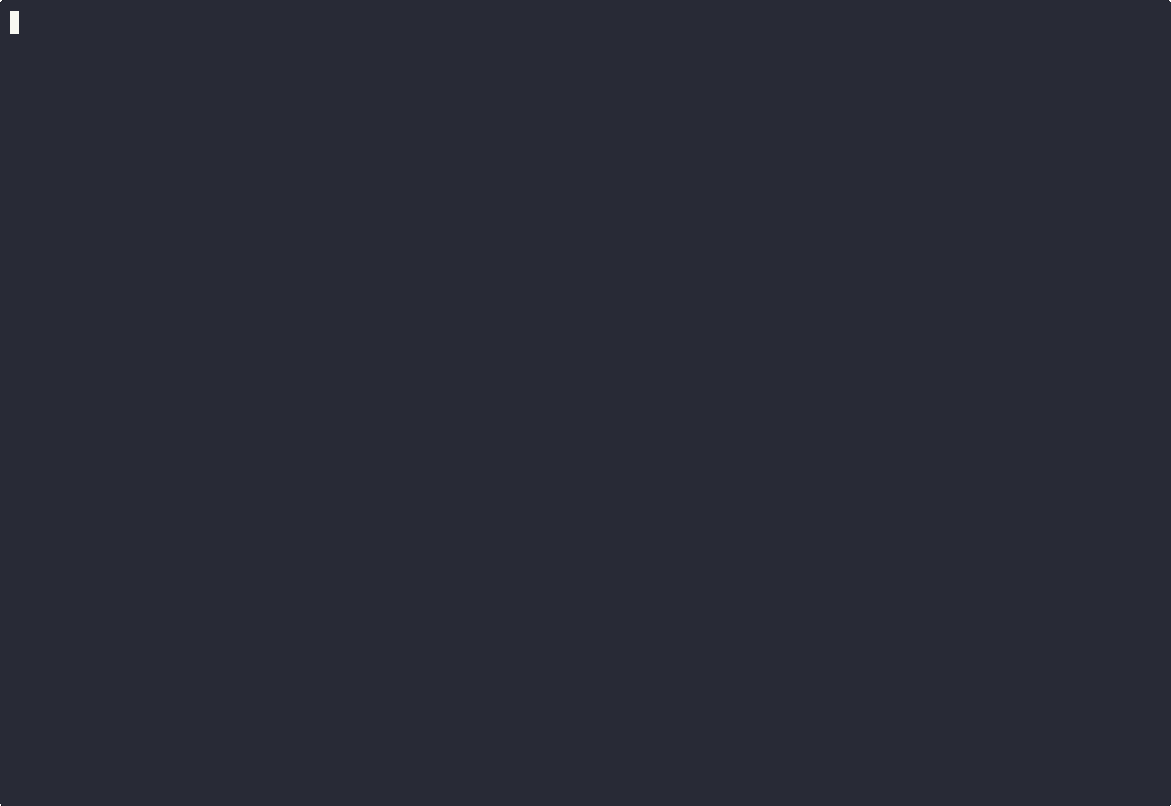
snoop preview

snoop

GitHubpandaadir05/snoop

A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
binary-analysisdebuggersdynamic-analysis-sandboxing+7
2236 months ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux

android-securitybinary-exploitationdebuggers+5
197 years ago
pike-agent preview

pike-agent

GitHubsynacktiv/pike-agent

Experimental Linux strace LLM agent
ai-securitydebuggersdynamic-analysis-sandboxing+5
216 months ago
CVE-2022-27666 preview

CVE-2022-27666

GitHubngtuonghung/cve-2022-27666

Heap buffer overflow exploit for CVE-2022-27666 in Linux kernel IPsec ESP6 implementation. Includes kernel build, debug setup with GDB stub, and…

binary-exploitationdebuggersexploitation+2
5 months ago
Previous1234567Next