
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.7k10 months ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.4k4 months ago
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
43515 days ago
Introspy-iOS preview

Introspy-iOS

GitHubisecpartners/introspy-ios

Security profiling for blackbox iOS

binary-analysisdebuggersdynamic-analysis-sandboxing+5
74010 years ago
BlobRunner preview

BlobRunner

GitHuboalabs/blobrunner

Quickly debug shellcode extracted during malware analysis
debuggersmalware-analysisreverse-engineering+1
6355 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

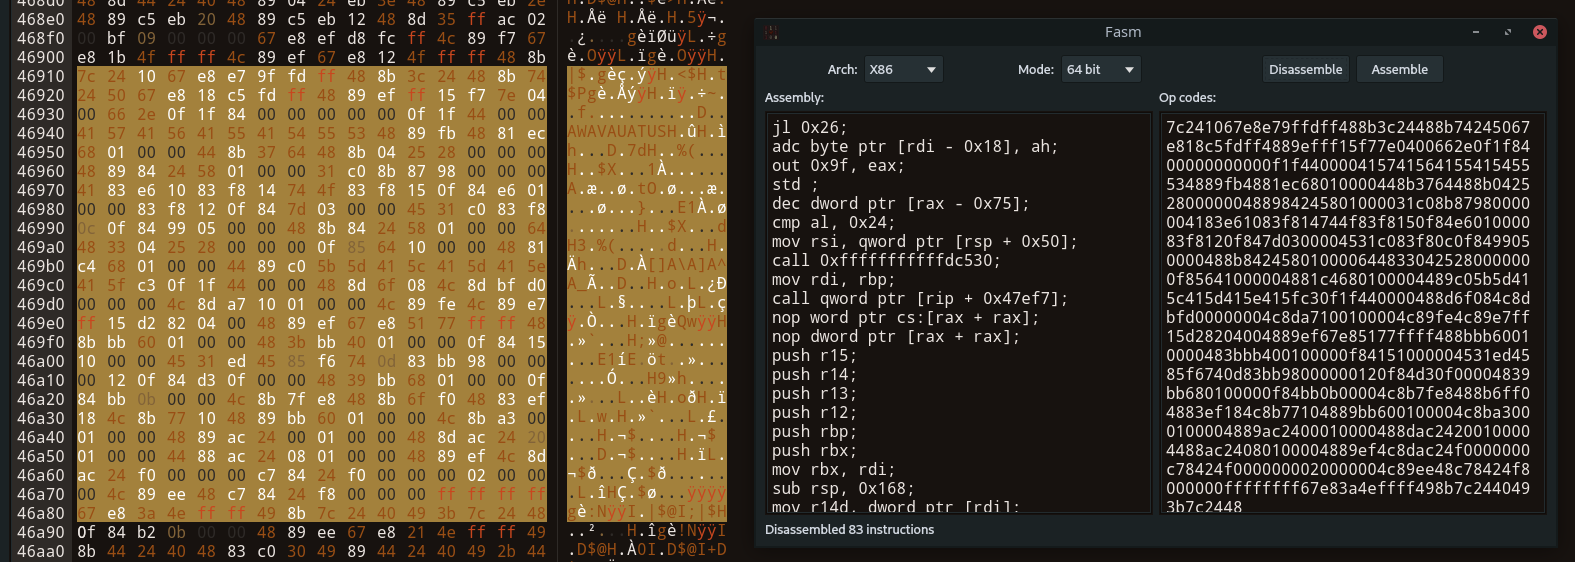
Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
fhex preview

fhex

GitHubecho-devim/fhex

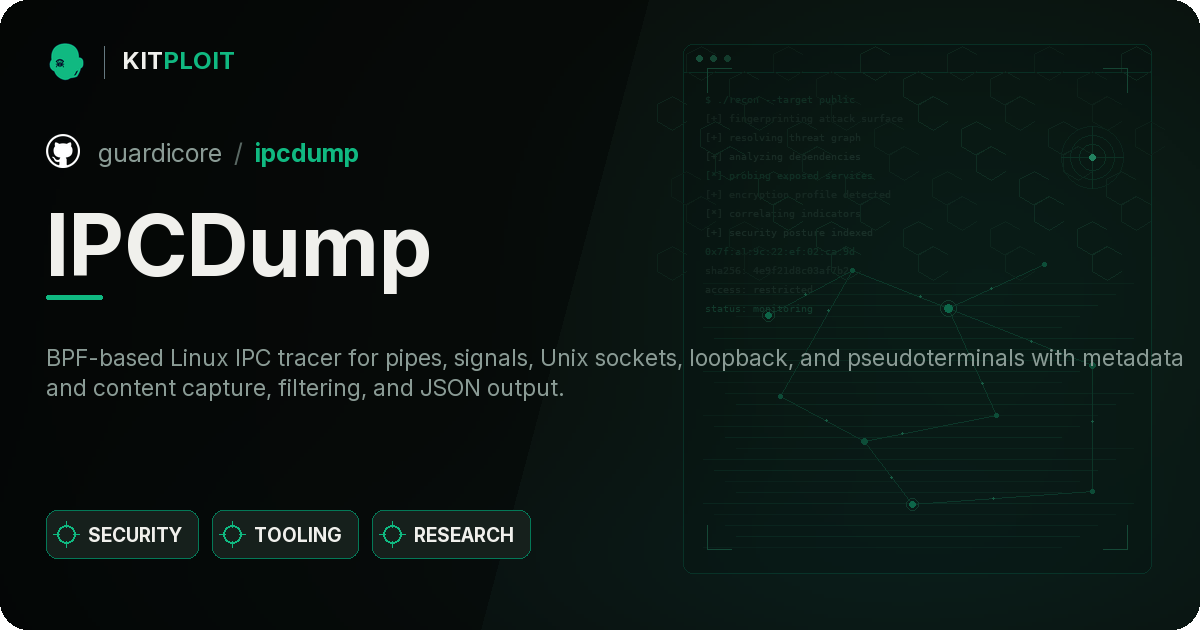
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
binary-analysisdebuggersforensics+2
4371 year ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
debuggersdynamic-analysis-sandboxingforensics+1
2475 years ago
hyperion-disassembler preview

hyperion-disassembler

GitHubsidenai/hyperion-disassembler

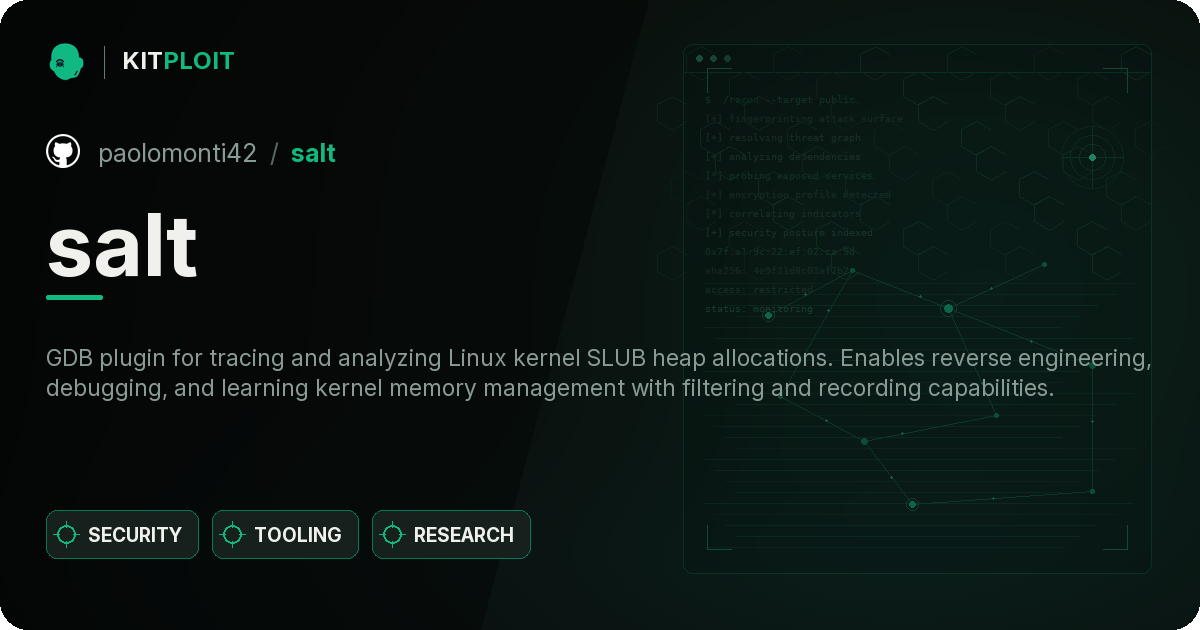
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
binary-analysisdebuggerseducation+5
2044 months ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
1578 years ago
UnconfuserEx preview

UnconfuserEx

GitHubmadmin3r/unconfuserex

Deobfuscator for ConfuserEx 2.
binary-analysisdebuggersmalware-analysis+2
734 months ago
functrace preview

functrace

GitHubinvictus1306/functrace

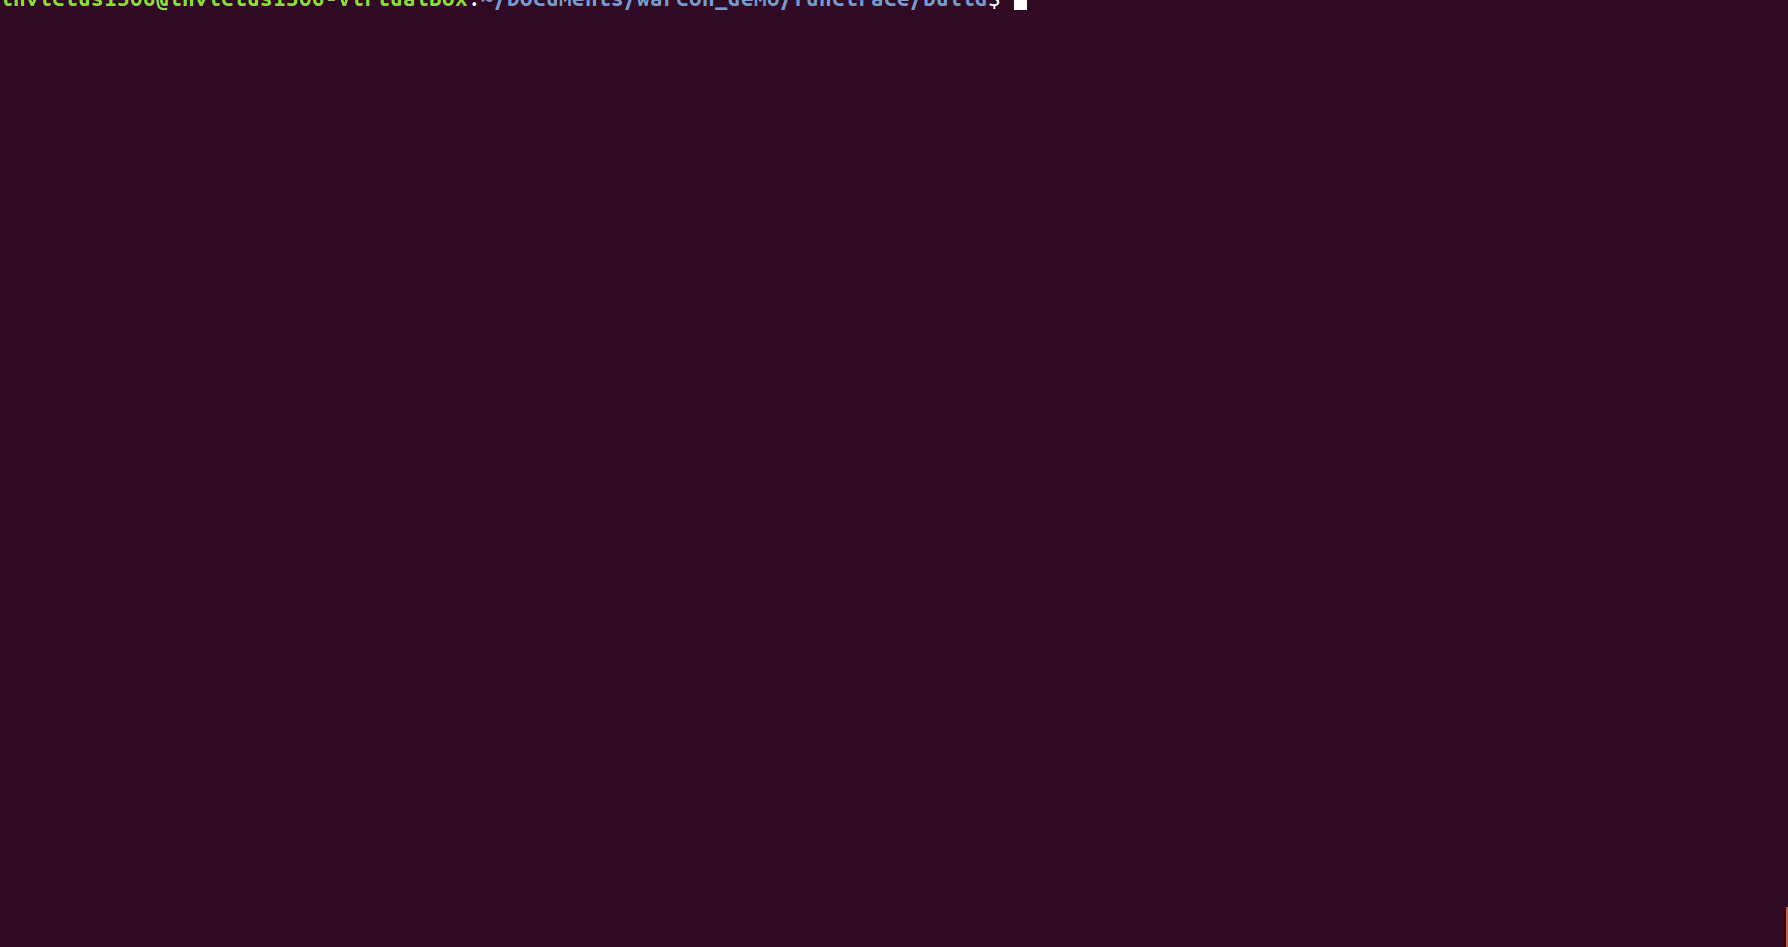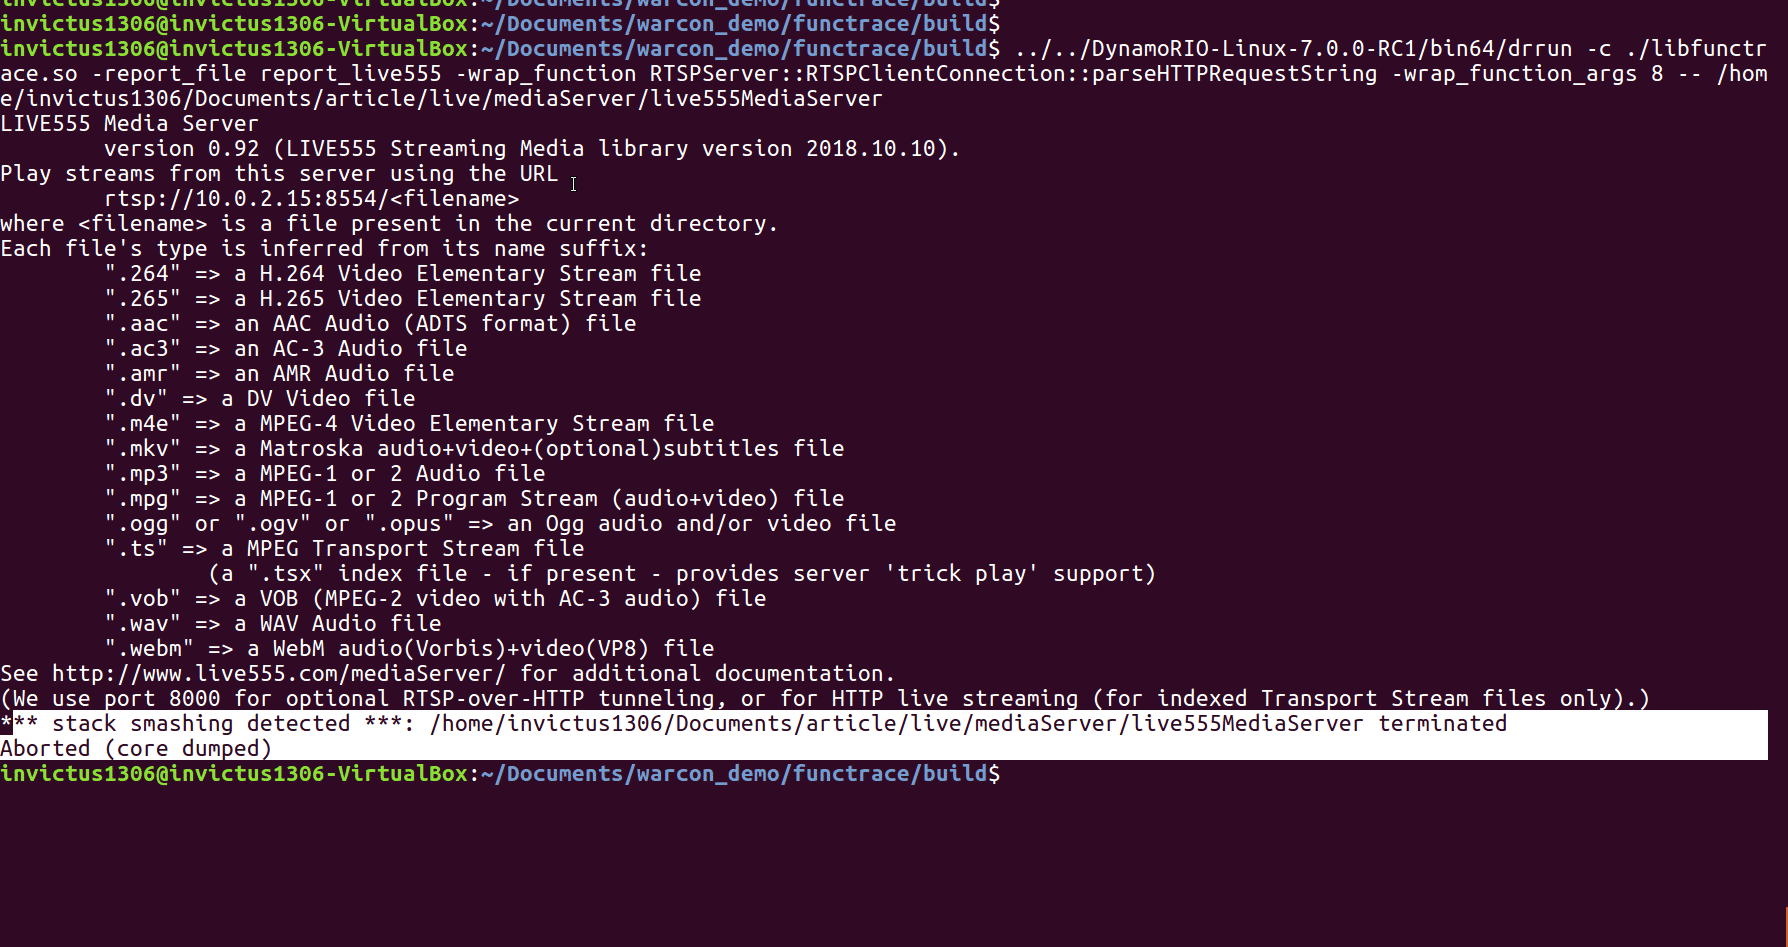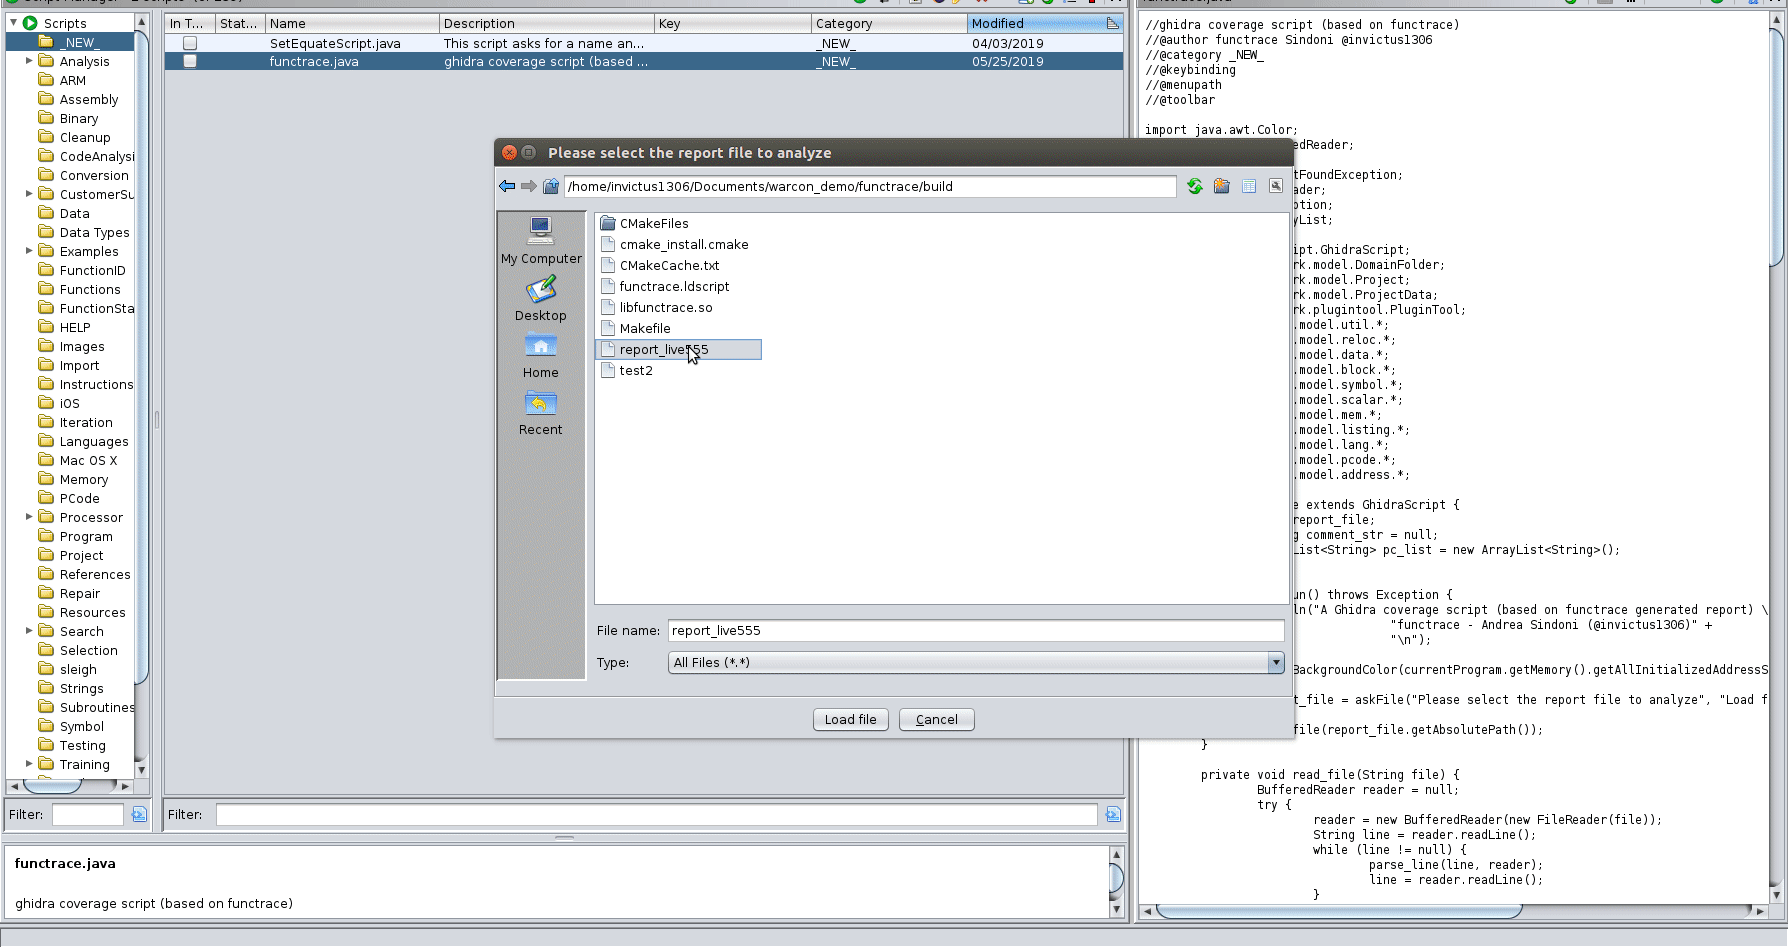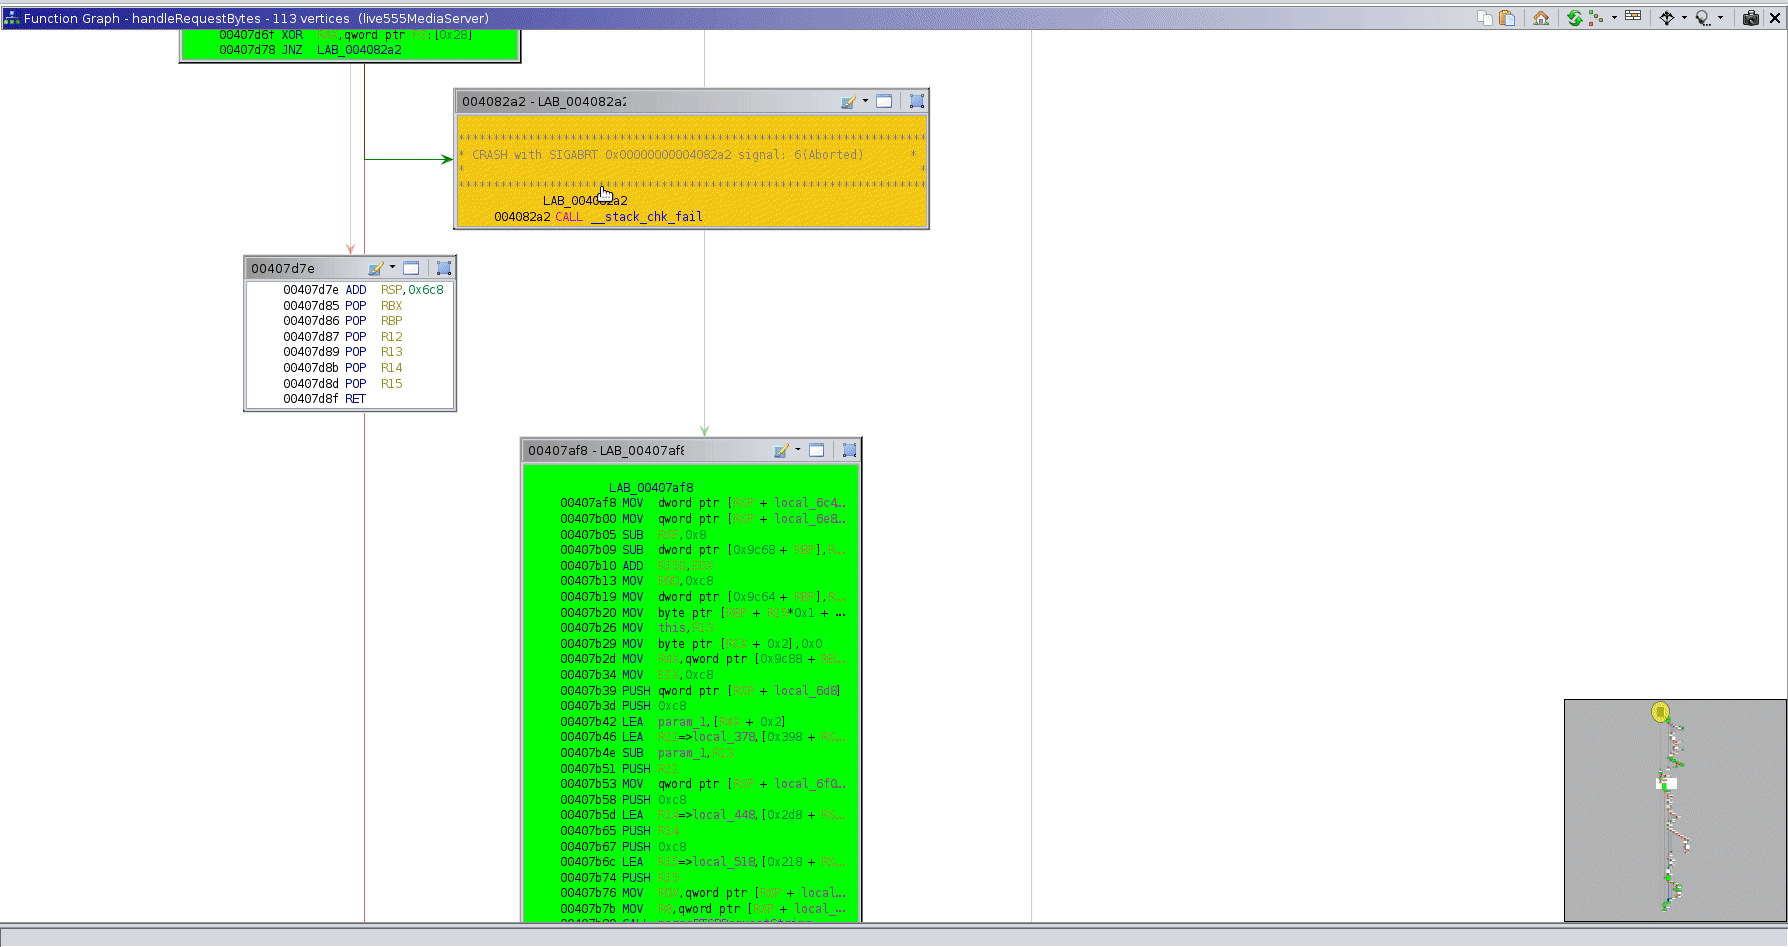
A function tracer
binary-analysisdebuggersdynamic-analysis-sandboxing+2
927 years ago
ebpfmon preview

ebpfmon

GitHubredcanaryco/ebpfmon

Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
debuggersdynamic-analysis-sandboxingutilities-frameworks
903 years ago
YaraVM preview

YaraVM

GitHubmilankovo/yaravm

This repository contains an IDA processor for loading and disassembling compiled yara rules.
binary-analysisdebuggersmalware-analysis+2
531 year ago
dconstruct preview

dconstruct

GitHubdeepquantum/dconstruct

A disassembler & experimental decompiler for TLOU2 DC Scripts.

binary-analysisdebuggersfirmware-analysis+2
231 month ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
204 months ago
CaptainHook preview

CaptainHook

GitHubsynacktiv/captainhook

Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
binary-analysiscode-analysisdebuggers+2
94 years ago
ASM-Obfuscator preview

ASM-Obfuscator

GitHubgmh5225/asm-obfuscator

Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…

binary-analysisdebuggersdefensive-tools+1
73 years ago
Previous1234Next