android-kernel-exploitation-lab

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

Cisco RV110w UPnP stack overflow

How to set up 2 VirtualBox VM to debug kernel driver using windbg

Enable Microsoft PDB support in Ghidra without installing Visual Studio

Heap analysis tooling for ptmalloc

A disassembler & experimental decompiler for TLOU2 DC Scripts.

Heap analysis tooling for dlmalloc

A game modding utility that makes injecting C/C++ code easier.

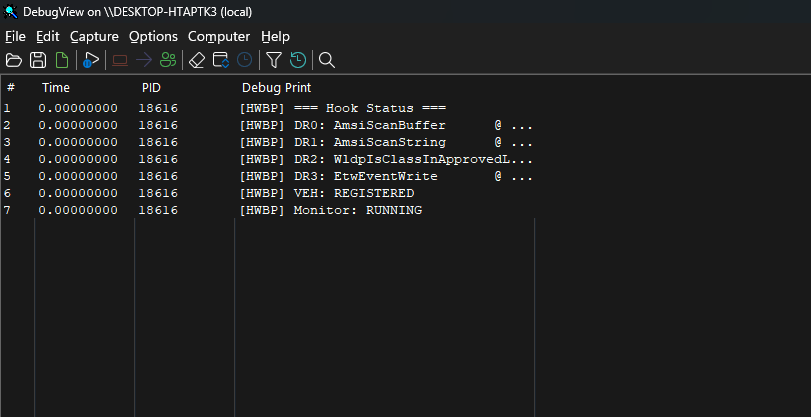
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).

WinDbg plugin to trace module transitions from a debugged driver.

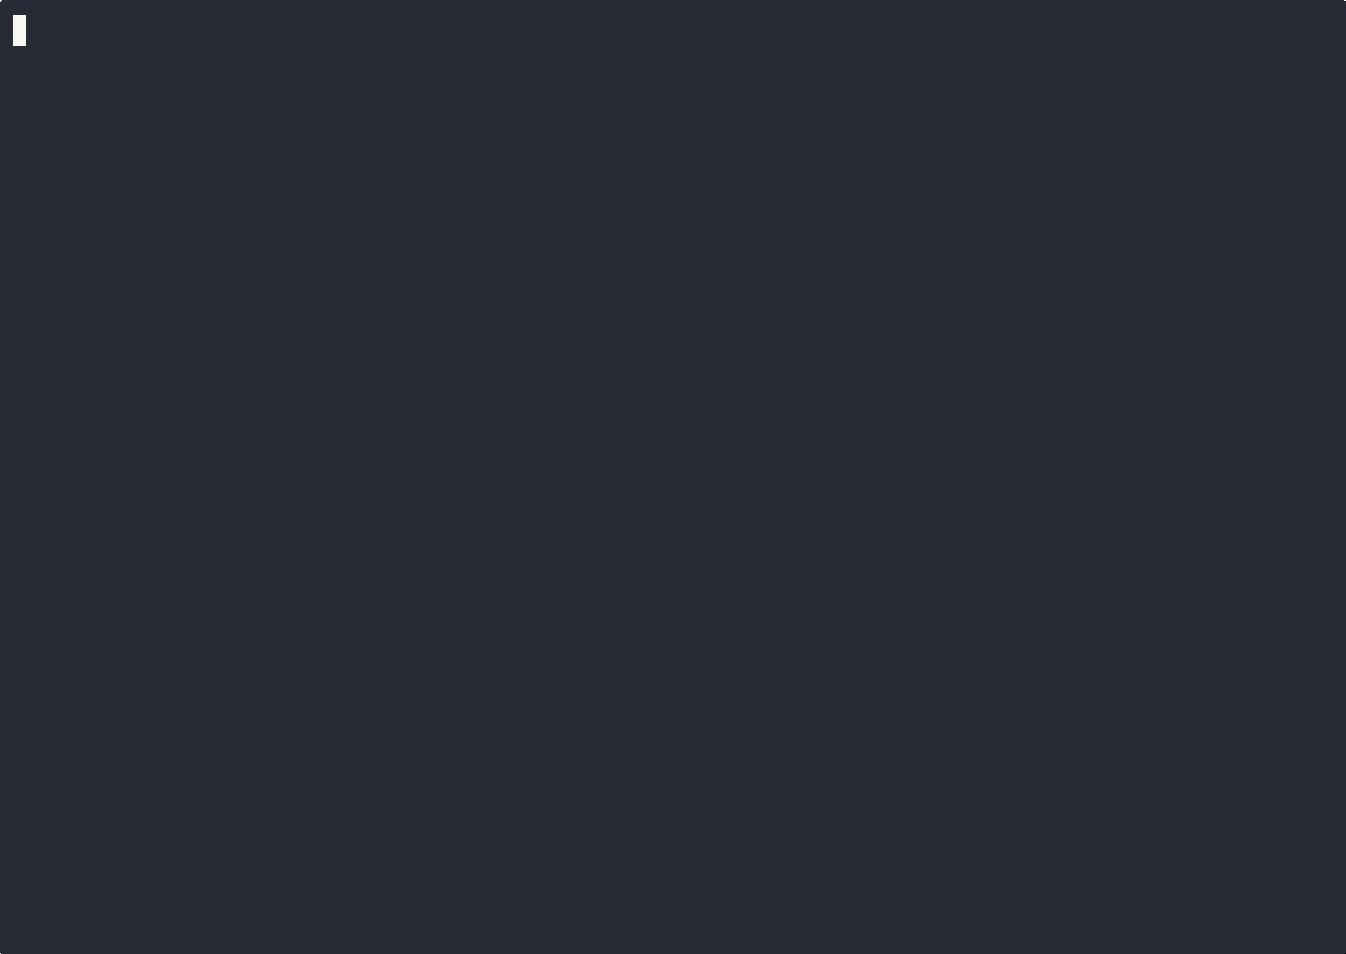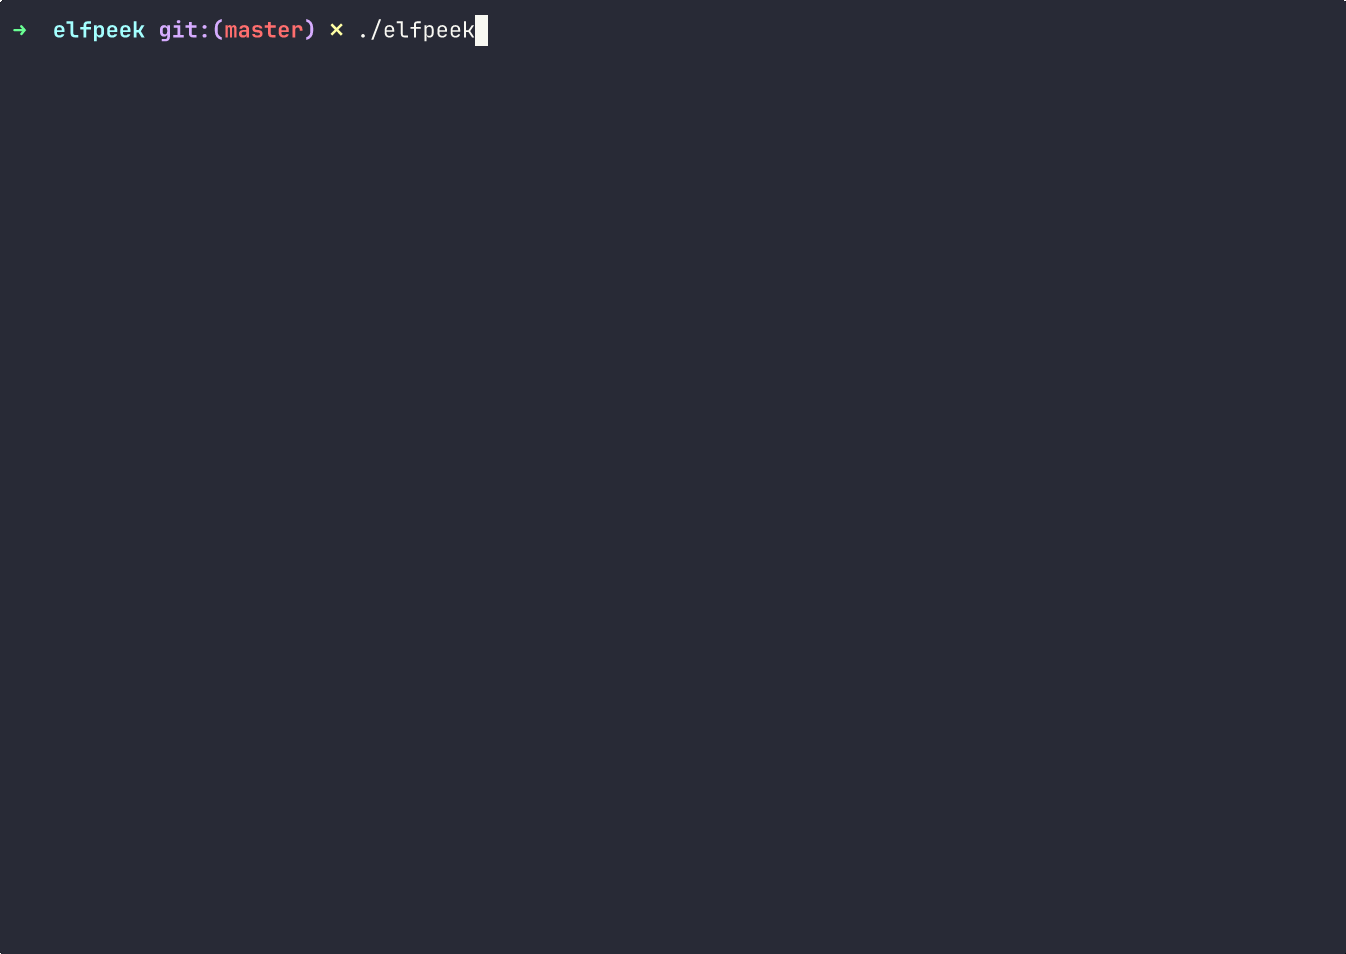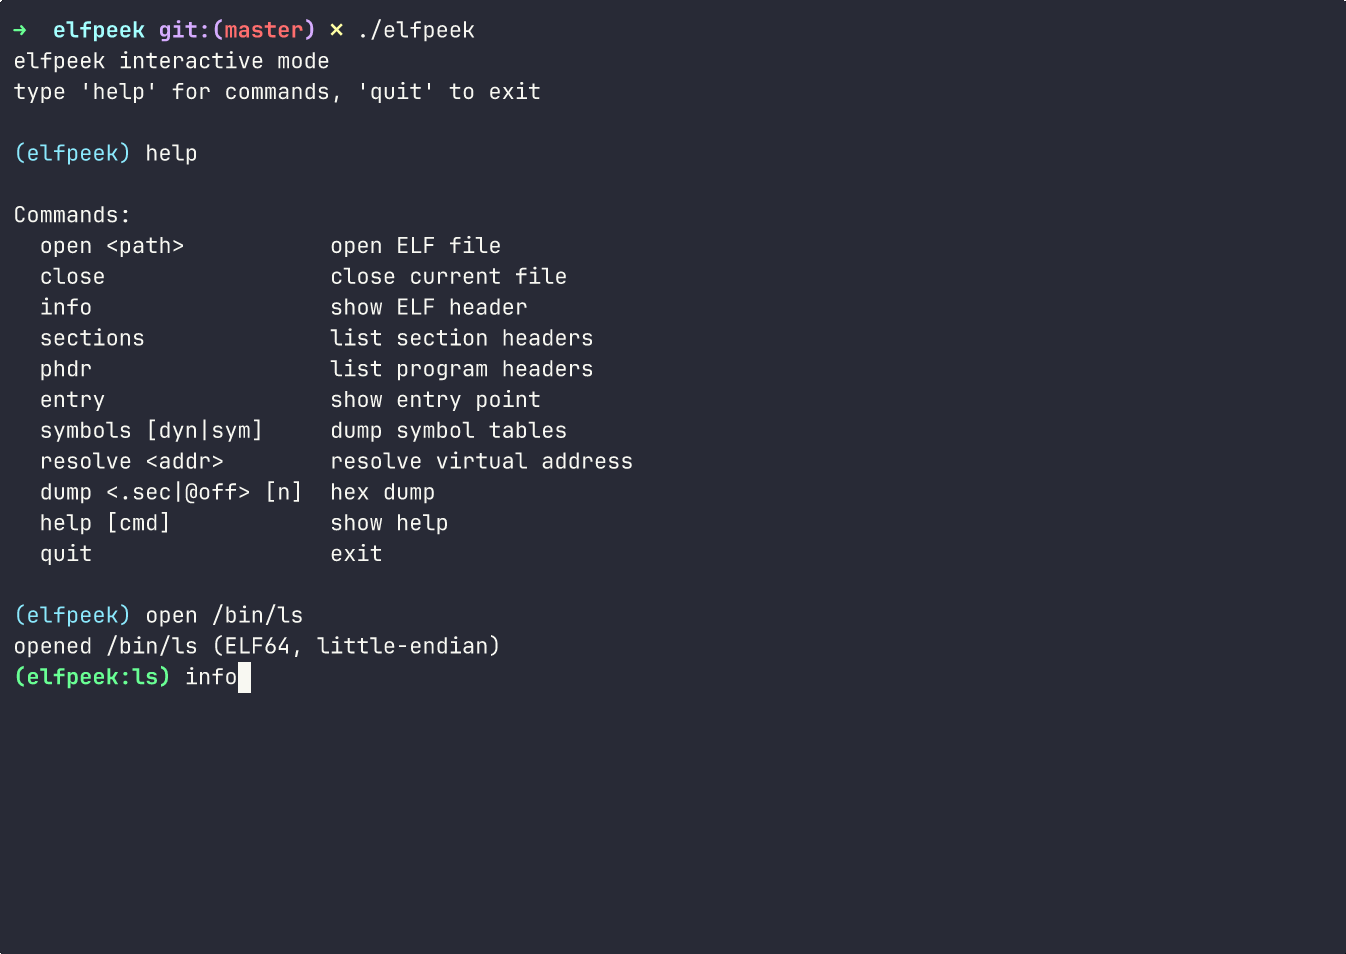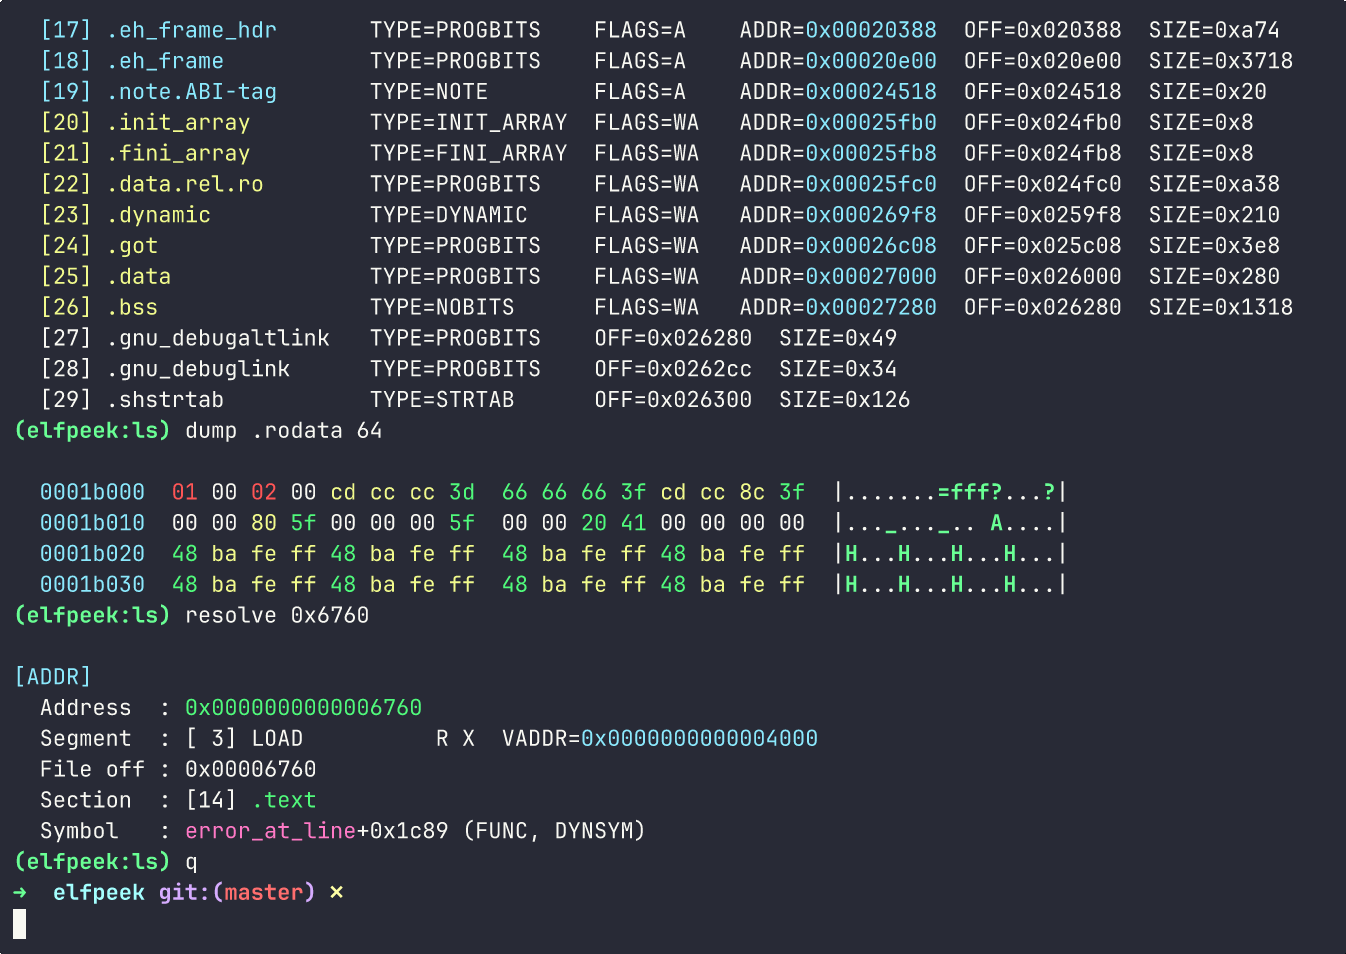
Minimal ELF inspector written in C for quick binary layout inspection

1day research effort

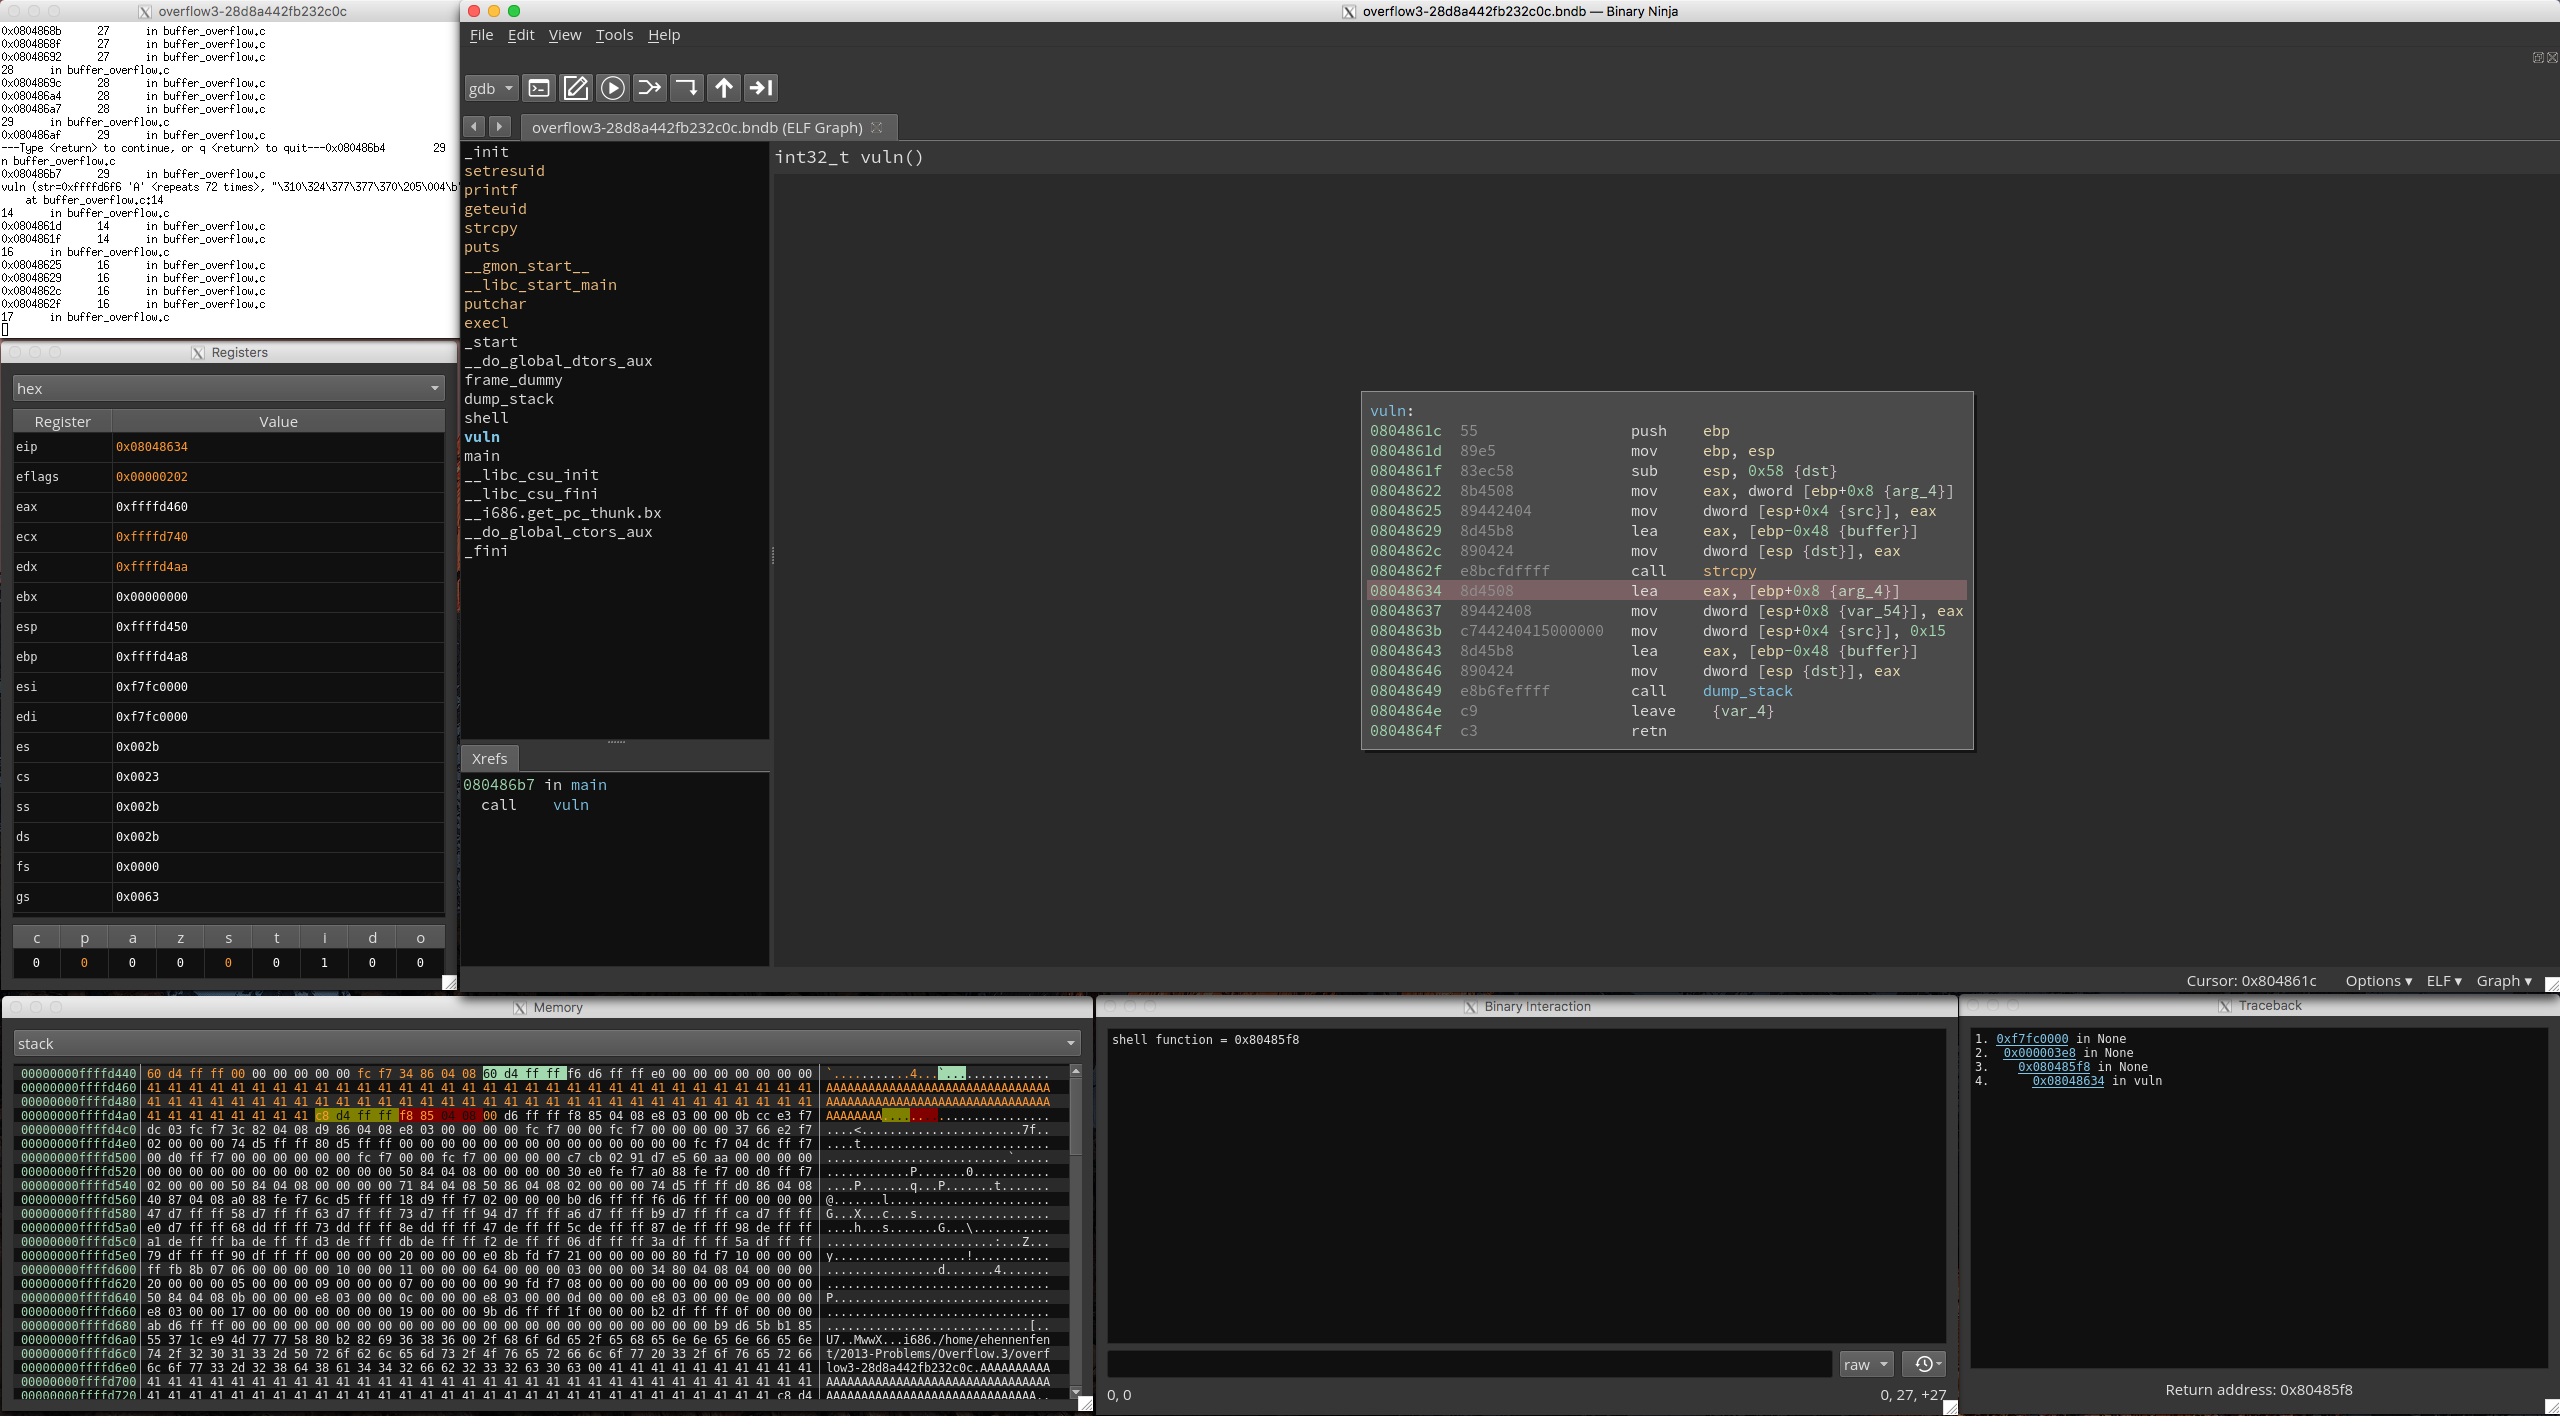
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…

MCP server for automated binary diffing.

This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.

Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241

reverse engineering, visual binary analysis