
Archived
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
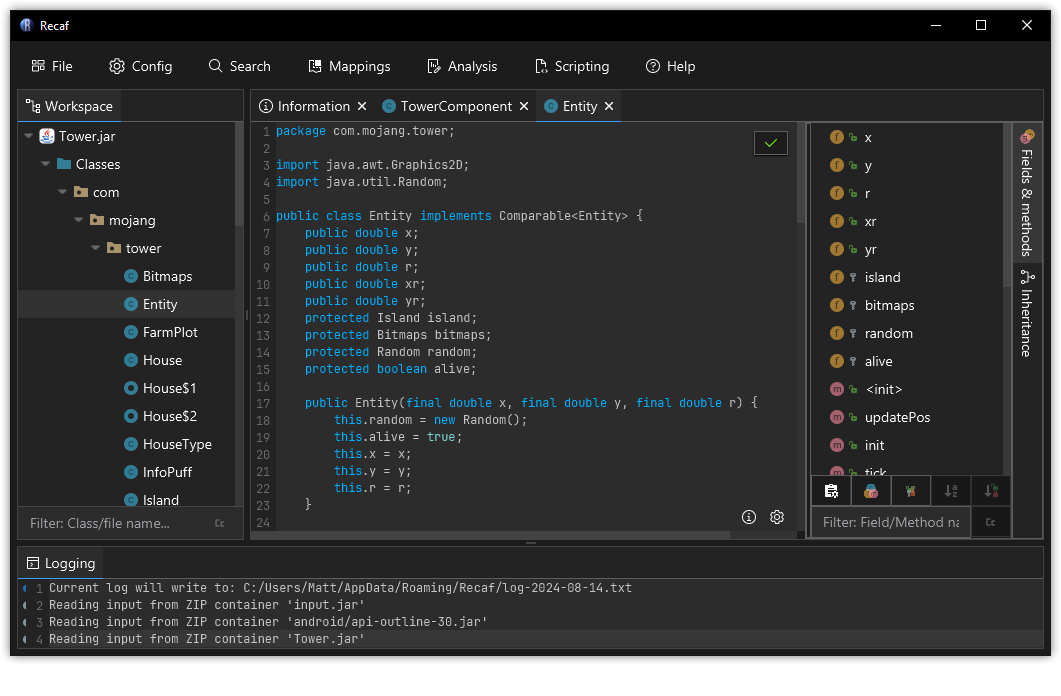
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
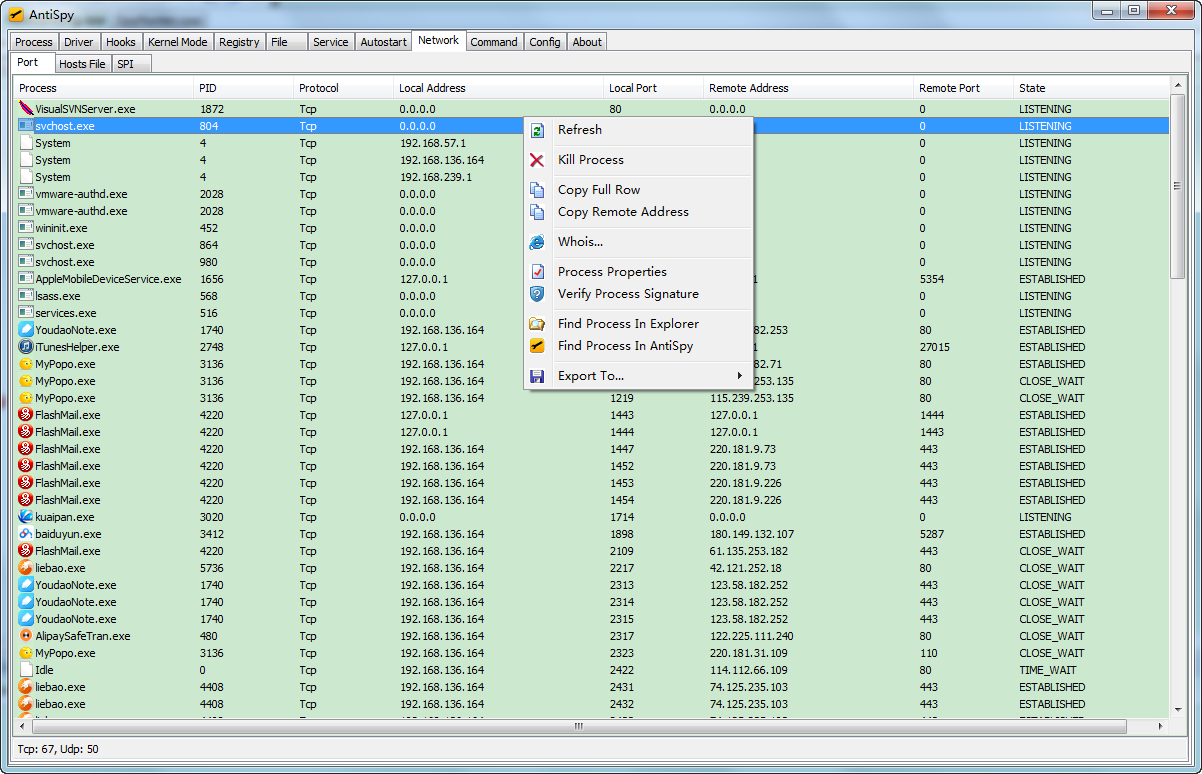 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
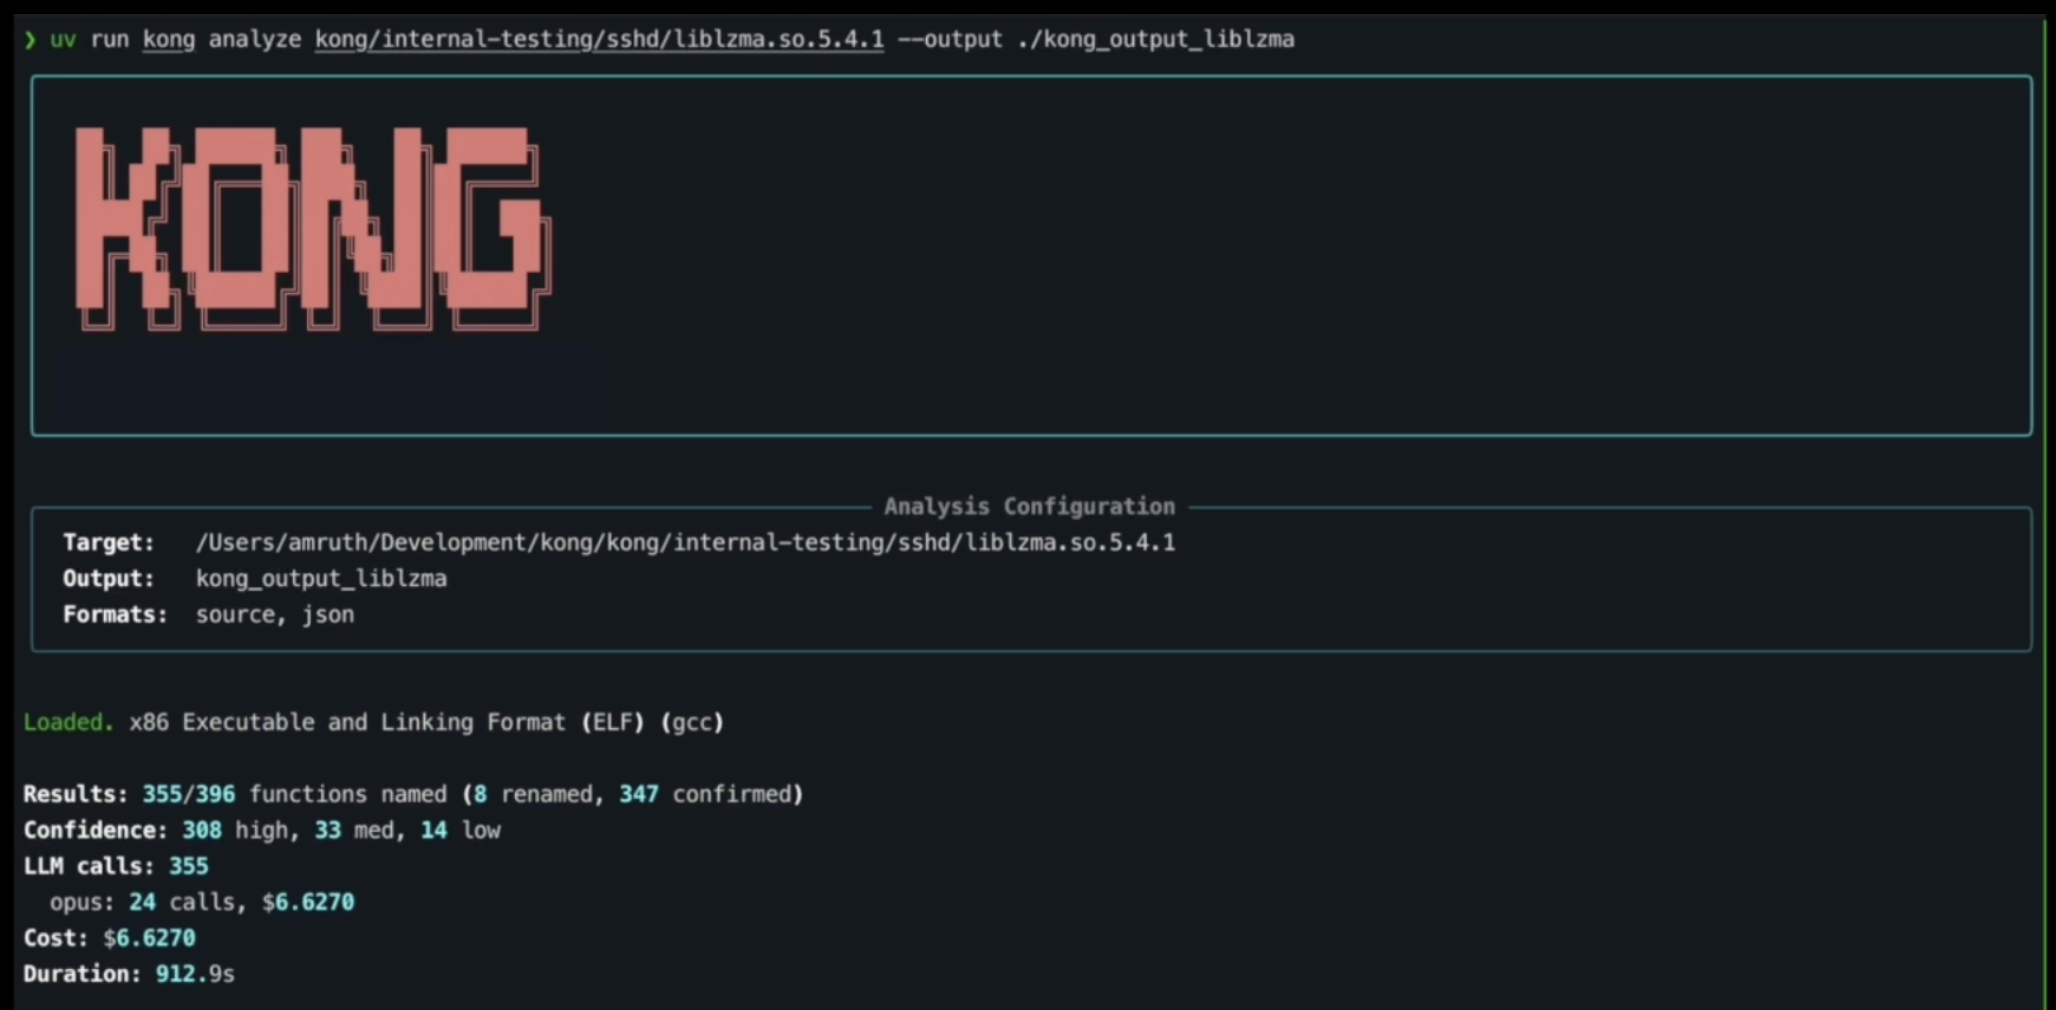 amruth-sn/kong
The world's first agentic reverse engineer.