
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
r0ak preview

r0ak

GitHubharryanon/r0ak

Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
binary-exploitationdebuggersexploitation+5
1088 years ago
r2web preview

r2web

GitHubradareorg/r2web

Access radare2 from anywhere, anytime.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
5128 days ago
lst2x64dbg preview

lst2x64dbg

GitHubutkonos/lst2x64dbg

Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
binary-analysisdebuggersreverse-engineering+1
1142 years ago
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
debuggersdynamic-analysis-sandboxingembedded-systems-security+7
852 months ago
cdb preview

cdb

GitHubpownjs/cdb

Automate common Chrome Debug Protocol tasks to help debug web applications from the command-line and actively monitor and intercept HTTP requests and…
debuggersnetwork-mappingpenetration-testing+2
725 years ago
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection

binary-analysisdebuggersdefensive-tools+1
272 months ago
drvtrace preview

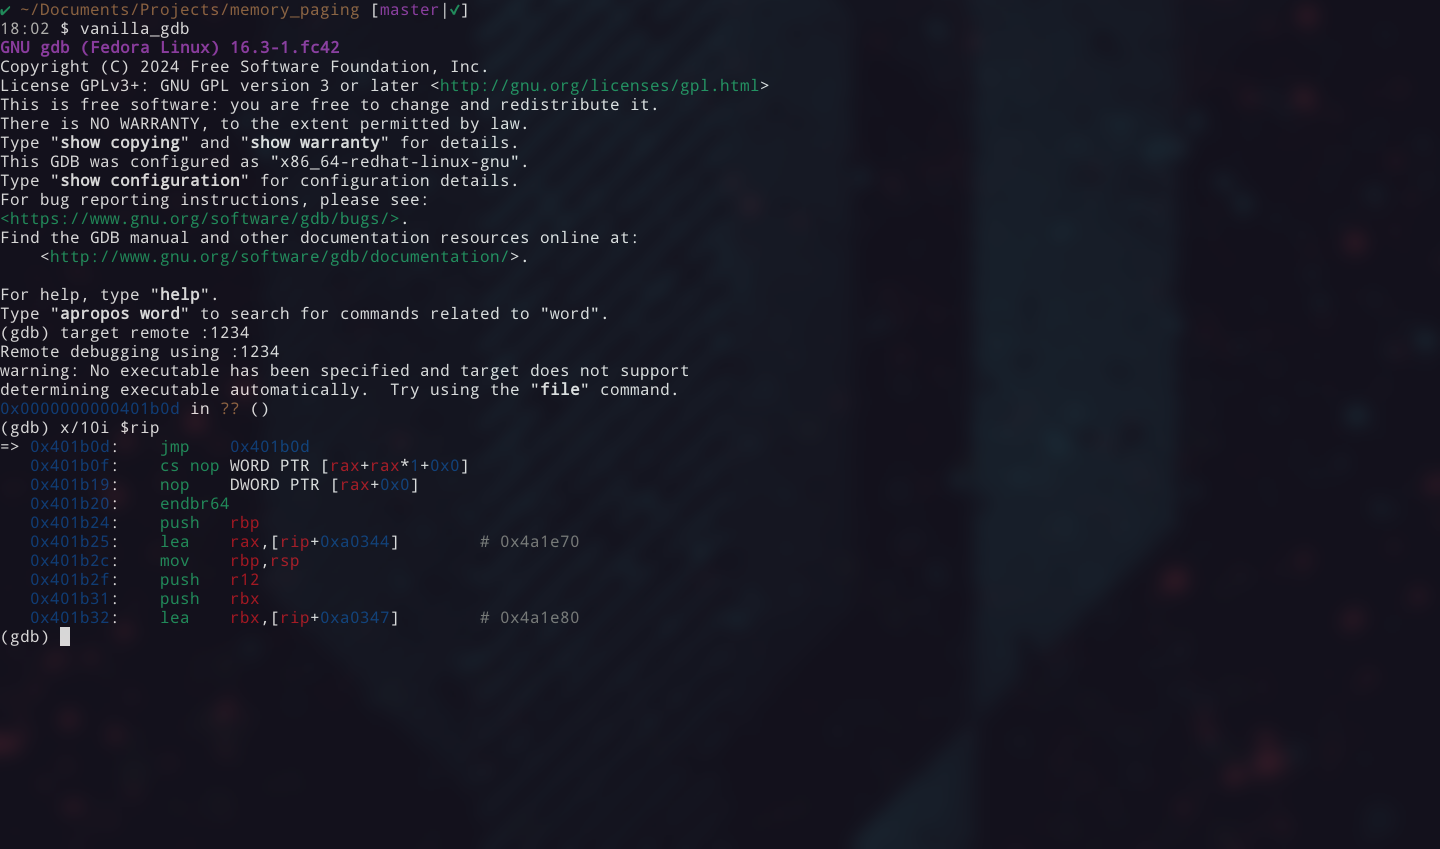
drvtrace

GitHubeversinc33/drvtrace

WinDbg plugin to trace module transitions from a debugged driver.
binary-analysisdebuggersreverse-engineering
5410 months ago
page_table_walk preview

page_table_walk

GitHubjazho76/page_table_walk

Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
287 months ago
CVE-2023-6241-Pixel7_Adaptation preview

CVE-2023-6241-Pixel7_Adaptation

GitHubilgobbo00/cve-2023-6241-pixel7_adaptation

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241

android-securitybinary-exploitationdebuggers+5
141 year ago
xtride preview

xtride

GitHubpr0me/xtride

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…

binary-analysisdebuggerseducation+5
264 months ago
LetMeGG preview

LetMeGG

GitHubgmh5225/letmegg

Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…

anti-botbinary-analysisdebuggers+1
154 years ago
hermit preview

hermit

GitHubxv4l3x/hermit

Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitybinary-analysiscode-analysis+7
721 days ago
Linksys-WRT54GL-Exploitation preview

Linksys-WRT54GL-Exploitation

GitHubumbertodellamonica/linksys-wrt54gl-exploitation

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

binary-analysisdebuggerseducation+9
25 months ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
binary-analysisdebuggersexploitation+3
28 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubcharlyrr/cve-2025-5548

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…

binary-exploitationdebuggerseducation+7
7 months ago
flare-ida preview
Archived

flare-ida

GitHubmandiant/flare-ida

IDA Pro utilities from FLARE team
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.5k2 years ago
Transformers-Forged-To-Fight-Offline-Version preview

Transformers-Forged-To-Fight-Offline-Version

GitHubgeamztheangrybirds727/transformers-forged-to-fight-offline-version

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…

binary-analysisbinary-exploitationcurated-resources+5
24 months ago
Previous1234Next