
idenLib
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]
binary-analysisdebuggersmalware-analysis+2
395
secrary/idenlibidenLib - Library Function Identification [This project is not maintained anymore]
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra
 ypl6/heaplens
CMPT733 Cybersecurity Lab II Project: GDB plugin for heap exploits inspired by CVE-2021-3156
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
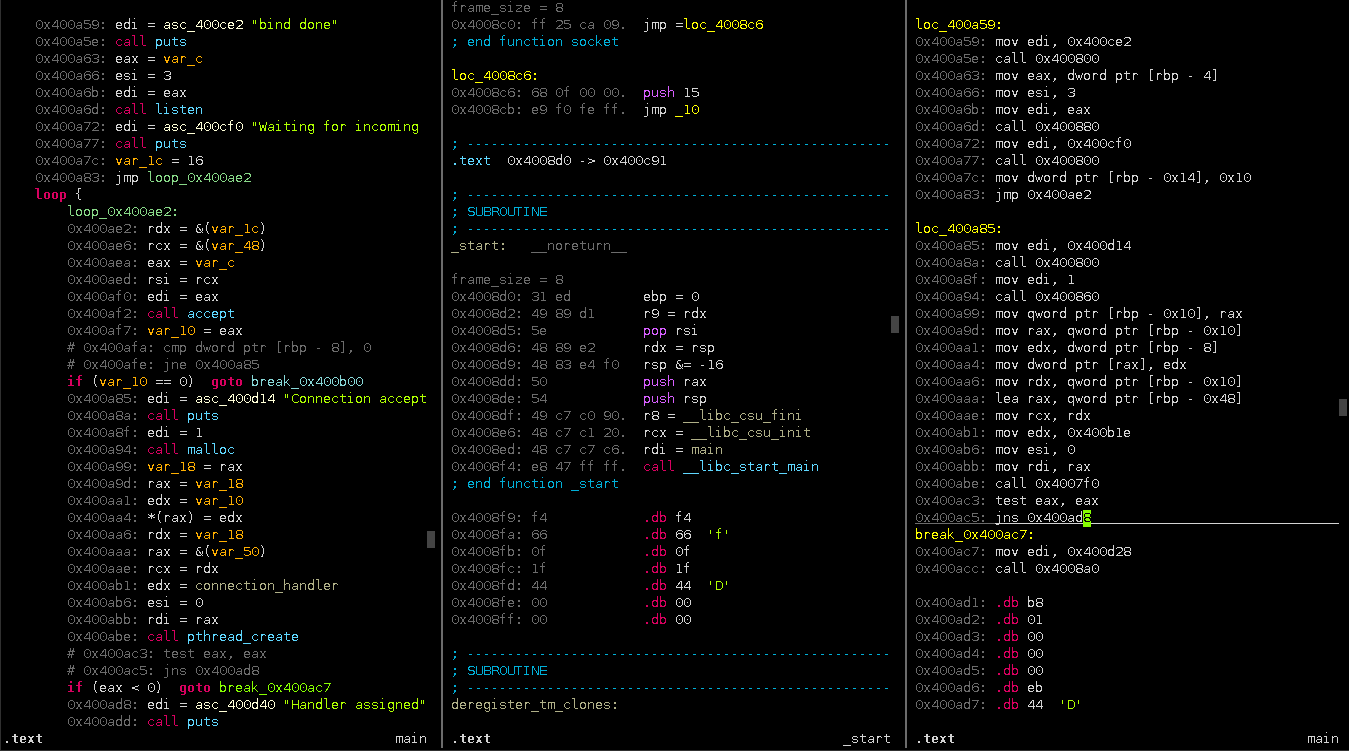 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
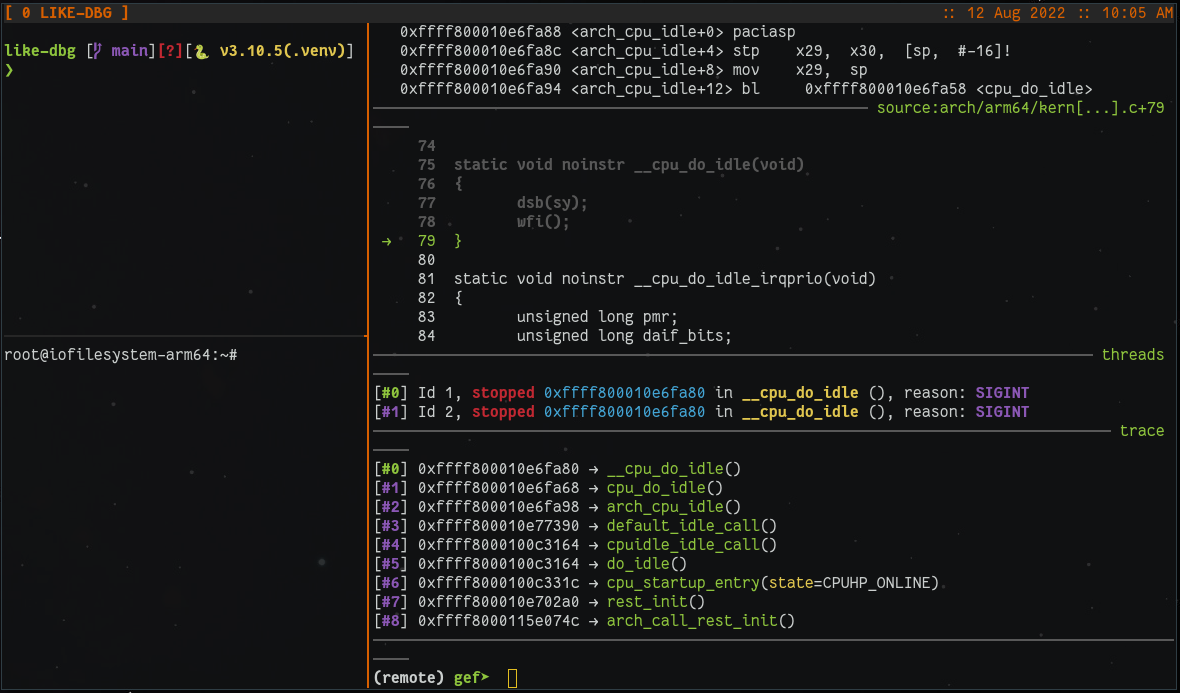 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
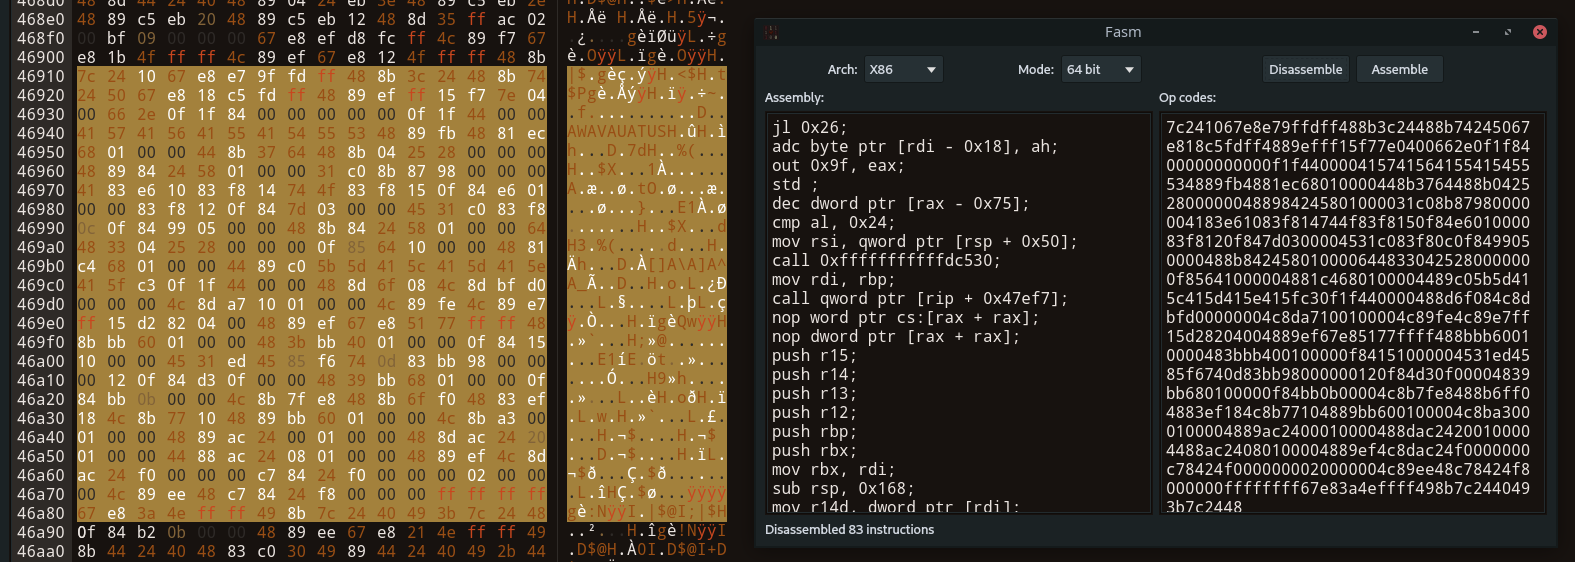 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 backengineering/themida-devirt
Themida Devirt Results
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…