

qiling
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
binary-analysisdebuggersdynamic-analysis-sandboxing+7
qilingframework/qilingA True Instrumentable Binary Emulation Framework
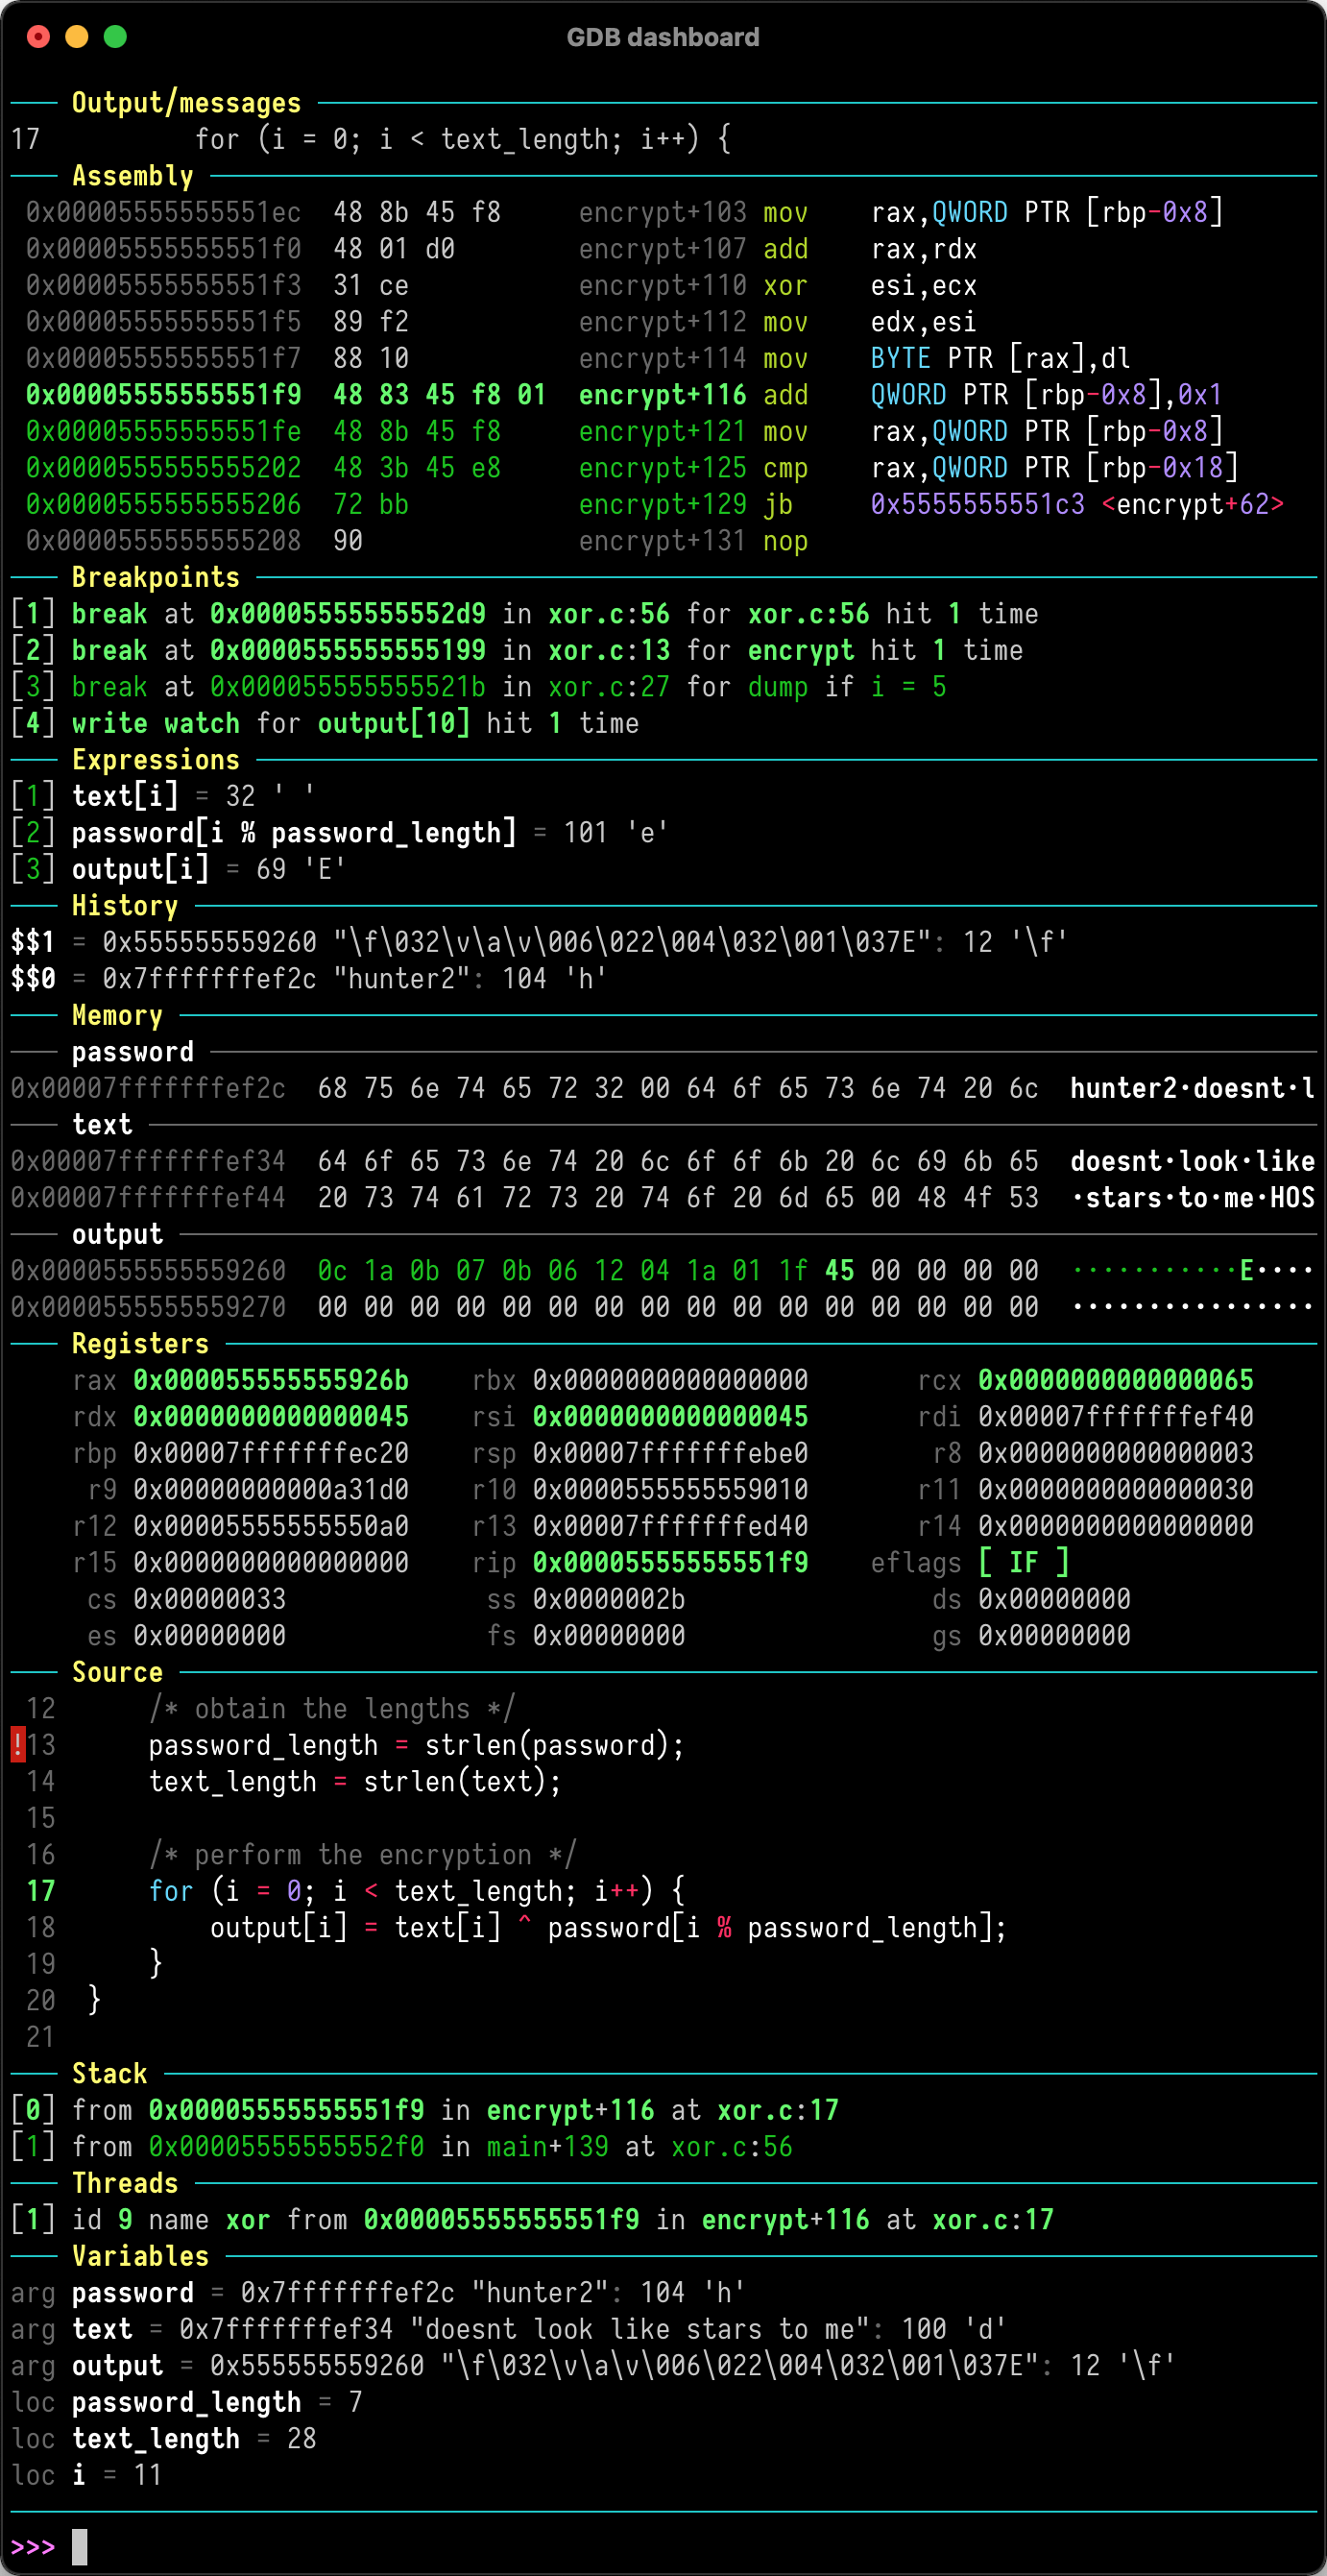 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
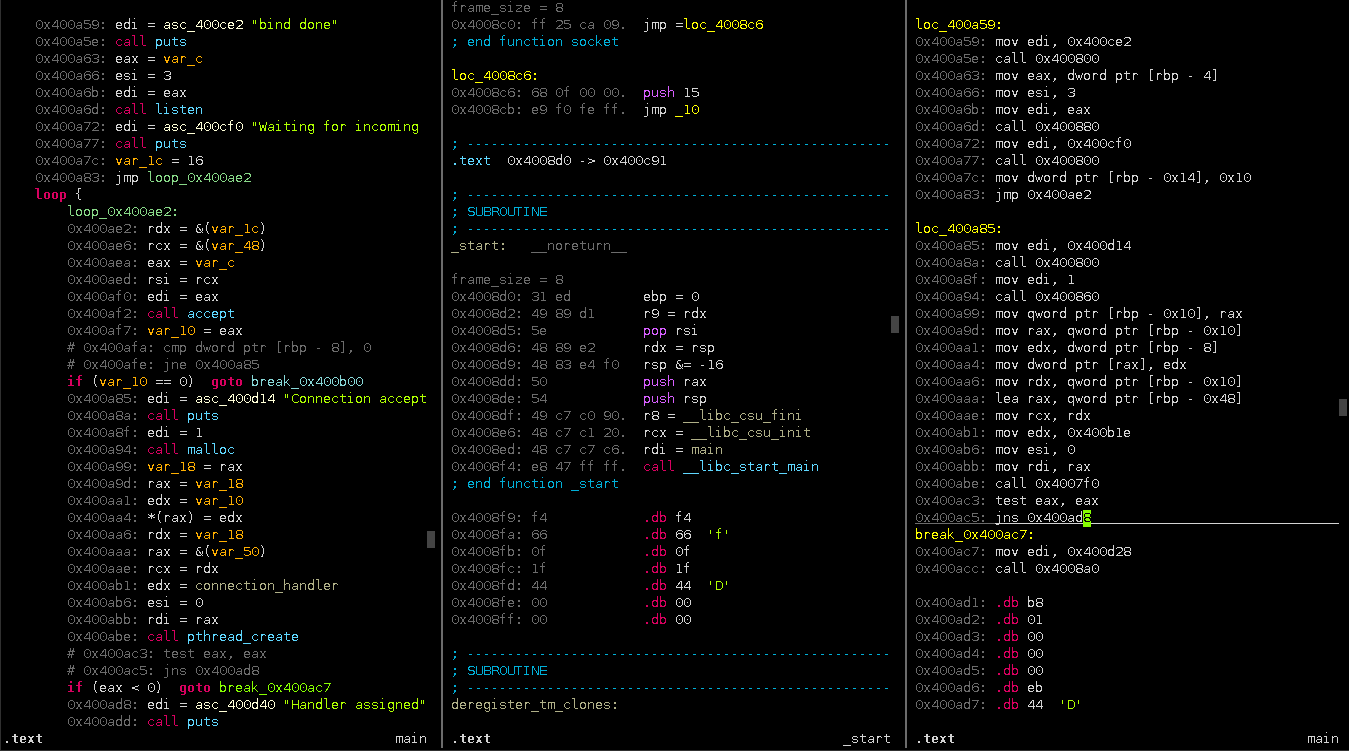 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
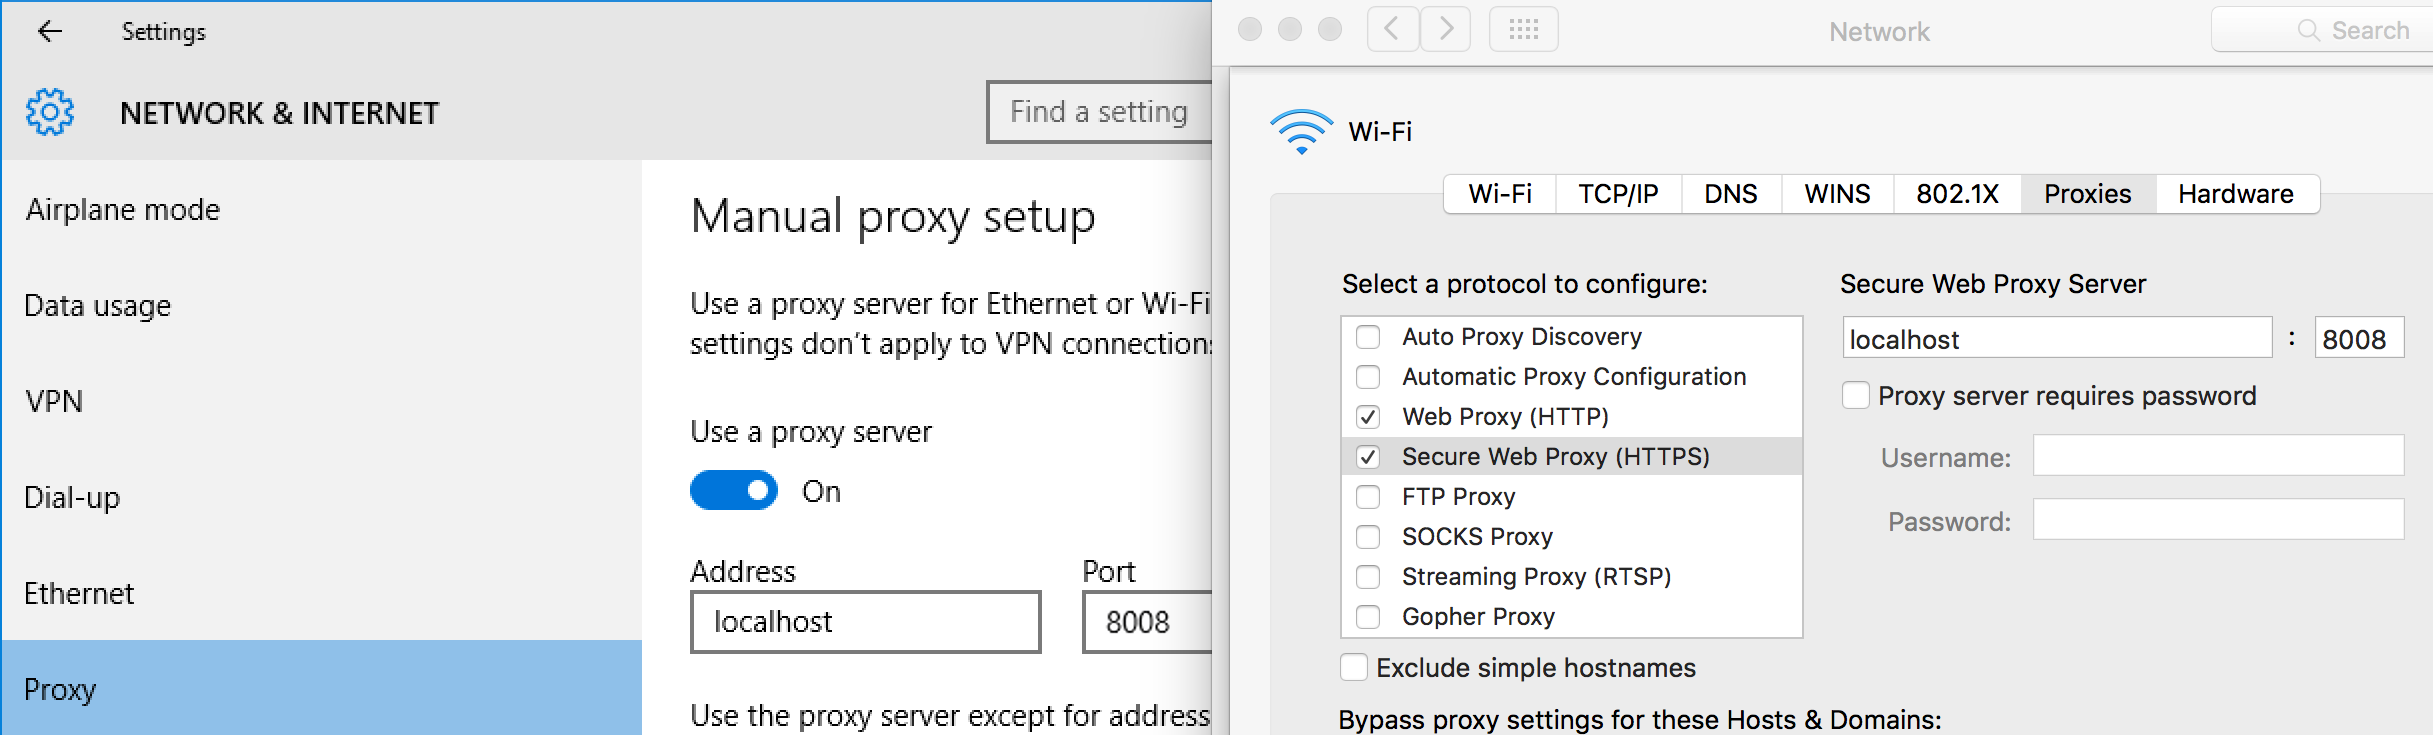 kdzwinel/betwixt
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.
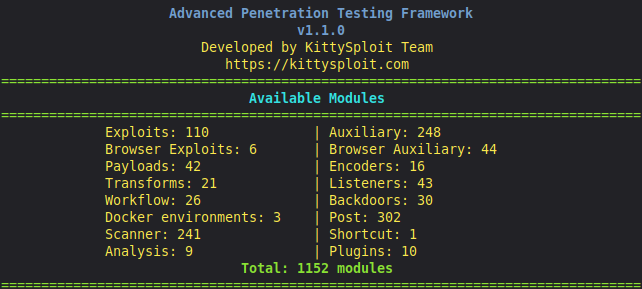 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
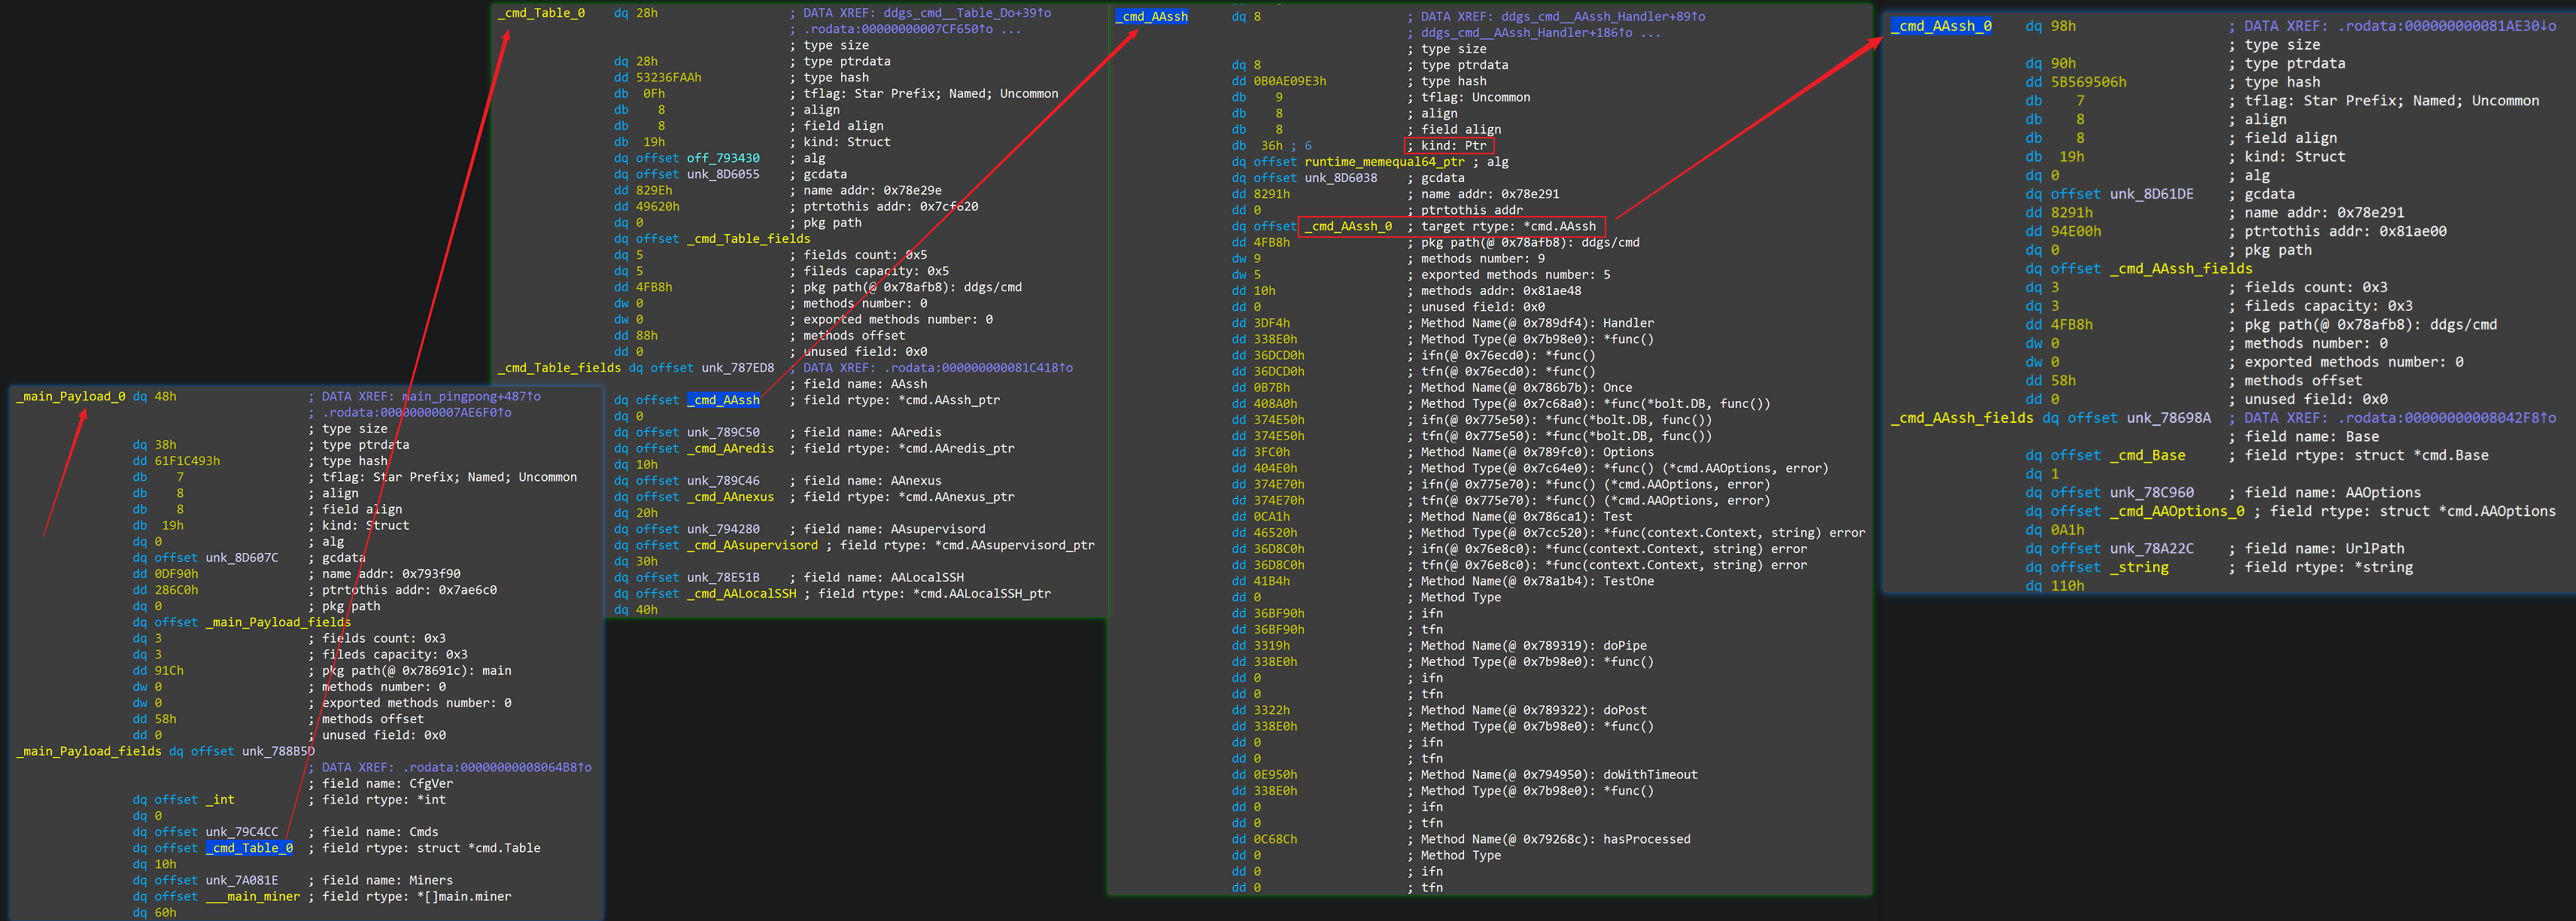 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
 hugsy/defcon_27_windbg_workshop
DEFCON 27 workshop - Modern Debugging with WinDbg Preview
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
 malwaretech/fsthook
A library for intercepting native functions by hooking KiFastSystemCall
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.