

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
27 results
LIEF preview

LIEF

GitHublief-project/lief

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…

ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k11h 6m ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
ai-assisted-reversingbinary-analysisdebuggers+3
1251 day ago
boxlambda preview

boxlambda

GitHubepsilon537/boxlambda

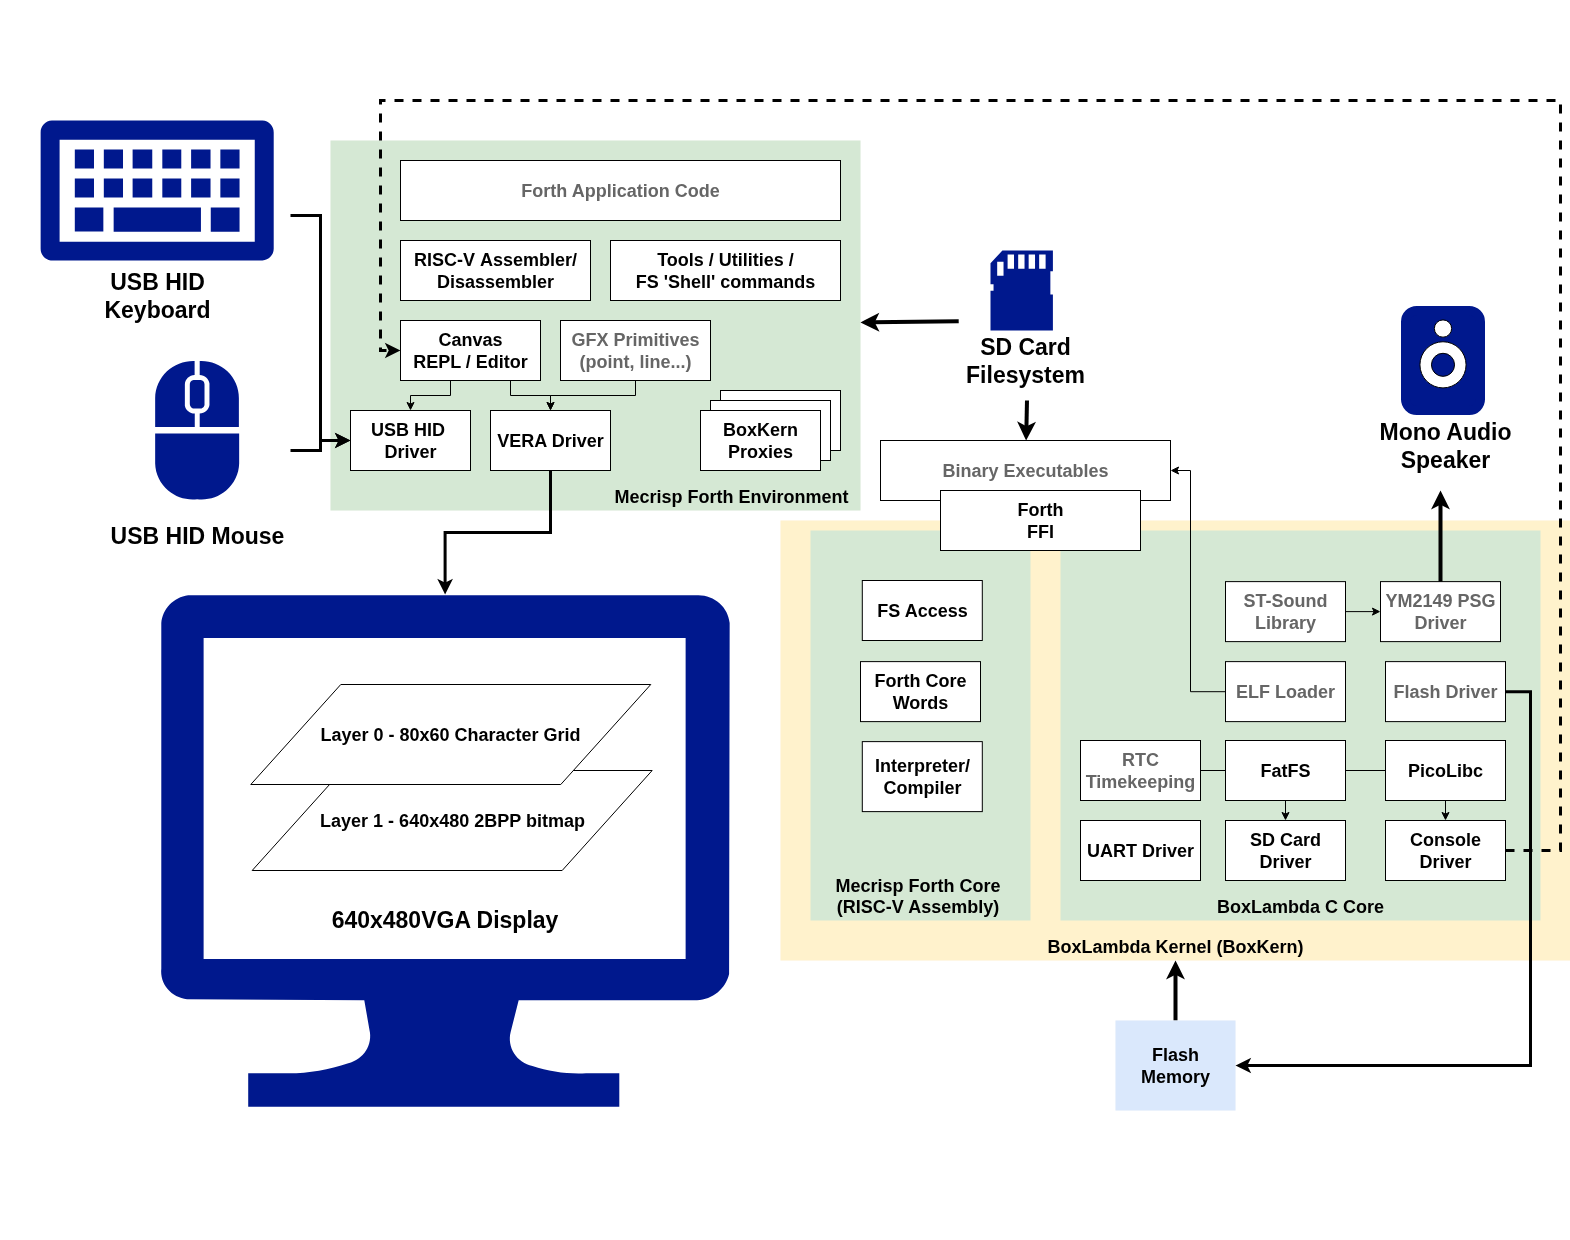
FPGA based microcomputer sandbox for software and RTL experimentation

debuggerseducationembedded-systems-security+5
866 days ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.4k14 days ago
CVE-2026-36980-Kernel-BSOD-DoS-PoC preview

CVE-2026-36980-Kernel-BSOD-DoS-PoC

GitHubcanomer/cve-2026-36980-kernel-bsod-dos-poc

Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
binary-exploitationdebuggersexploitation+2
15 months ago
CVE-2026-36981-Kernel-EoP-PoC preview

CVE-2026-36981-Kernel-EoP-PoC

GitHubcanomer/cve-2026-36981-kernel-eop-poc

Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
binary-exploitationdebuggersexploitation+4
25 months ago
themida-devirt preview

themida-devirt

GitHubbackengineering/themida-devirt

Themida Devirt Results
binary-analysisdebuggersfirmware-analysis+3
1265 months ago
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…

ai-assisted-reversingbinary-analysisdebuggers+4
137 months ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

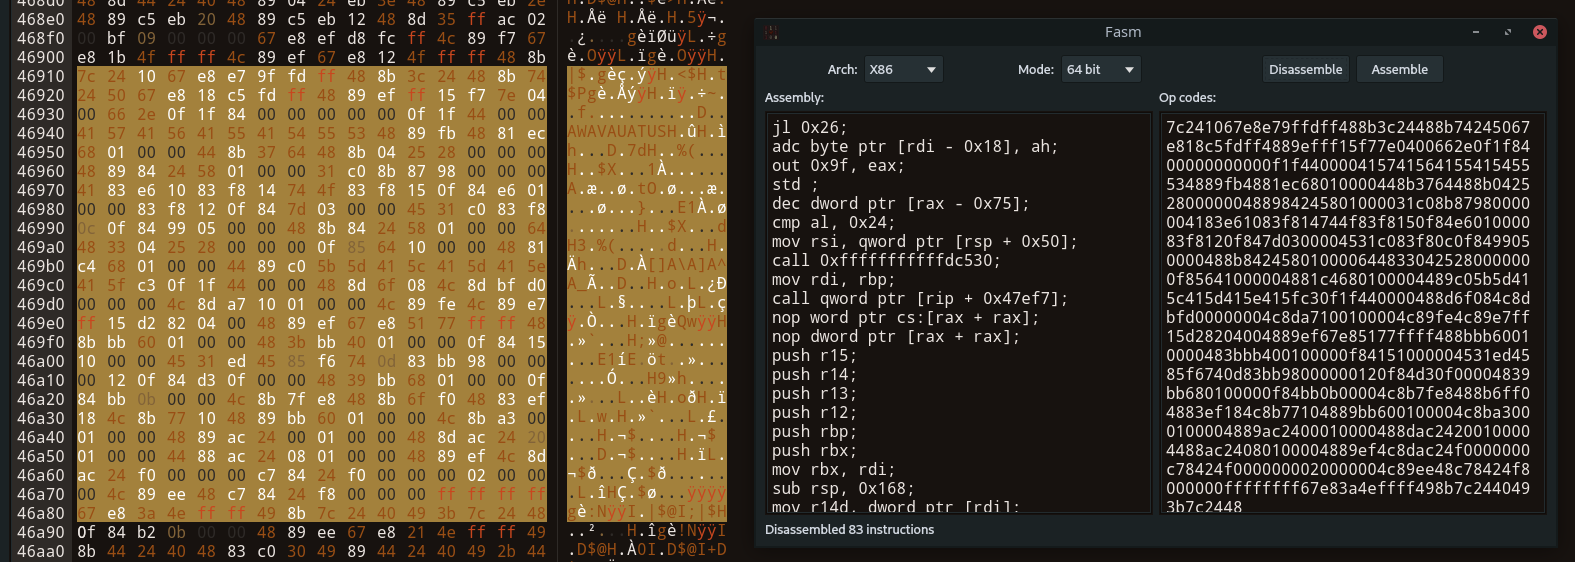
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
android-securitybinary-analysisdebuggers+4
7217 months ago
thats_no_pipe preview

thats_no_pipe

GitHubsynacktiv/thats_no_pipe

Windows named pipe hooking toolkit
binary-analysisdebuggersdynamic-analysis-sandboxing+3
467 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubelrajiii/cve-2025-5548

Buffer overflow in FreeFloat FTP Server 1.0

binary-exploitationdebuggerseducation+8
7 months ago
icicle-python preview

icicle-python

GitHubicicle-emu/icicle-python

Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
431 year ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
4511 year ago
fhex preview

fhex

GitHubecho-devim/fhex

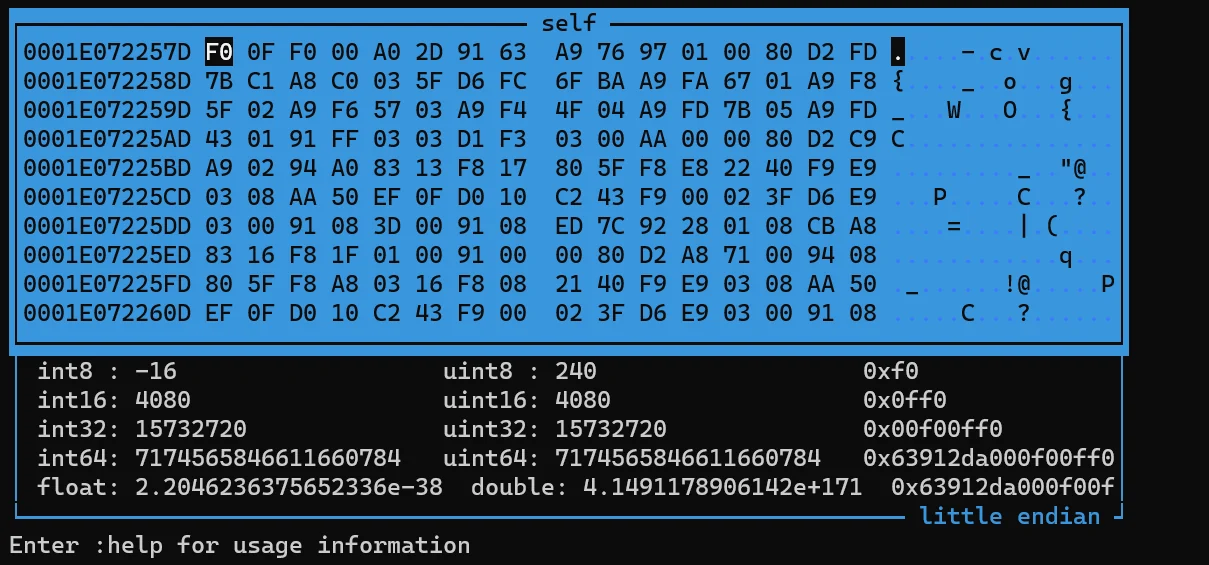
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
binary-analysisdebuggersforensics+2
4361 year ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
ManticoreUI preview

ManticoreUI

GitHubtrailofbits/manticoreui

The Manticore User Interface with plugins for Binary Ninja and Ghidra
binary-analysisdebuggersdynamic-analysis-sandboxing+1
743 years ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
thematrix preview

thematrix

GitHubenkomio/thematrix

a PE Loader and Windows API tracer. Useful in malware analysis.

api-securitydebuggersdynamic-analysis-sandboxing+2
1424 years ago
Previous12Next