
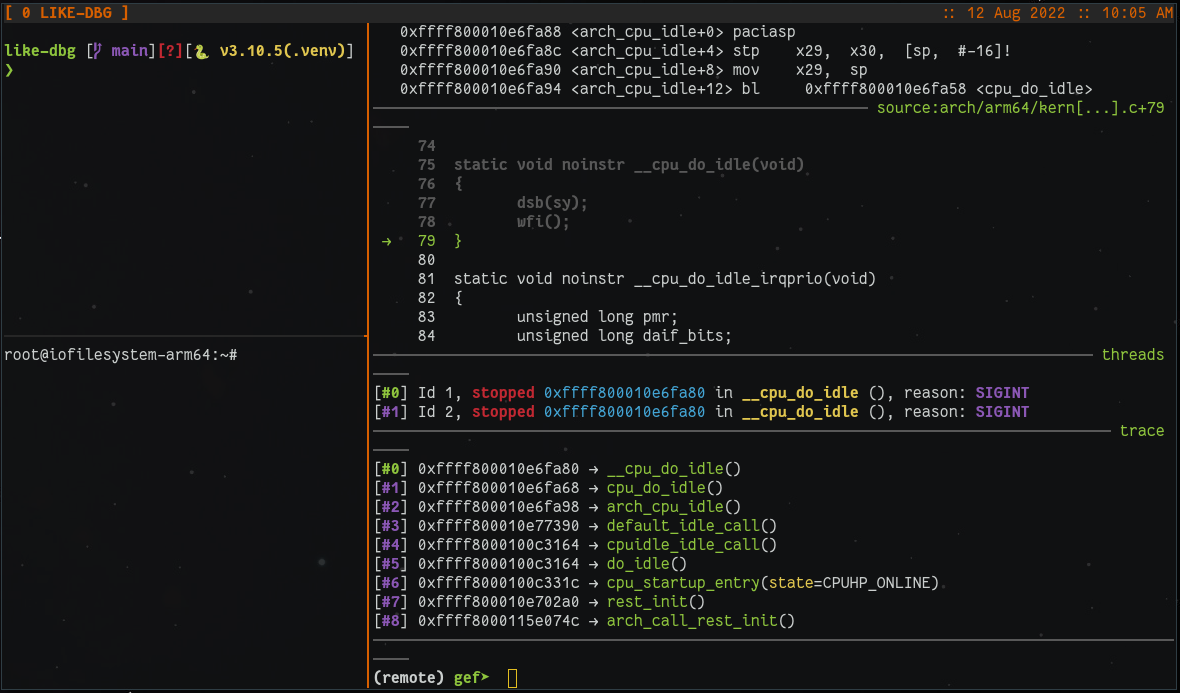
like-dbg
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
binary-exploitationctfdebuggers+2
7699 days ago
0xricksanchez/like-dbgFully dockerized Linux kernel debugging environment
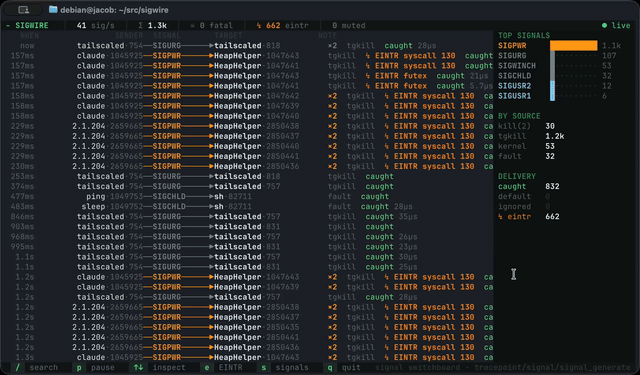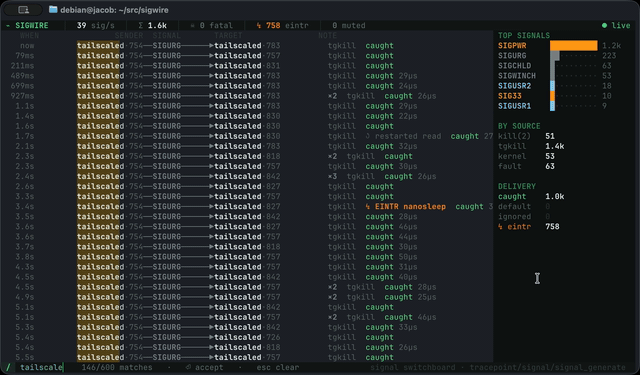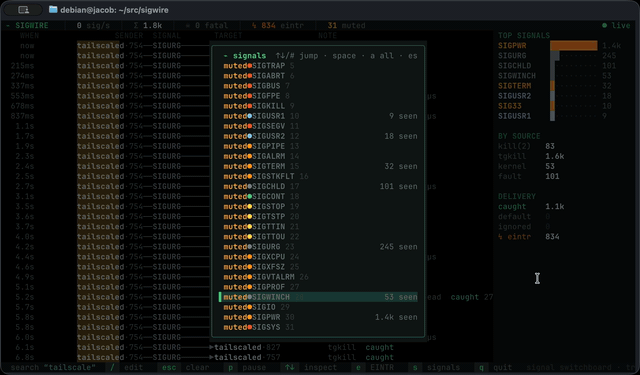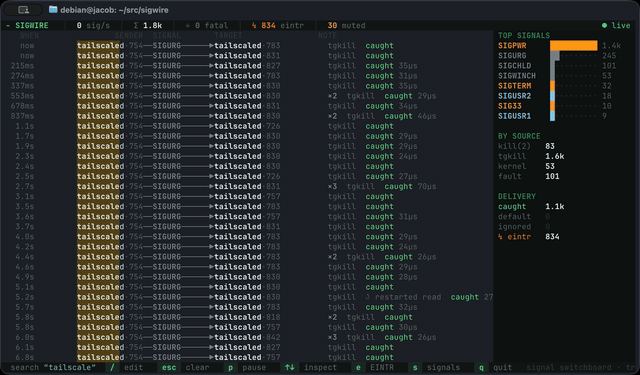 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
 ngtuonghung/cve-2022-27666
Heap buffer overflow exploit for CVE-2022-27666 in Linux kernel IPsec ESP6 implementation. Includes kernel build, debug setup with GDB stub, and…
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
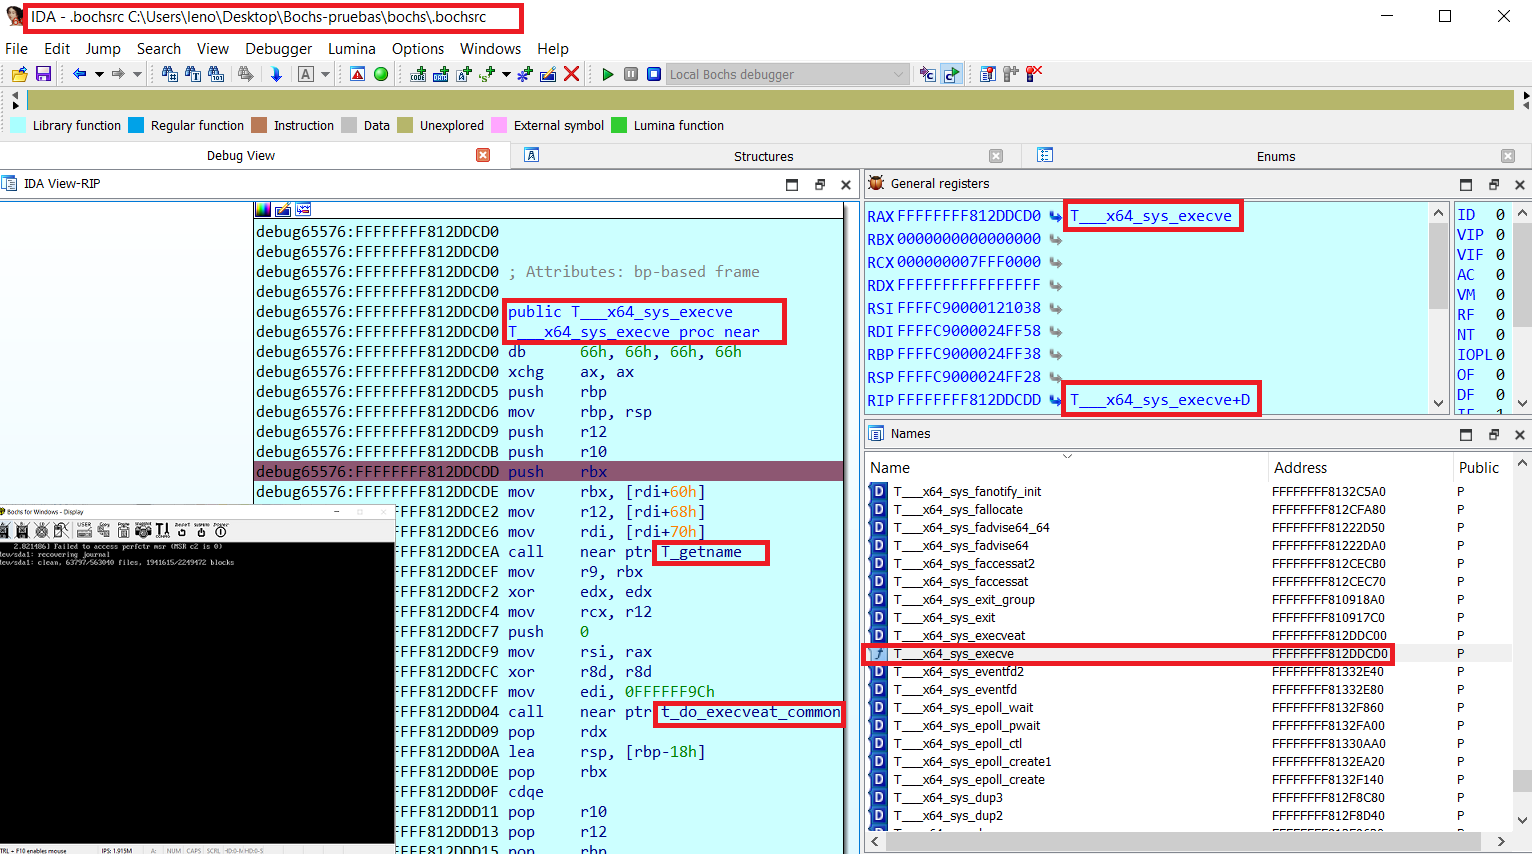 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-14356
Linux kernel source tree modified for CVE-2020-14356, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 dsfau/cve-2018-1000199
Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…