

EVENSTAR
 winterknife/evenstar
Intel 64/Windows low-level experiments
binary-analysisbinary-exploitationdebuggers+5
1183h 37m ago
winterknife/evenstarIntel 64/Windows low-level experiments
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
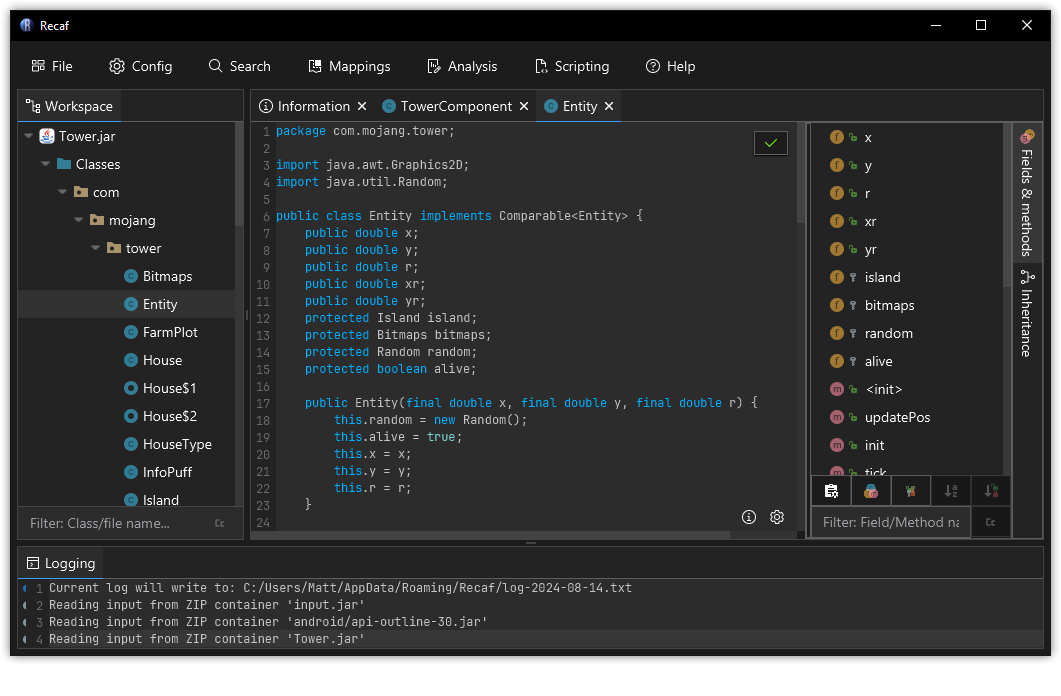

 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 angr/angr
A powerful and user-friendly binary analysis platform!
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…