

PrologWinDbg
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
binary-analysisdebuggersdigital-forensics+4
10
dumpanalysis/prologwindbgUse Prolog to analyze memory dumps and stopped live processes in WinDbg.
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 chichou/vscode-frida
Unofficial frida extension for VSCode
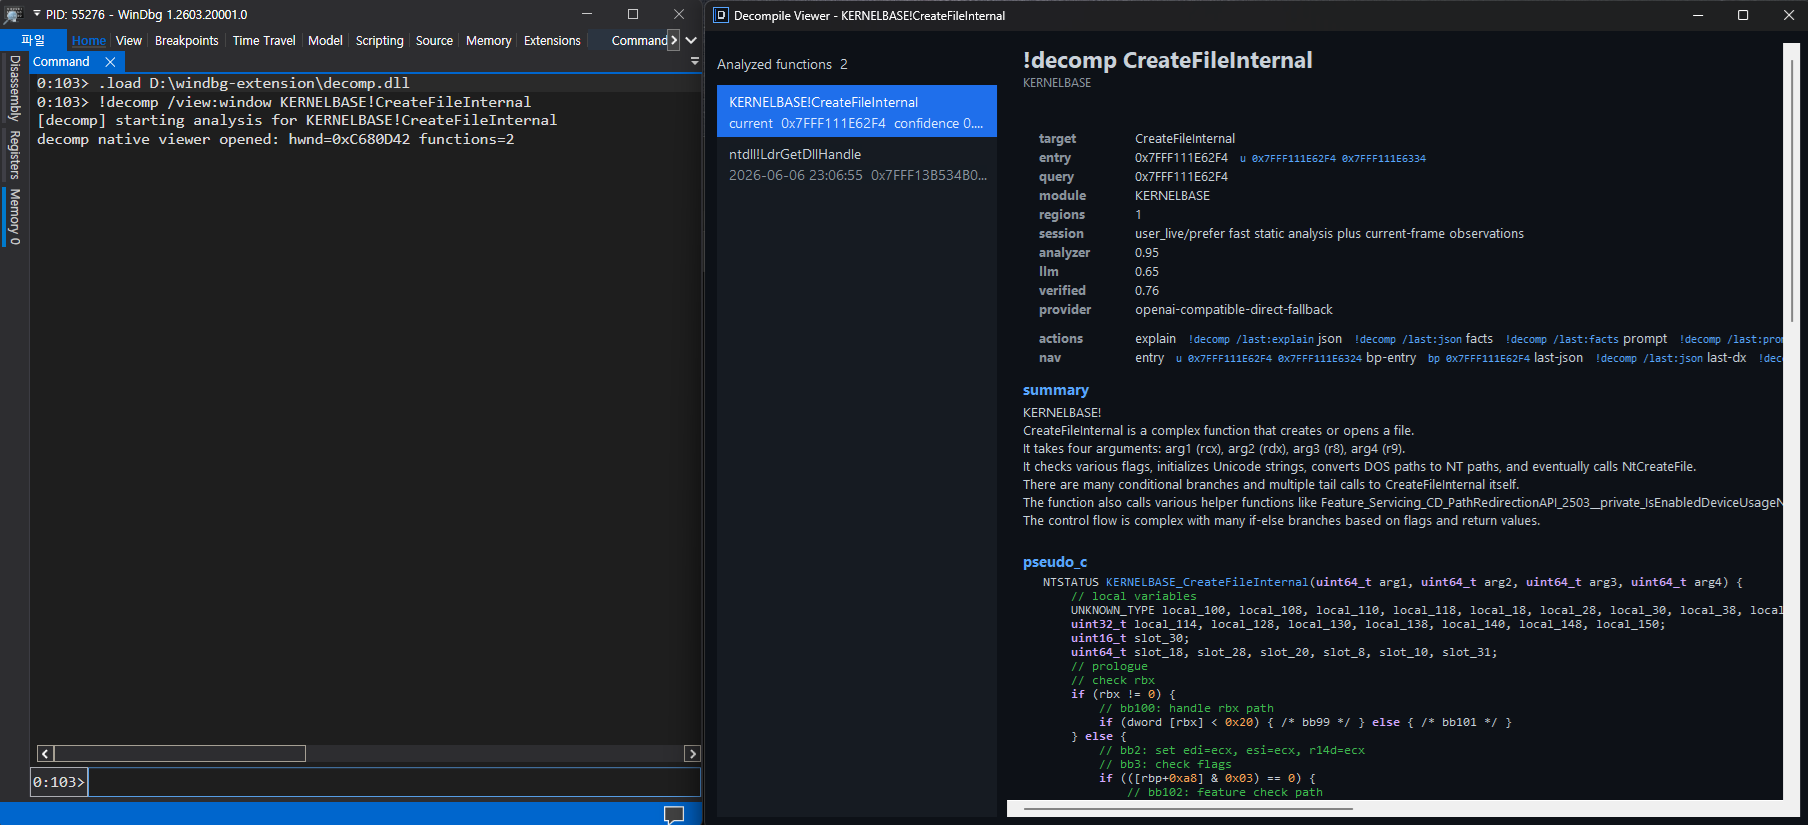 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
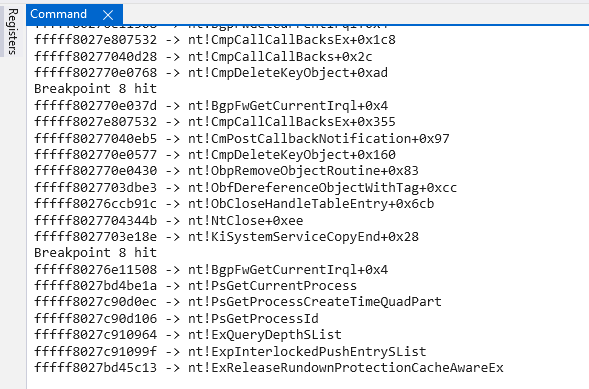 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
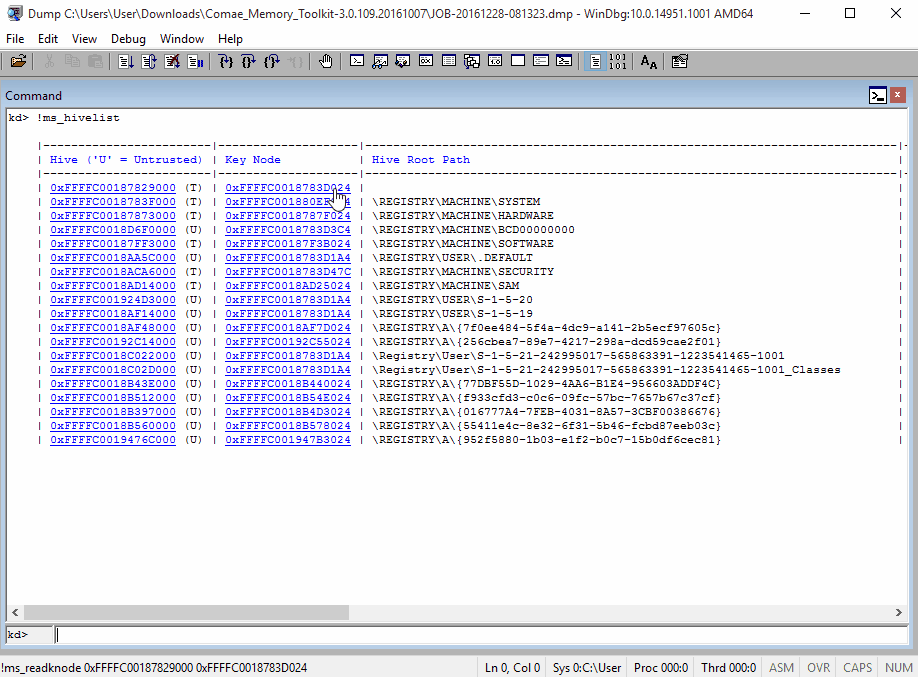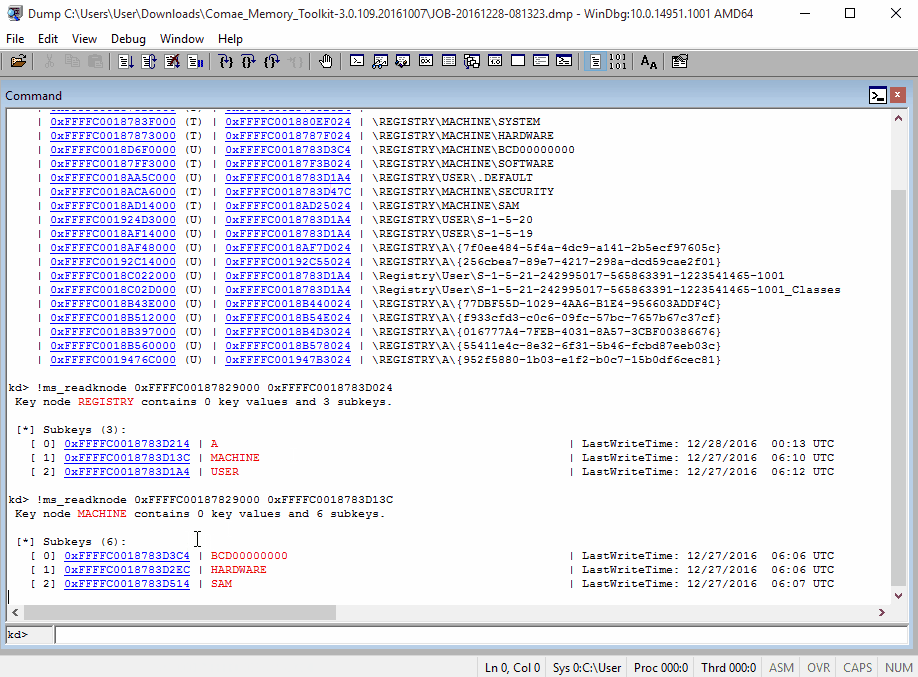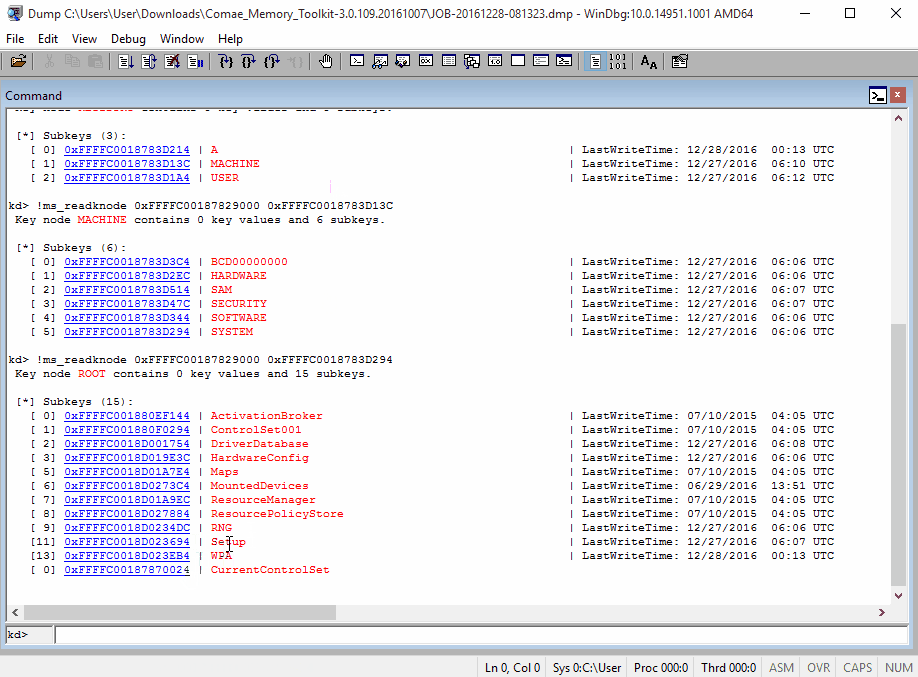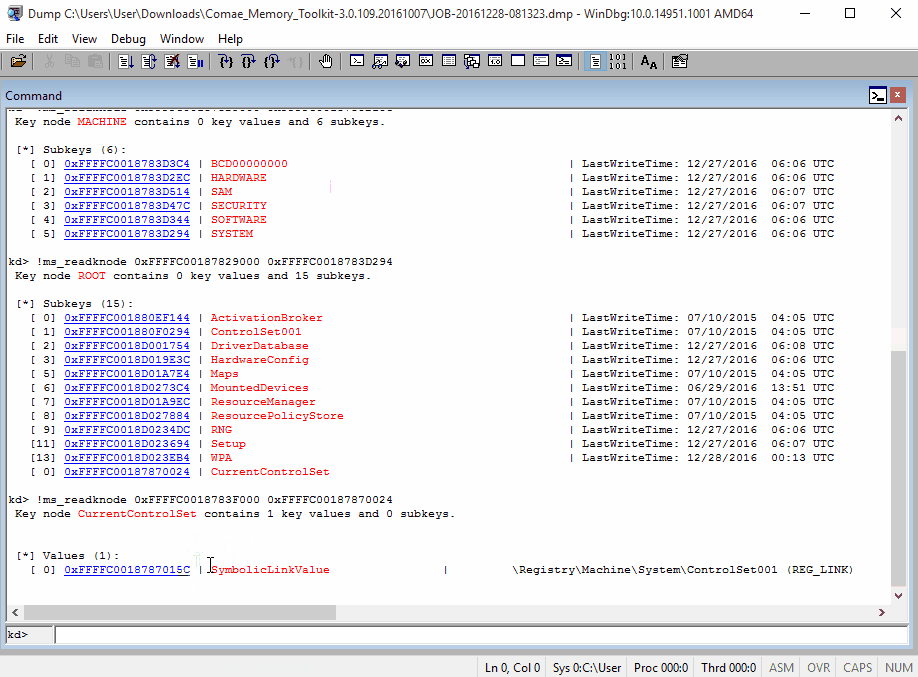 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension