
rr
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
binary-analysisdebuggersdynamic-code-analysis
rr-debugger/rrRecord and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
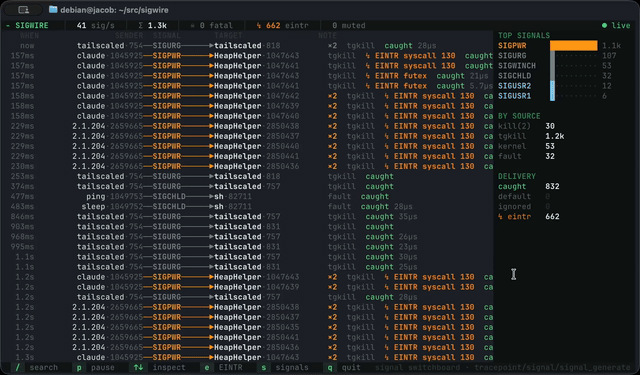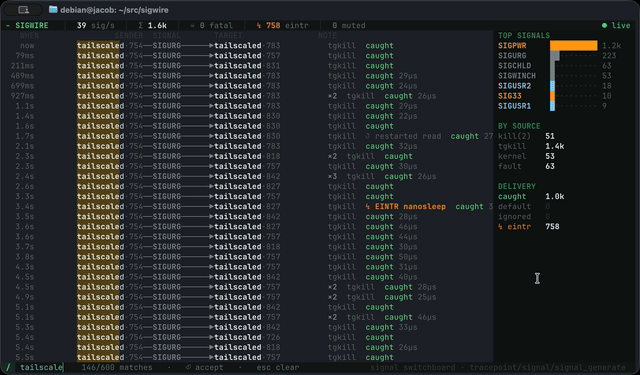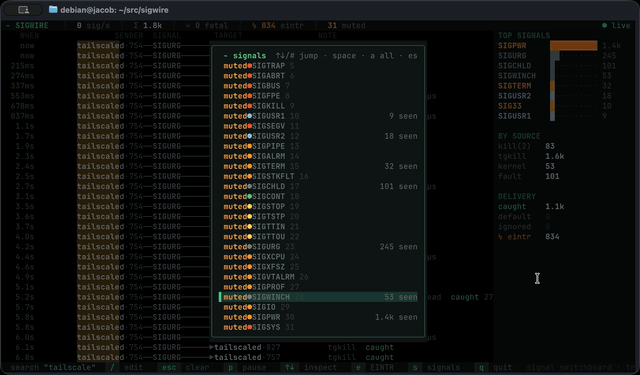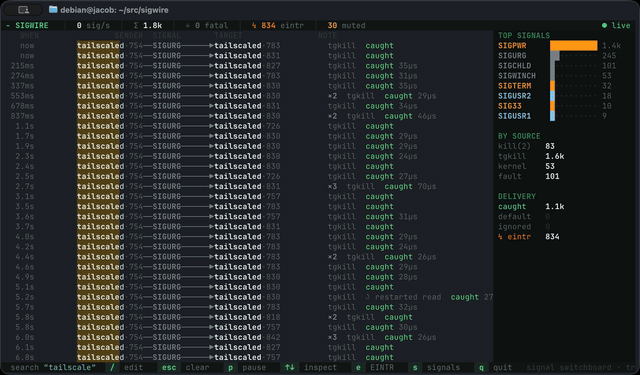 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
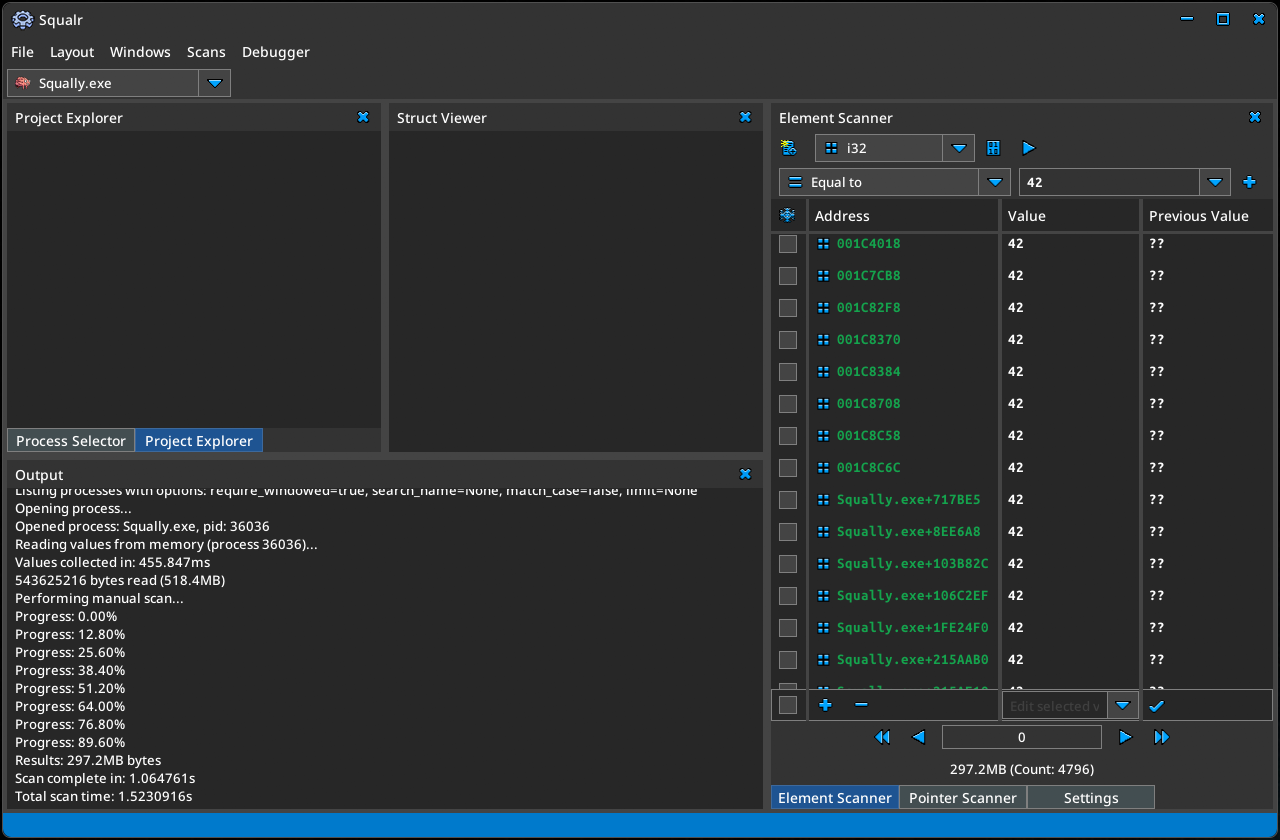 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
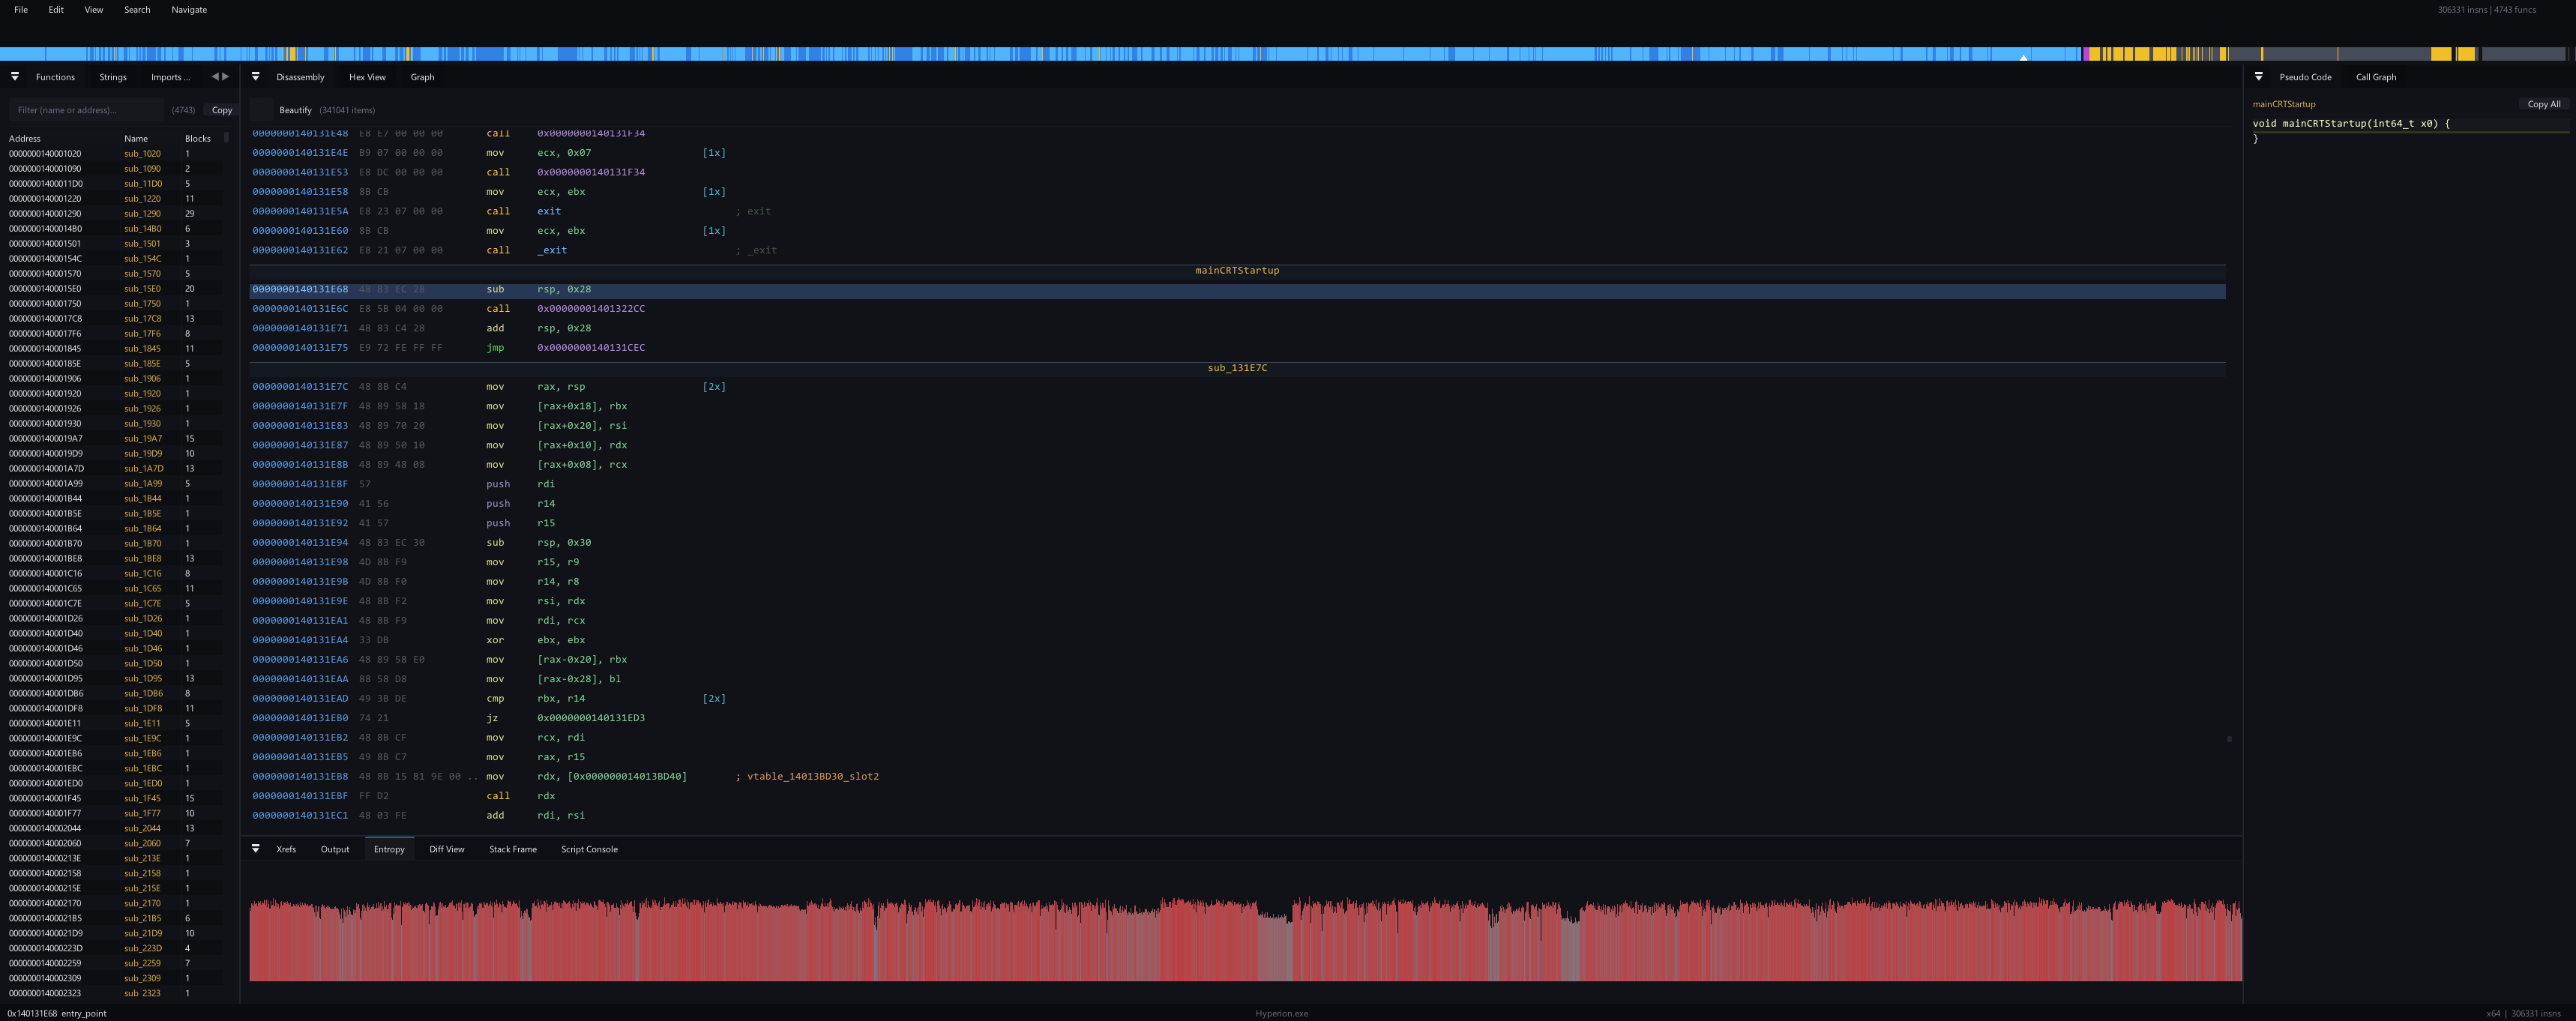 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
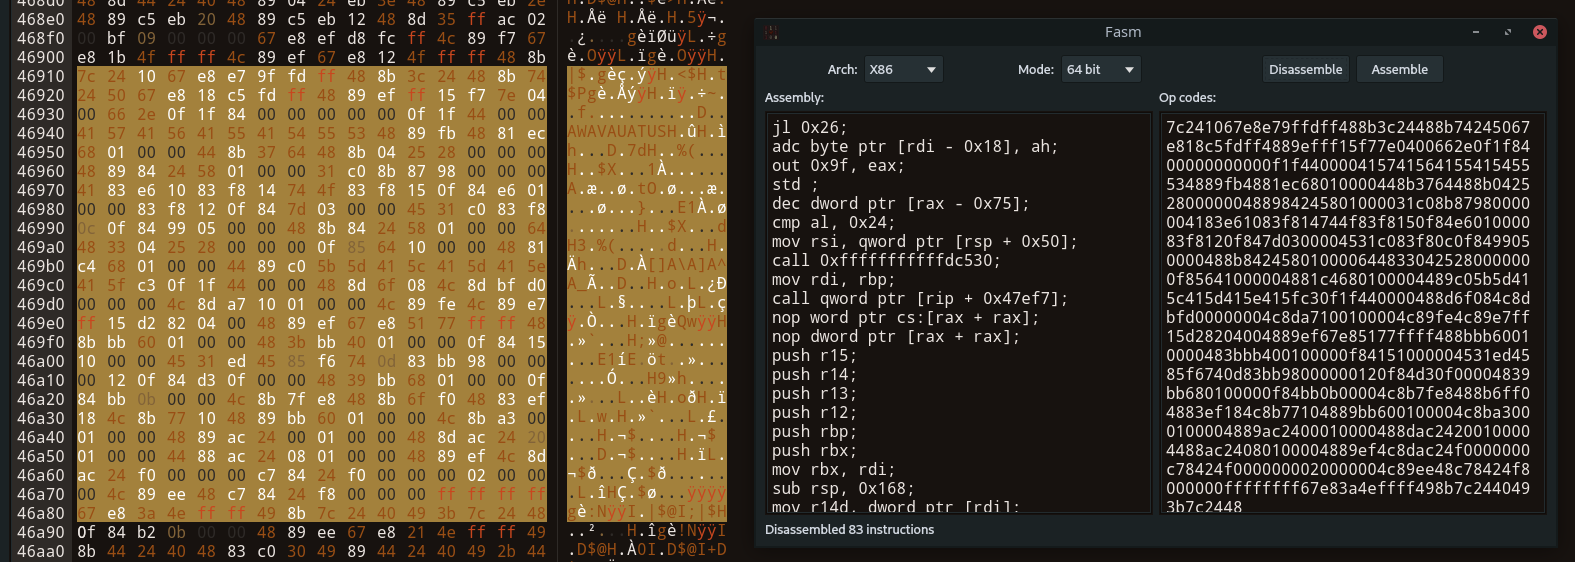 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
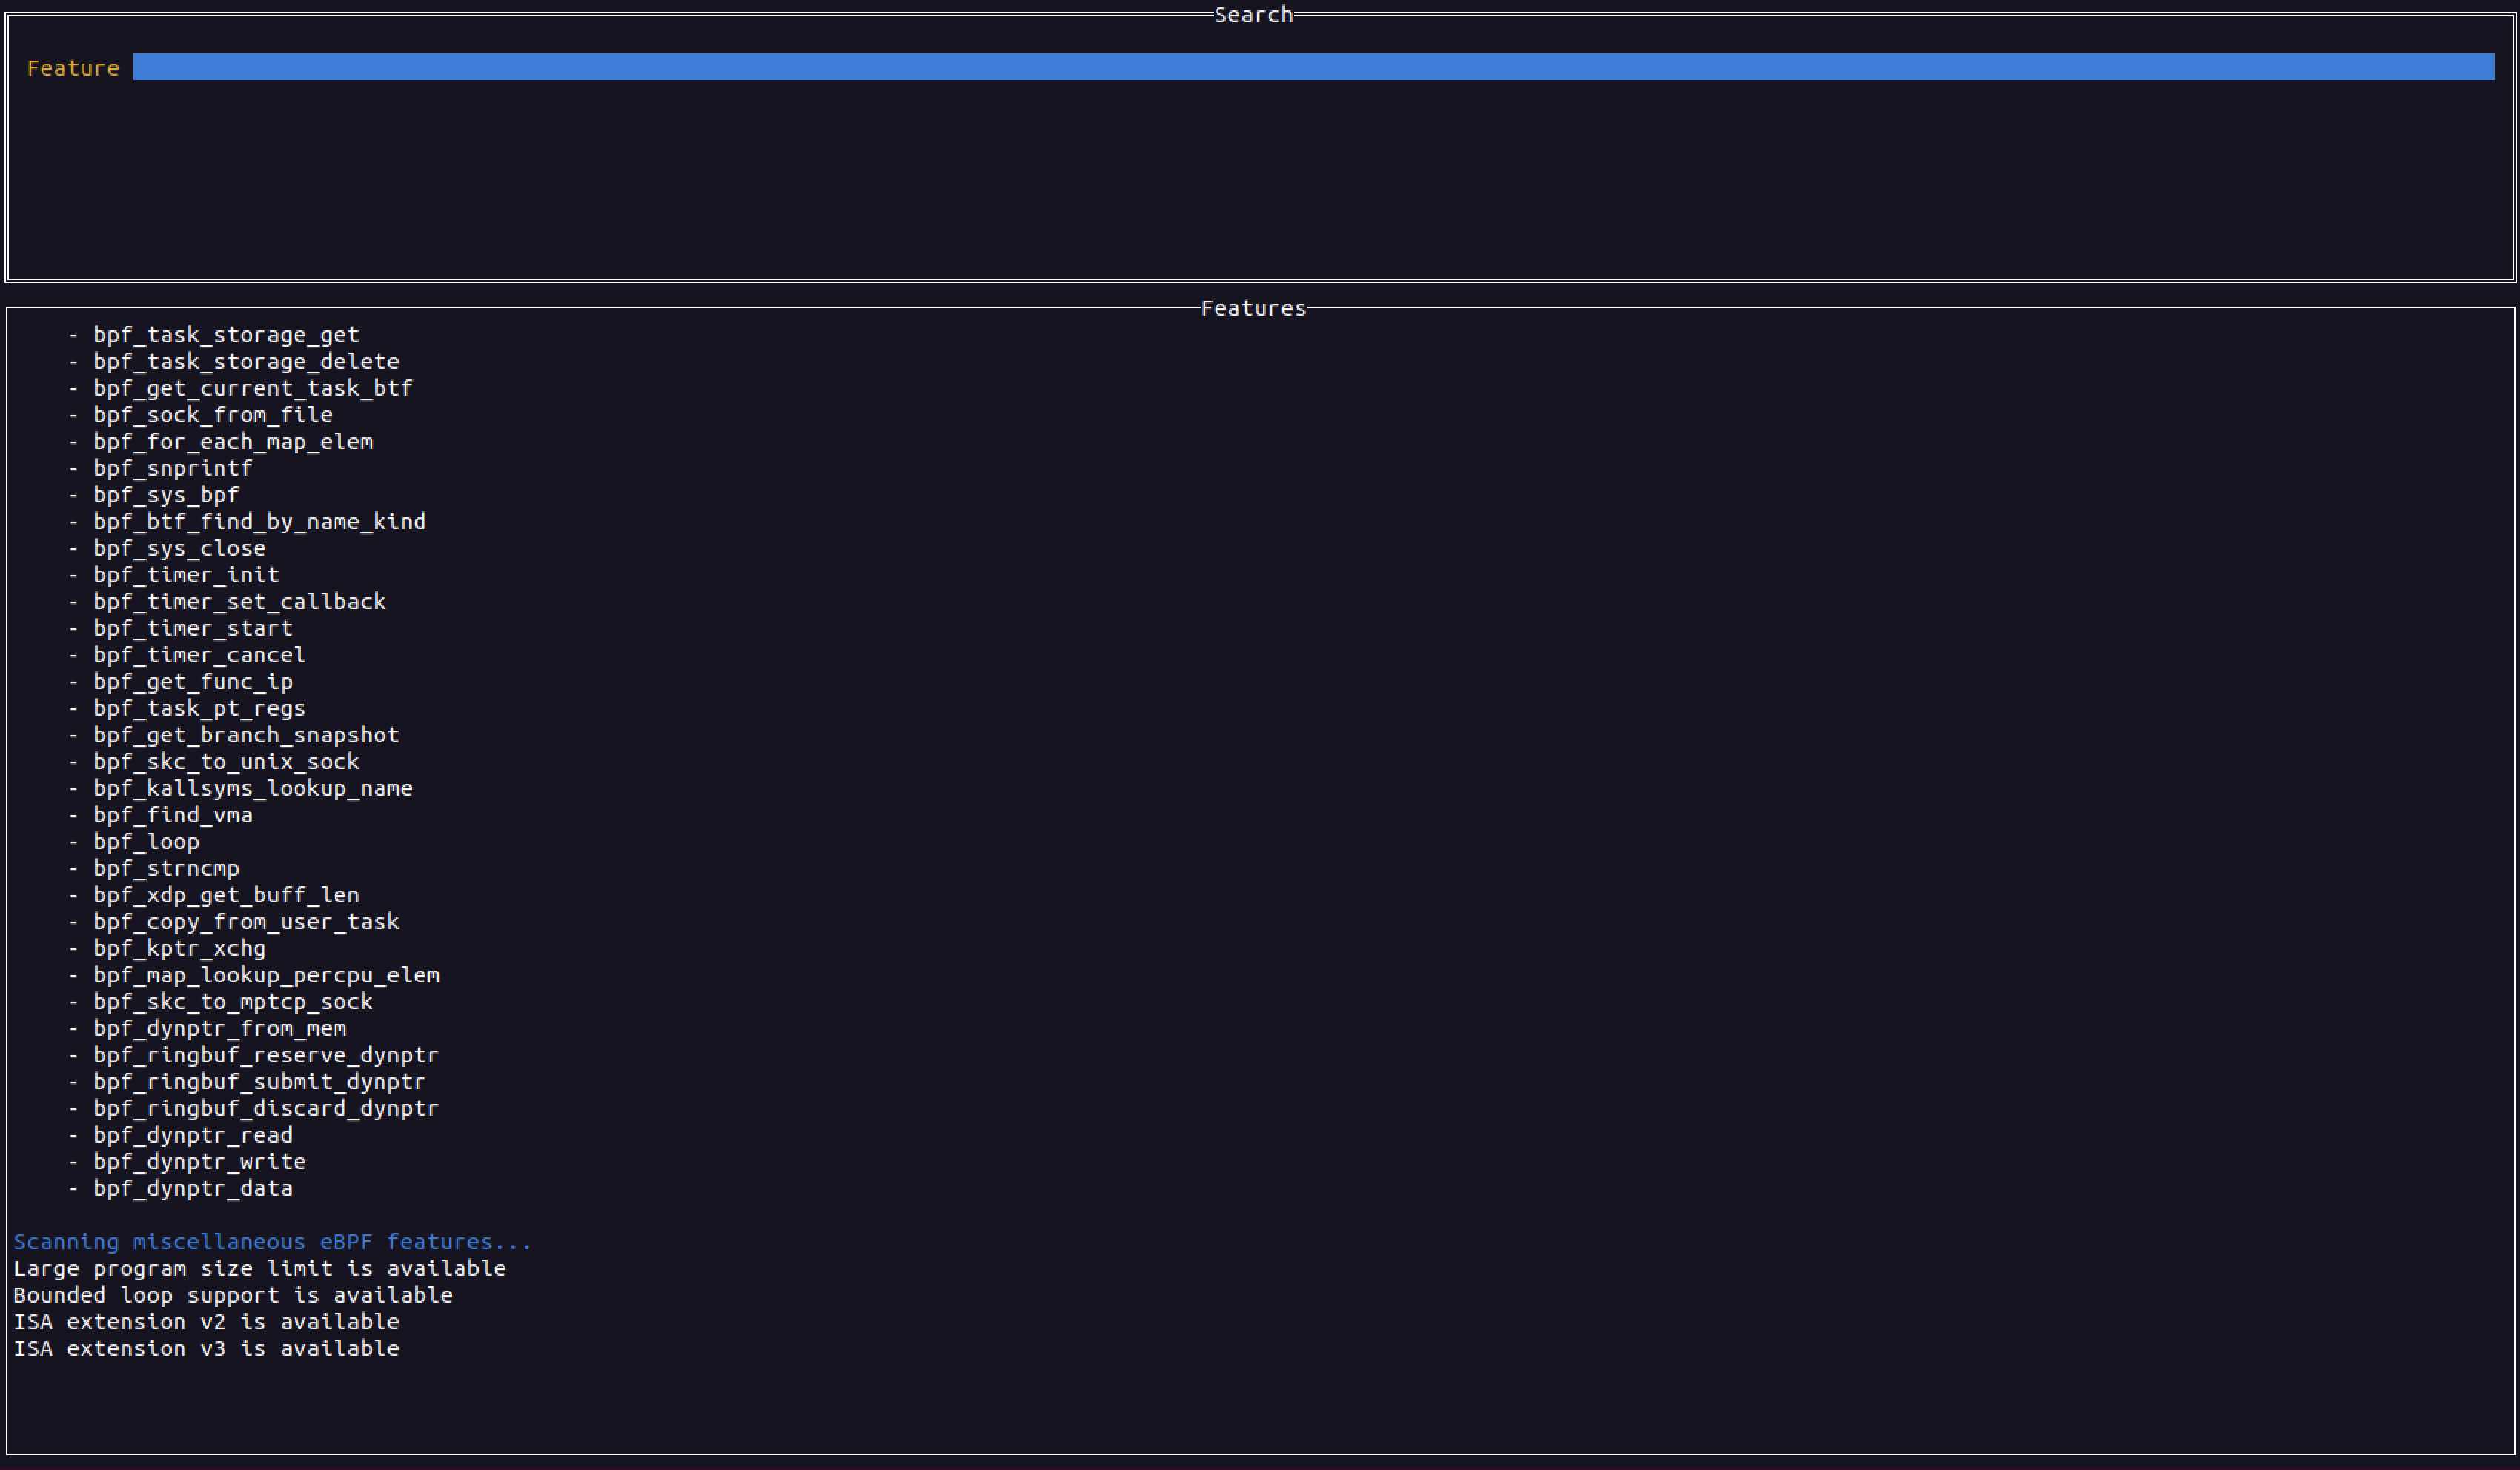 redcanaryco/ebpfmon
Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 guardicore/ipcdump
BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel