Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

My musings with PowerShell

Security profiling for blackbox iOS

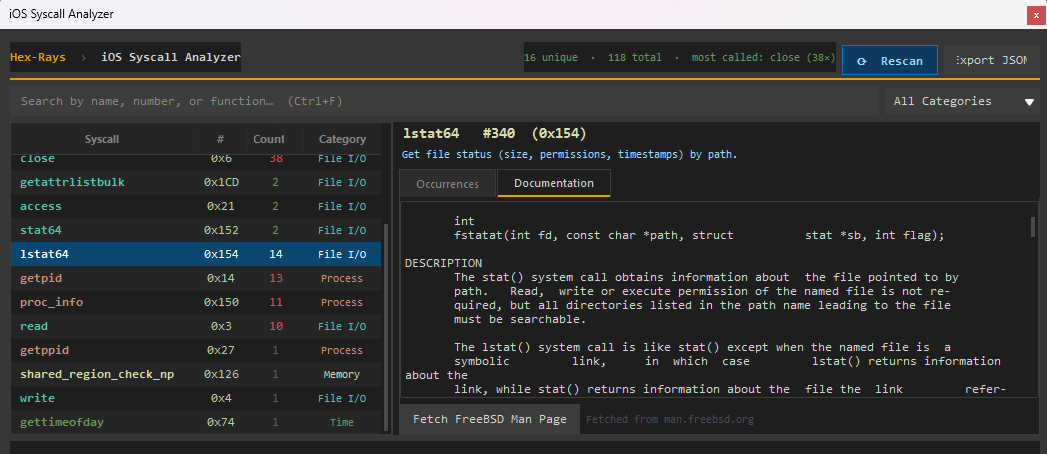
iOS Syscall Explorer for IDA 9.X

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…


Educational lab for analyzing and exploiting CVE-2025-5548 (FreeFloat FTP Server buffer overflow) with step-by-step guides, debugger setup, and…

A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol

Python dumper/explorer for MCD Runtime Projects used by ODIS

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…

Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

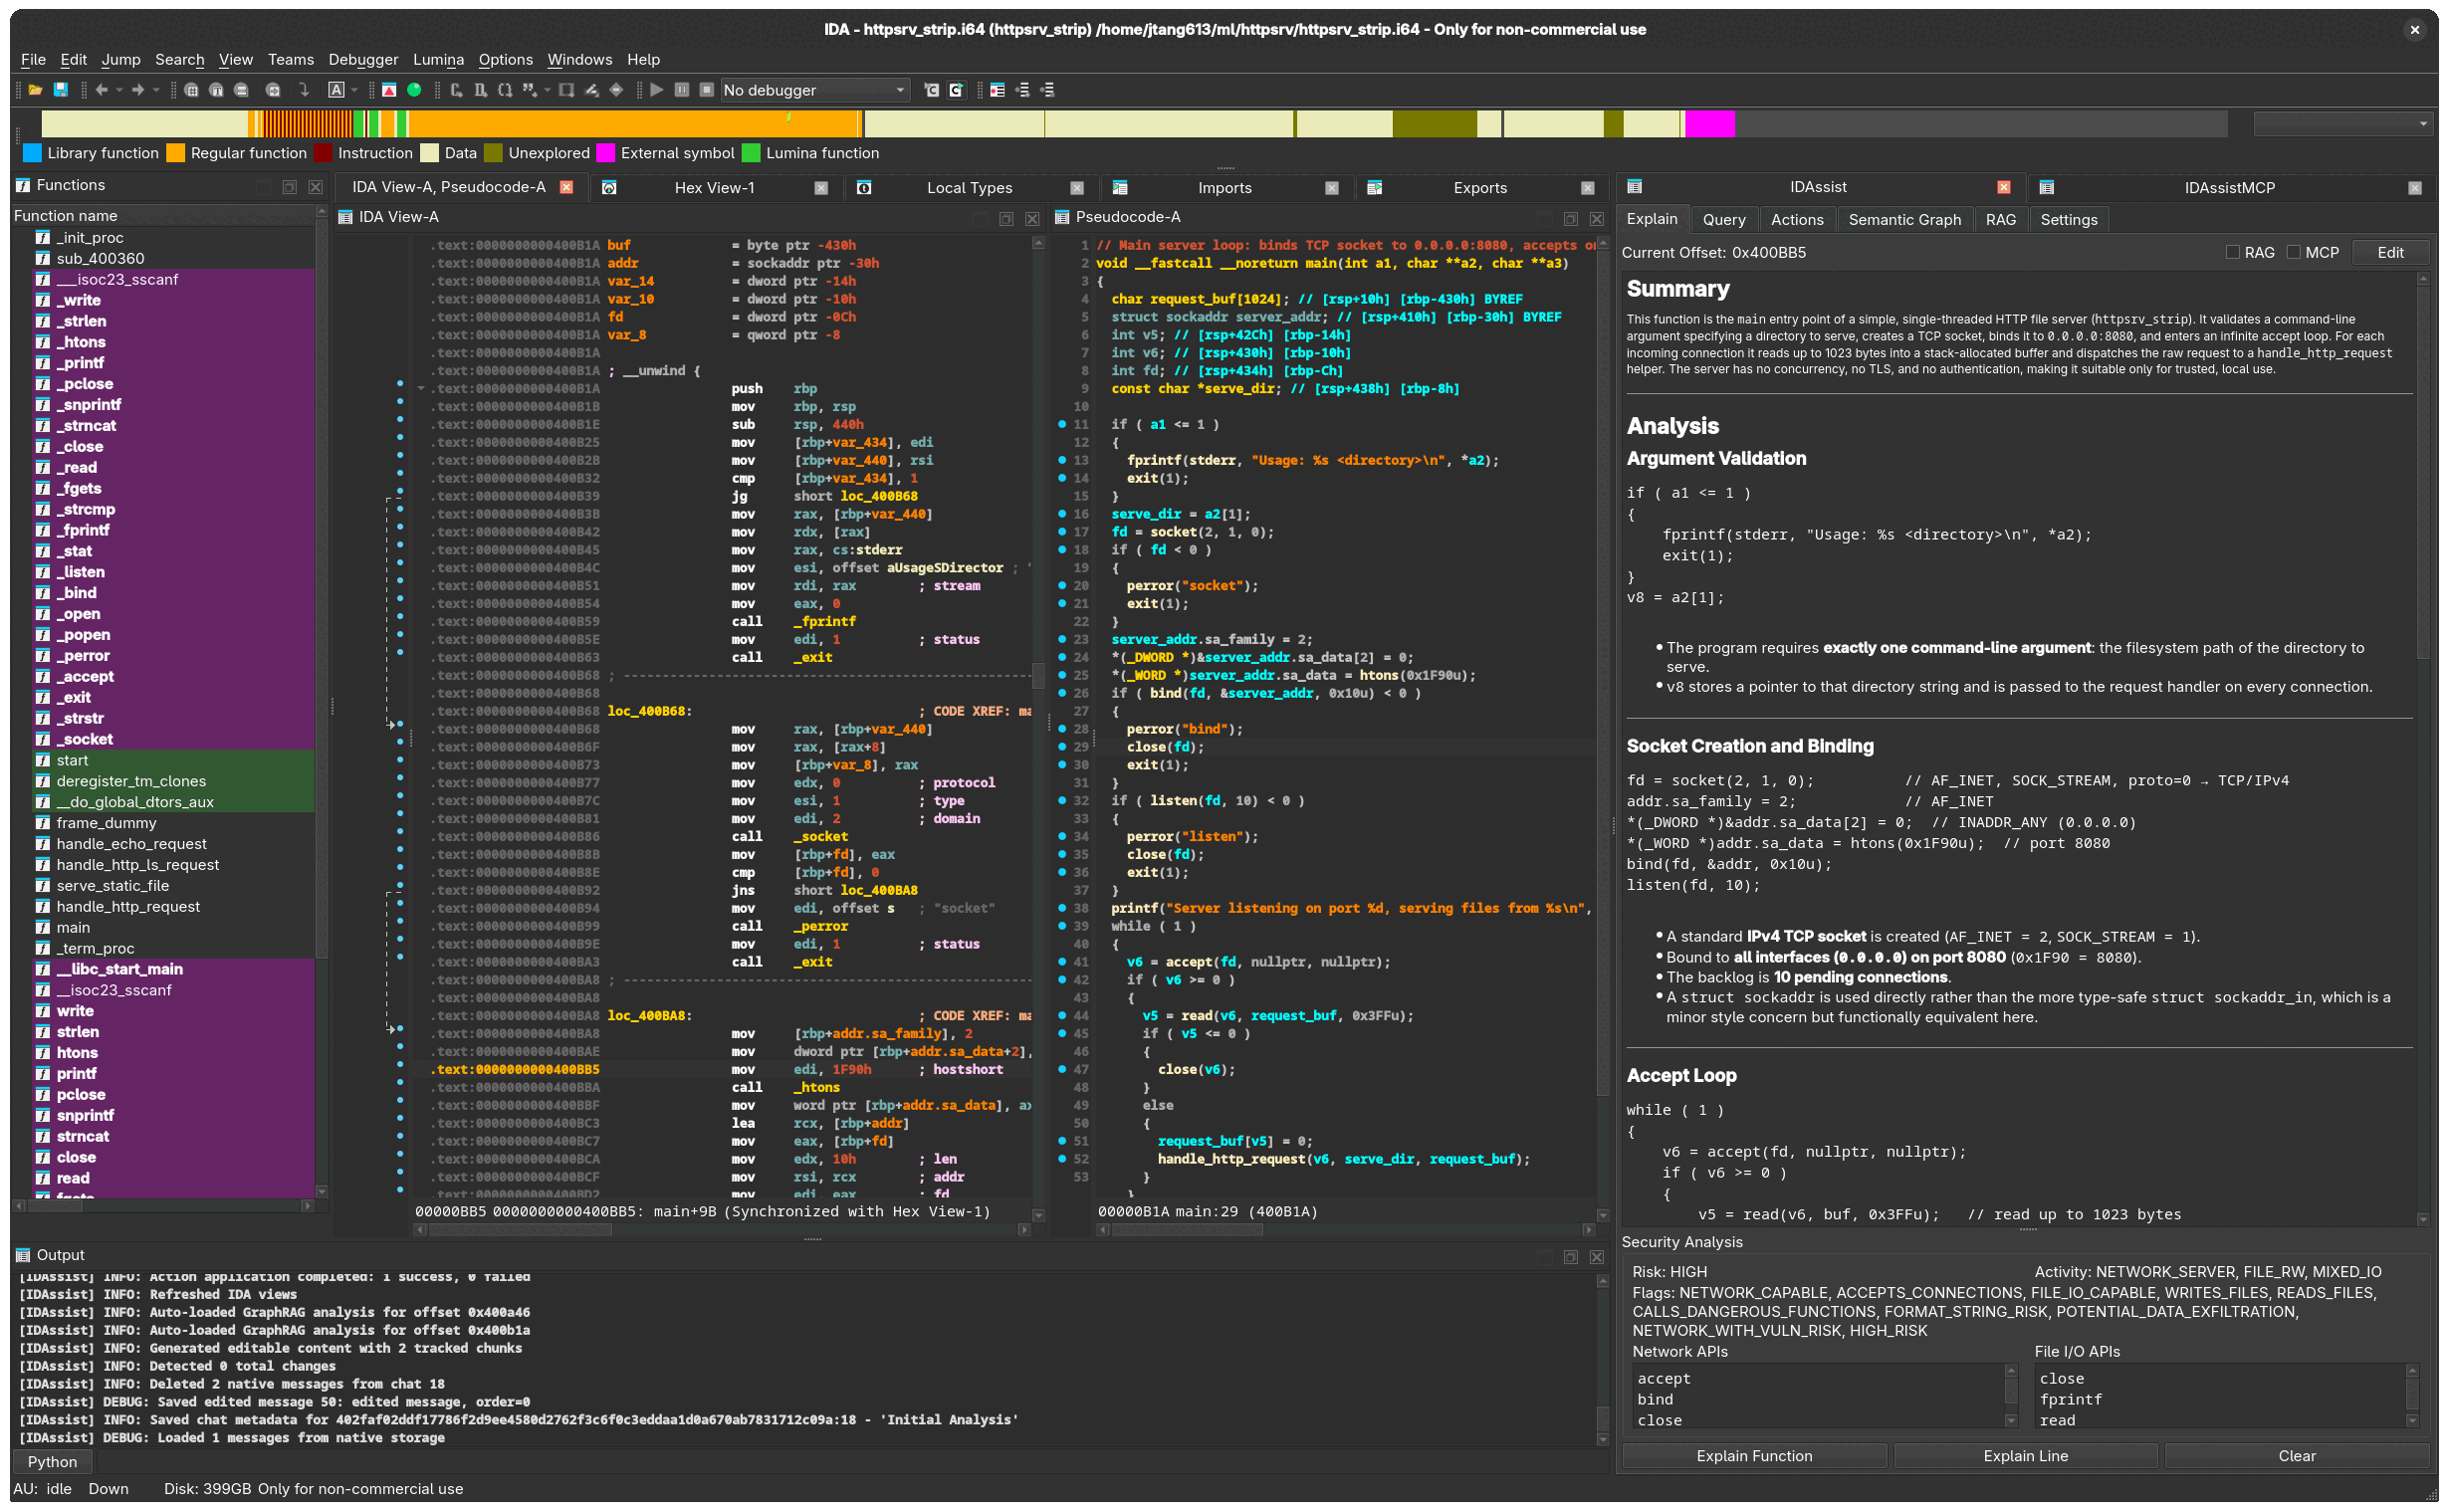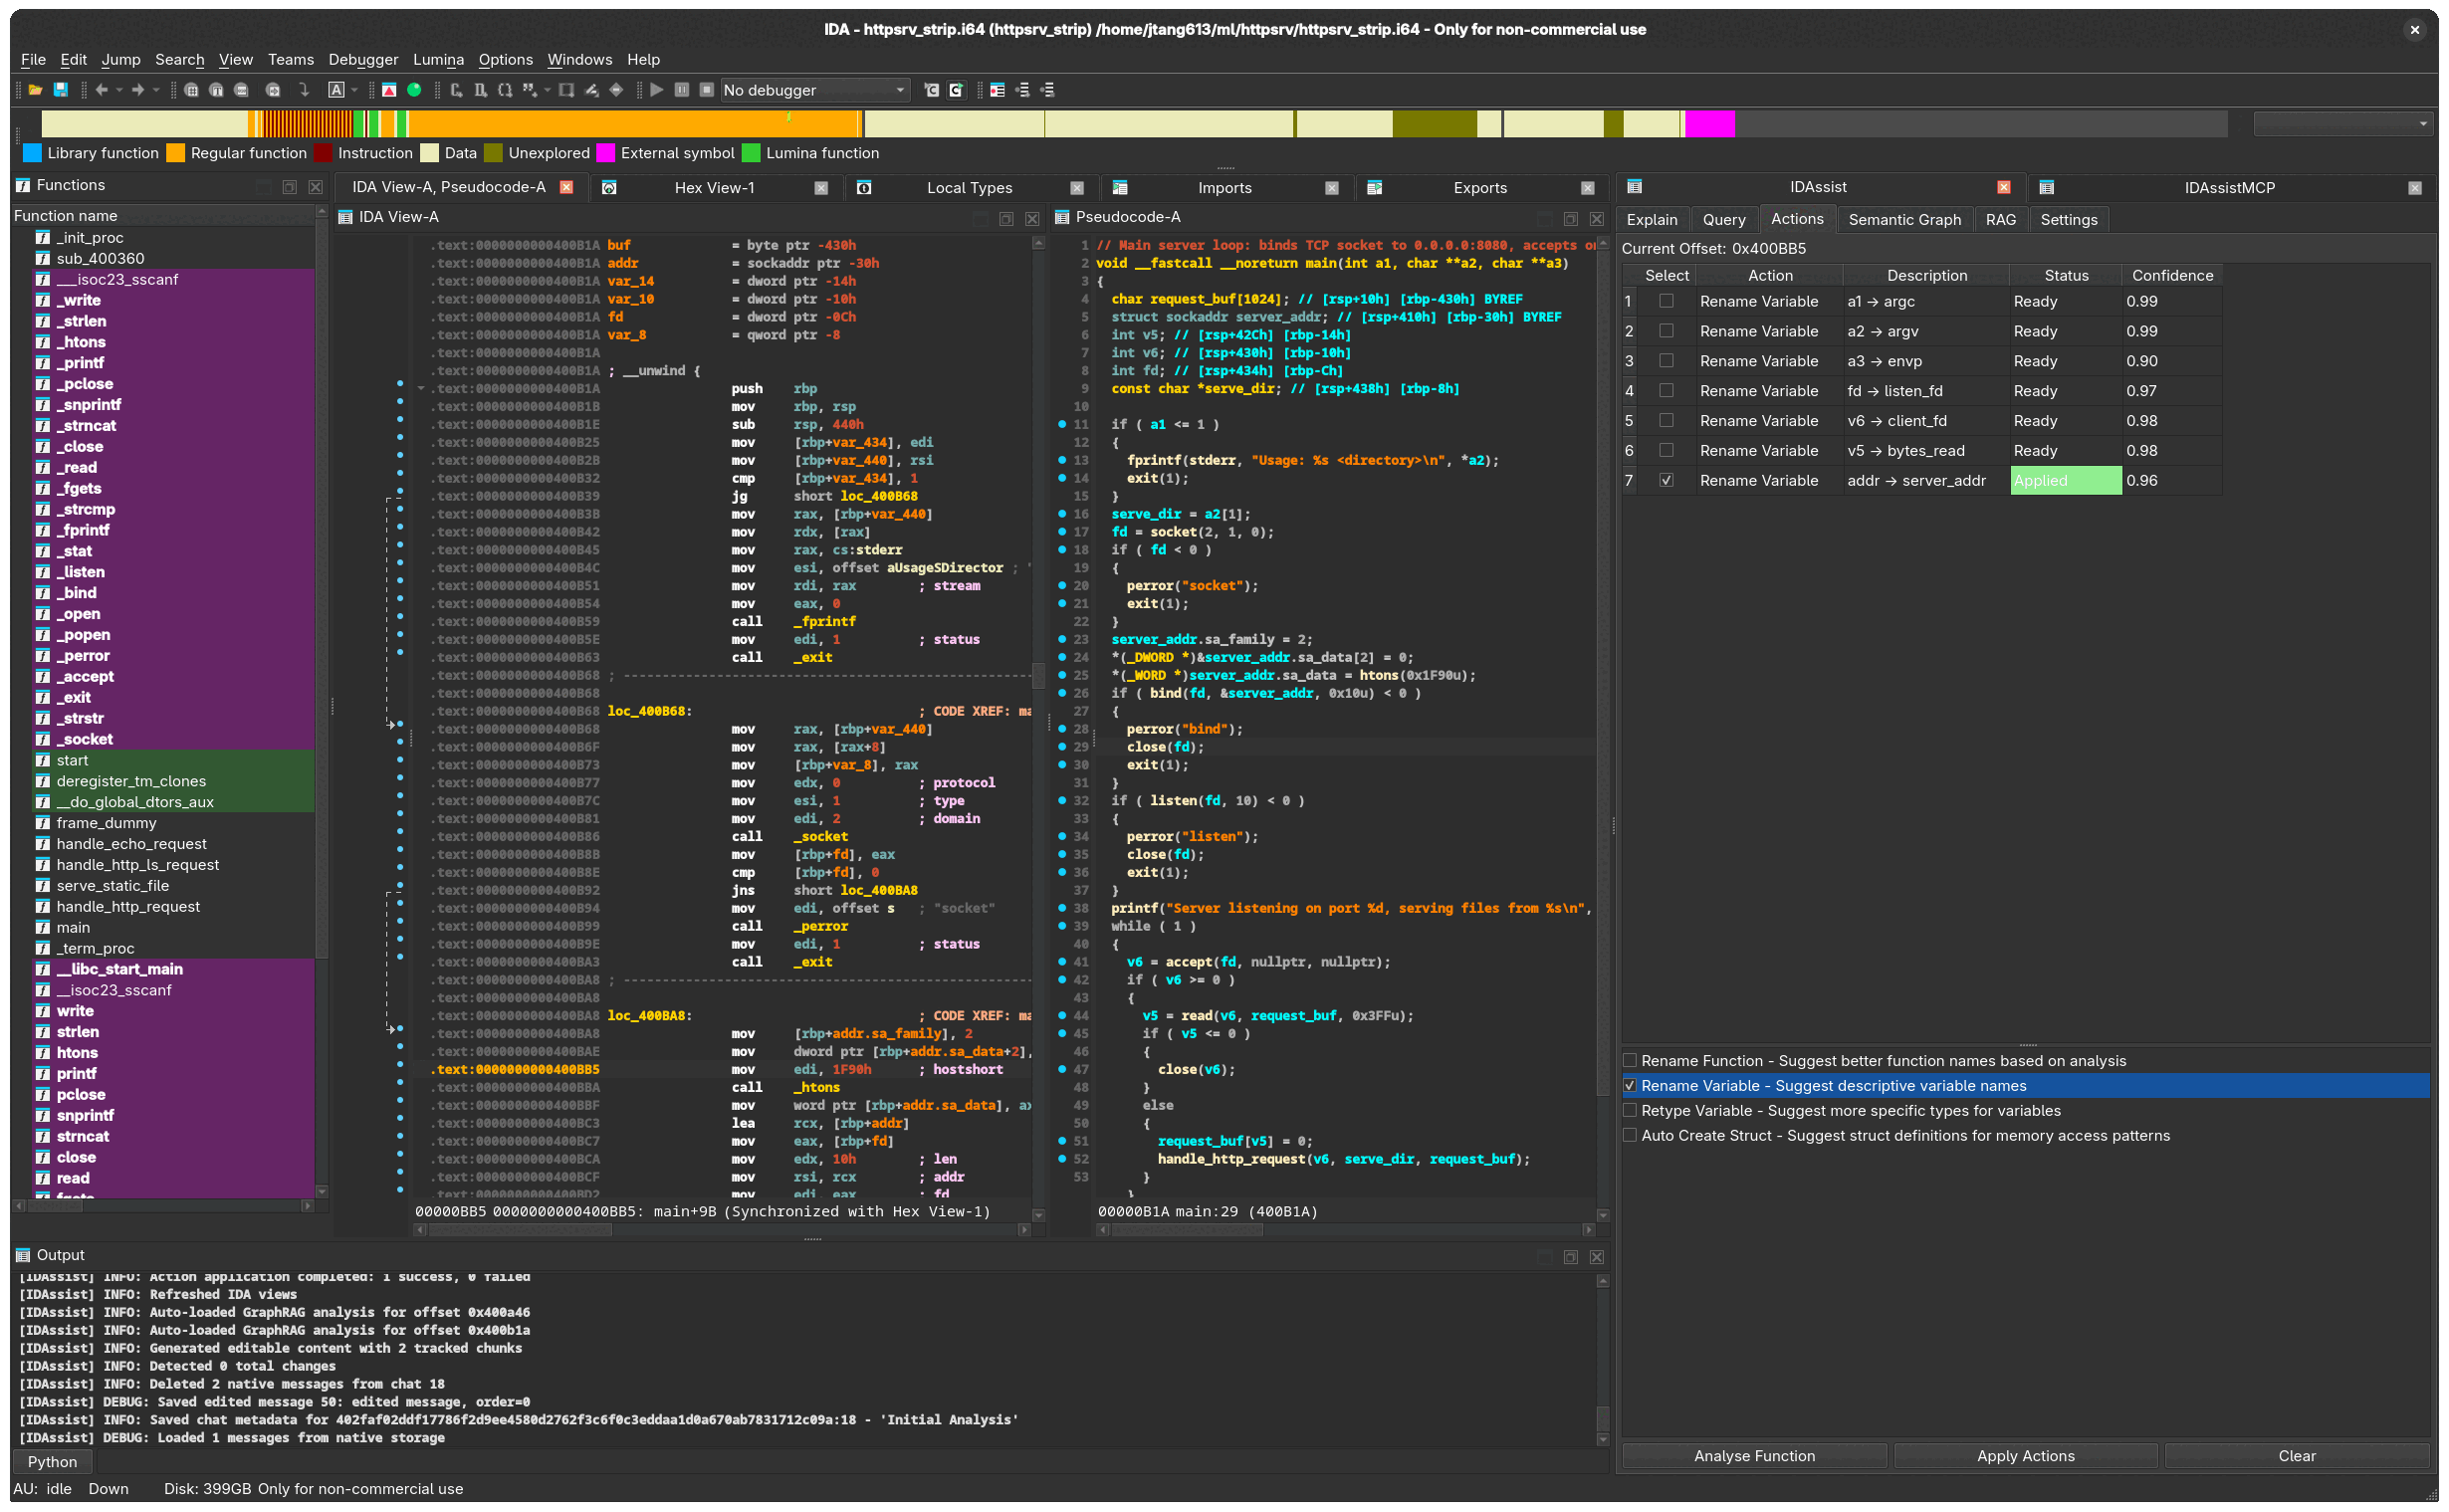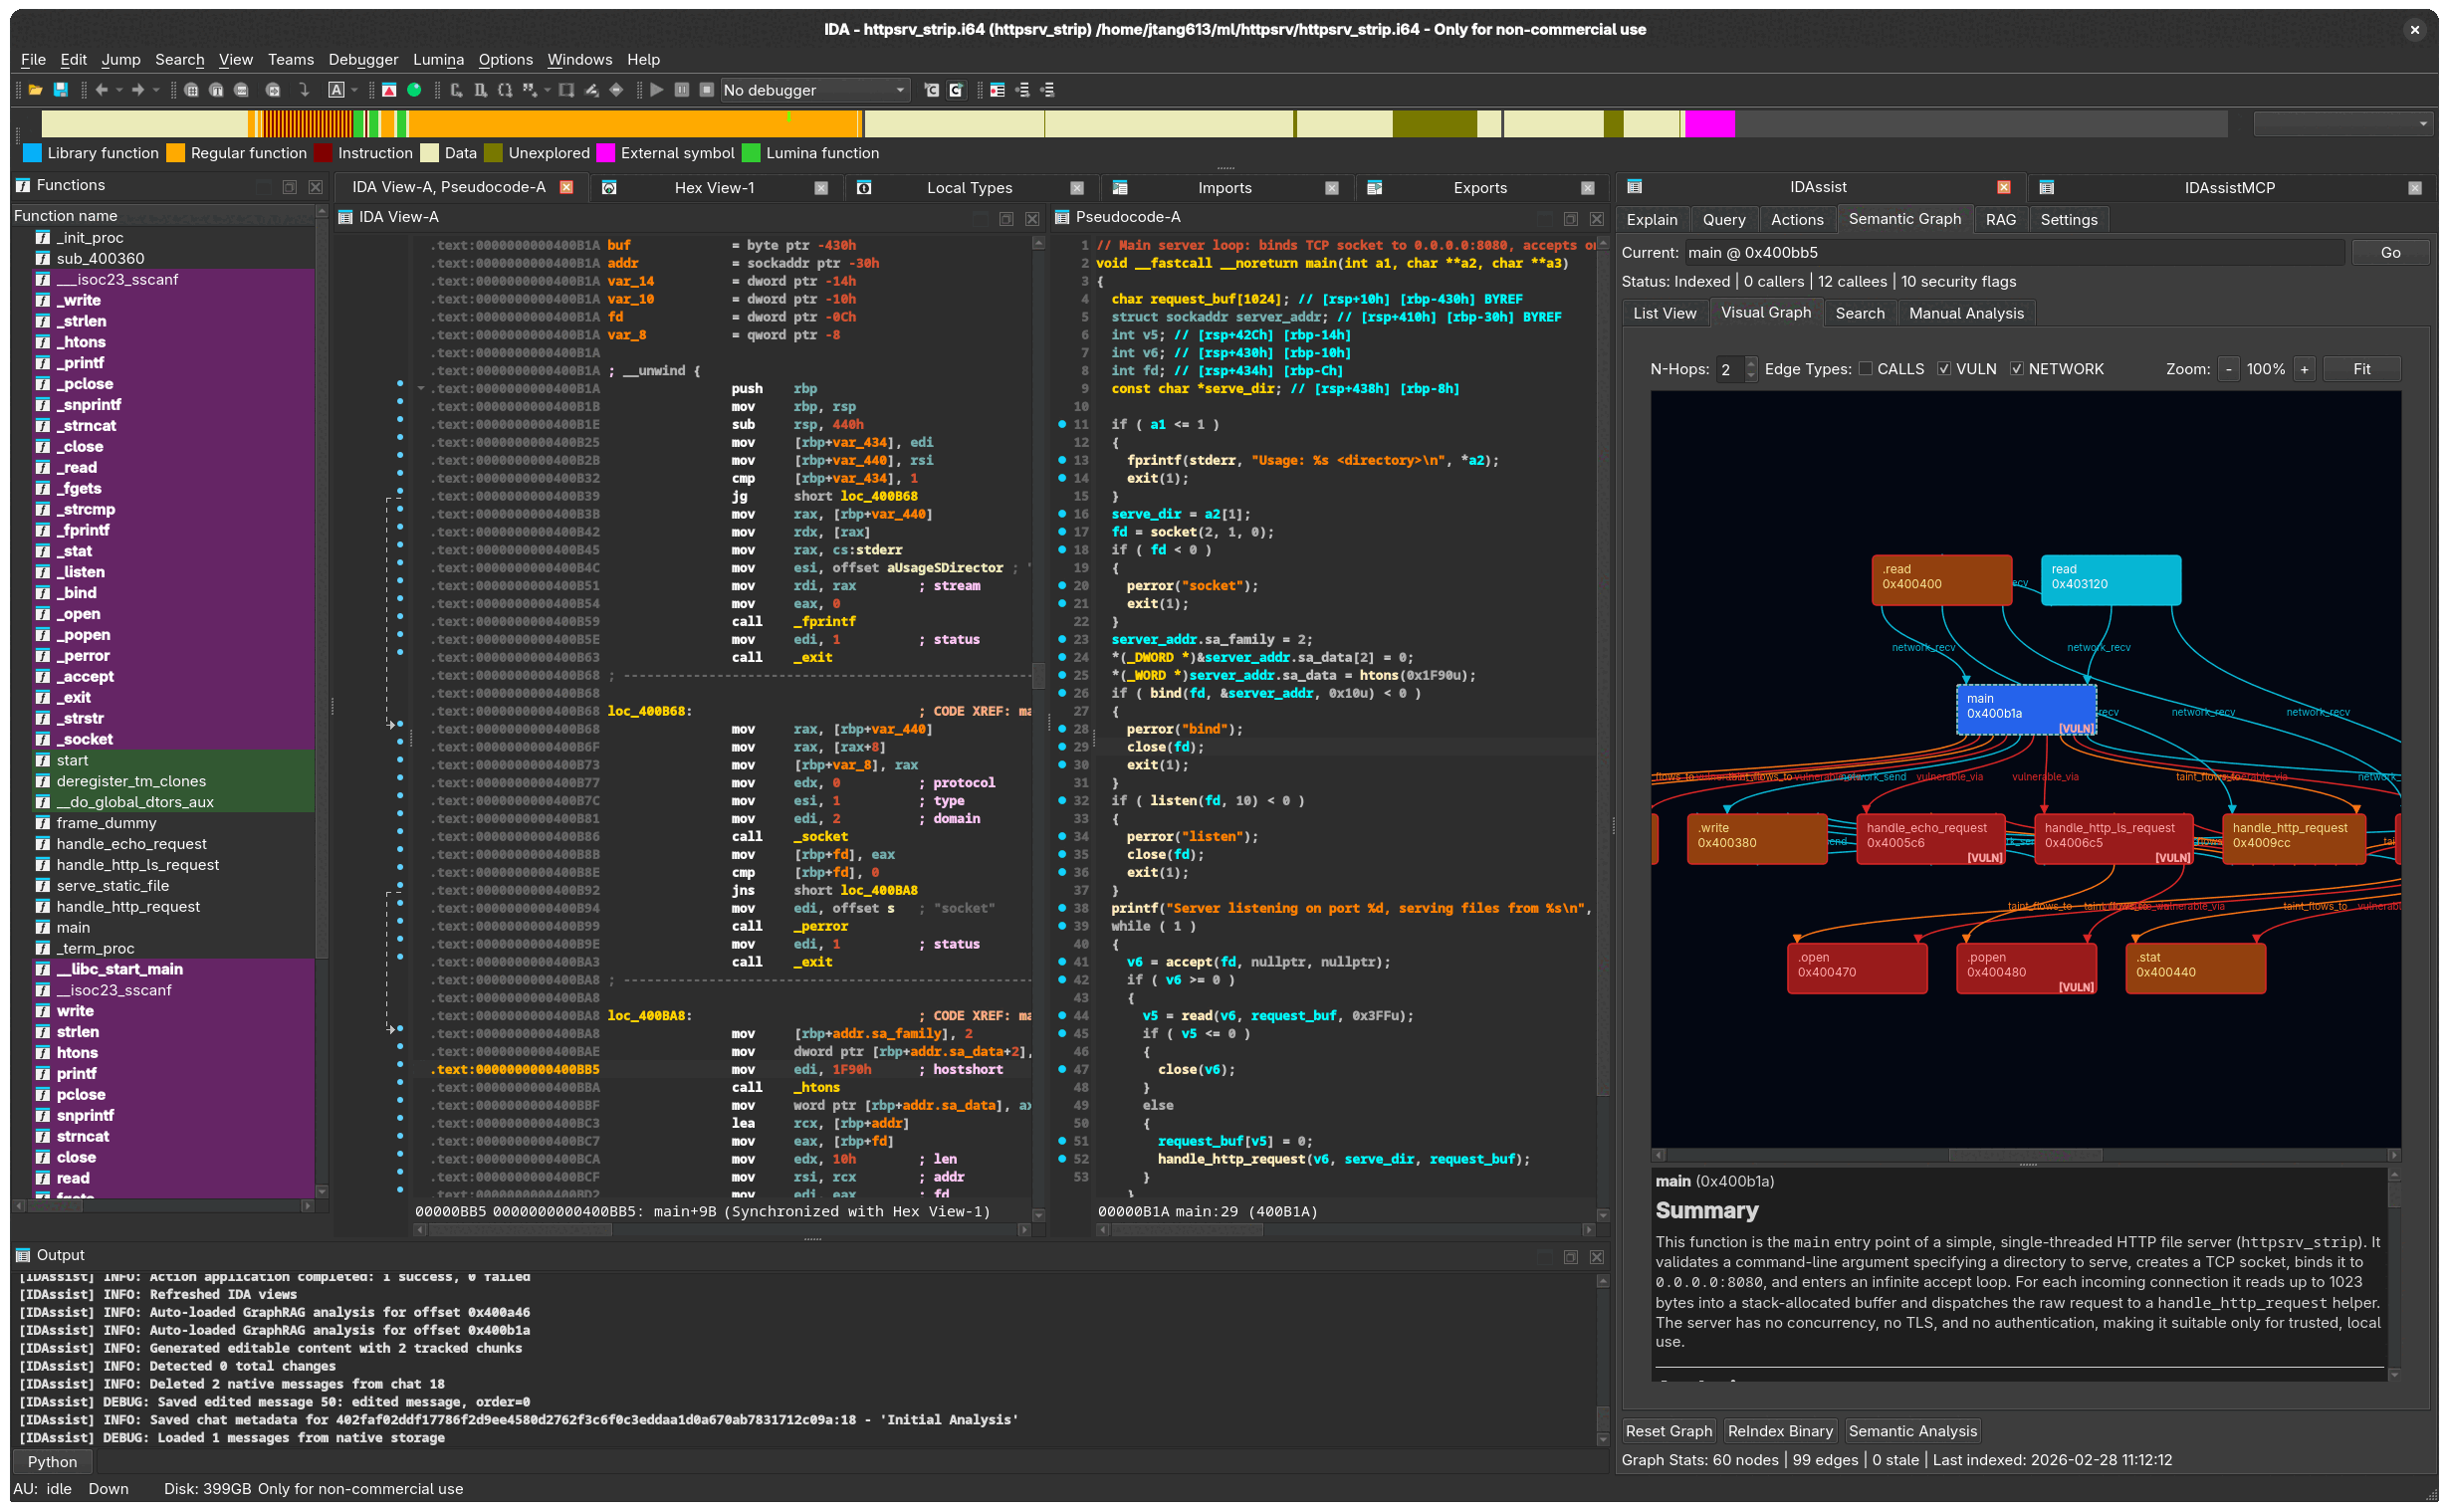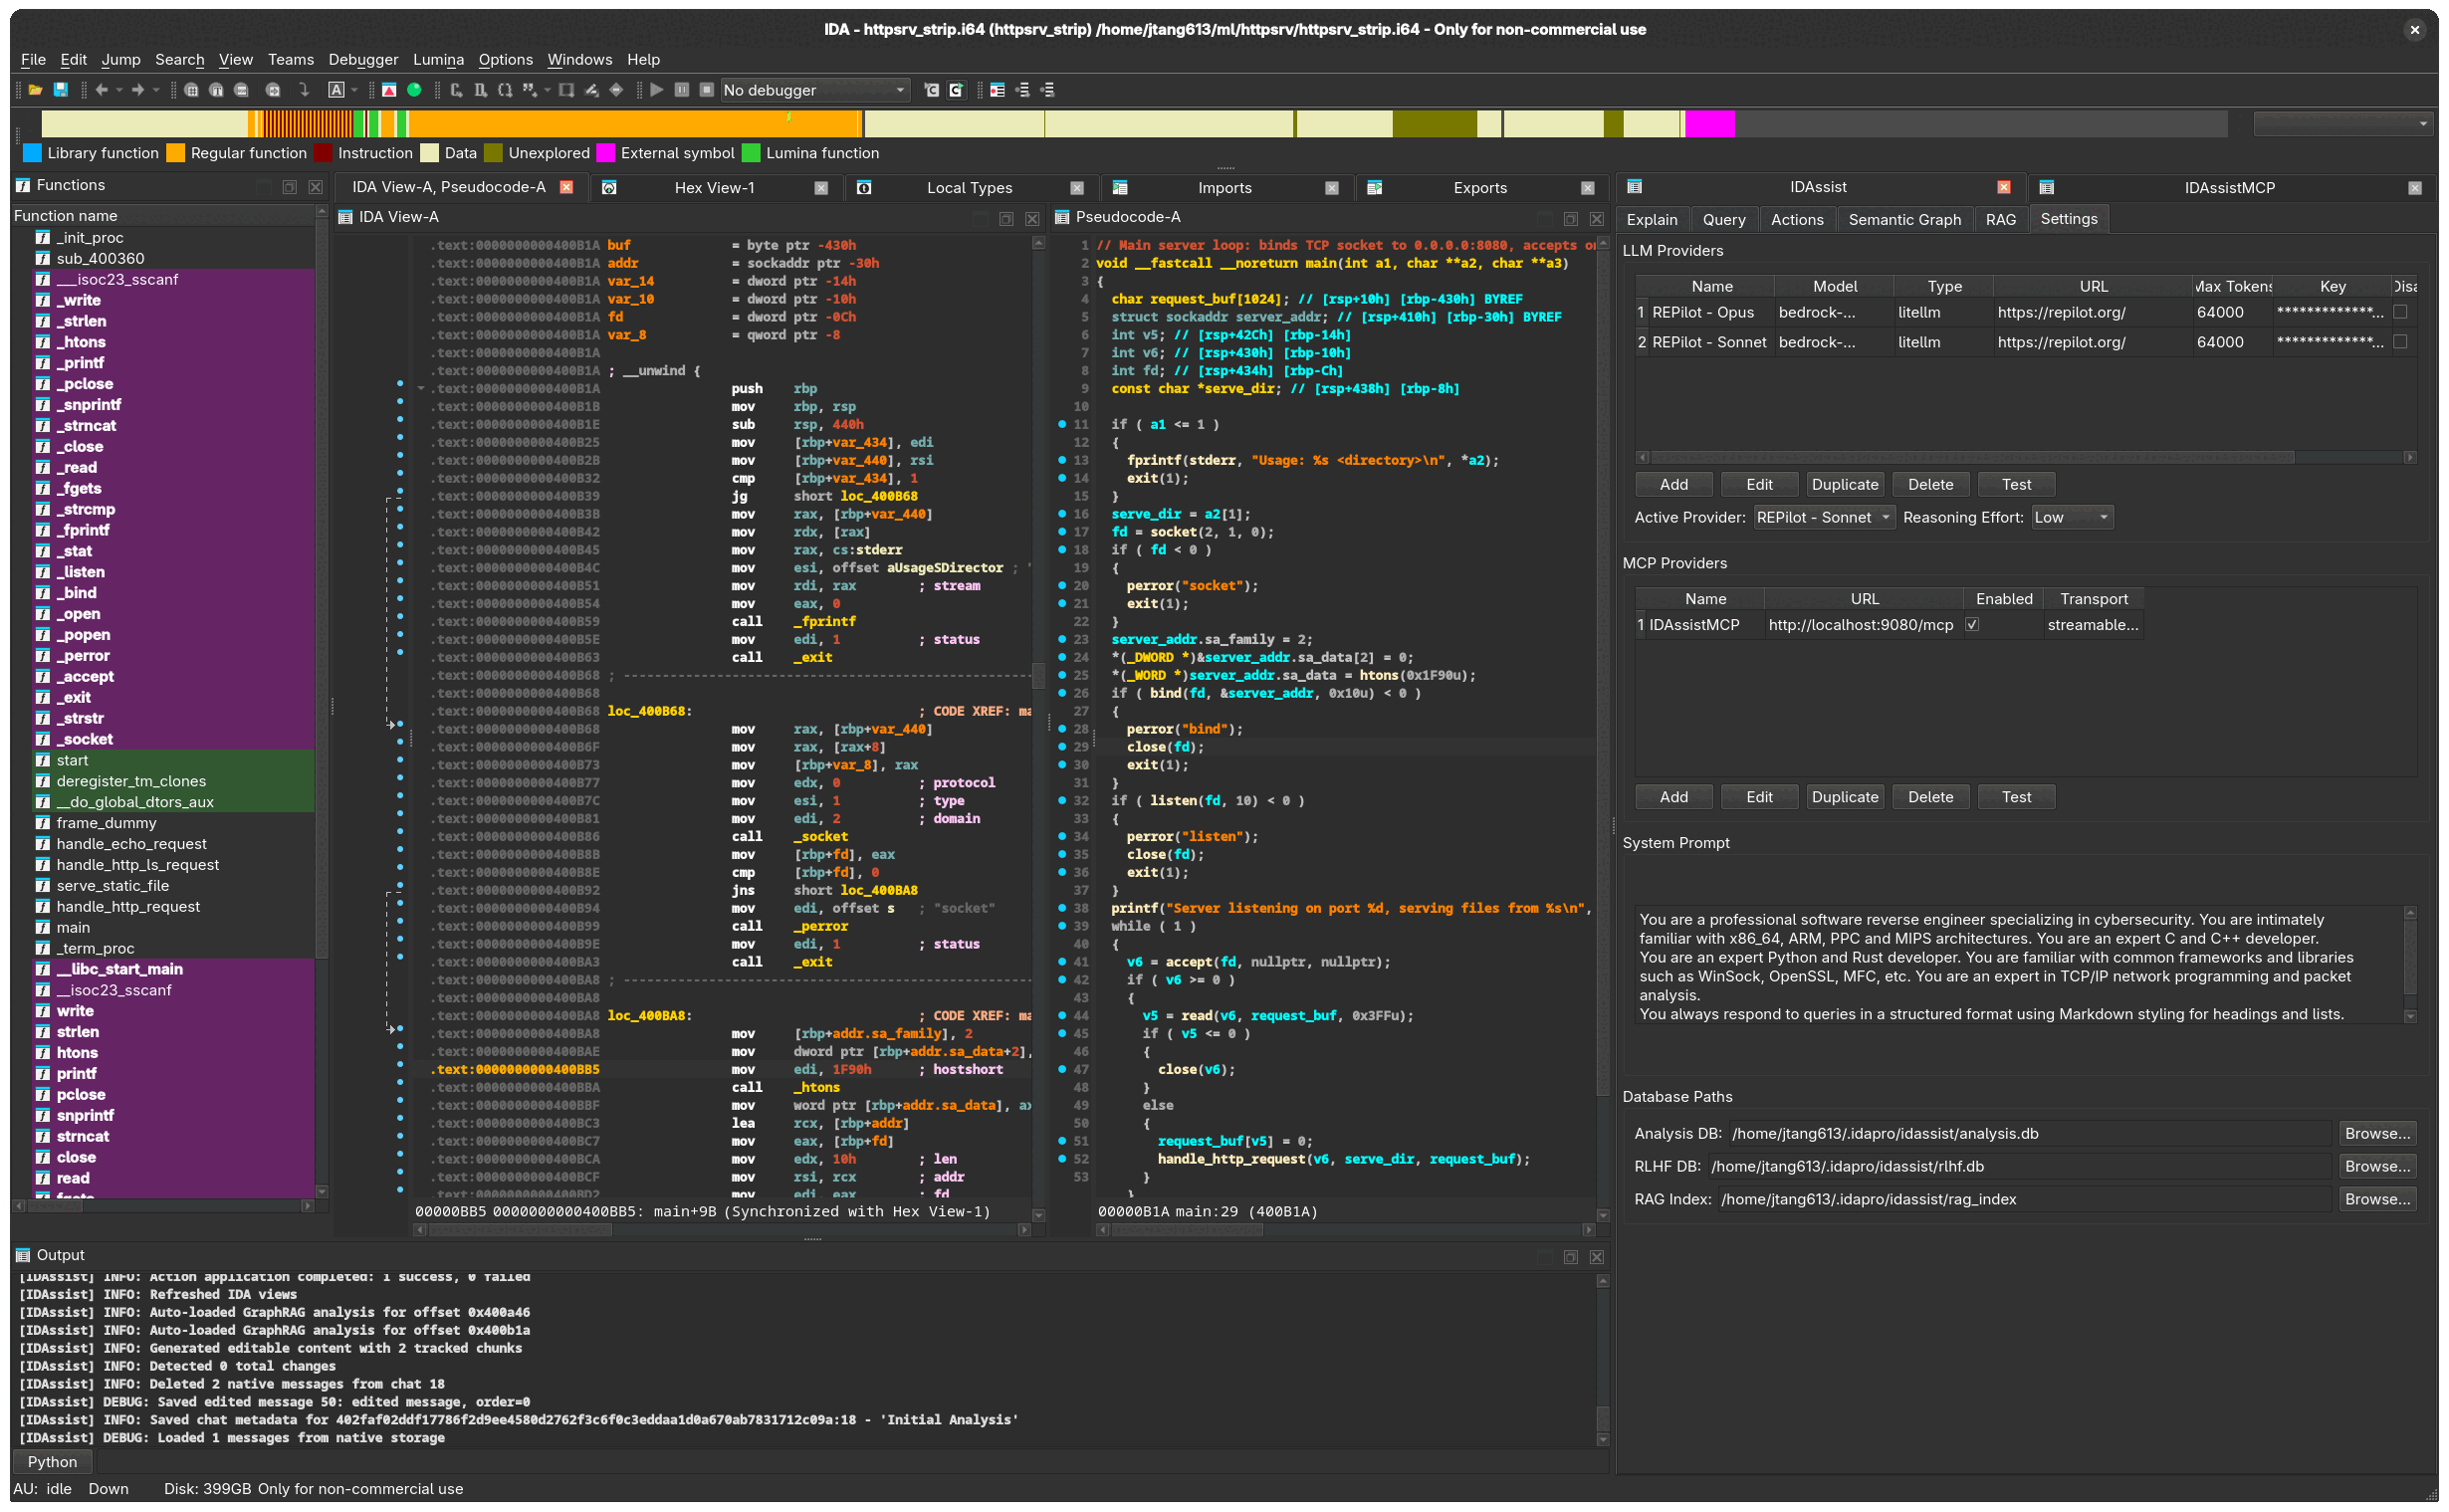
AI-Powered Reverse Engineering Plugin for IDA Pro

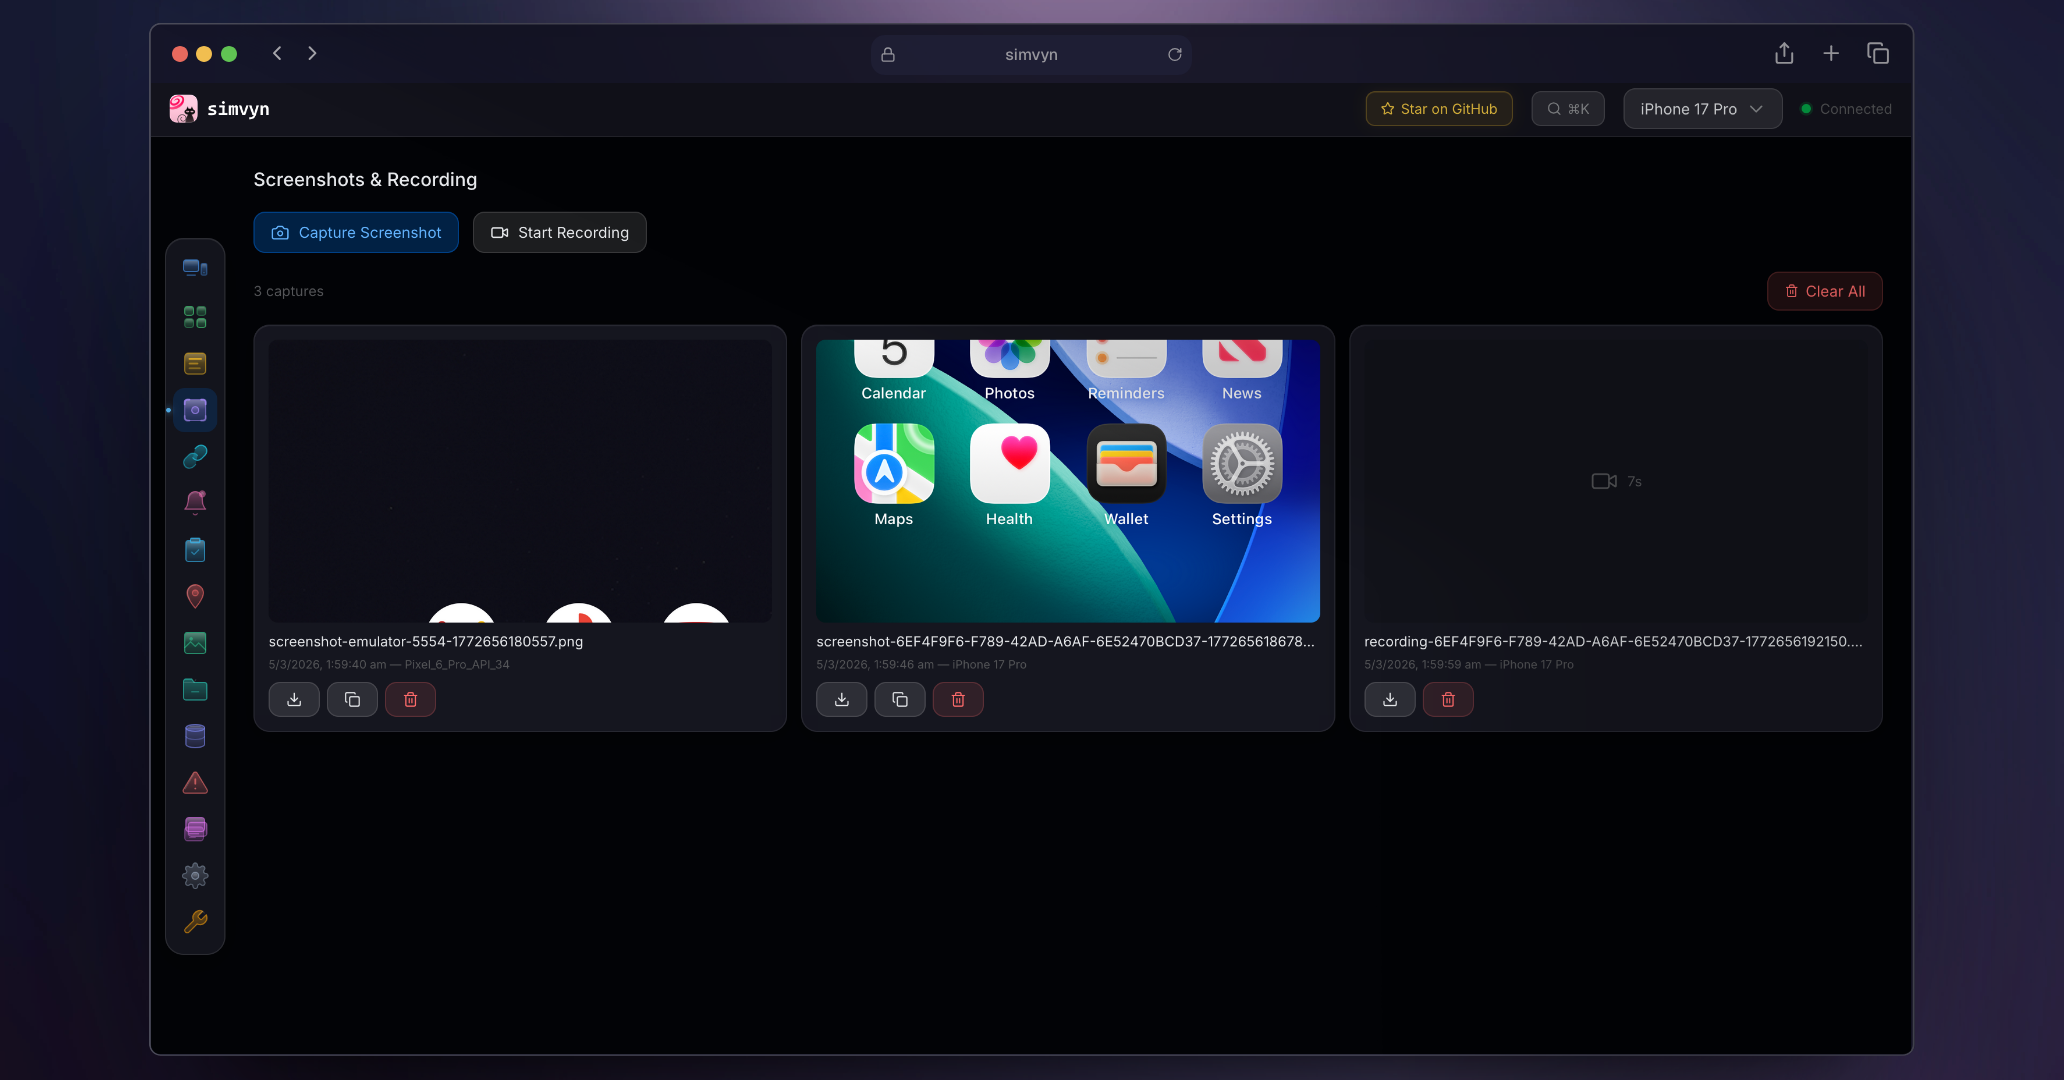
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

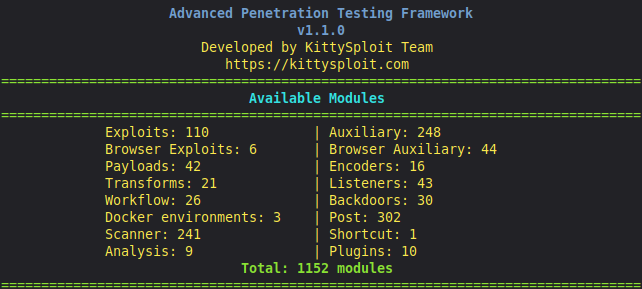
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....

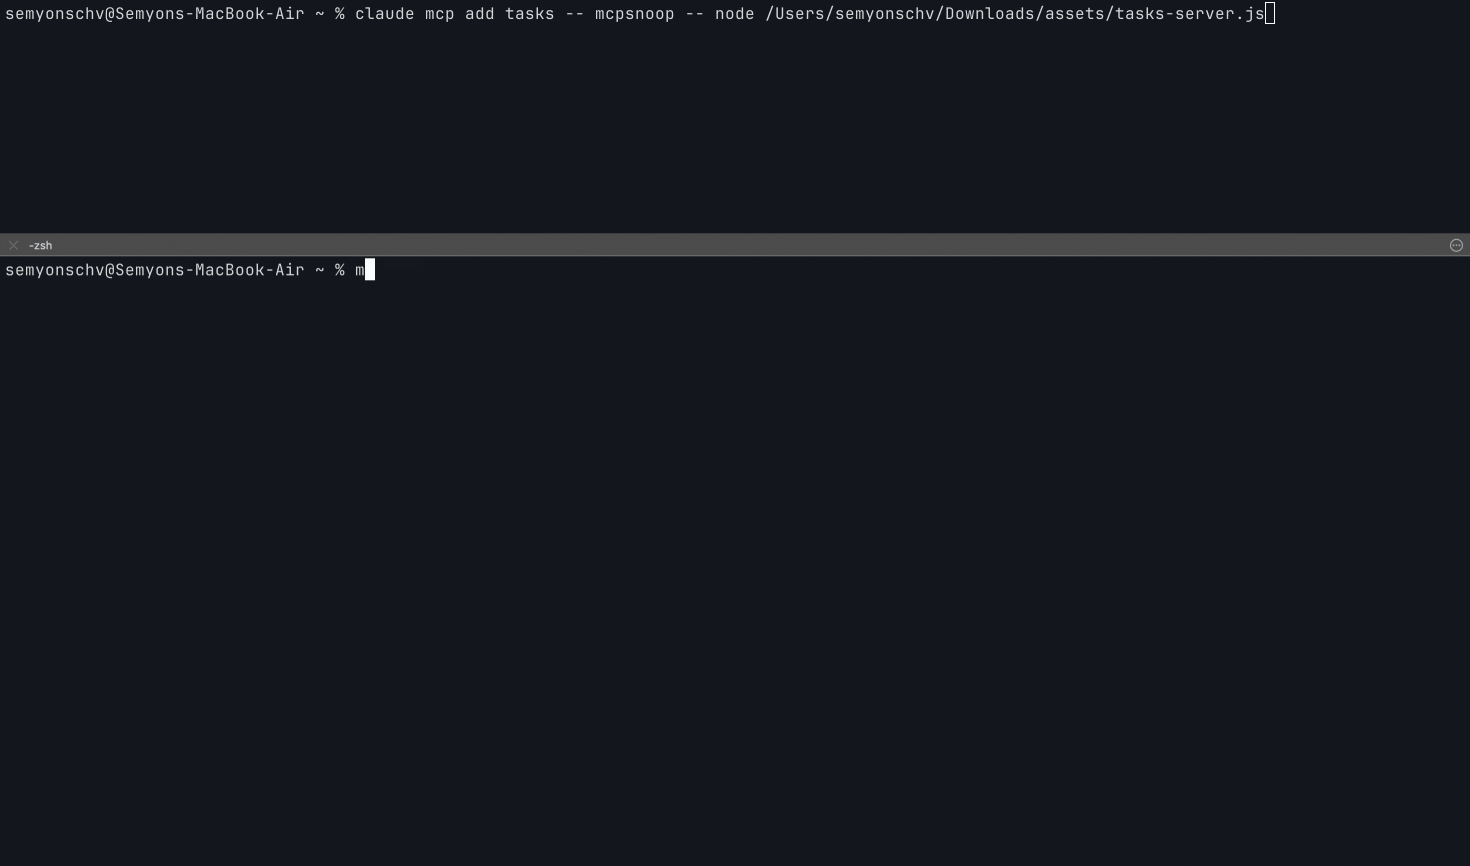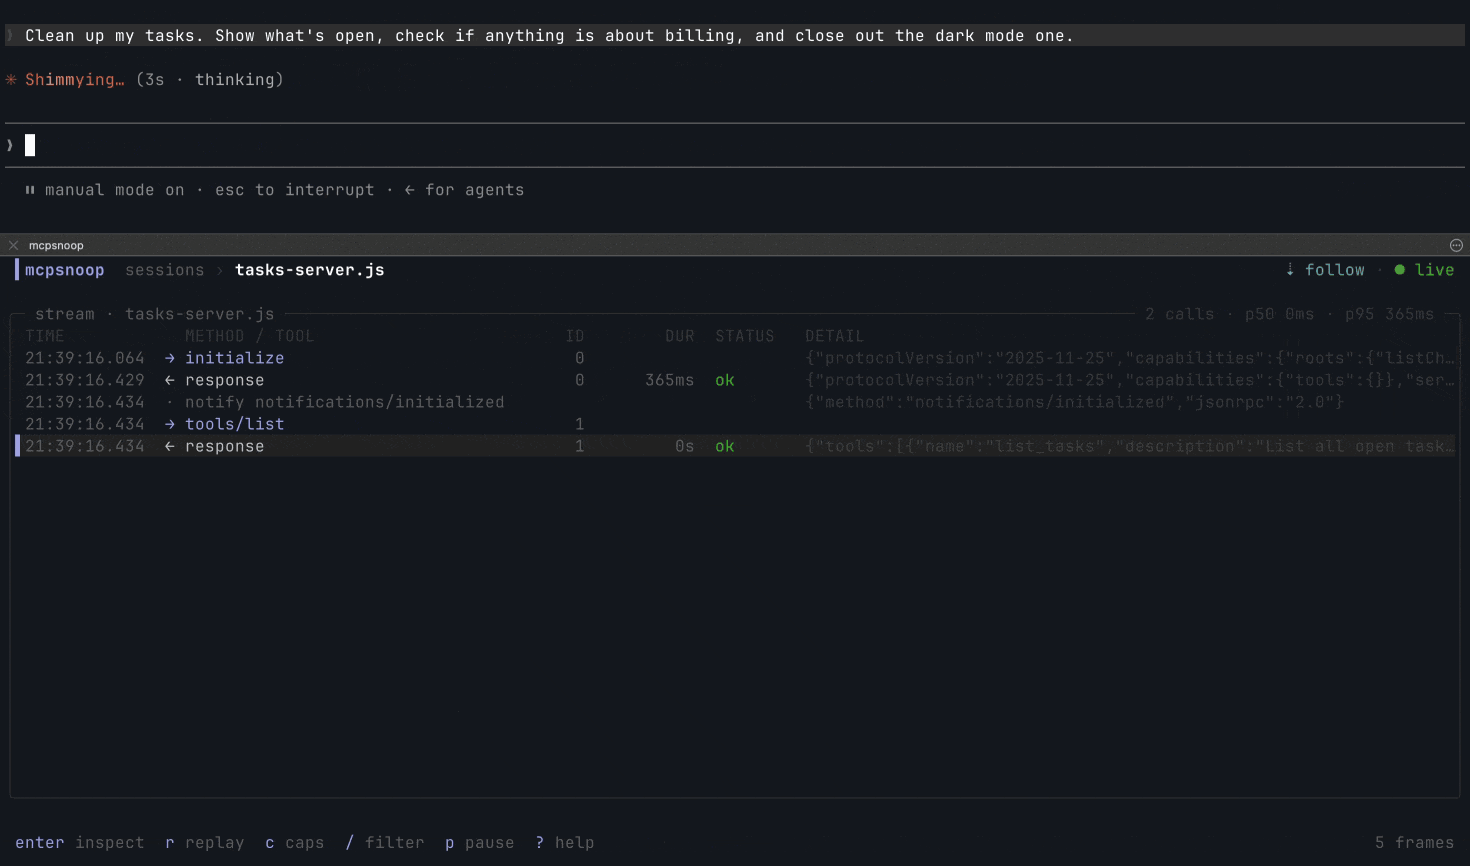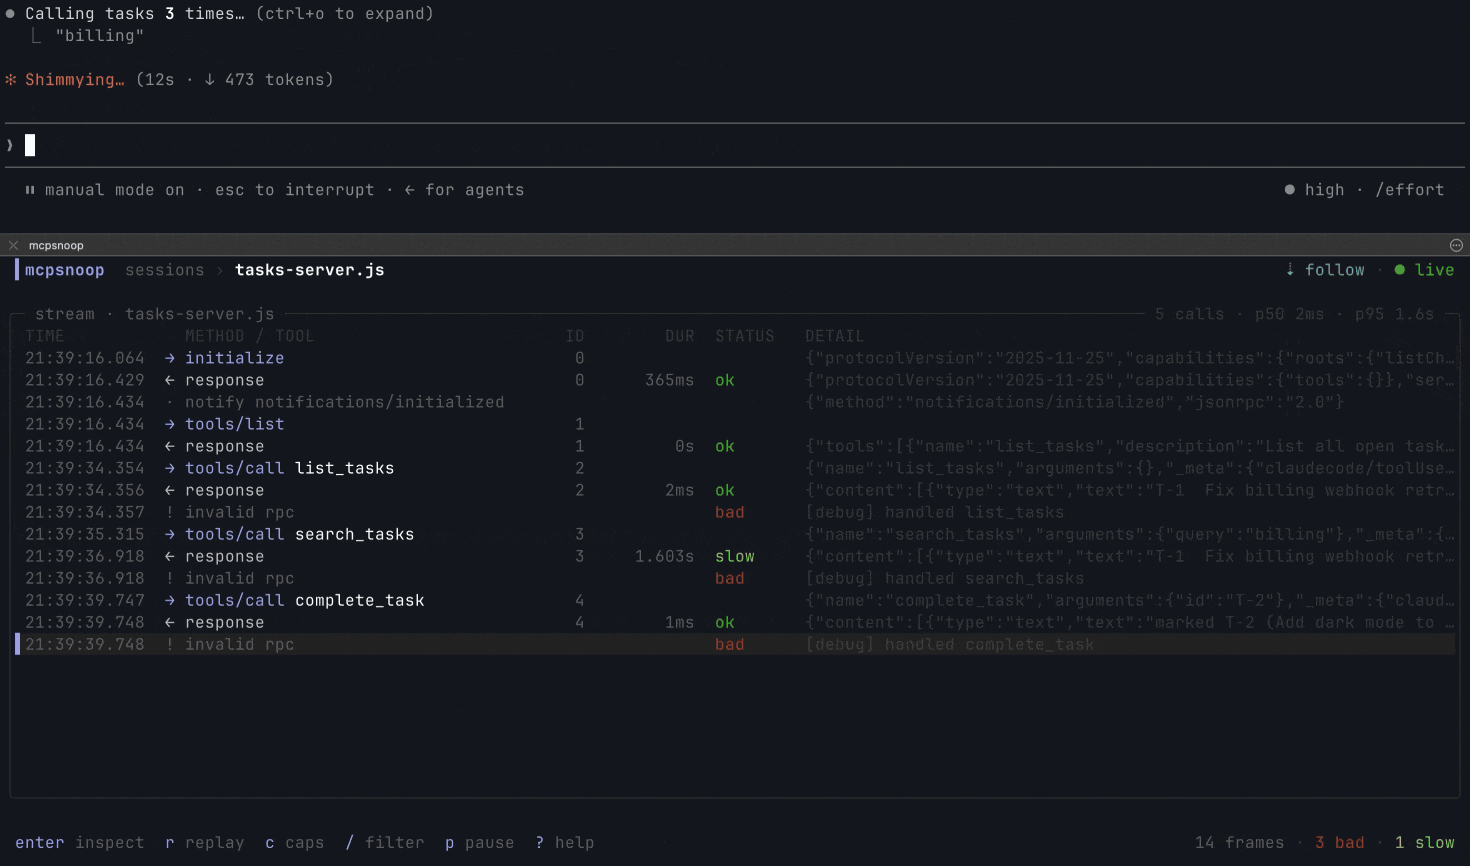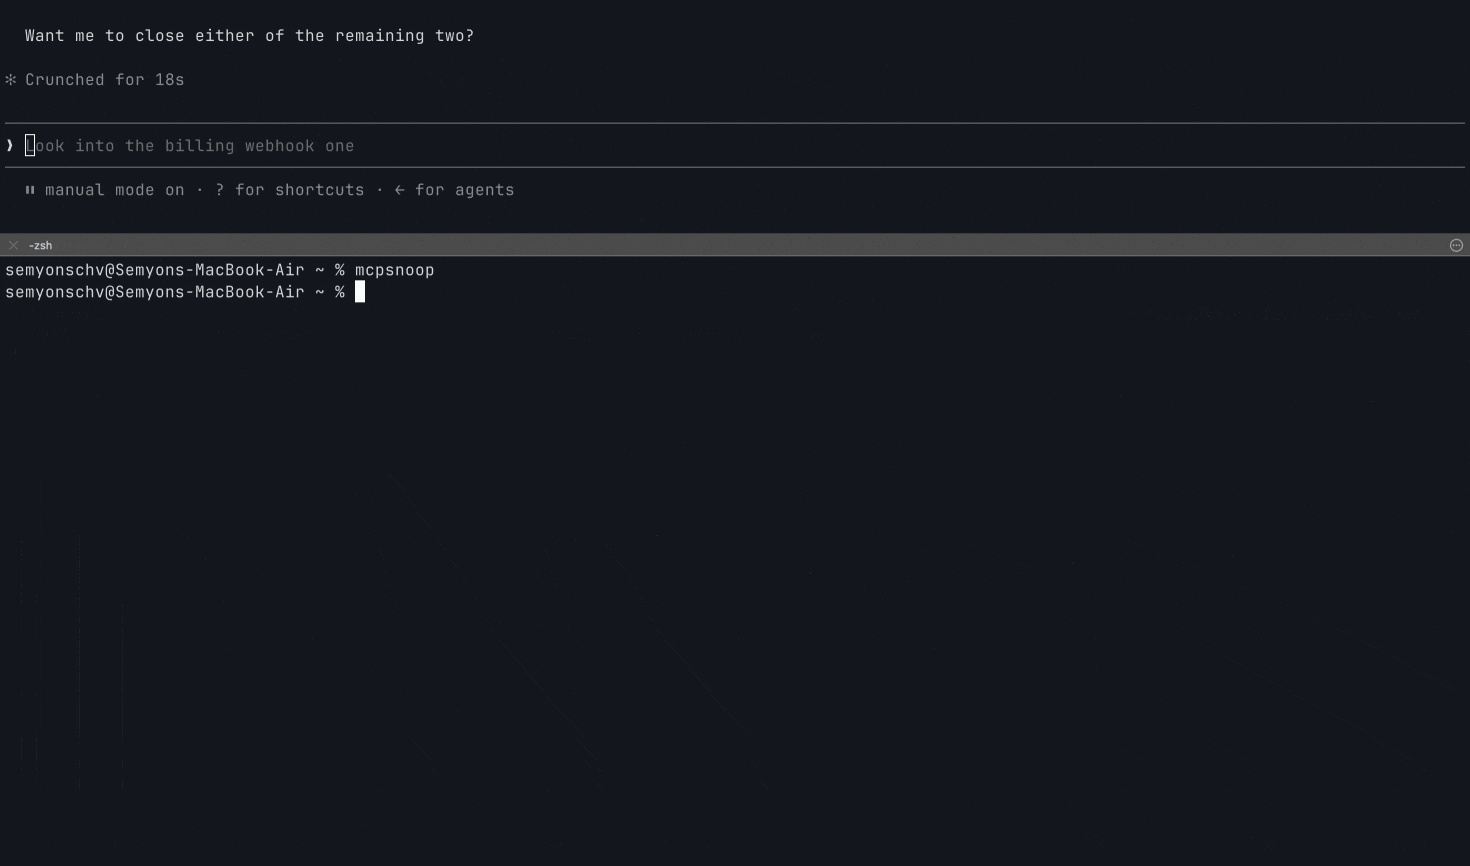
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…