

hermit
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitybinary-analysiscode-analysis+7
6
xv4l3x/hermitInspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
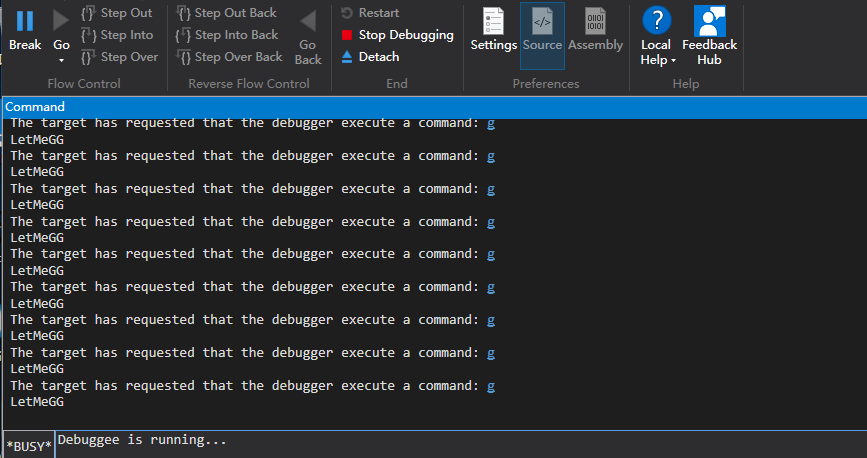 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
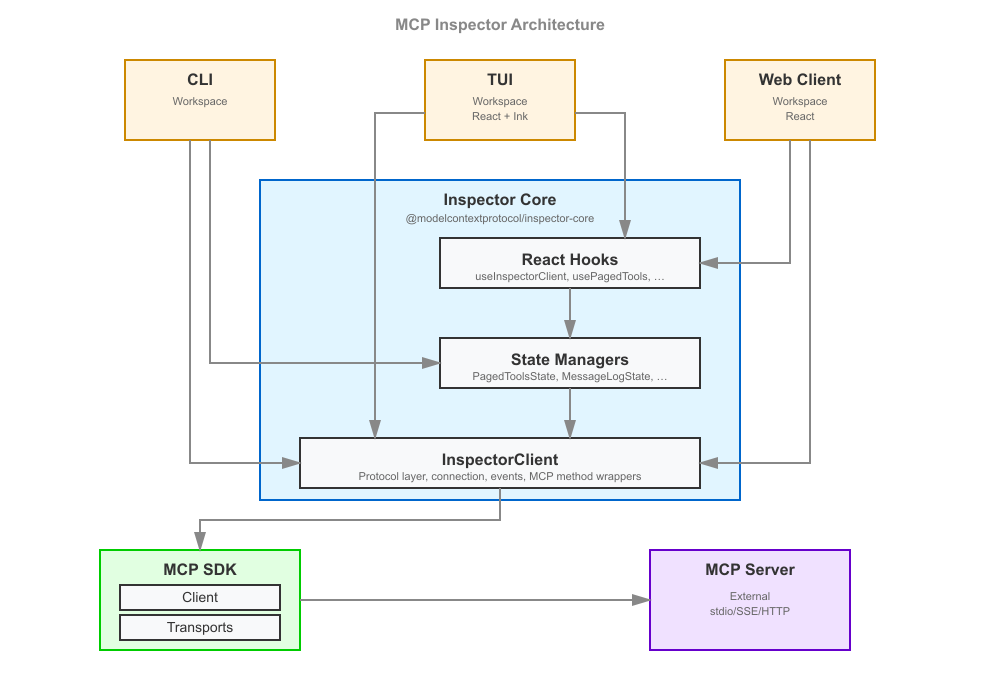 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
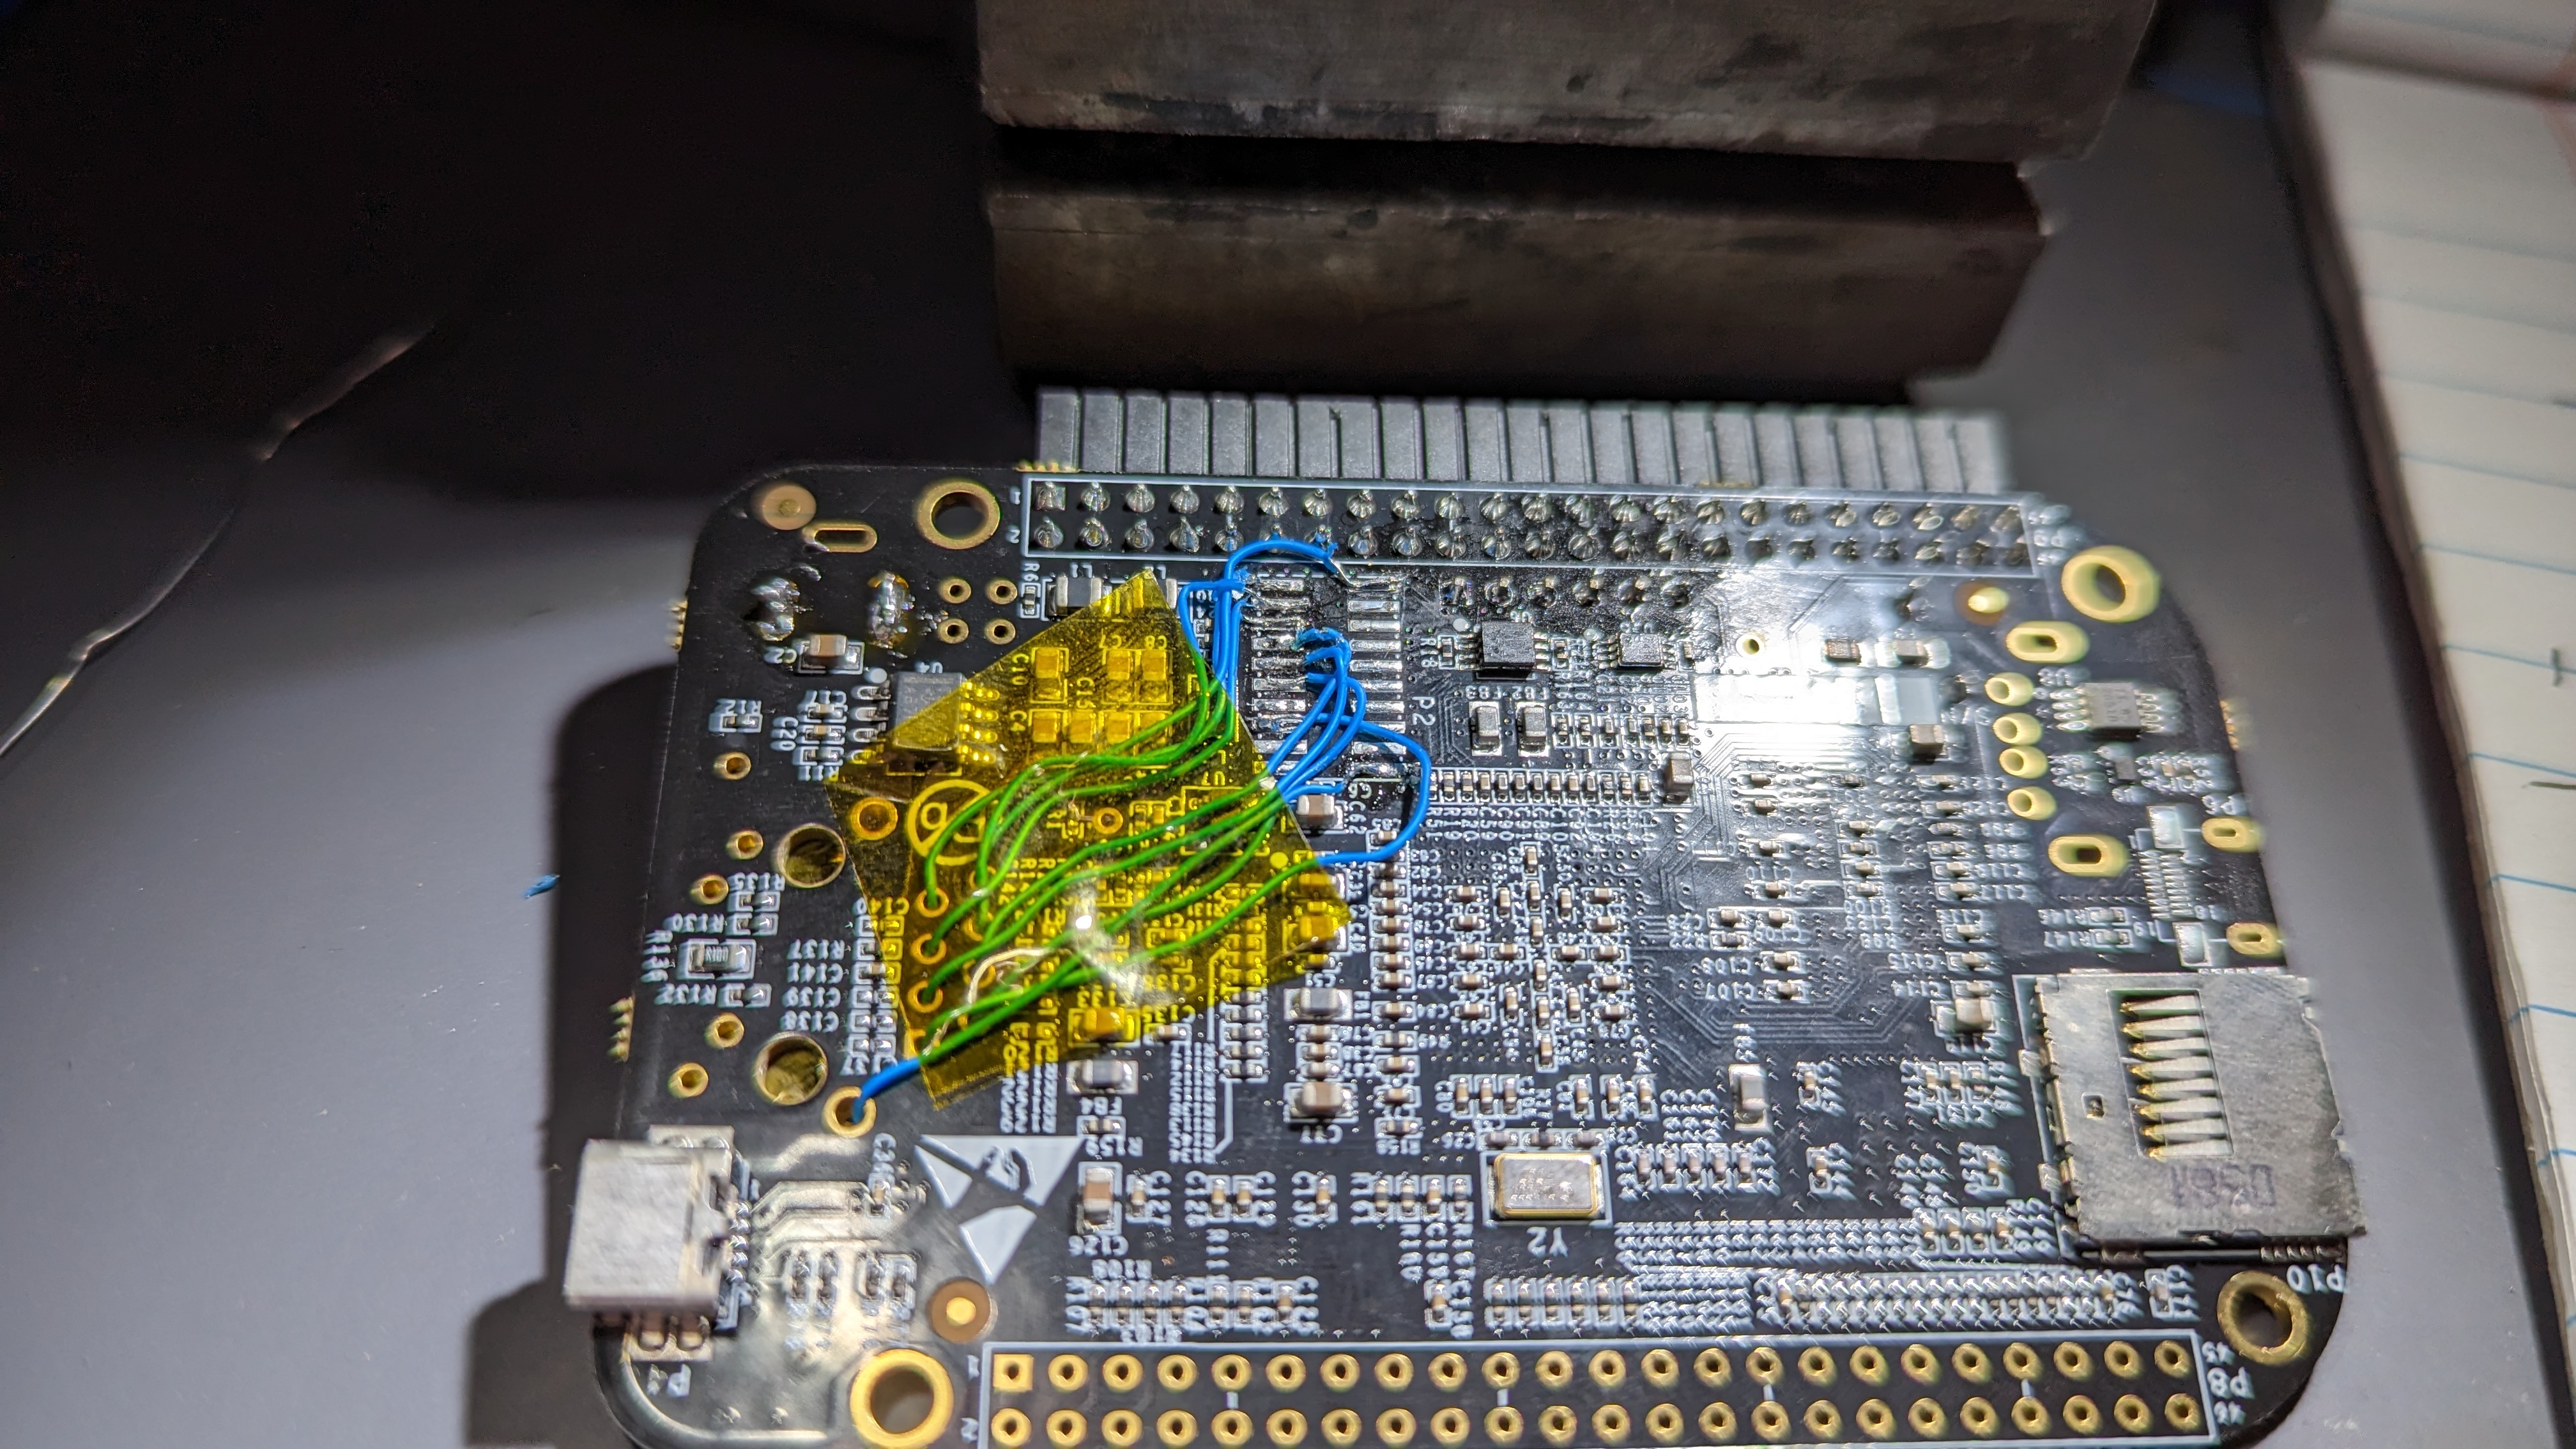 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 piffd0s/ntoskrnl-metadata
eprocess offset puller for relevant member offsets and function addresses for cve-2026-40369
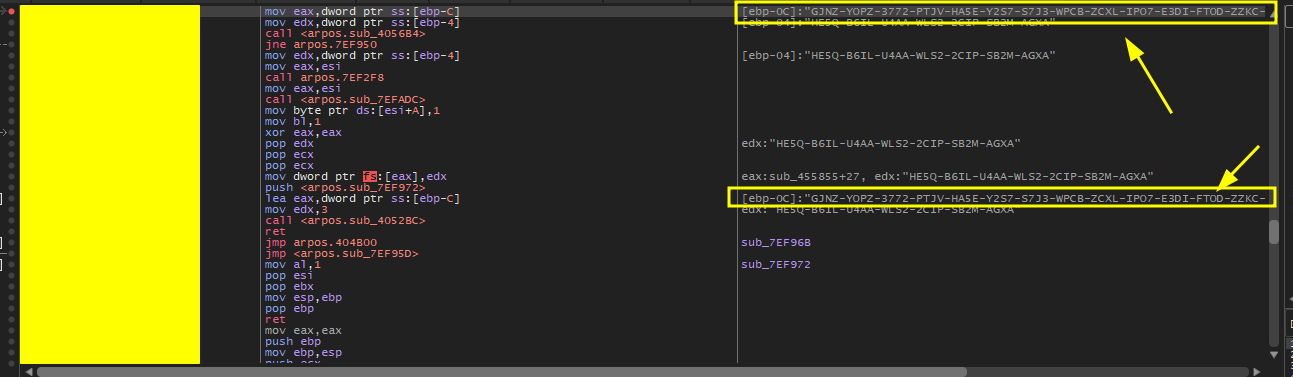 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
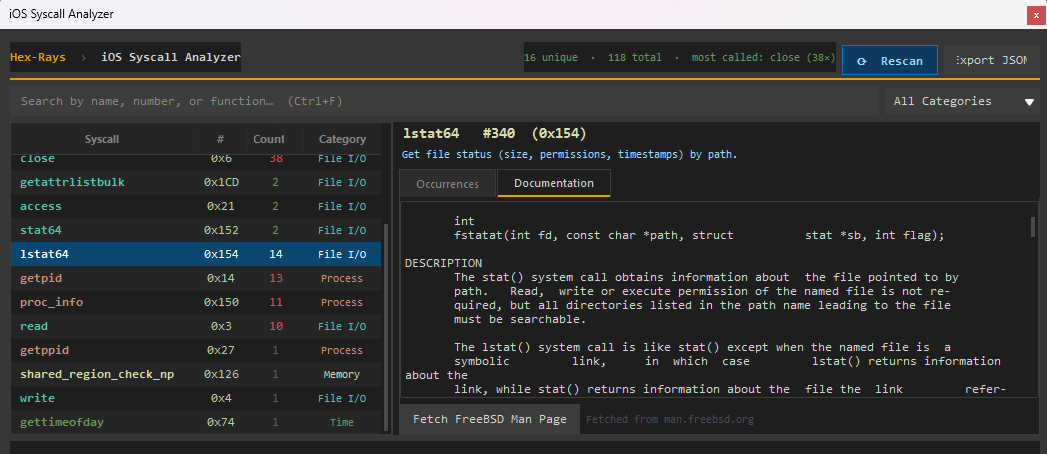 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…