
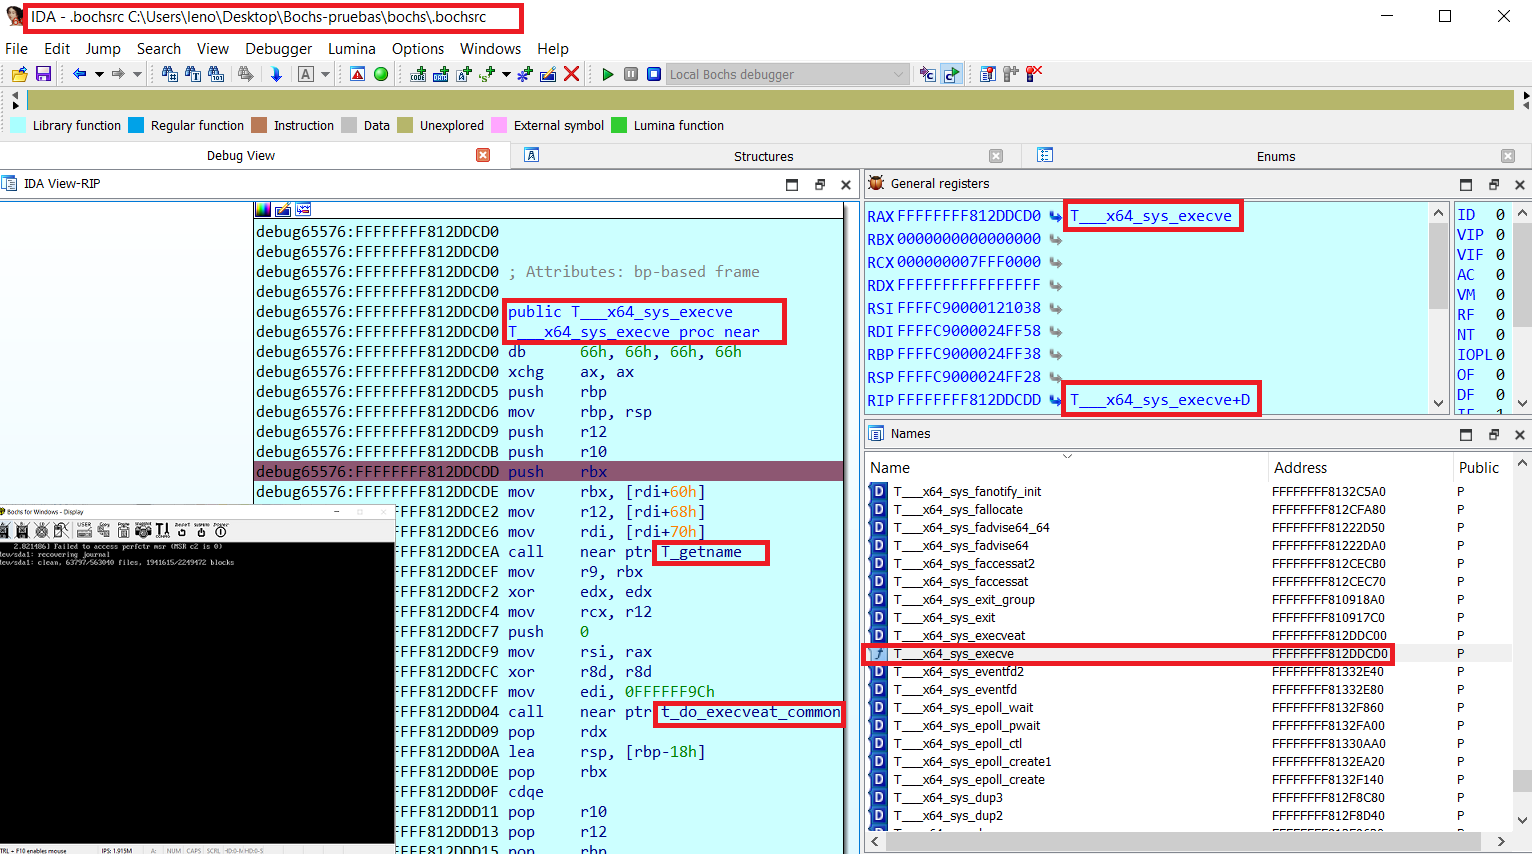
bochs_linux_kernel_debugging
 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
binary-analysisdebuggerseducation+1
33
therealdreg/bochs_linux_kernel_debuggingTools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
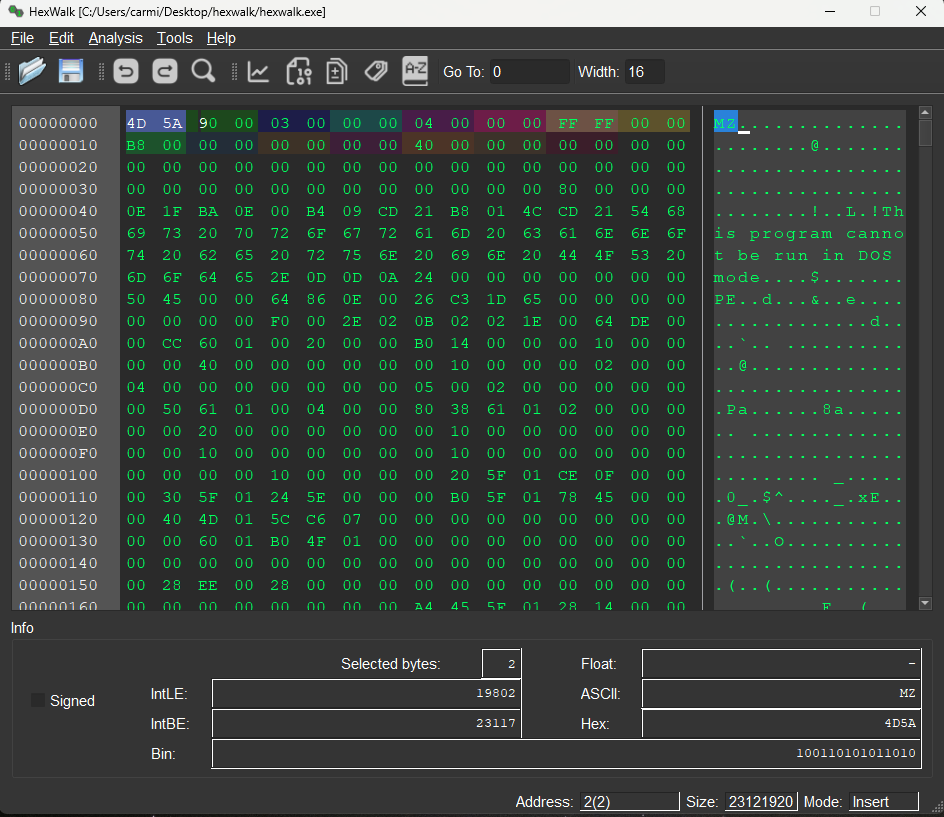 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
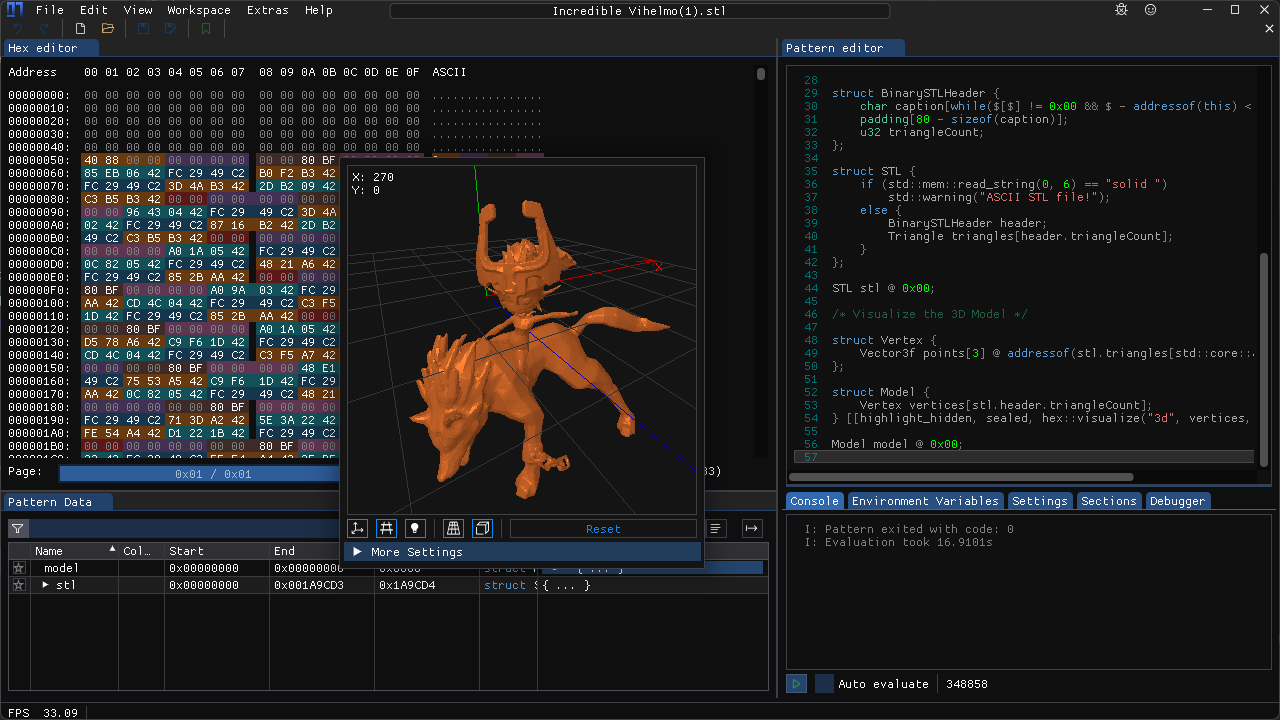 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
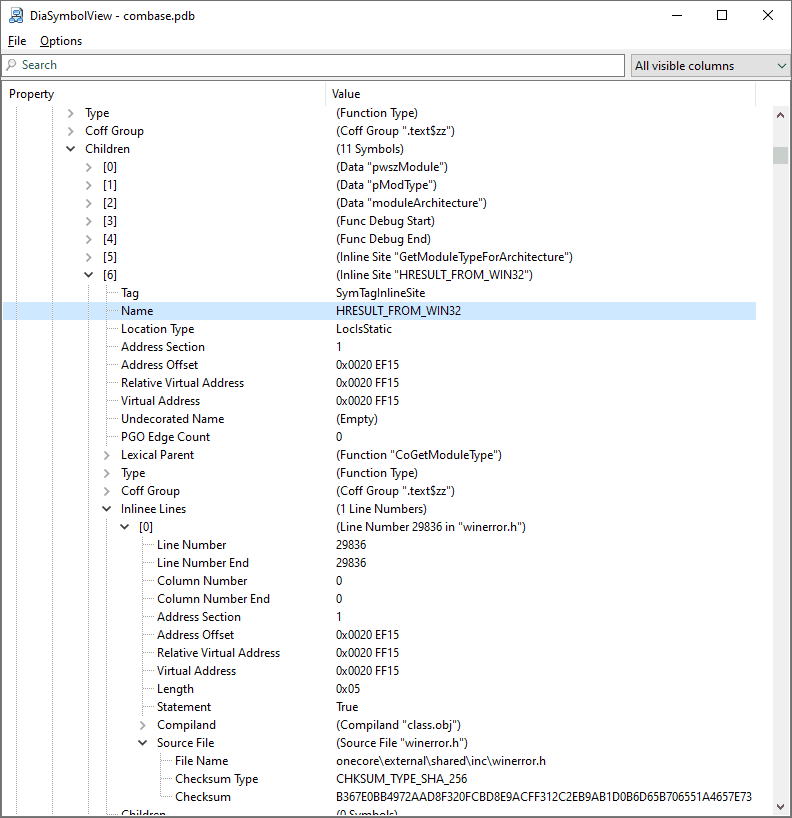 diversenok/diasymbolview
PDB file inspection tool
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 cdacesec/cve-2022-31902
Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 iddoeldor/frida-snippets
Hand-crafted Frida examples
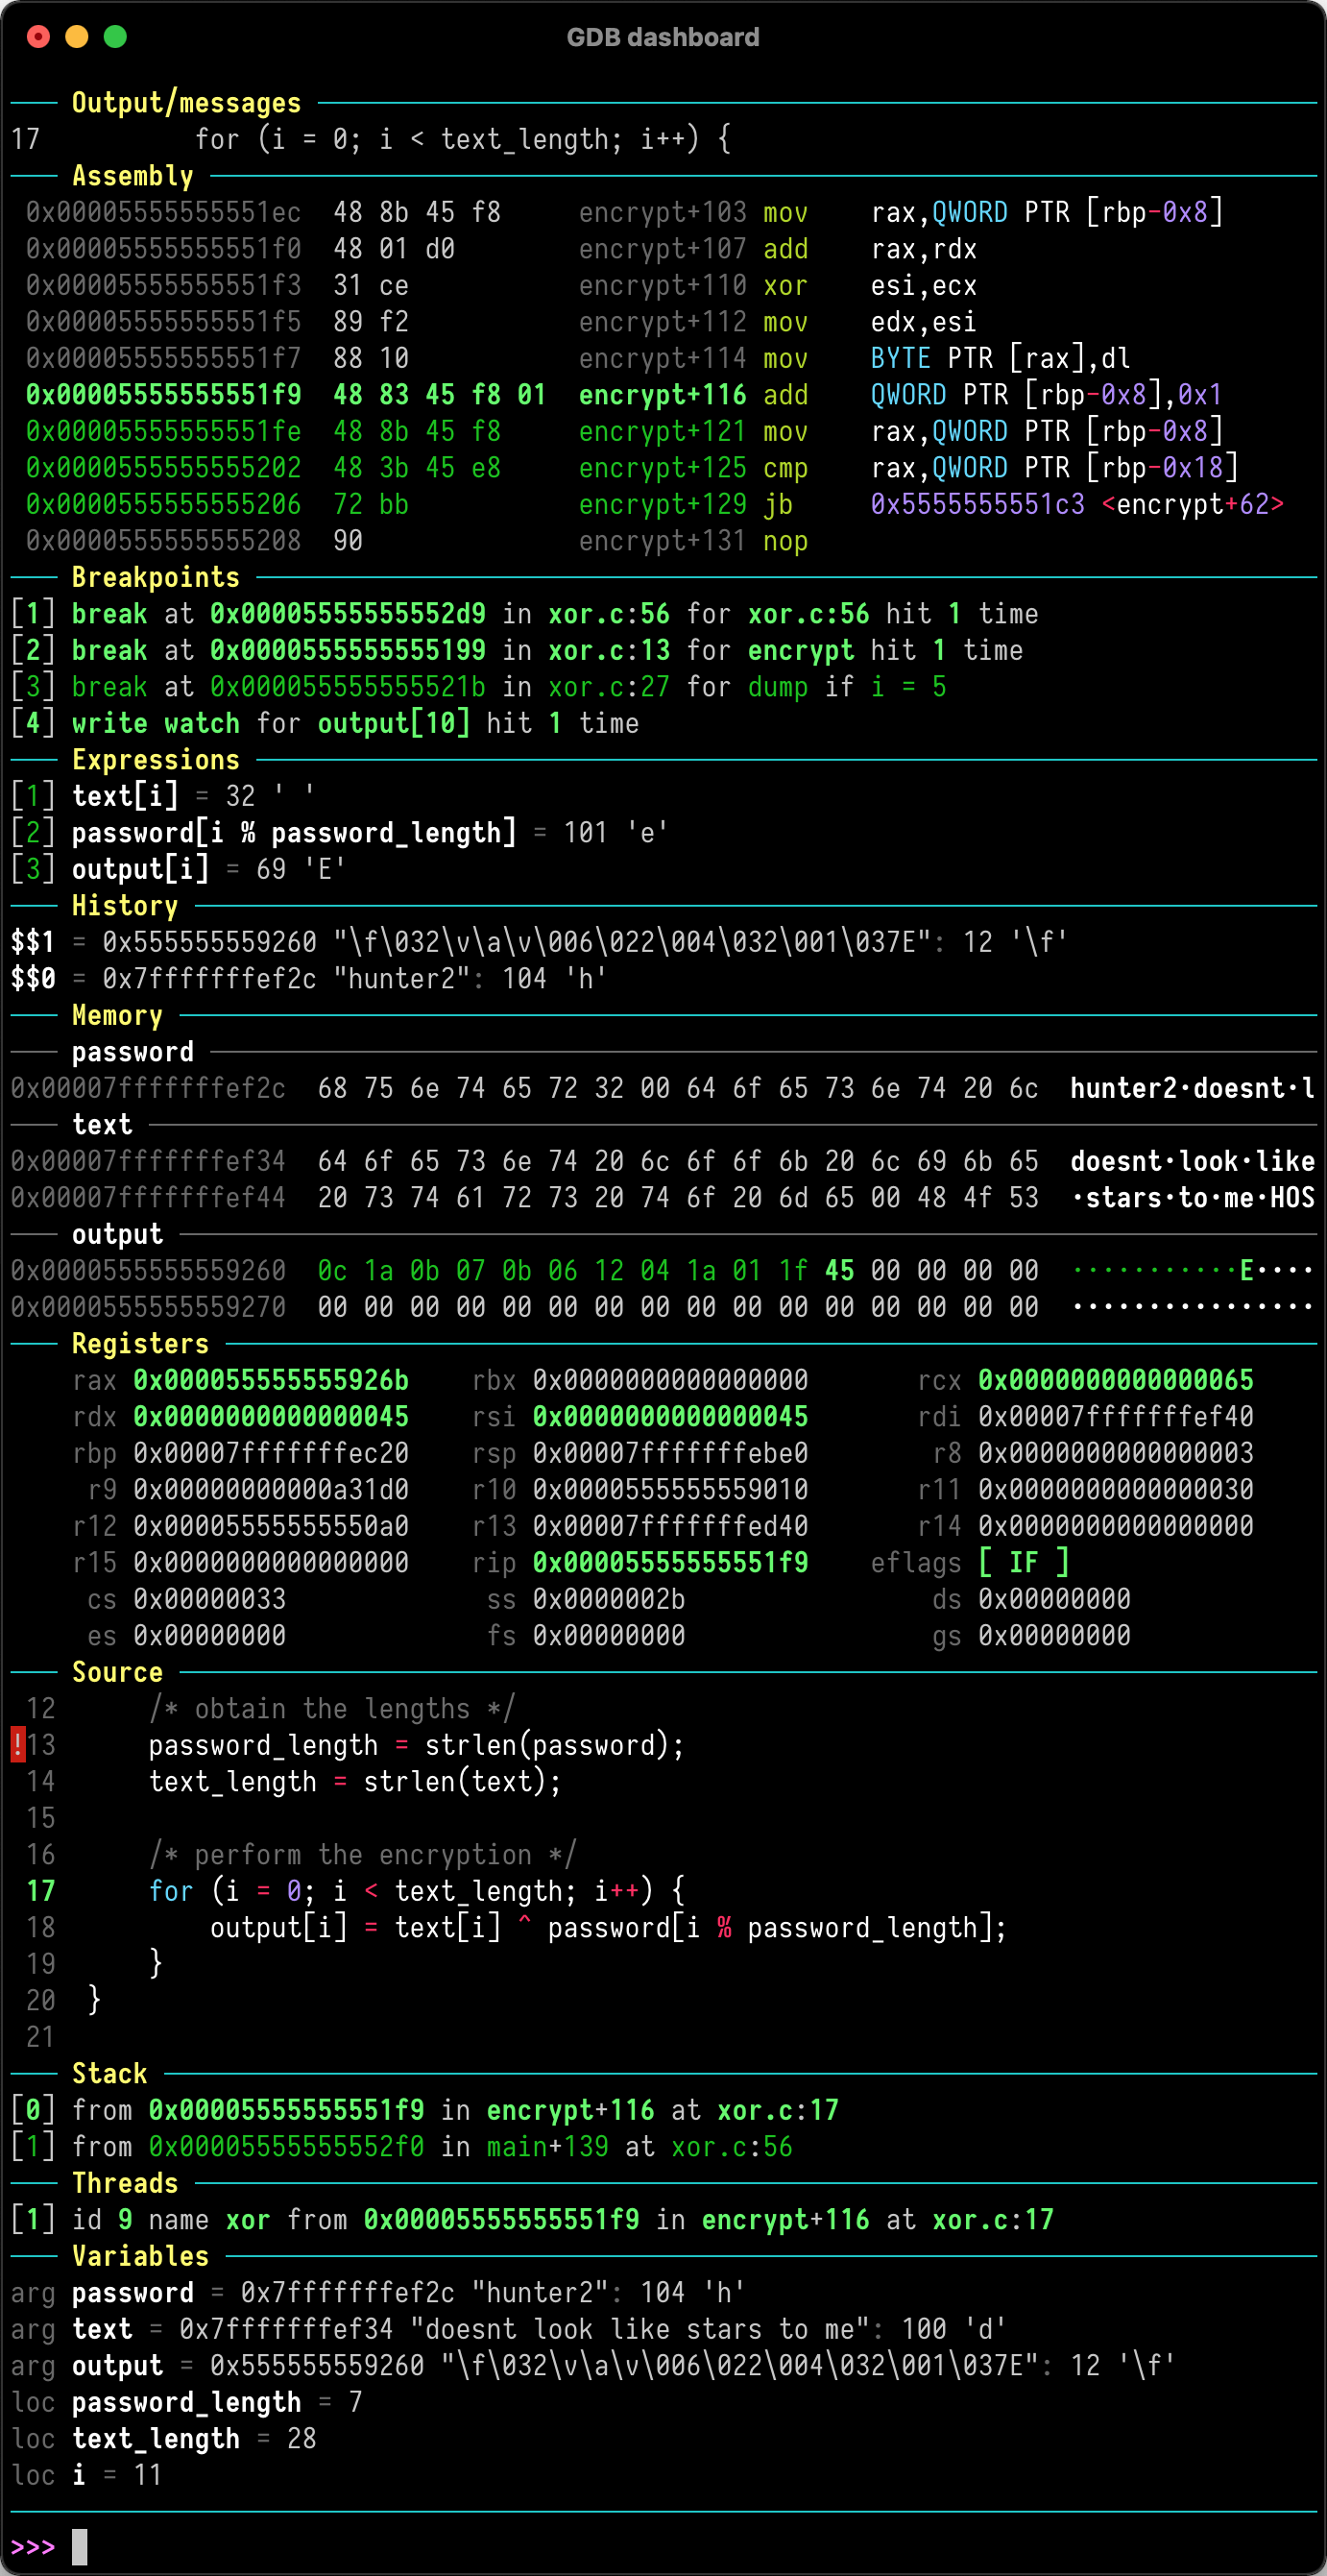 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 amossys/memitm
Tool to make in memory man in the middle
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
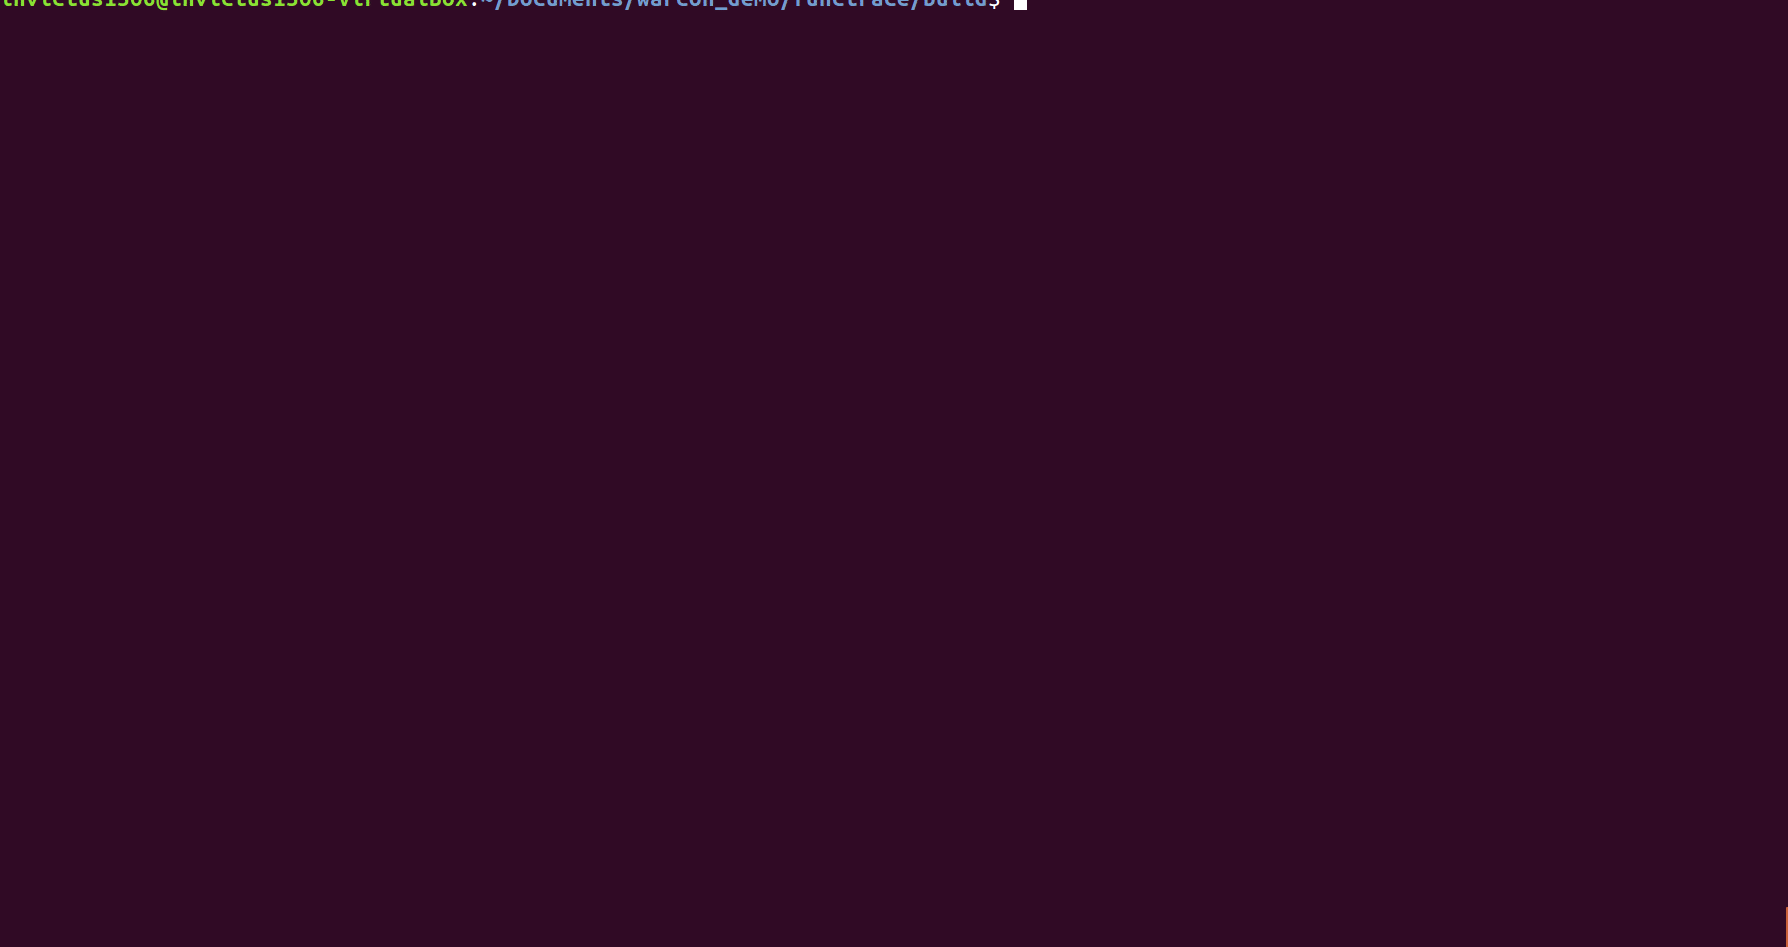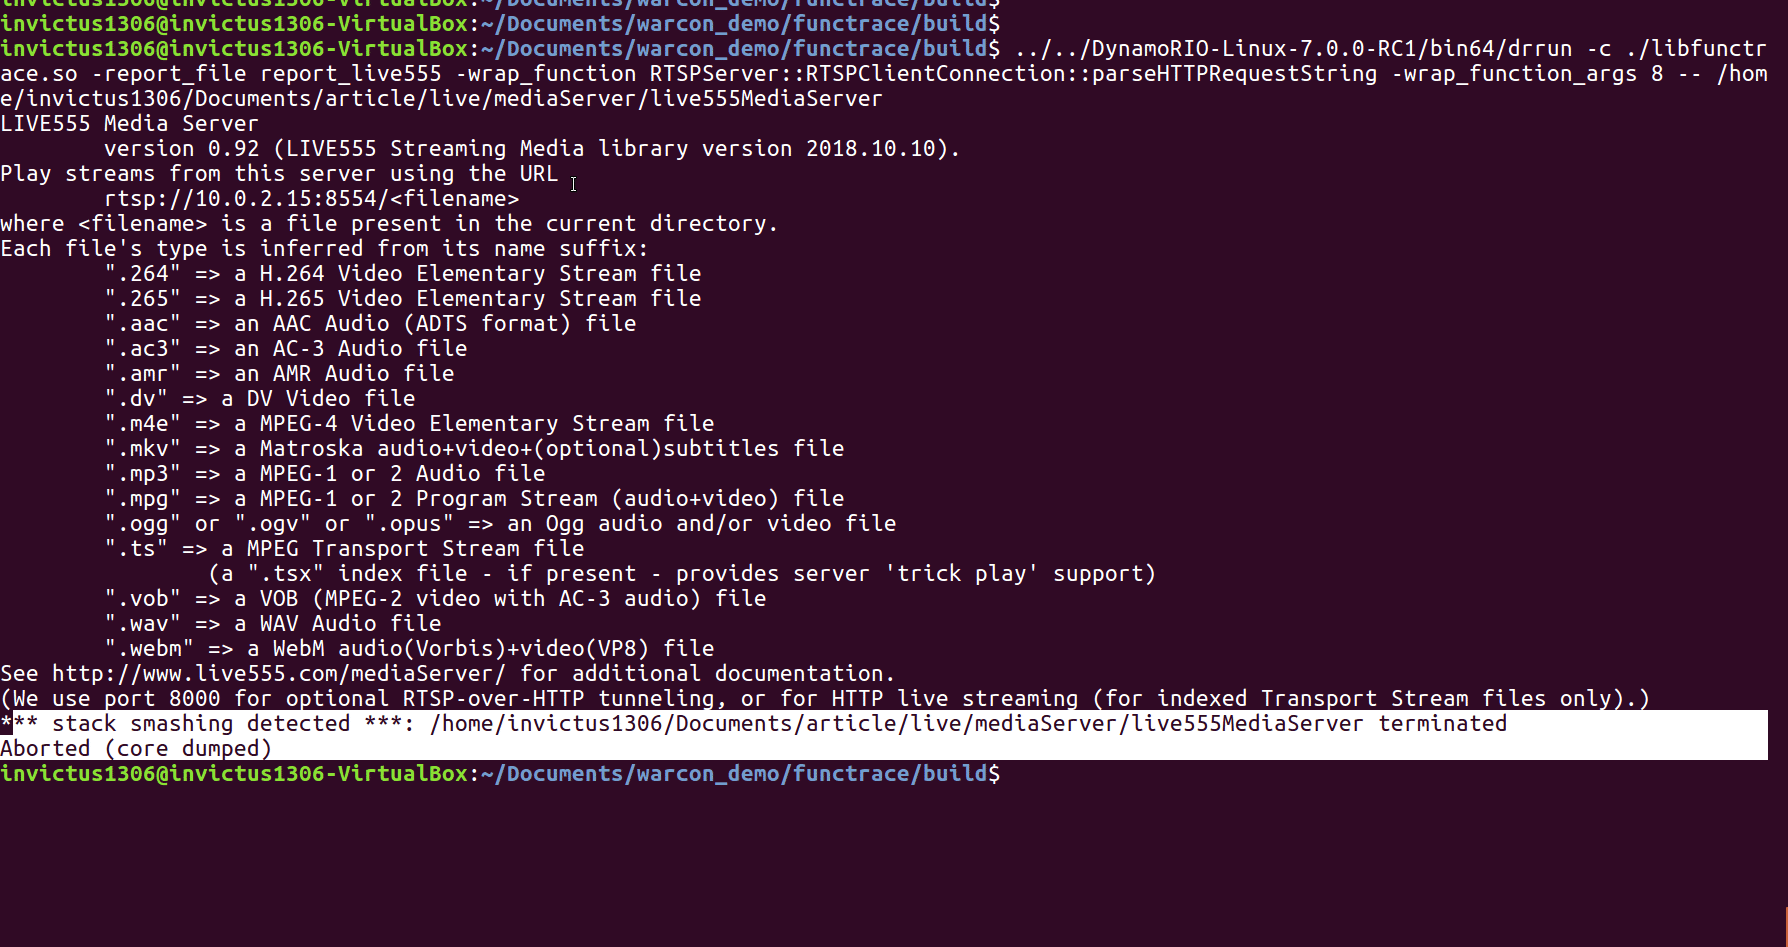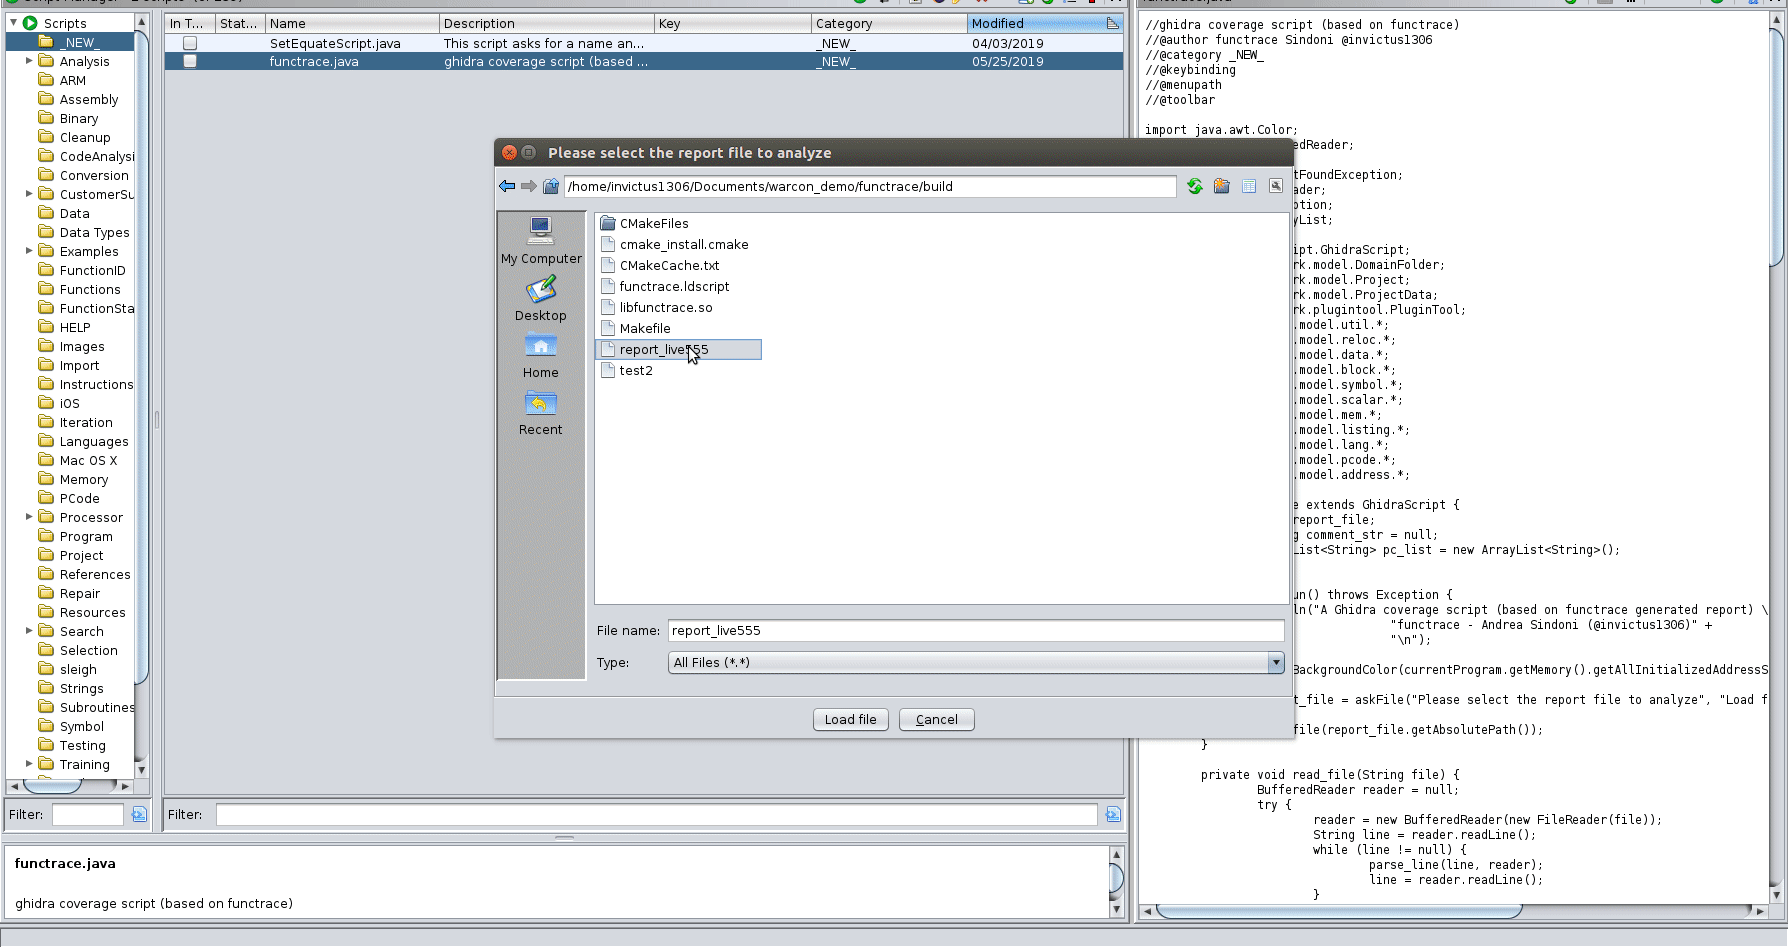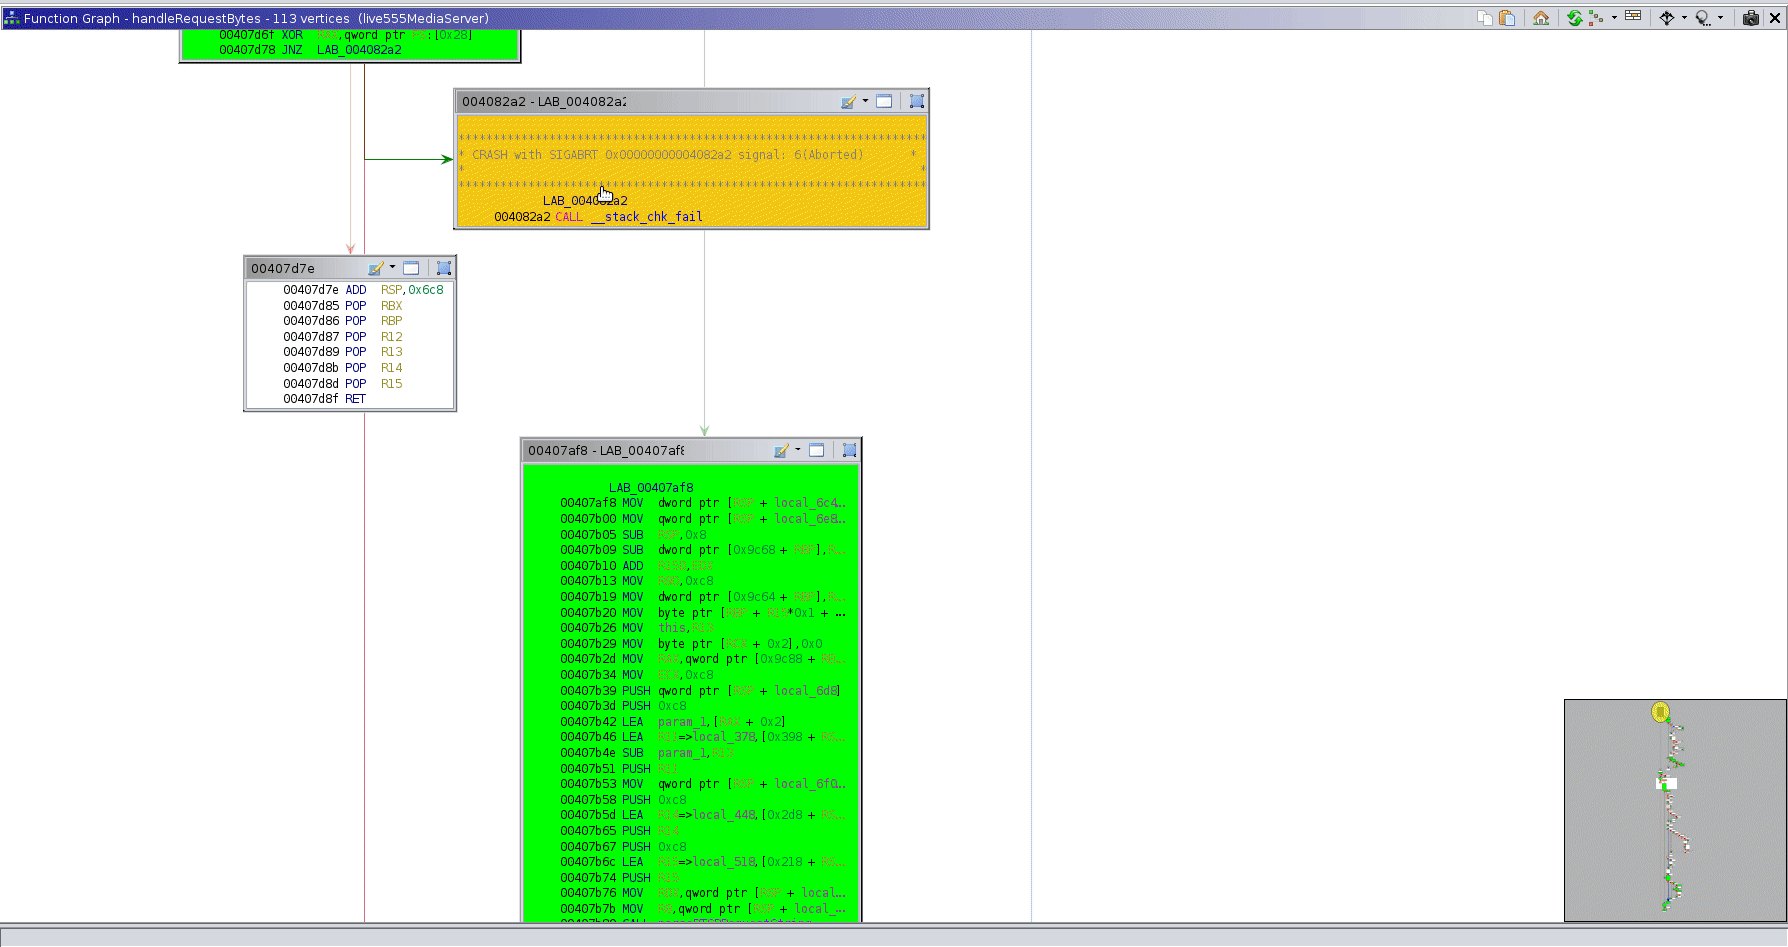 invictus1306/functrace
A function tracer
 zodiacon/alltools
All reasonably stable tools