
unthemidator
 x86rc/unthemidator
An automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool
binary-analysisbinary-exploitationdebuggers+4
391
x86rc/unthemidatorAn automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 gmh5225/hooktools
Basic injectable for analyzing the behavior of evasive malware
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
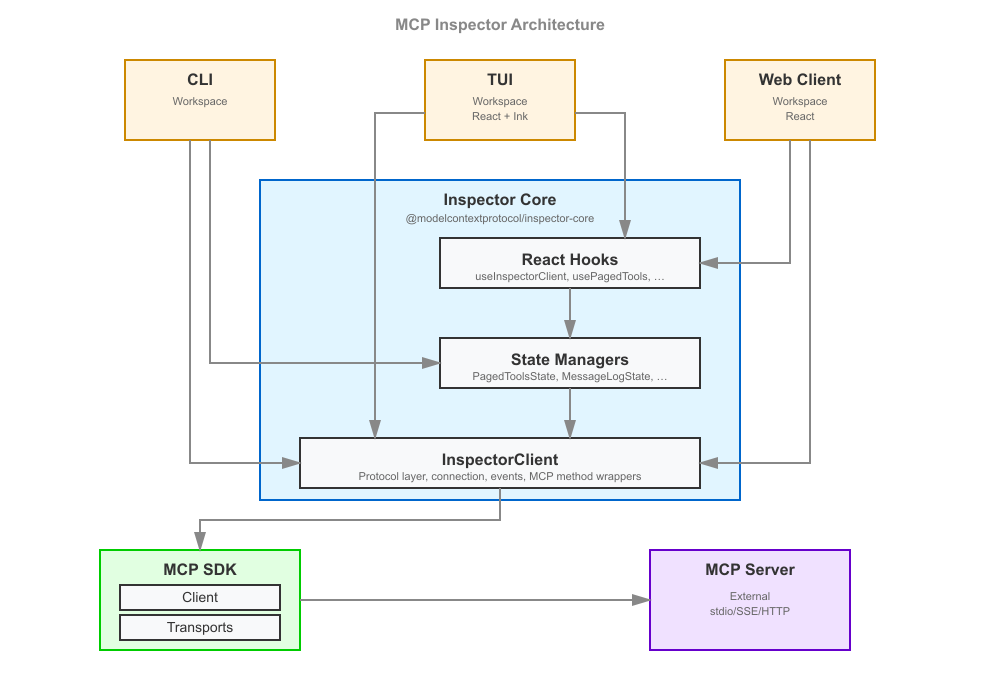 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
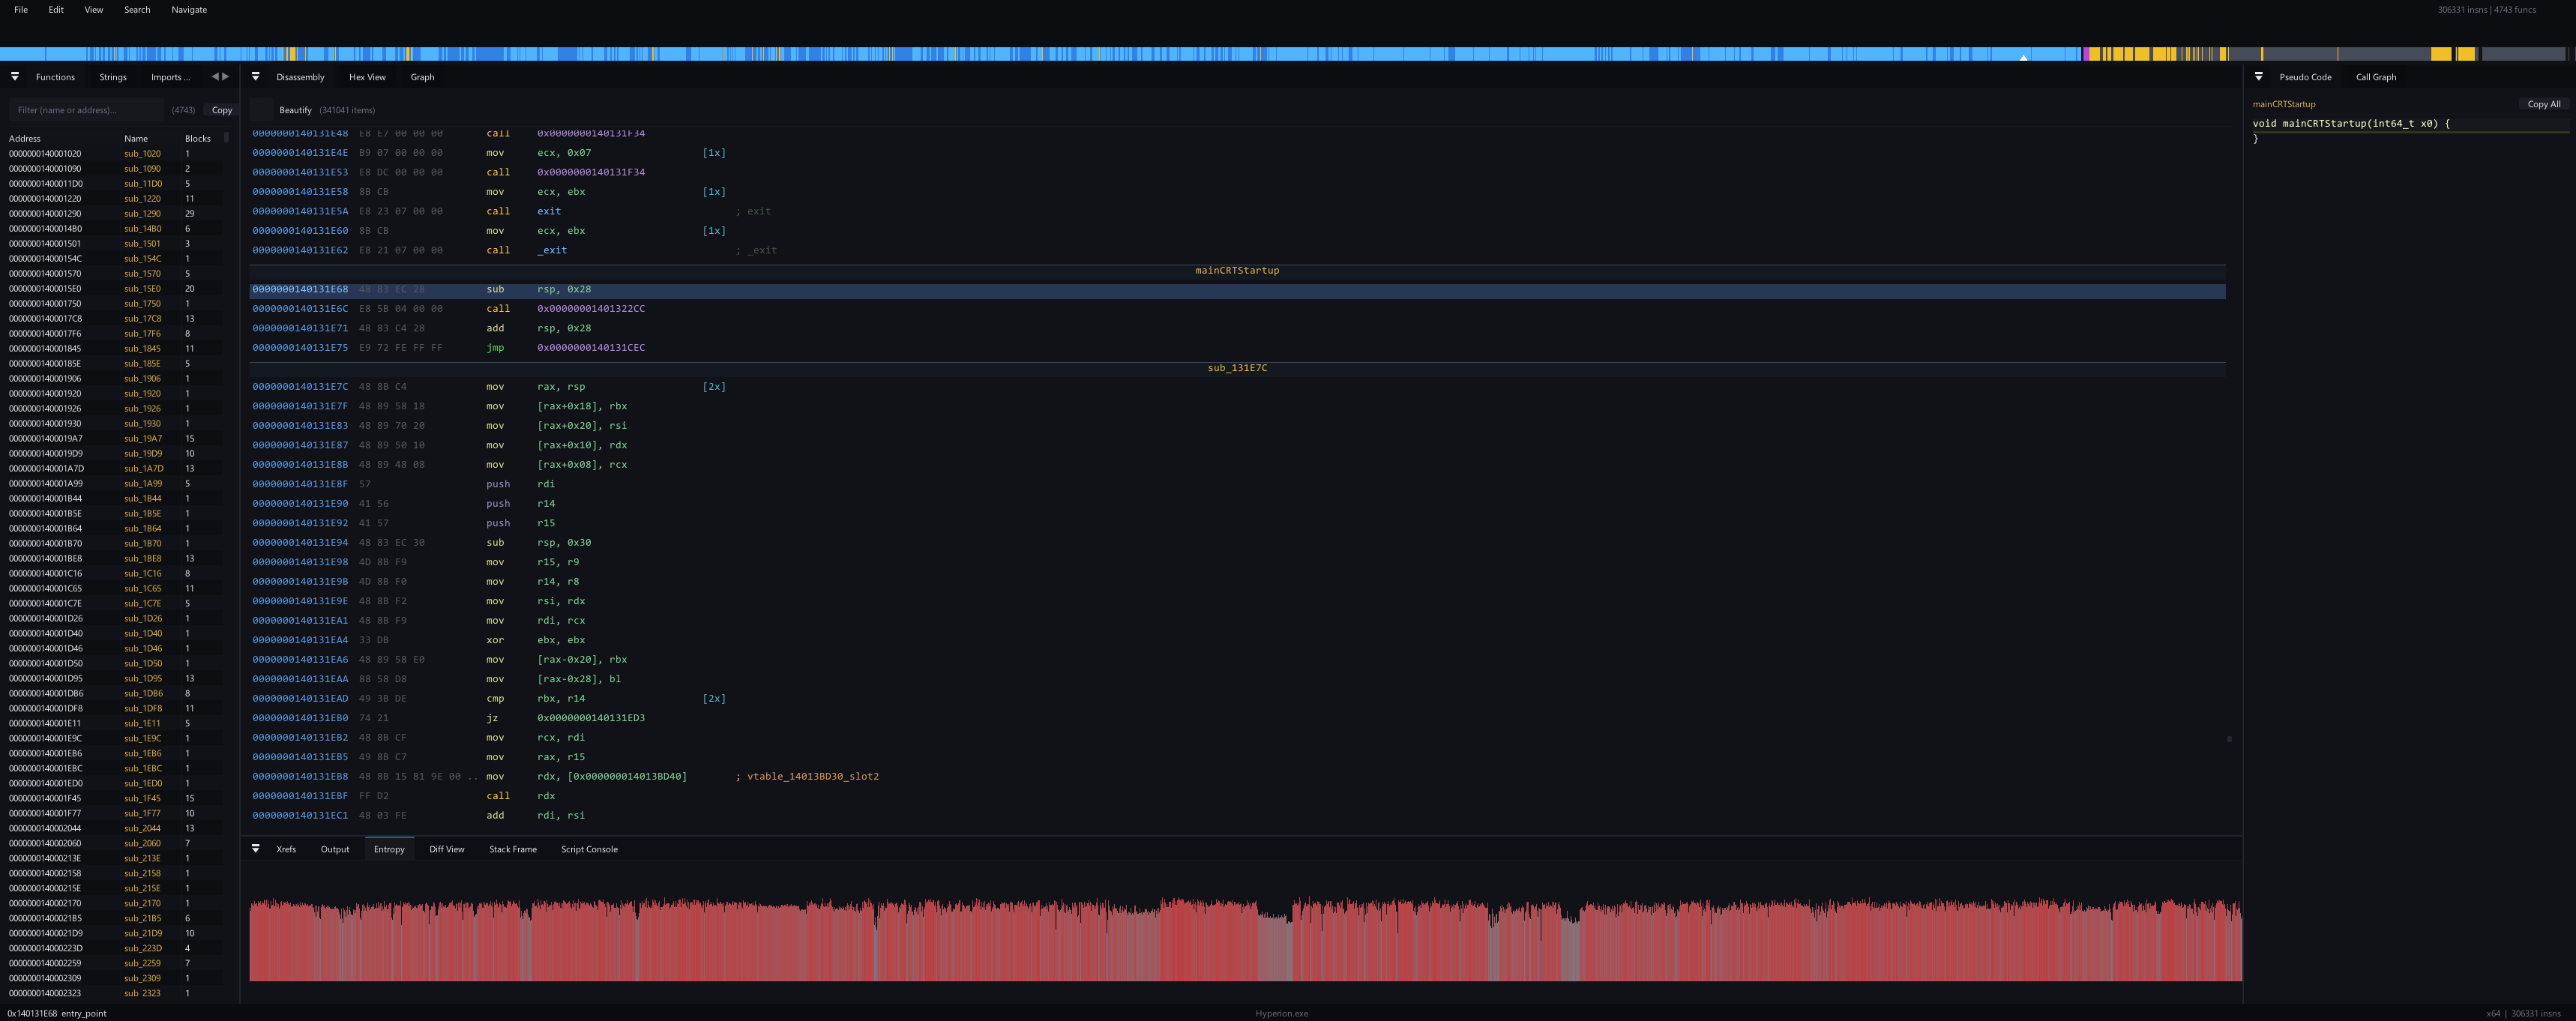 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
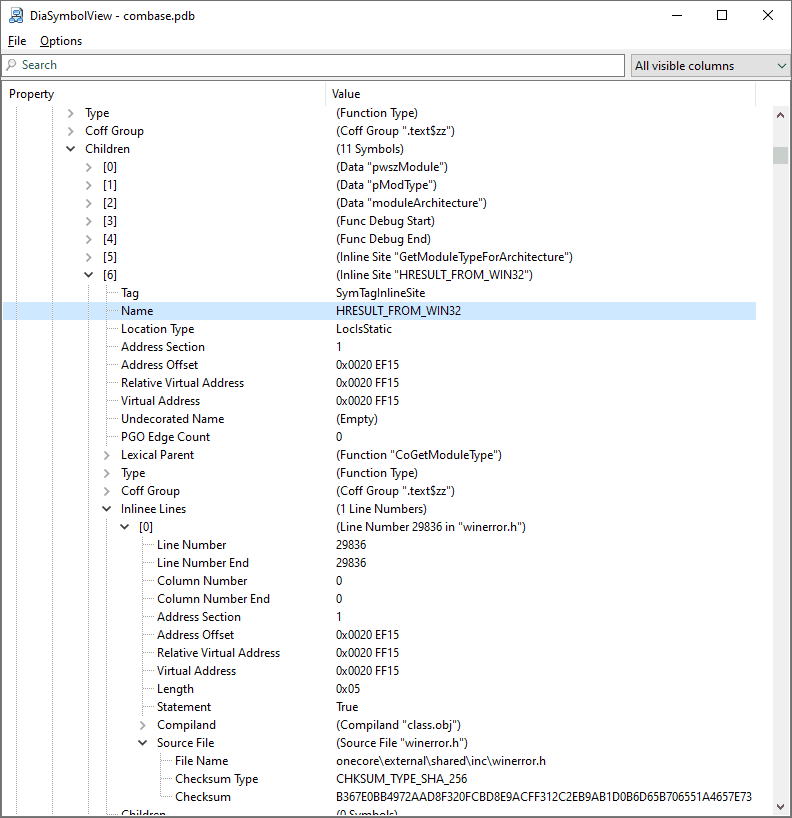 diversenok/diasymbolview
PDB file inspection tool