

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
50.8k8h 20m ago
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
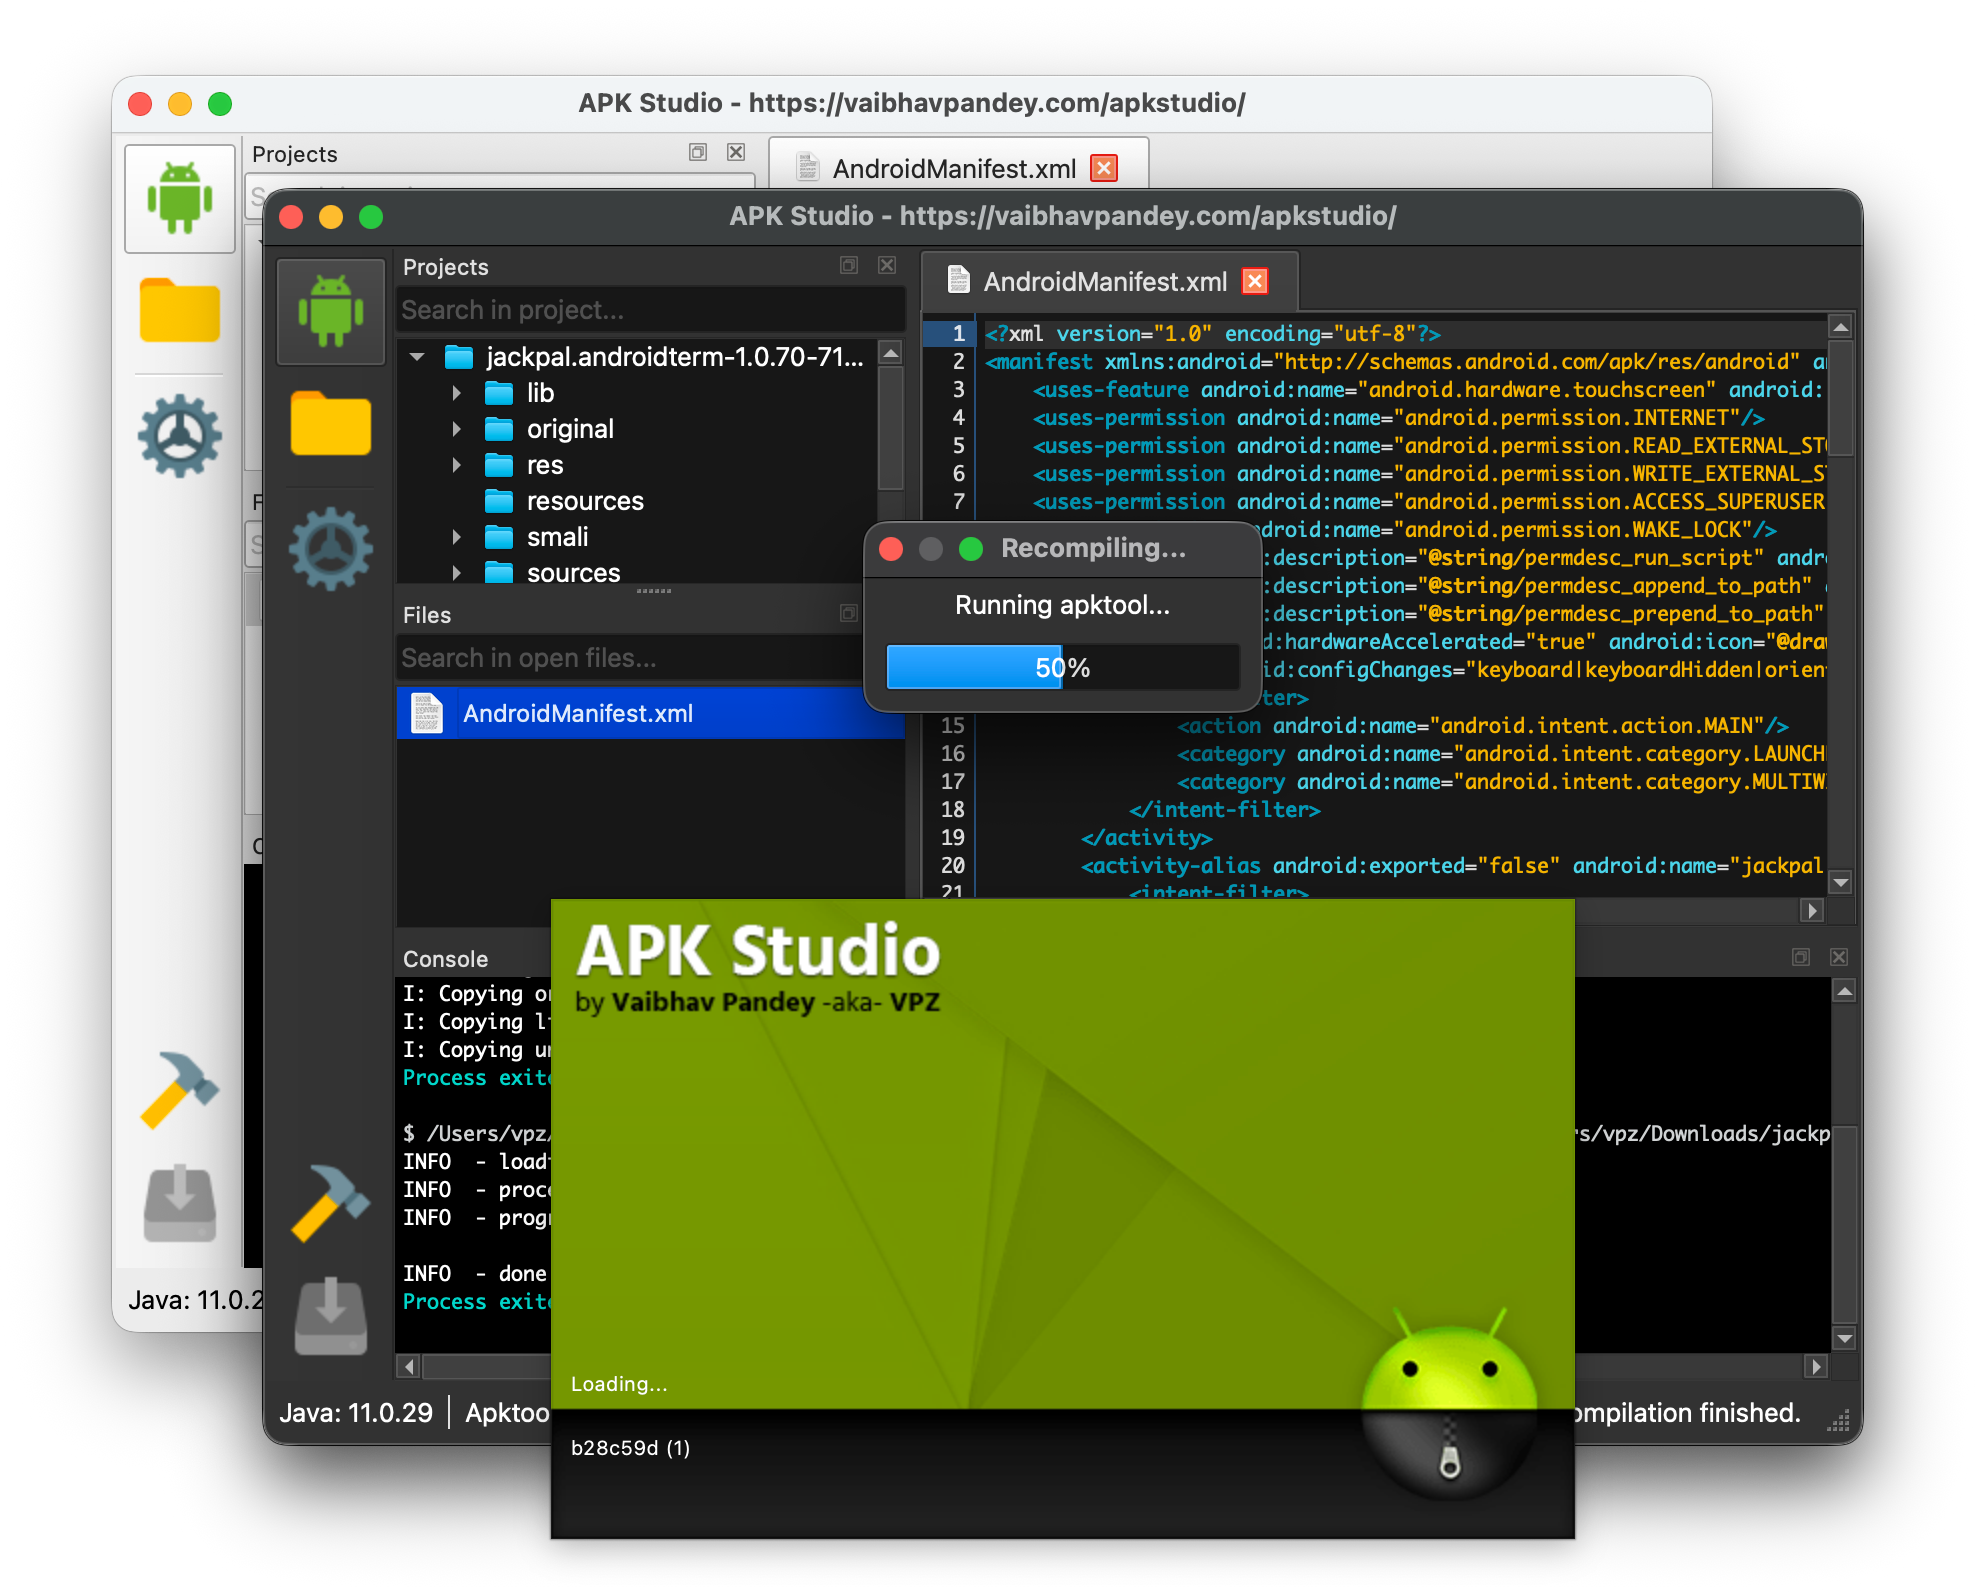 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
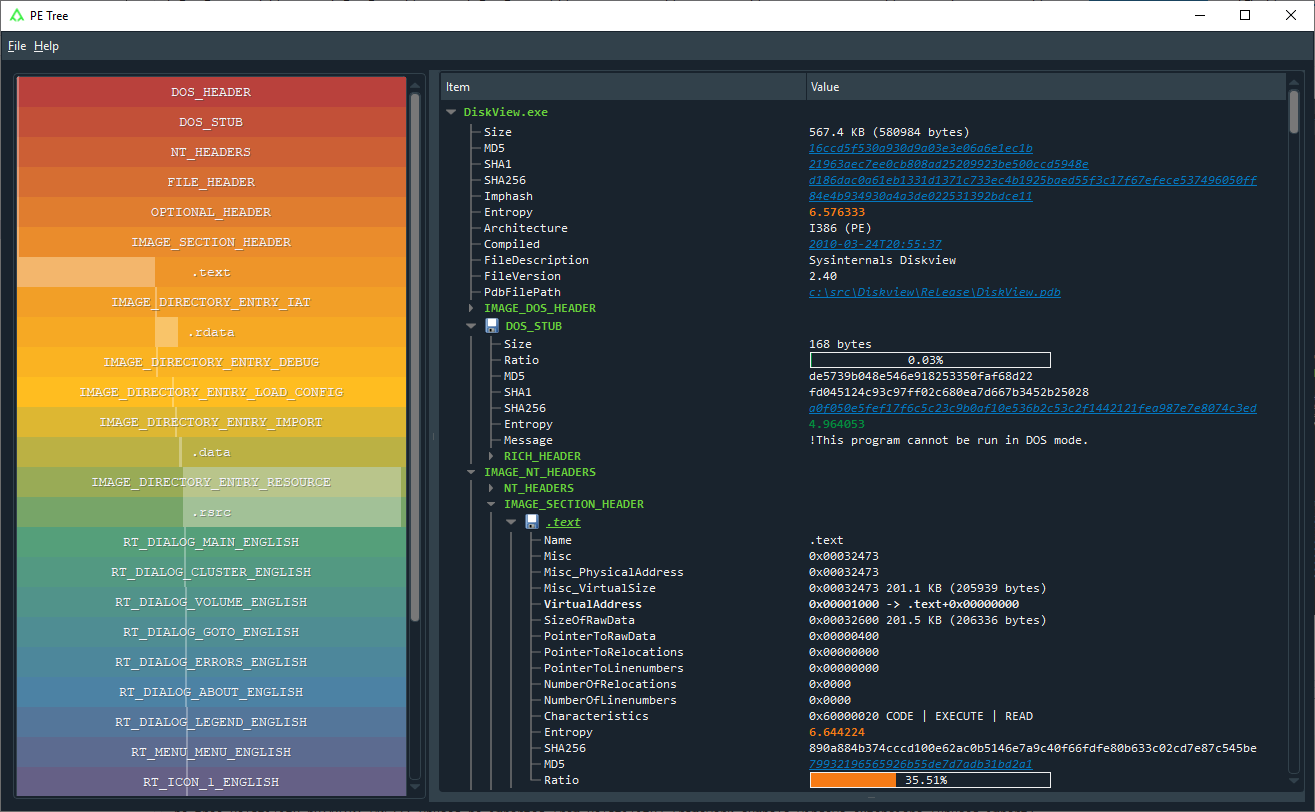 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
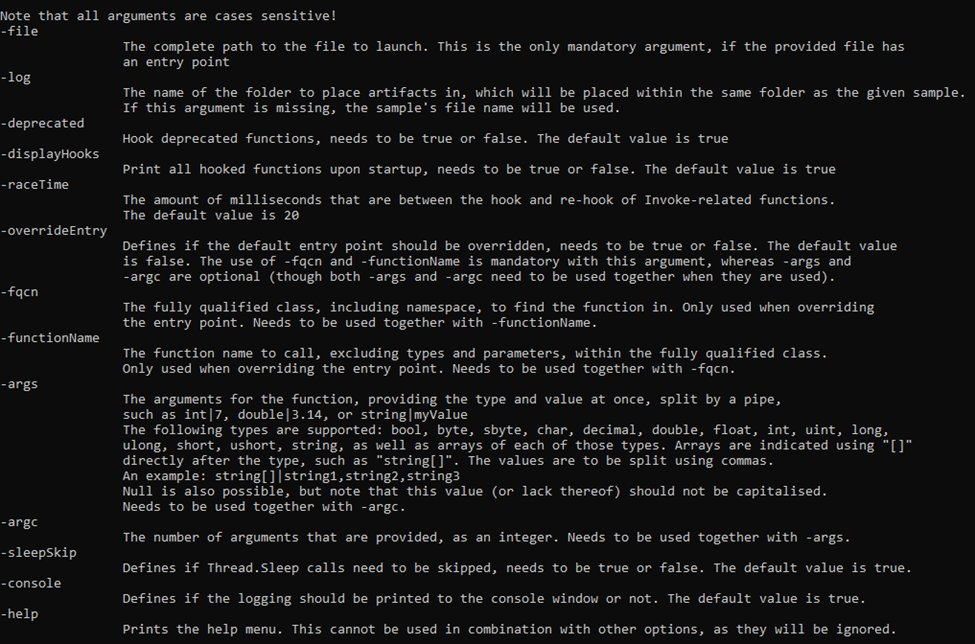 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
 irsdl/burpsuitejsbeautifier
Burp Suite JS Beautifier
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 cdacesec/cve-2022-31901
Proof-of-concept exploit demonstrating a denial-of-service vulnerability in Notepad++ (x86) versions up to 8.4.9, triggered by opening specially…
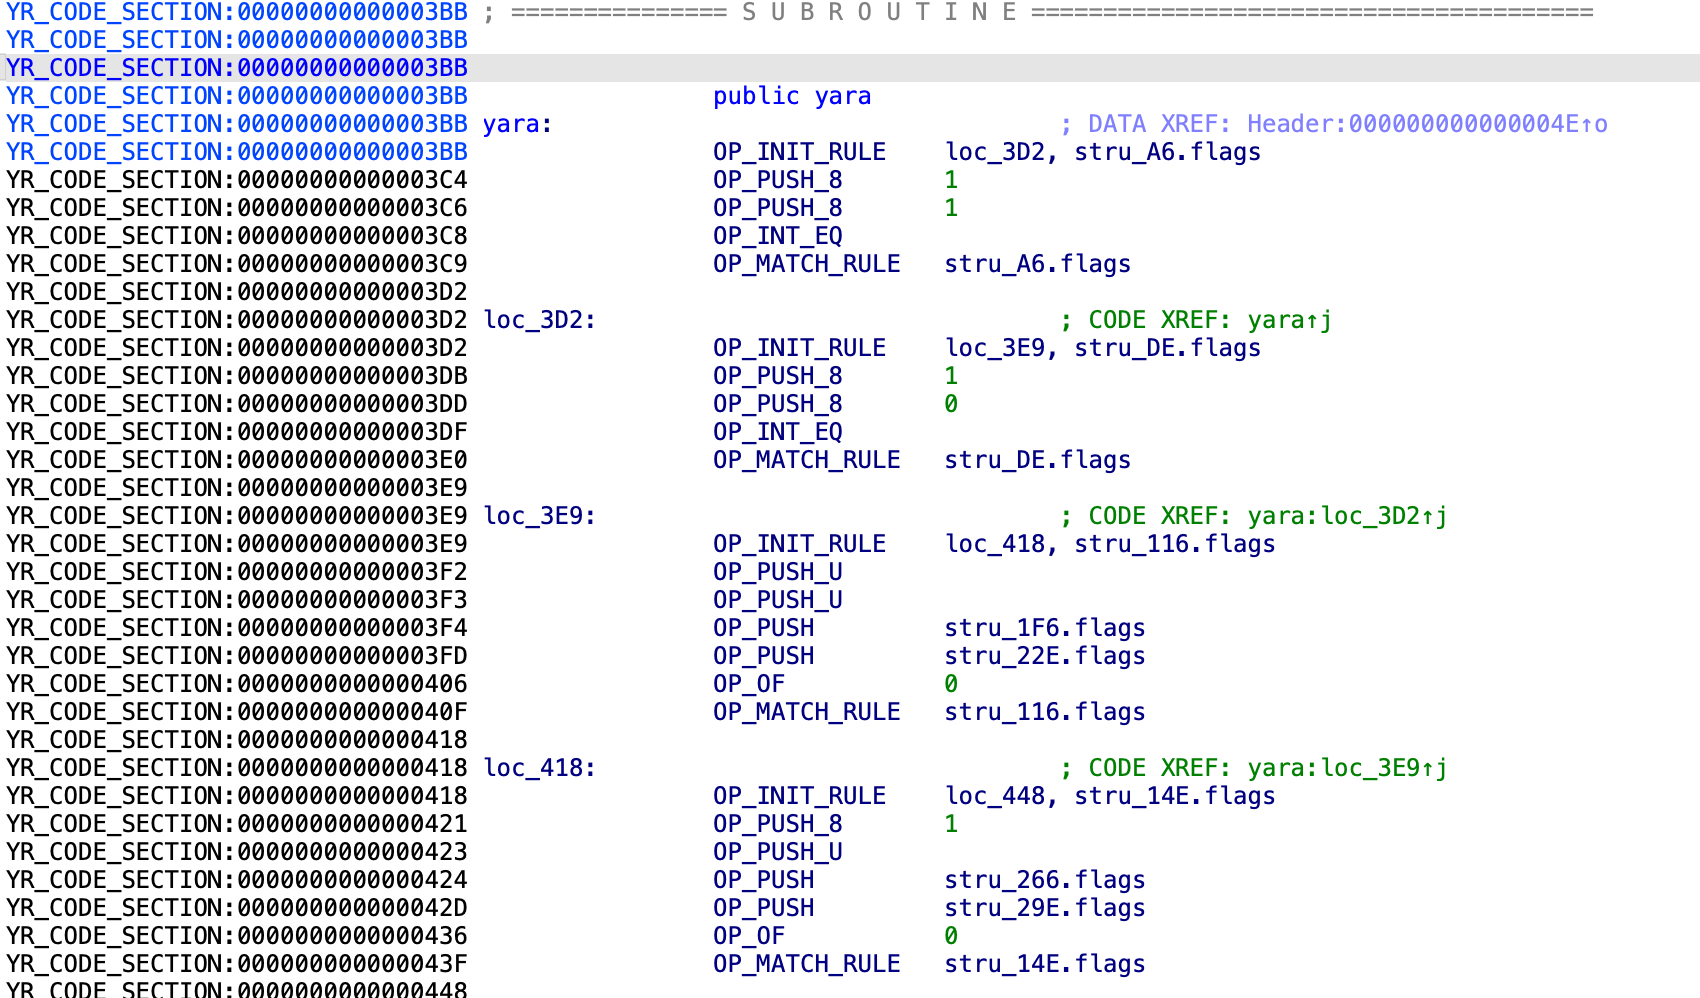 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
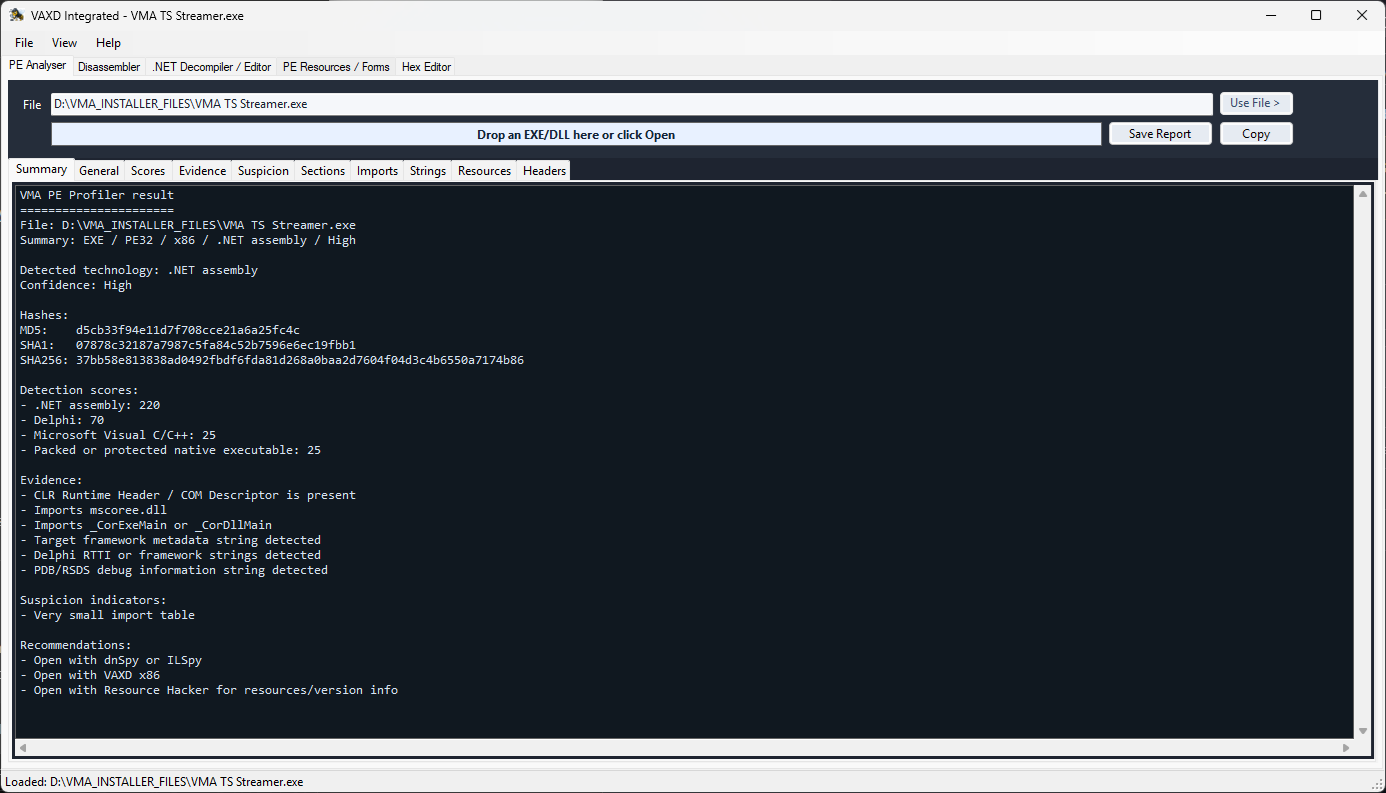 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.