CVE-2026-21004-SQLite-FTS3-Match-Infoleak-via-Query-Crafting

Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…

Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing

Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…

Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…

Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…

Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…

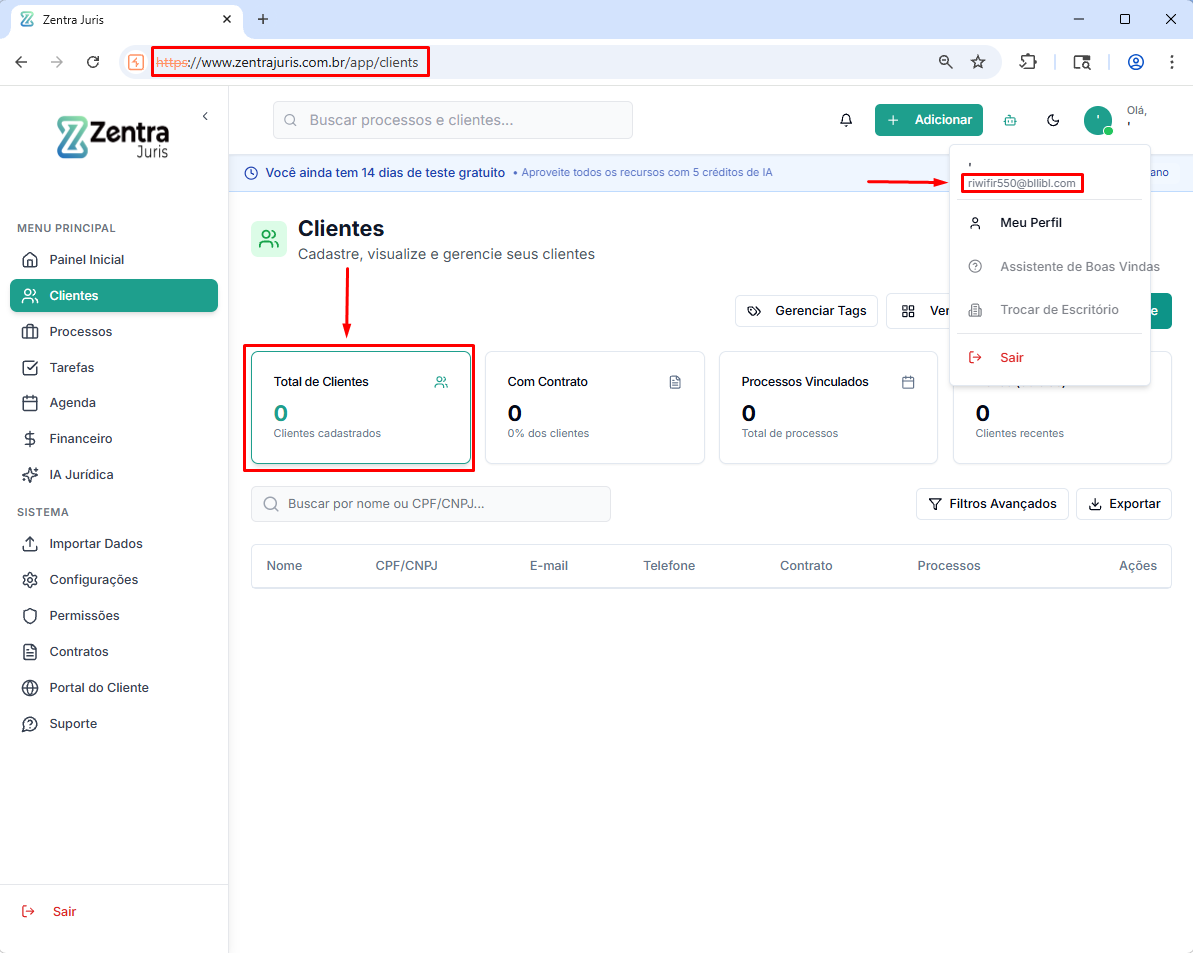
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…

Tool designed to help identify open Elasticsearch servers that are exposing sensitive information

Python tool for exploiting CVE-2021-35616

WordPress WP-Advanced-Search <= 3.3.9 - Unauthenticated SQL Injection

SQL Injection vulnerability discovered in Grocery Store Management System 1.0