atproto
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
api-securityauthenticationcloud-infrastructure-security+6
94
blacksky-algorithms/atprotoFork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 sadshade/cve-2022-24706-couchdb-exploit
Apache CouchDB 3.2.1 - Remote Code Execution (RCE)
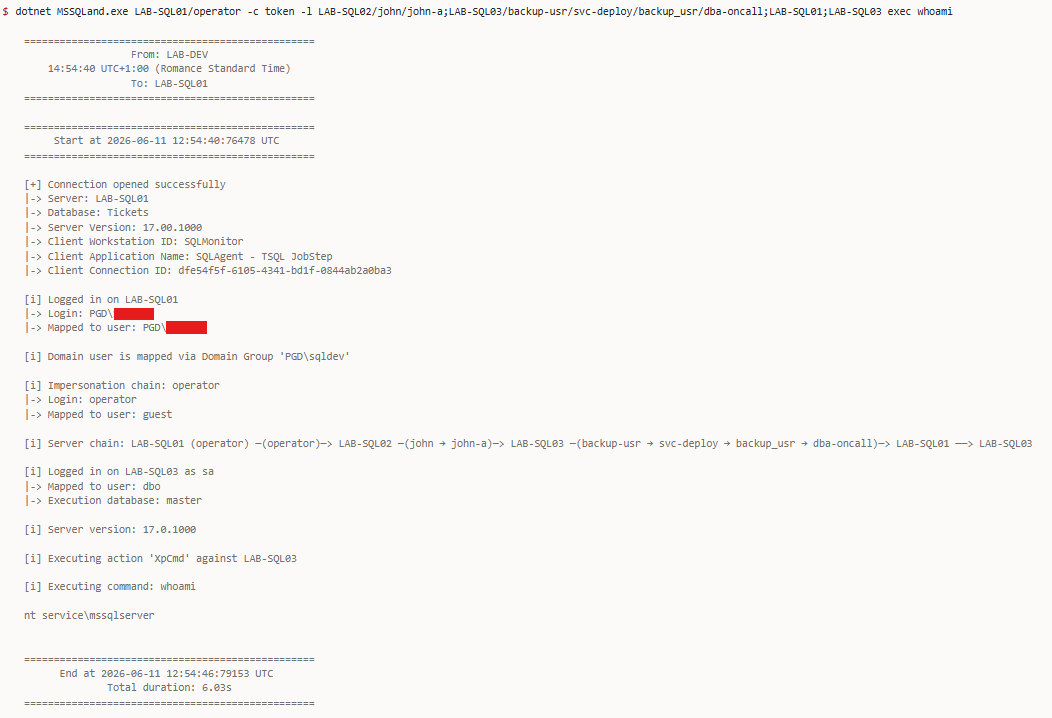 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
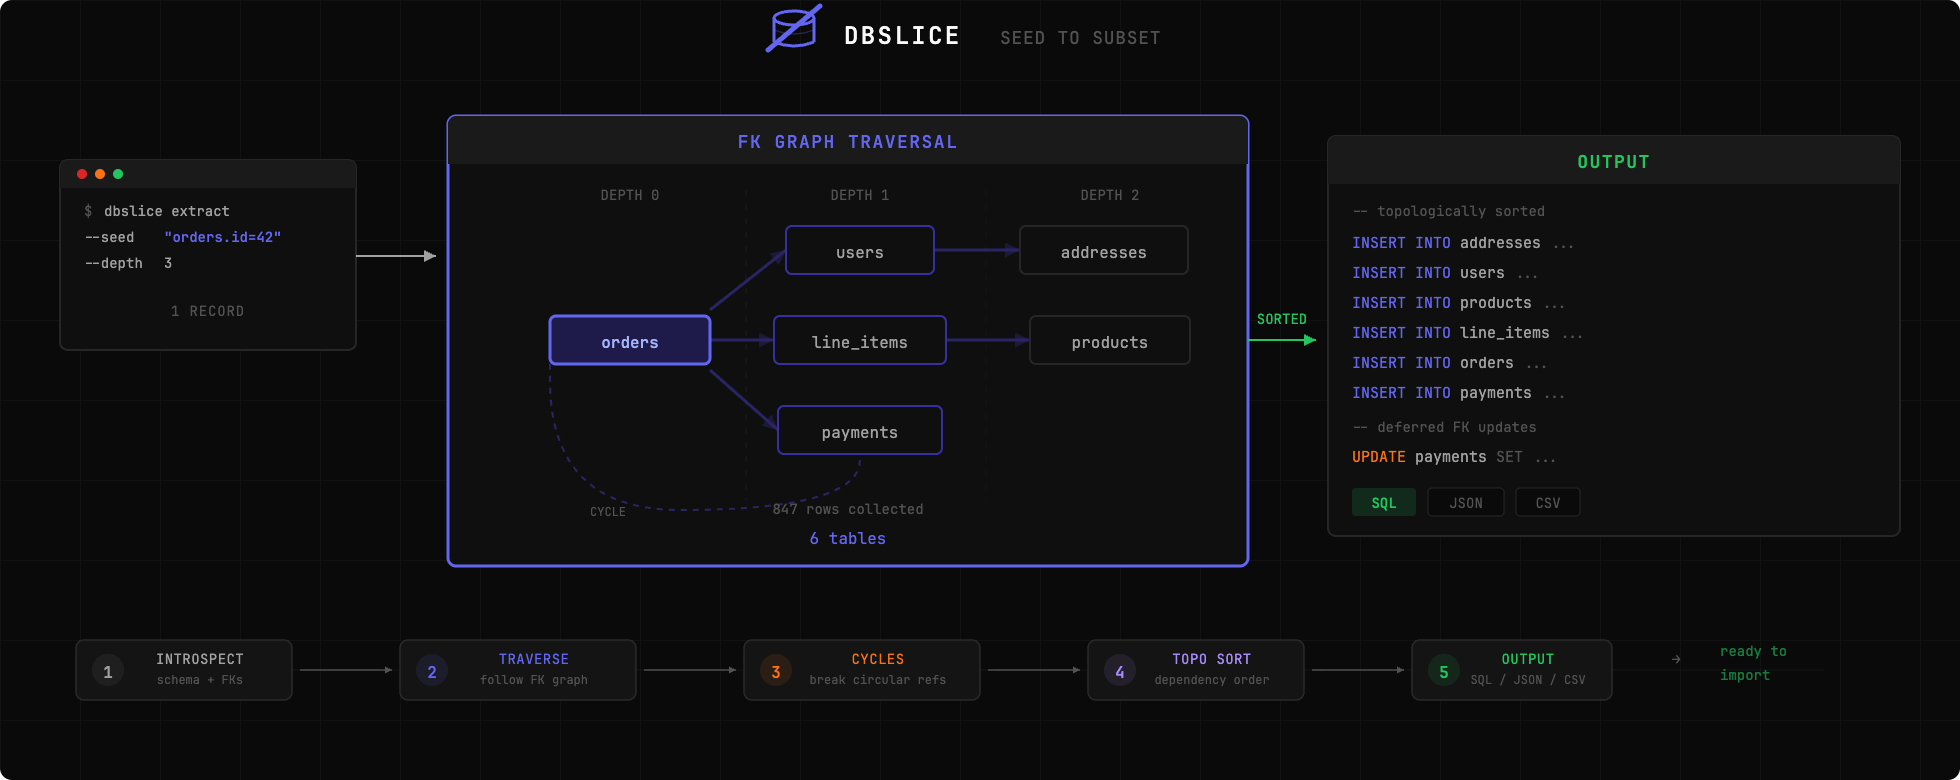 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 geraldoalcantara/cve-2023-49988
Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "npss" parameter at rooms.php
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
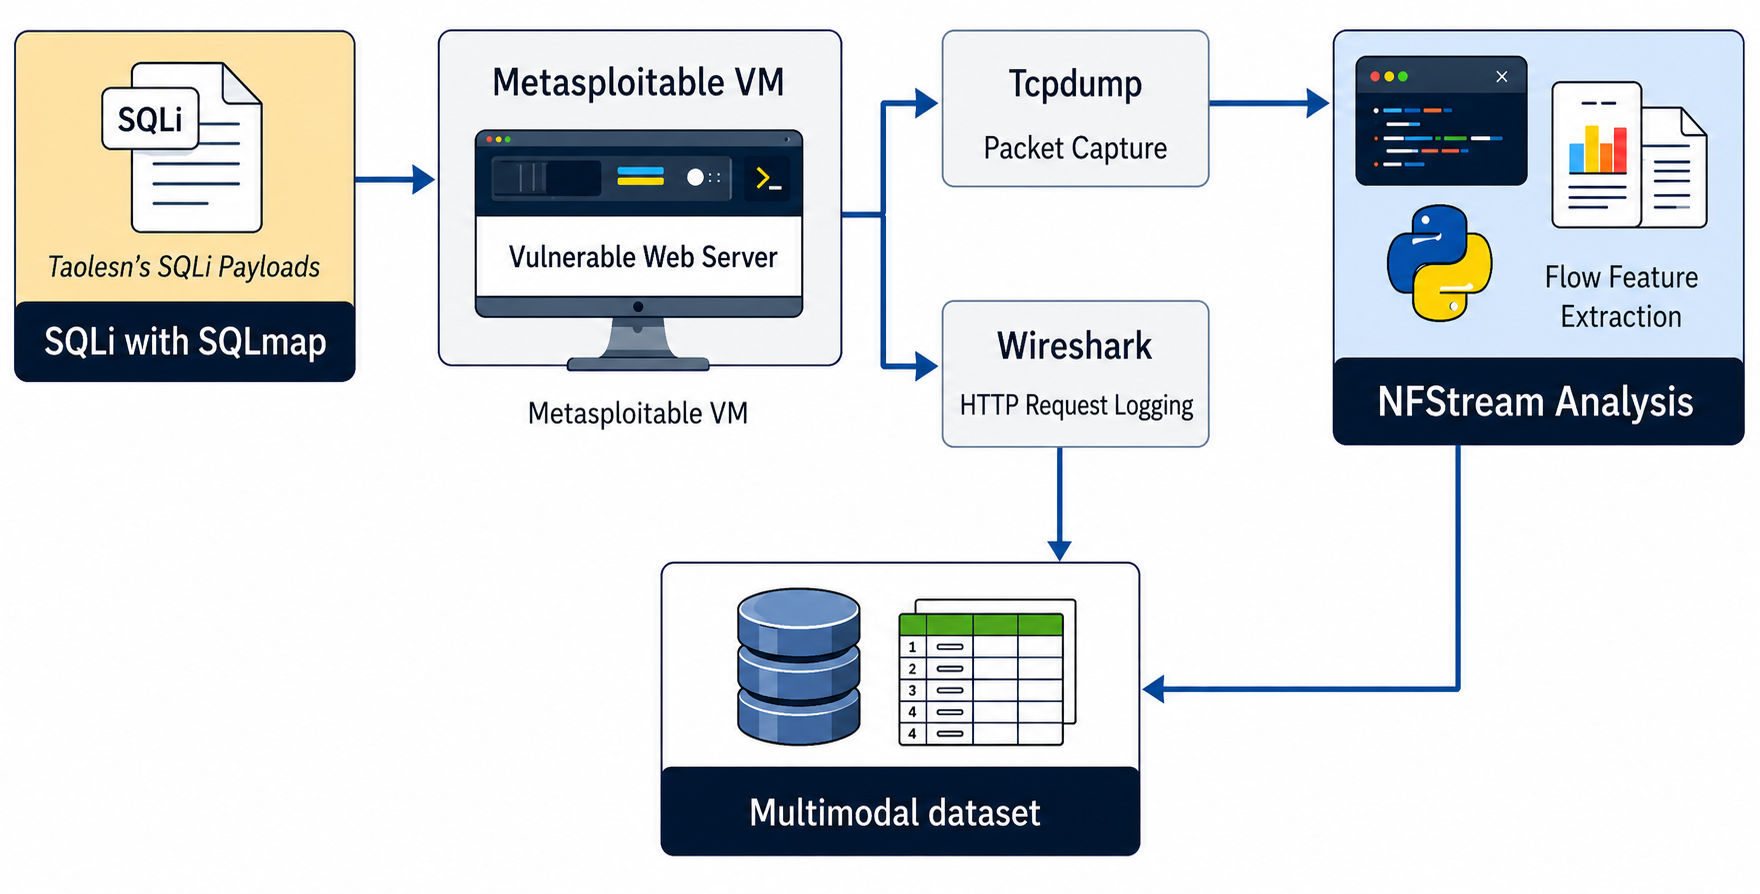 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.
 xenom0rph97/cve-2024-30896
Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…
 kara-git/cve-2026-49048-joomcck-sqli
CVE-2026-49048 — JoomCCK 6.4.0 Unauthenticated SQL Injection (CVSS 9.8)
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 sshipanoo/cve-2024-44542
Documentation of a SQL injection vulnerability in Todesk v1.1 via the title parameter, enabling remote information disclosure through crafted URL…