

checkov
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
cloud-infrastructure-securitycloud-securitycode-analysis+12
9.1k
bridgecrewio/checkovStatic analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 synacktiv/bissap
A new open-source tool to quickly audit SAP permissions.
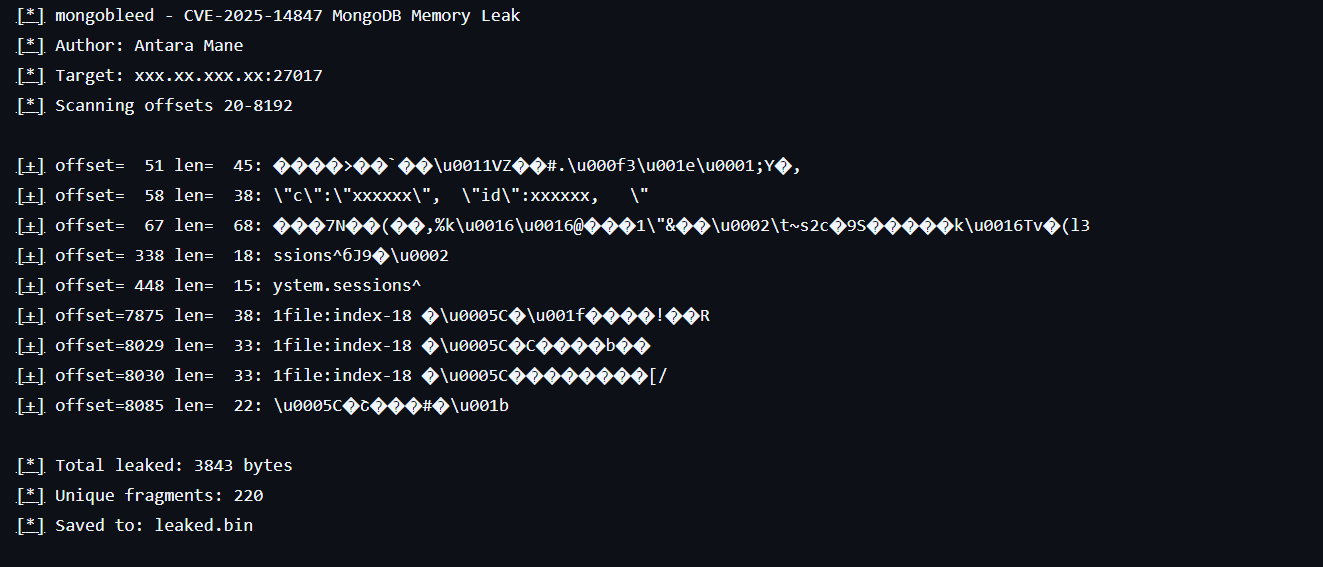 infosecantara/cve-2025-14847-mongodb
Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…
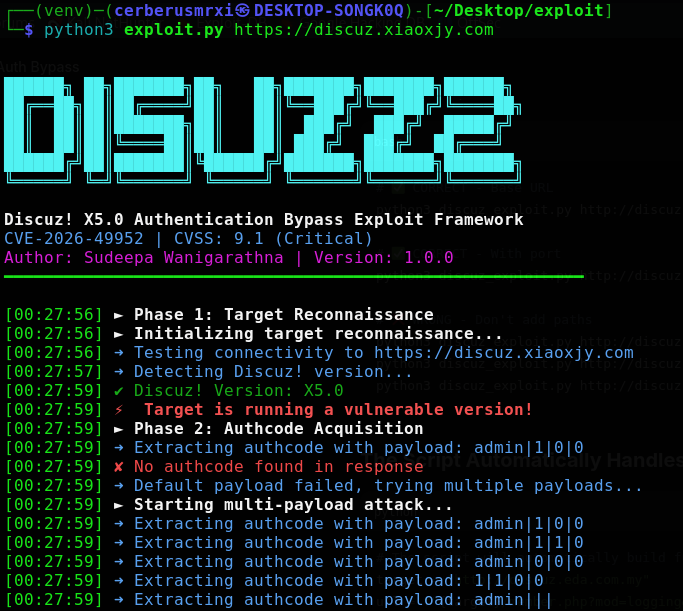 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
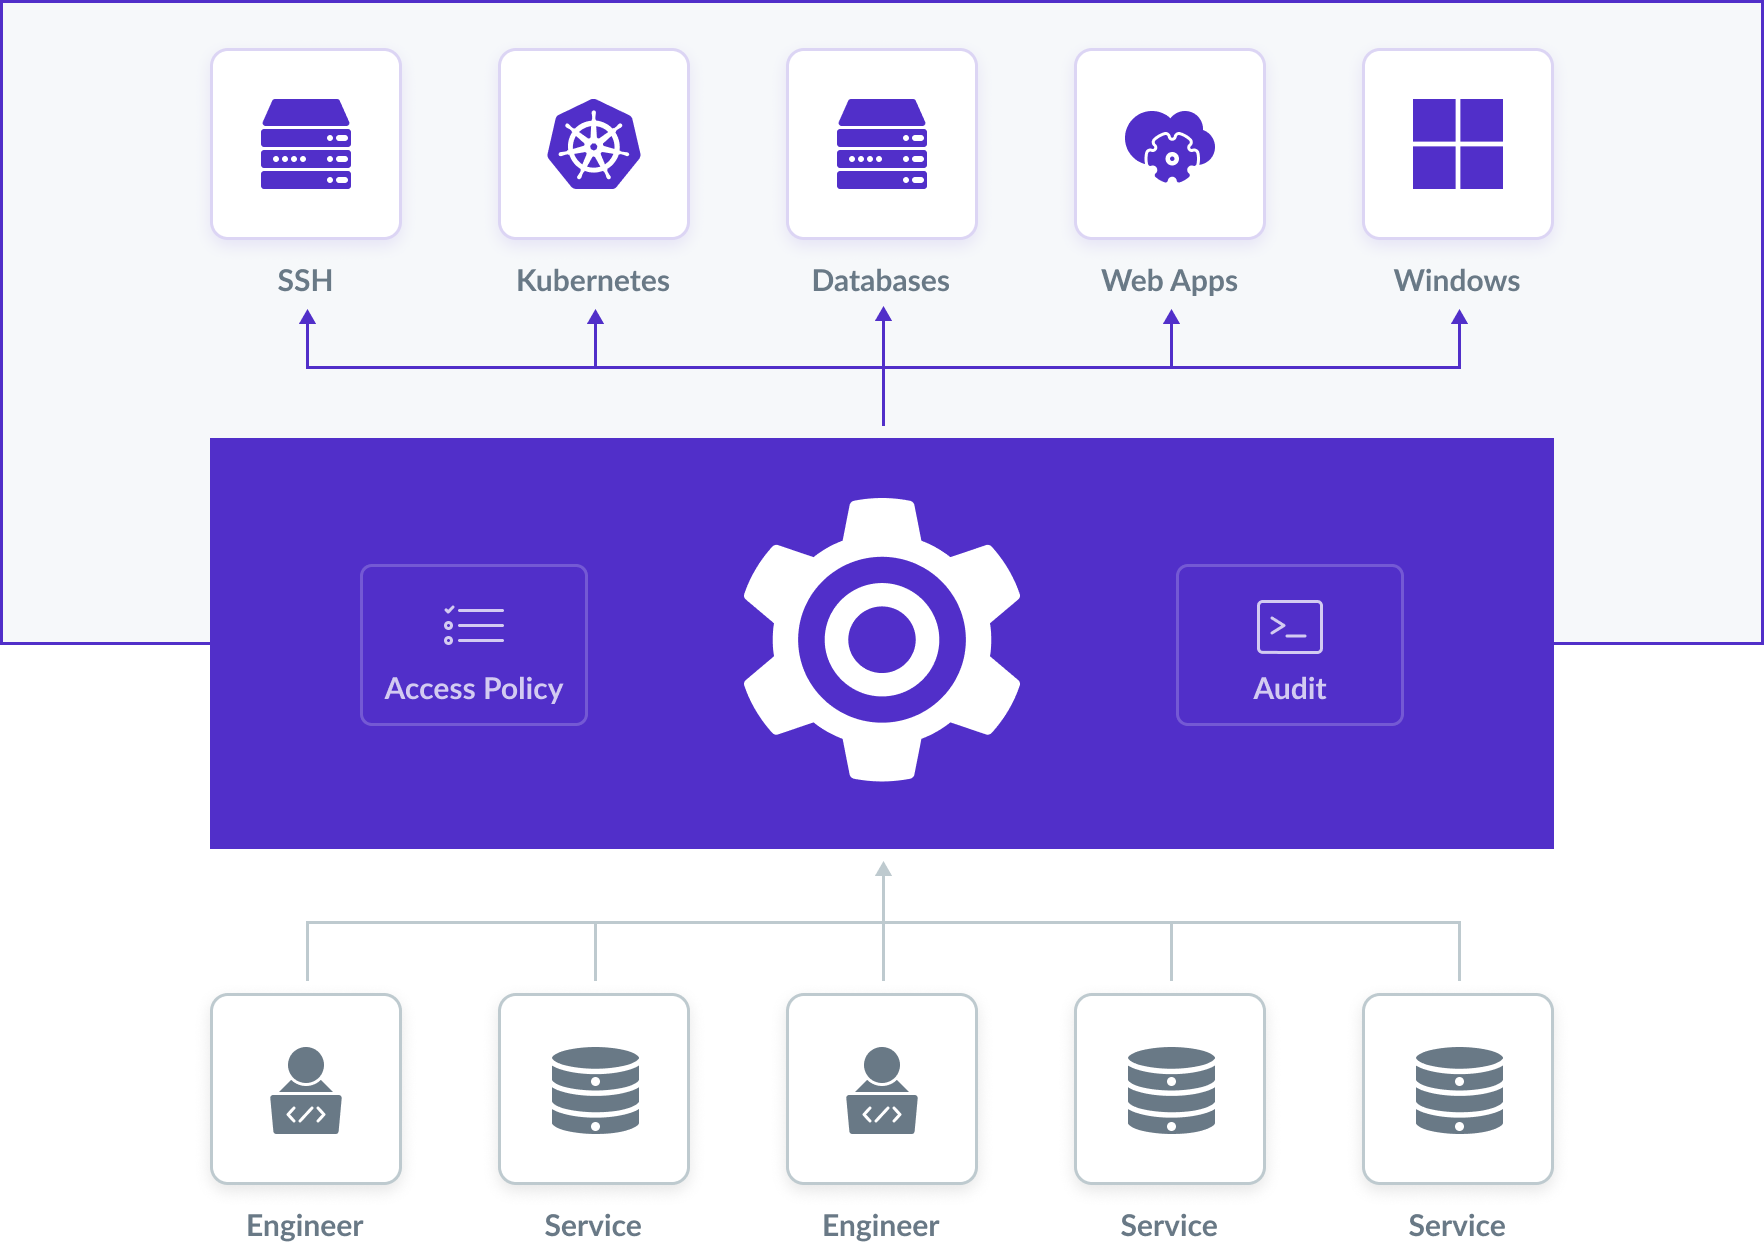 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 jas502n/sscms_decrypt
sscms database decrypt
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0