
CVE-2024-34226
 dovankha/cve-2024-34226
Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution.
database-securityexploitationpenetration-testing+2
dovankha/cve-2024-34226Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution.
 xmyronn/cve-2026-7229-sqli
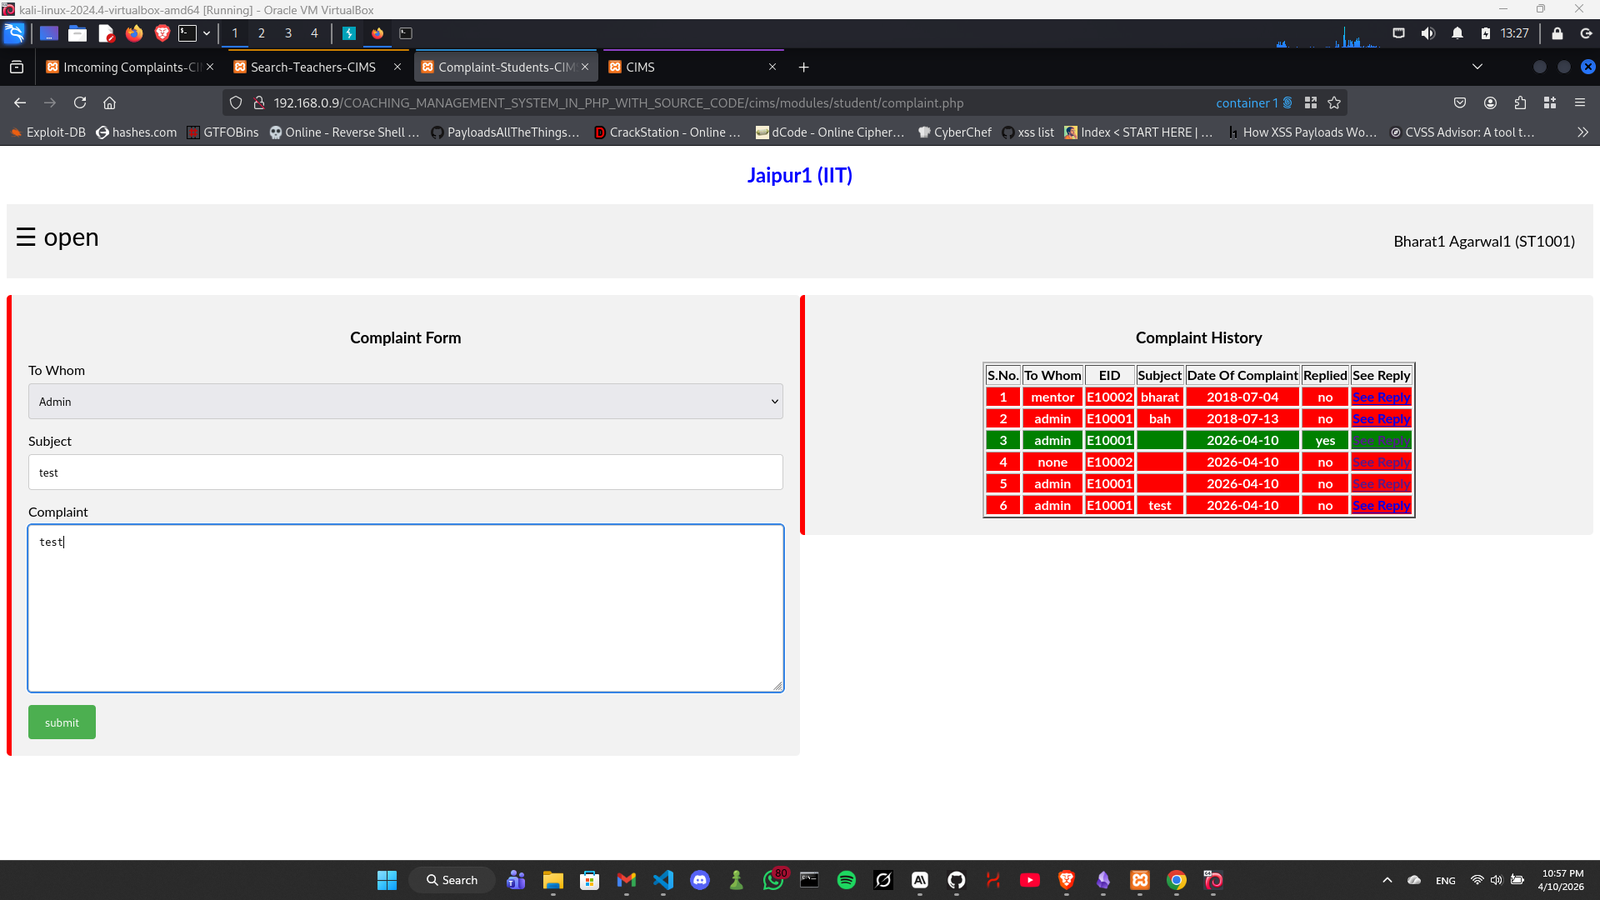
Proof of concept for authenticated SQL injection in Coaching Management System, demonstrating database dump via unsanitized complaintreply parameter.
 sacx-7/cve-2025-50867
Proof-of-concept for a time-based blind SQL injection vulnerability in the takeassessment2.php endpoint of CloudClassroom-PHP-Project 1.0,…
 amitlttwo/cve-2022-31626
Proof-of-concept exploit for CVE-2022-31626, a buffer overflow in PHP's pdo_mysql with mysqlnd driver that can lead to remote code execution.