
testenv
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
database-securityeducationlabs-practice+3
sqlmapproject/testenvA collection of web pages vulnerable to SQL injection flaws
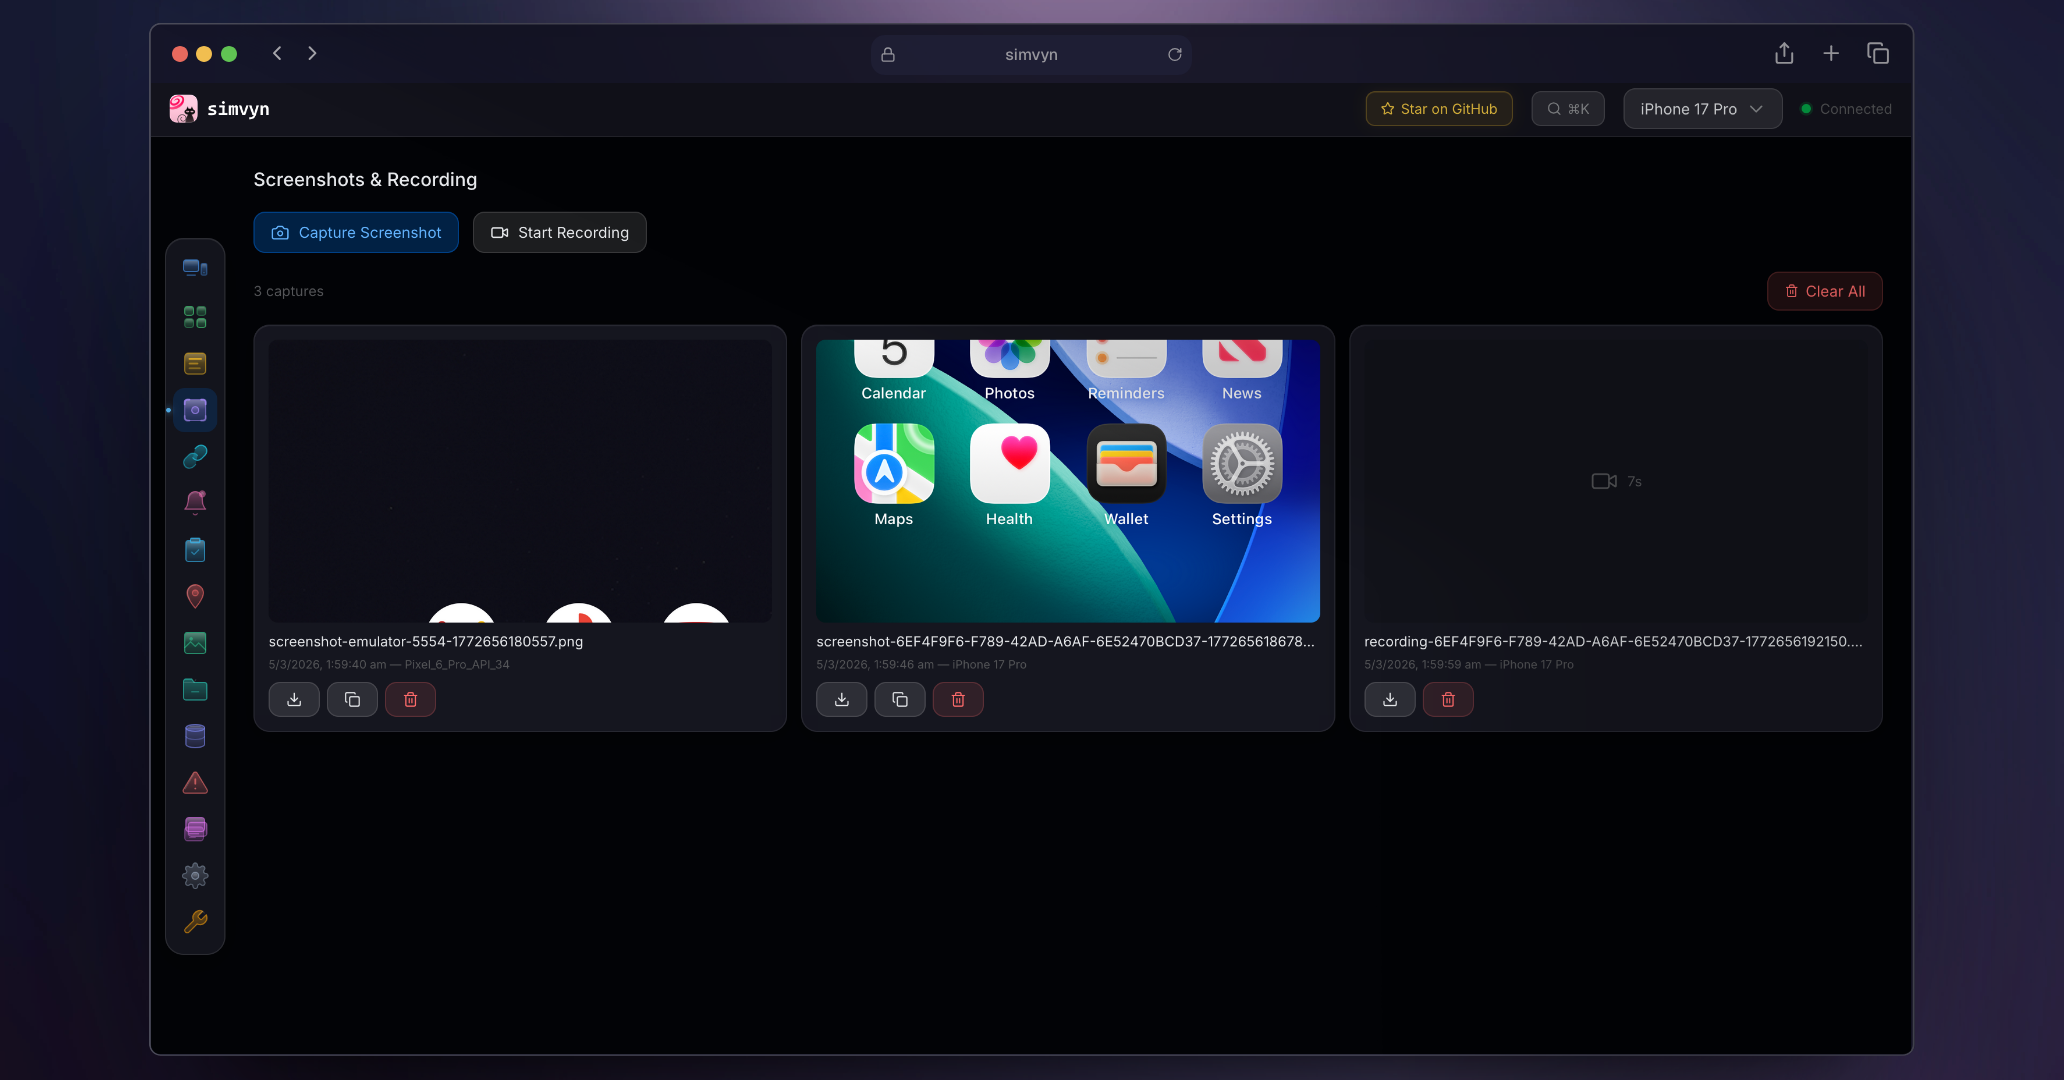 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 cert-polska/mquery
YARA malware query accelerator (web frontend)
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 aeyesec/cve-2022-34265
PoC for CVE-2022-34265 (Django)
 sysdream/pysqli
Python SQL injection framework
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
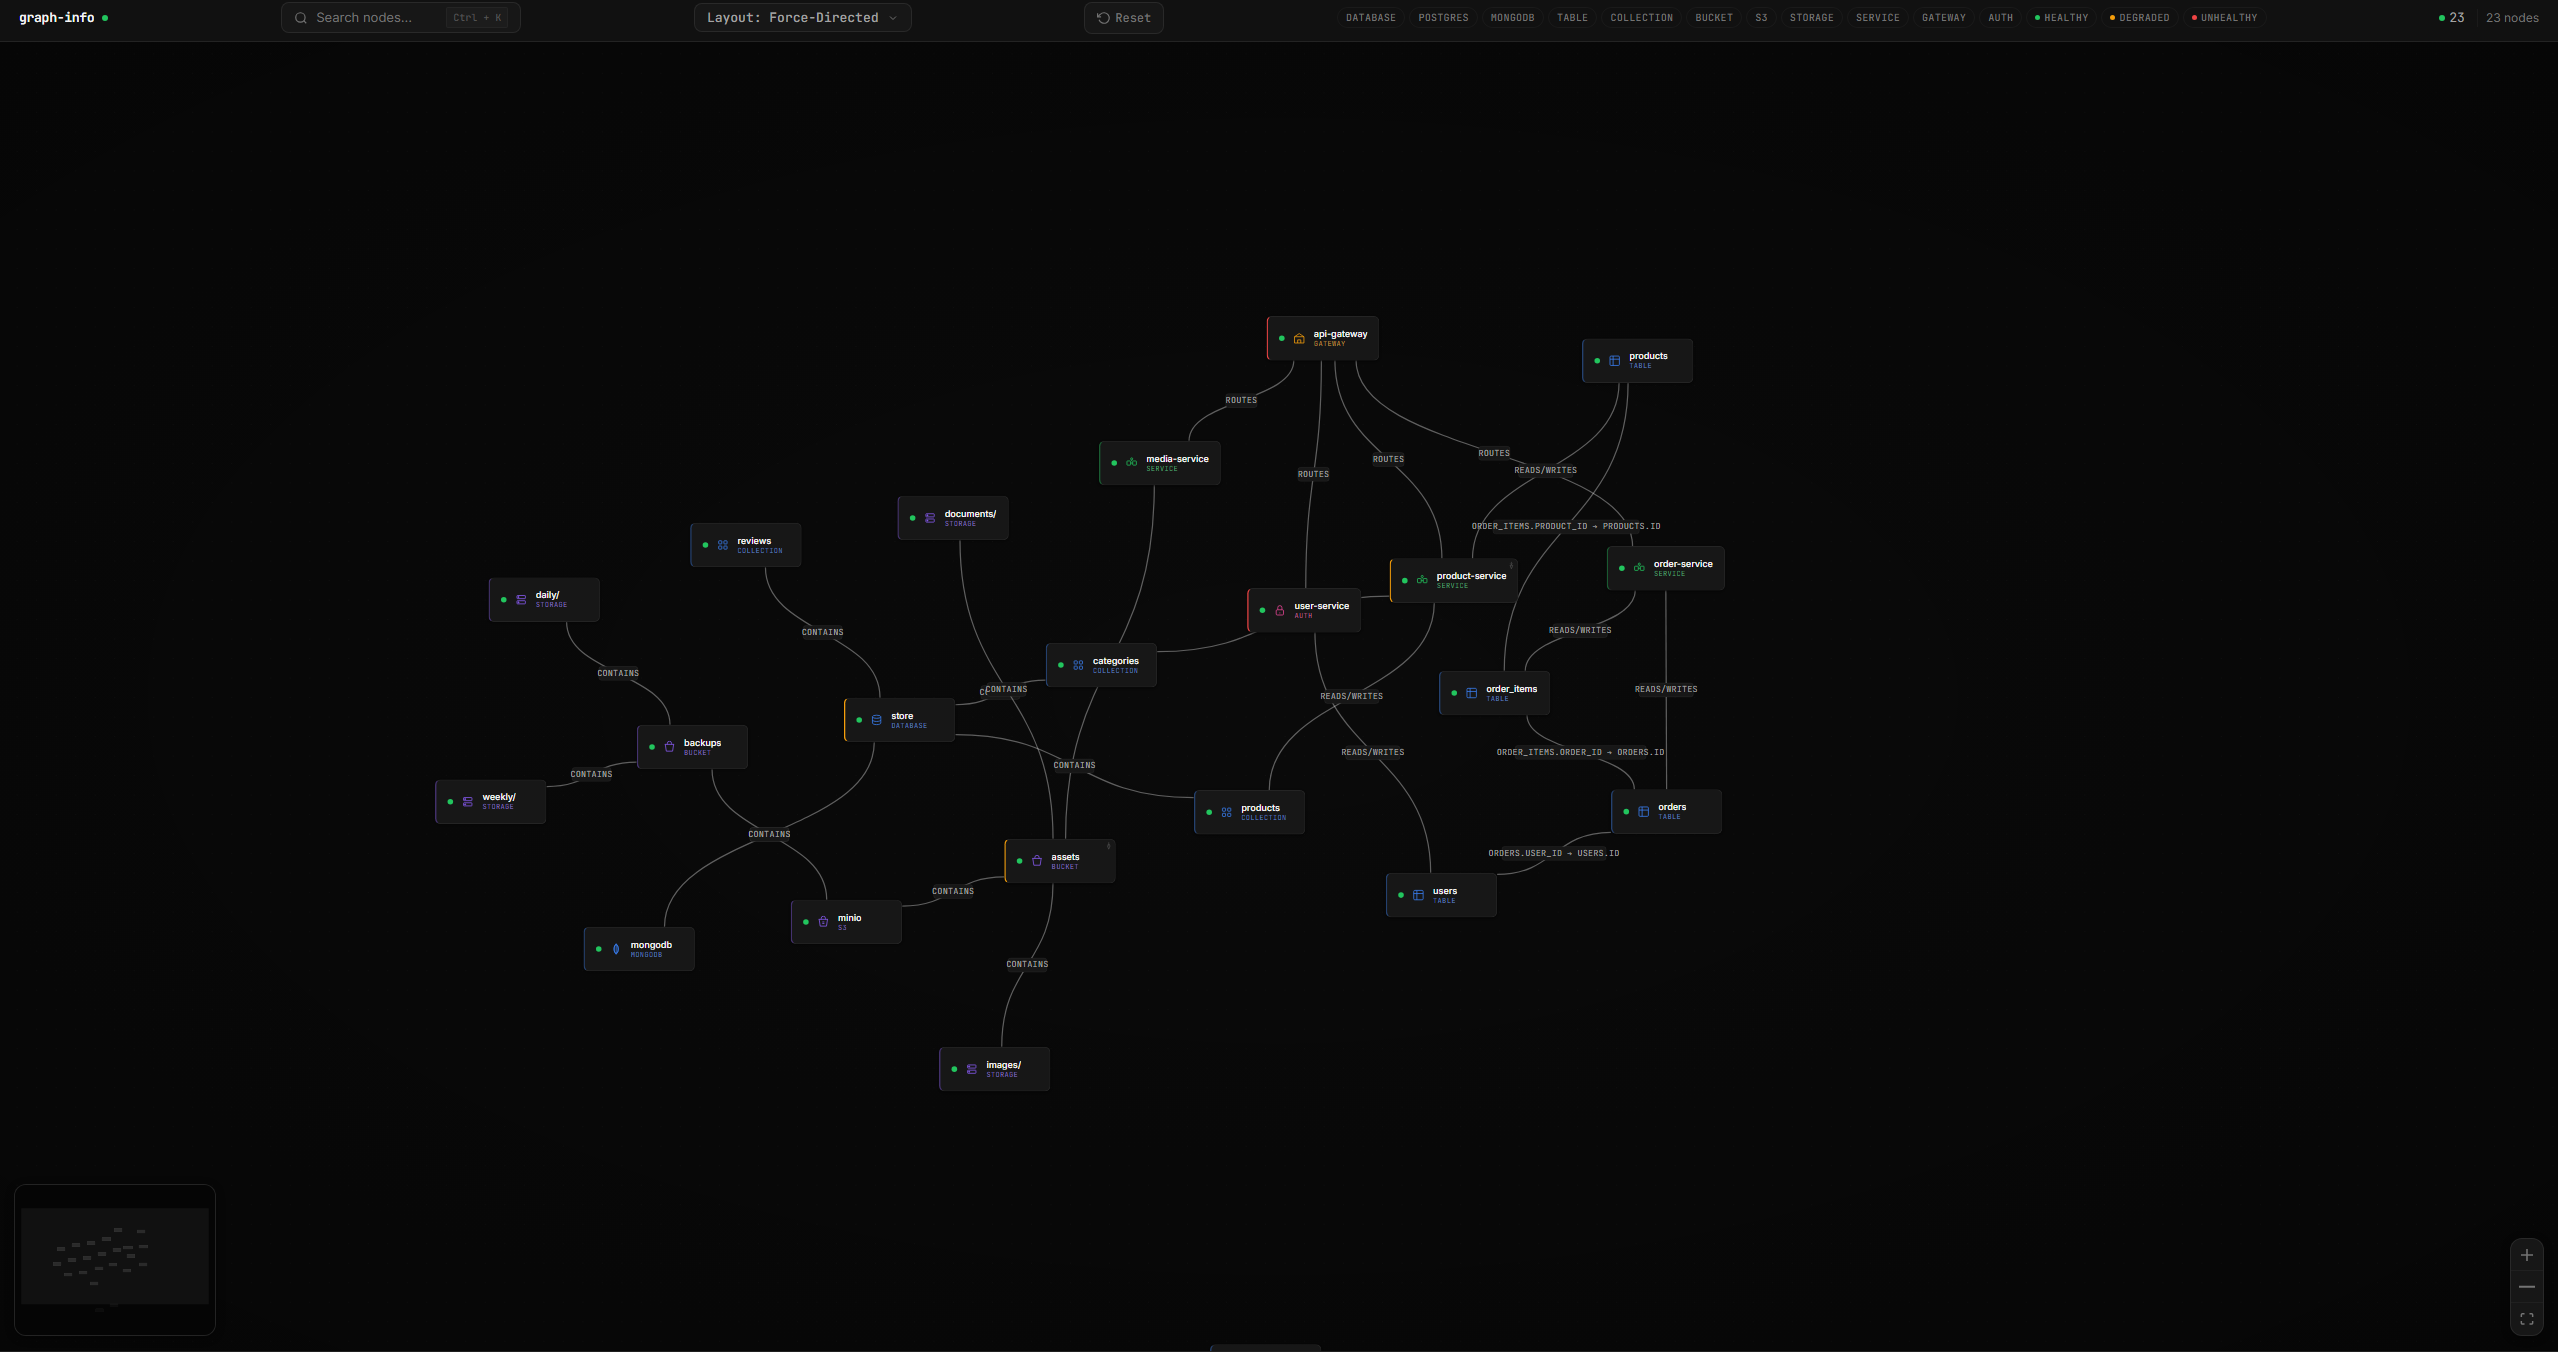 guilherme-grimm/graph-go
simply nodes and graphs
 sadicann/andor
Blind SQL Injection Tool with Golang
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 synacktiv/cve-2024-43468
Exploit for CVE-2024-43468: unauthenticated SQL injection in Microsoft Configuration Manager Management Points, enabling arbitrary SQL execution and…