
CVE-2020-2969
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
database-securityexploitationpassword-attacks+2
emad-almousa/cve-2020-2969Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 kamal-marouane/cve-2022-28346
A flaw was found in the Django package, which leads to a SQL injection. This flaw allows an attacker using a crafted dictionary containing malicious…
 sakthivel10q/sakthivel10q.github.io
🛠 Exploit the CVE-2025-14847 MongoDB vulnerability to reveal sensitive information through crafted zlib-compressed packets and real-time output.
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 agarma/cve-2020-24913-poc
A Poc for CVE-2020-24913, a SQL injection vulnerability in qcubed (all versions including 3.1.1) in profile.php via the strQuery parameter allows an…
 yoyosh/darkreplica
CVE-2026-23631 (DarkReplica) Redis Exploit
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
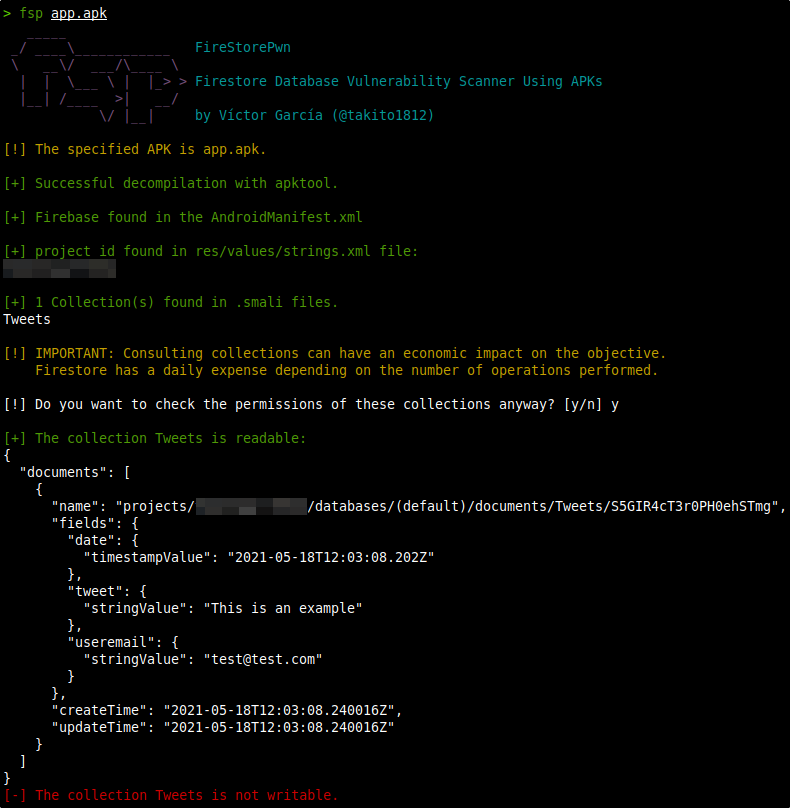 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 xbz0n/cve-2024-33911
Proof-of-concept exploit for CVE-2024-33911, a post-authenticated SQL injection vulnerability in The School Management WordPress plugin v10.3.4,…