

CVE-2024-51030
 vighneshnair7/cve-2024-51030
Proof-of-concept exploit for SQL injection in Sourcecodester Cab Management System 1.0, demonstrating arbitrary SQL execution via the id parameter in…
database-securityexploitationinformation-gathering+3
vighneshnair7/cve-2024-51030Proof-of-concept exploit for SQL injection in Sourcecodester Cab Management System 1.0, demonstrating arbitrary SQL execution via the id parameter in…
 akhlak2511/cve-2024-50972
Proof-of-concept for SQL injection in Itsourcecode Construction Management System 1.0, demonstrating time-based injection via borrow_id parameter and…
 amnnrth/cve-2025-14847
This script is used to identify MongoDB services that are network-exposed and allow unauthenticated protocol handshakes.
 randomrobbiebf/cve-2024-7854
Woo Inquiry <= 0.1 - Unauthenticated SQL Injection
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 gnosticplayers/solr-grab
Steal Apache Solr instance Queries with or without a username and password.
 magichk/cve-2021-22146
PoC exploit for CVE-2021-22146 that dumps Elastic ECE databases (versions 7.10.0 to 7.13.3) during internal penetration tests.
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 watchdog1337/cve-2024-42327_zabbix_sqli
POC for CVE-2024-42327, an authenticated SQL Injection in Zabbix through the user.get API Method
 xploitgh0st/cve-2025-26794-exploit
SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 nu1l0/cve-2024-46636-sqli-modaps
SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…
 strobelpierre/cve-2026-9082
Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…
 ivansmc/cve-2025-10351-poc
Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework
 tunahantekeoglu/mongodeepdive
Context-Aware Memory Leak Scanner & Exploit for CVE-2025-14847.
 rrespxwnss/cve-2025-63572
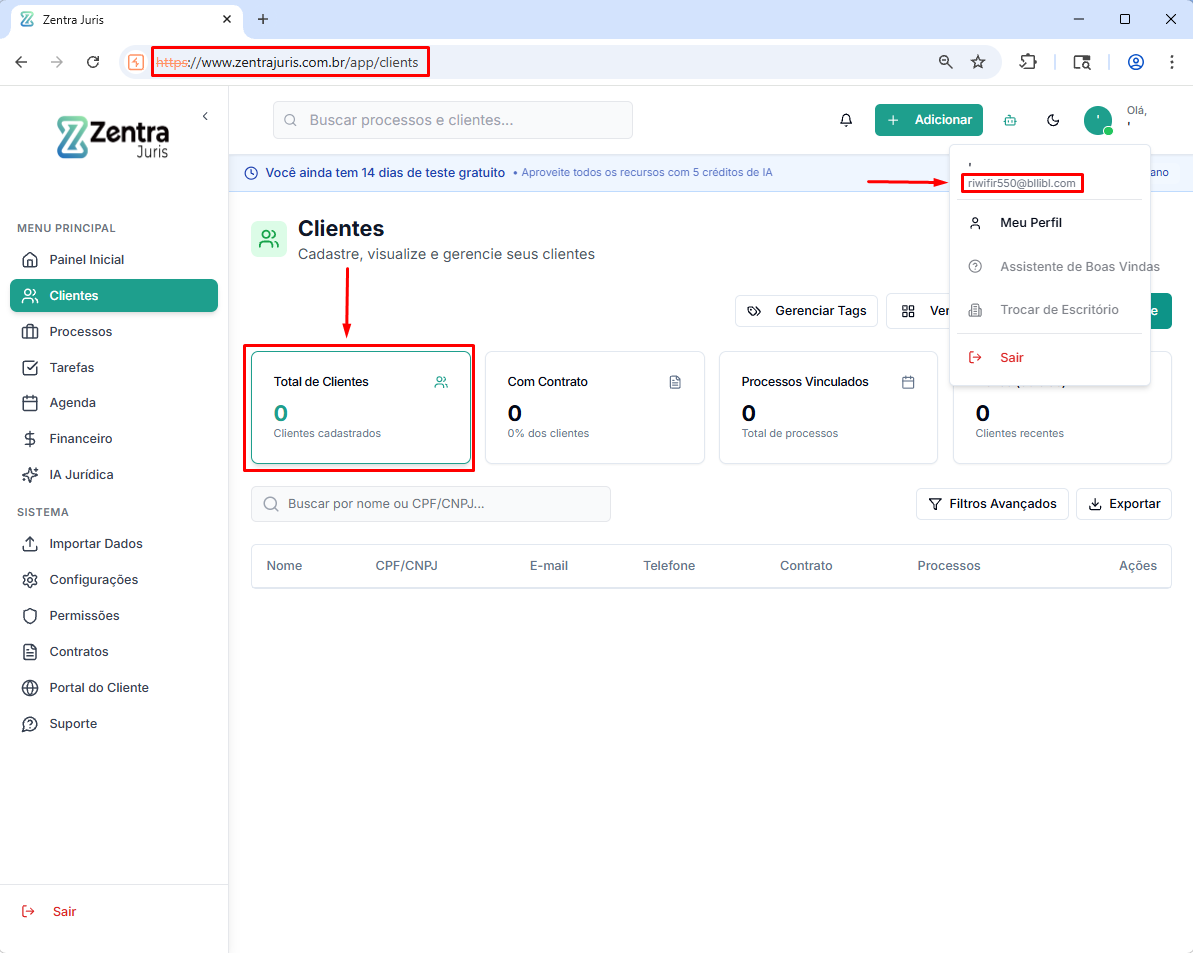
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…