
CVE-2025-1094
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
database-securityeducationexploitation+5
1
aninfosec/cve-2025-1094It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
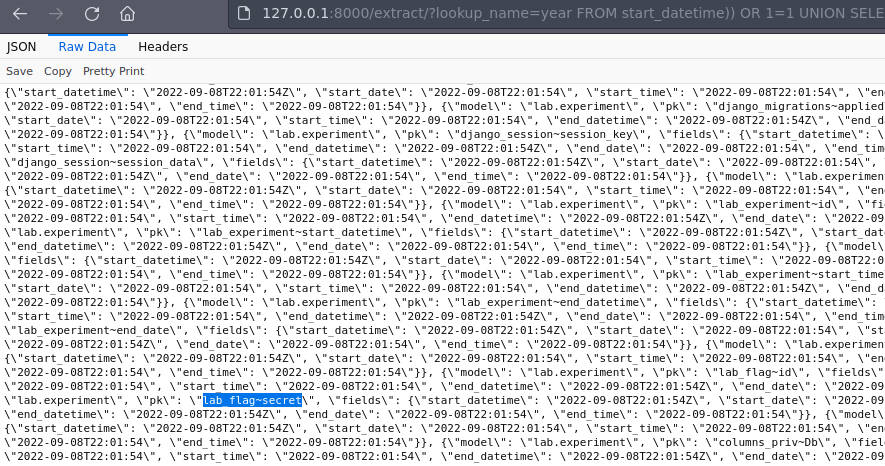 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 vfa-tuannt/cve-2025-14847
Remake of CVE-2025-14847 MongoDB vulnerability demonstration
 chrissub08/cve-2026-33917_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-33917: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
 khengar9274-web/moveit-transfer-2023-breach
Educational case study of the MOVEit Transfer SQL injection breach (CVE-2023-34362) by Cl0p ransomware group, covering attack timeline, exploitation,…
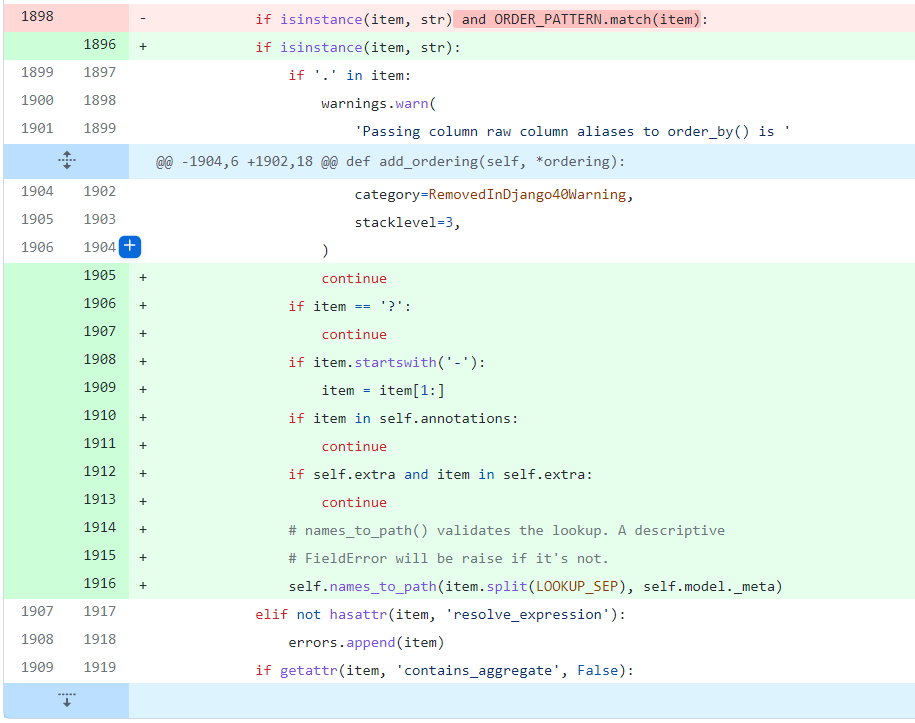 luuanhduc/cve-2021-35042
Django SQL injection vulnerability
 akhlak2511/cve-2024-50970
Proof-of-concept demonstrating time-based SQL injection in Itsourcecode Online Furniture Shopping Project 1.0 via the id parameter in orderview1.php,…
 kamenriderdarker/cve-2024-46532
Reproduction of SQL Injection Vulnerabilities in OpenHIS
 0xs4h4/cve-2025-28009
SQL Injection in Dietiqa App v1.0.20 (CVE-2025-28009) – Unauthenticated remote data access via vulnerable parameter.
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…